Summary
- A DHCP server on the local network can install classless static routes through option 121, and a route more specific than the VPN's default route wins. The traffic leaves over the physical interface while the tunnel reports itself connected and the kill switch stays idle.
- The identifier that made this news, CVE-2024-3661, describes a protocol — IETF DHCP, version 0 — while NVD's enrichment names commercial VPN clients. The researchers' strongest remedy is not a client setting but a network namespace at the provider.
In the researchers' own account of TunnelVision, the connection indicator kept saying connected while traffic left the tunnel. That single sentence is the whole story, and it is worth being precise about why it happened, because the reasons are unflattering to a security product's central promise.
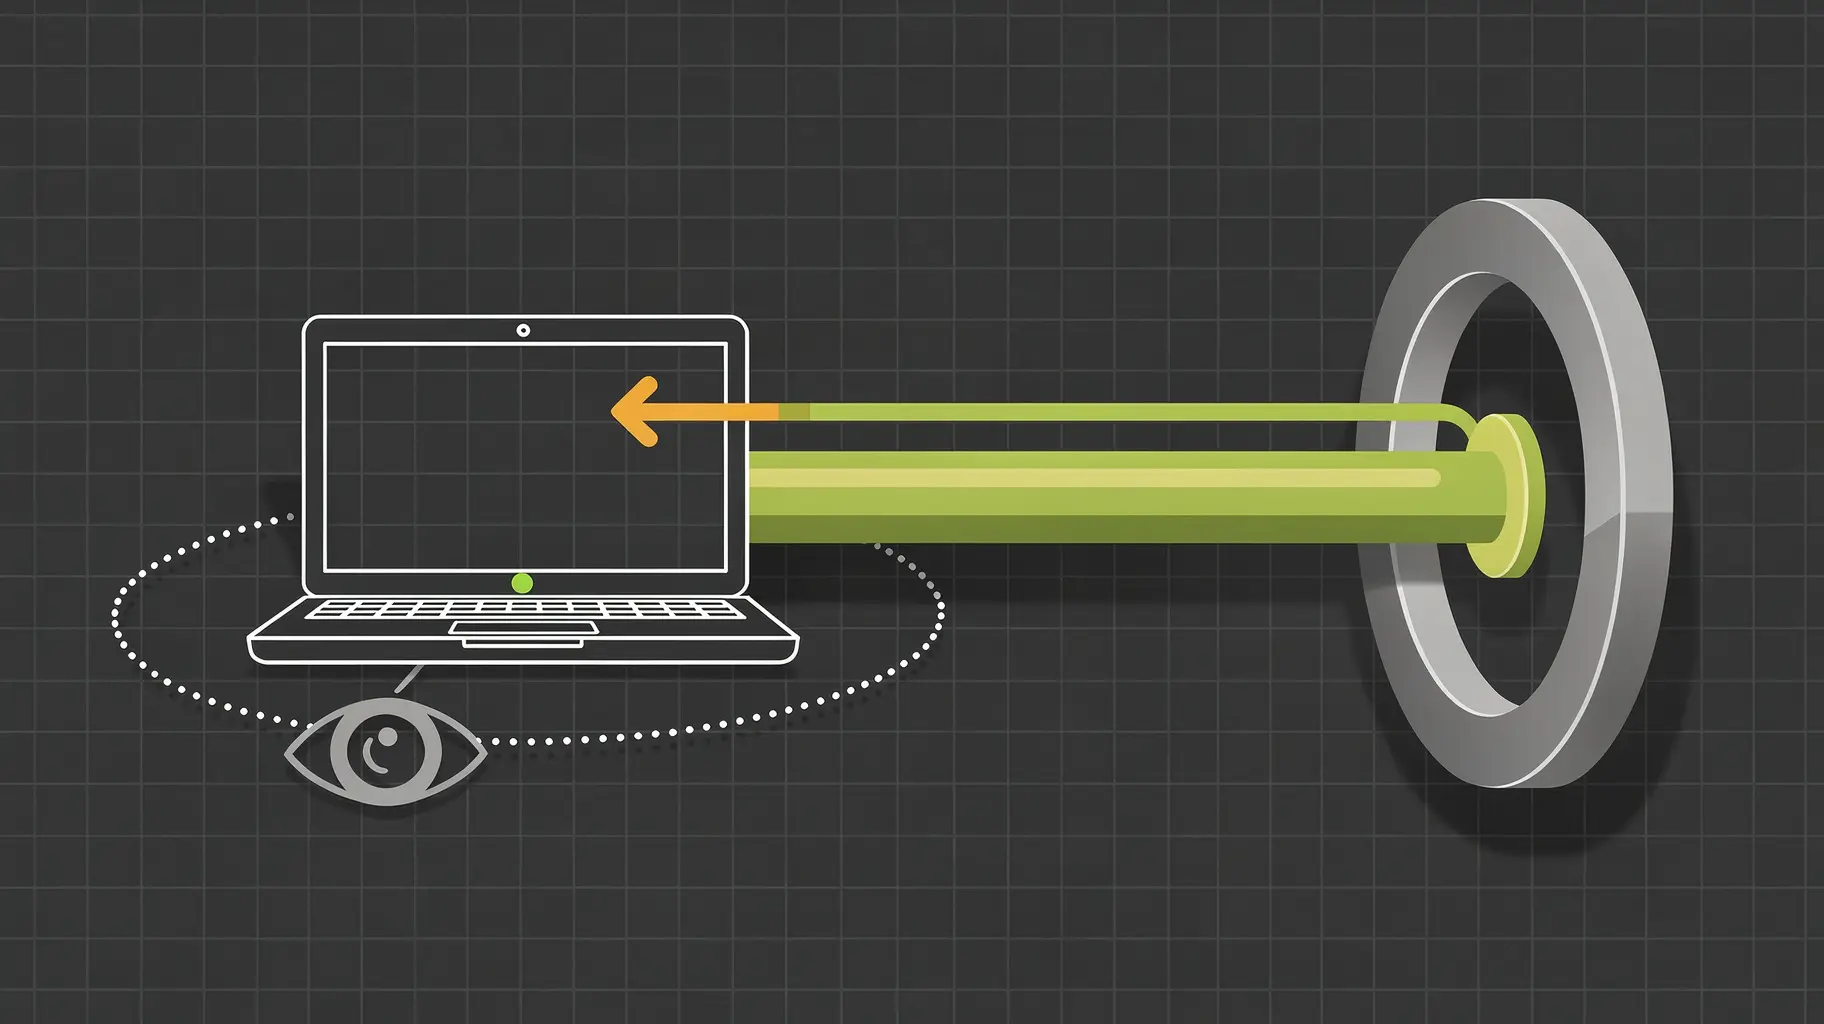
A VPN client that works by routing rules does not own your traffic. It owns a route table. When the tunnel comes up, the client installs a broad default route and sends everything through the encrypted interface. A DHCP server on the same local network can hand the client classless static routes in option 121, and each of those routes carries a longer prefix than the tunnel's default. Routers prefer the more specific entry.
So the traffic named by that longer prefix steps out of the tunnel onto the physical interface — over the very link the tunnel itself already uses — and the control channel sees nothing wrong, because nothing about it is wrong. The cipher is intact. The kill switch, which watches the tunnel, has no event to react to. In the researchers' testing it did not engage.
Two preconditions do the work. The client must accept a lease from a server the attacker controls, and the client must implement option 121 at all. The write-up describes rogue DHCP starvation, response races during renewal and ARP spoofing as same-network ways to reach that position. It also records which systems it observed behaving this way — Windows, Linux, iOS and macOS — and which did not: Android, because Android did not support option 121. That detail matters more than it looks. The affected set here is a set of implementations, tested, not a category called "all VPN clients".
Any product whose client ignores option 121 is not in this story at all. The write-up also notes that VPNs relying only on routing rules are exposed whether the tunnel runs WireGuard, OpenVPN or IPsec, and that the cryptography was never the part that failed.
The warning is older than the product category
Option 121 is not a bug. It is a feature with a documented downside, and the document is RFC 3442, published in December 2002. The option carries destination descriptors and router addresses — no separate interface identifier, which is precisely why the supplied route arrives without the client knowing which link it belongs to. A client that supports option 121 must install the routes it is given, apart from narrow local-subnet exceptions. When option 121 is present, that client must ignore the Router option entirely.
The RFC does not pretend this is safe. In its own words, the classless static routes option can be used to misdirect network traffic. It goes on to warn that the option can cause denial of service or enable a man-in-the-middle attack by naming a snooper's router address. For compatibility, administrators are advised to send both the Router option and the classless routes, with clients giving precedence to the classless ones. The earlier framework, RFC 2132 from March 1997, had already split the two ideas: option 3 carries a list of routers on the client's subnet, option 33 carries classful static route pairs, and the default route was made illegal in option 33 for good reason. Twenty-one and a half years separate the December 2002 warning from the May 2024 disclosure. The hazard did not arrive unannounced. It arrived documented, in a document implementers were expected to read.
What the record actually says
The identifier attached to this work is CVE-2024-3661, and its own fields are worth reading rather than assuming. The CVE record is in state PUBLISHED, assigned by cisa-cg, with dateReserved 2024-04-11, datePublished 2024-05-06 and dateUpdated 2024-08-28 — twenty-five days from reservation to publication, and 114 days from publication to that update, both counted from the record's own dated fields. Its title is "DHCP routing options can manipulate interface-based VPN traffic". Its affected declaration names vendor IETF, product DHCP, version 0, status affected. That is a statement about a protocol, not about a vendor.
The enrichment at NVD says something else, and this is where a careful reader has to slow down. The NVD record carries vulnerability status Analyzed, published 2024-05-06T19:15:11.027Z and last modified 2026-06-17T07:44:45.760Z — roughly two years and six weeks apart, on the record's own timestamps. It assigns CVSS 3.1 base score 7.6 High, vector AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:L: adjacent network, low complexity, no privileges, no user interaction, unchanged scope, high confidentiality impact with low integrity and availability impact. And it separately enumerates product configurations naming FortiClient, Cisco AnyConnect or Secure Client, Palo Alto GlobalProtect, Citrix Secure Access Client, F5 BIG-IP Access Policy Manager, WatchGuard clients and Zscaler Client Connector. Those names come from a database's configuration enrichment. They are not vendor confirmations, and their presence does not mean every listed client refuses the route or fails to.
So three different scopes are circulating around one identifier, and they are not interchangeable: a protocol-level CNA declaration naming IETF DHCP version 0; a database's product list; and the researchers' broader claim about routing-based VPNs as a class. A reader who picks any one of them and calls it the whole scope will be wrong in a specific, checkable way. There is also a register mismatch worth naming. The write-up presents a technique built from intended DHCP and routing behaviour; the enriched record carries a High severity score. Both can be true of the same mechanism, and neither quietens the other.
Where the fix actually lives
The remedy the researchers rank first is not a checkbox on a client. Their sentence is short: "The strongest recommendation we have is for VPN providers to implement network namespaces on operating systems that support them." On Linux they describe namespaces as a complete fix, because a namespace isolates the interfaces and the routing table together — the route the DHCP server hands over lands in a table that has no path to the tunnel's traffic.
Everything else on their list is an alternative with a price. A firewall rule that blocks the physical interface except for DHCP and VPN-server traffic works, and can produce selective denial of service plus a traffic-analysis side channel. Telling the client to ignore option 121 while the tunnel is up works, and can break legitimate connectivity — which is why they say that if you do it, it should be mandatory rather than optional.
A trusted cellular hotspot, a non-bridged virtual machine and simply avoiding untrusted networks for confidential work are all real mitigations, and all of them are about where you sit rather than what the client does. For organisations that run their own networks, the list is unglamorous and sound: DHCP snooping, ARP protections, and encrypting internal resources with HTTPS or comparable protocols. And for VPN providers, two asks that are really one: document your mitigations, and stop claiming protection against all local-network attacks.
For the operator holding the laptop, the check that survives all of this is a route table read. Compare the routes installed before and after the tunnel comes up. Look at which interface each route names. Ask whether the DHCP client will accept a lease from any server that answers first, and whether it honours option 121 at all. Those questions have answers on the host, and the answers do not depend on a vendor's marketing page.
That last point is where the evidence stops and I have to be exact about it. I did not read a vendor advisory for this article, so I cannot tell you that any named product now refuses an option-121 route — only that its name appears in an enrichment list. The NVD detail page opened but returned no readable lines, so the NVD description and severity here come from the official API record and the indexed result rather than from that page. The CVE Program page rendered only a JavaScript shell, so the record's fields were read from the CVE List JSON instead. The canonical RFC 3442 address returned HTTP 429 and all RFC substance came from the plain-text rendering. If that sounds like an unusual amount of plumbing to mention in one paragraph, it is because a routing story is exactly the kind where a confident reconstruction would be worse than a documented gap. Nothing in this archive had covered TunnelVision before: a literal search of our own published record on 17 November 2026 returned no rows. The firm behind the disclosure is Leviathan Security Group, Inc., and its page is where the mechanism, the testing and the ranking of remedies come from.
Member Briefing
Read the full trend briefing
Members read the full briefing with the source notes behind every finding.
Strategic Circle
A daily briefing in your language, built from changes we have verified.
Join for USD 20/monthCancel anytime.
Members also get the full research library, a daily briefing on the networks they follow and the private forum.