
Summary
- Route flap damping converts recent withdrawal history into a decaying penalty and suppresses a route once that local score crosses a configured threshold; the score predicts neither legitimacy nor future behavior.
- RFC 7196 recommends much more conservative thresholds than older defaults and permits a calculate-only mode, because excessive damping can turn ordinary convergence into prolonged loss of reachability.
A history score becomes an enforcement decision
RFC 2439 begins with a real control-plane problem. Repeated route changes consume decision-process capacity and force forwarding entries to be added and removed. Under enough load, one struggling router can add work to its peers and contribute to a wider failure pattern. A BGP implementation cannot assume that a sender will shield it from instability.
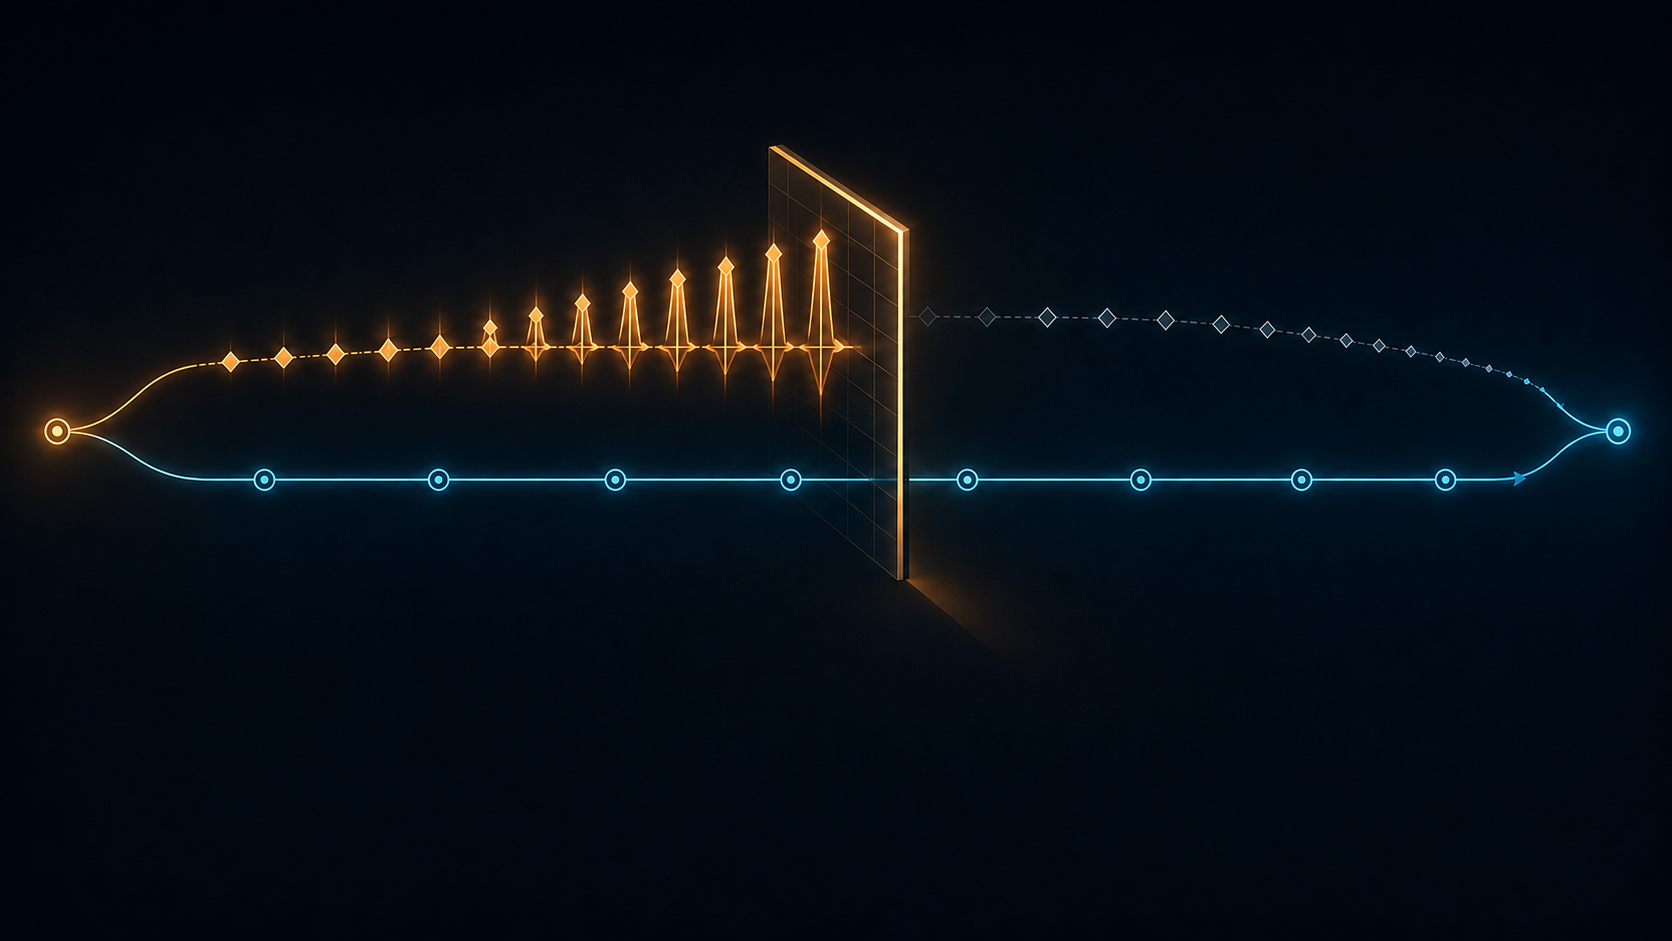
Route flap damping responds with memory. It keeps an instability figure for each external route, increases that figure when the route is withdrawn and reduces it exponentially while the route remains unchanged. Above a cutoff threshold, the route is suppressed. Below a reuse threshold, it can be used again, with a maximum hold time limiting how long prior instability can keep it out.
The mechanism is deliberately local. RFC 2439 applies stability-sensitive suppression when receiving routes from external peers. Applying the technique to IBGP-learned routes, or withholding advertisements after route selection, can create routing loops. Damping therefore does not authorize a network to redefine whether a prefix exists. It lets one border decide whether recent behavior justifies temporarily refusing or withholding that route within a precisely bounded part of the control plane.
The threshold separates beneficiaries from those who pay
The beneficiaries are the router and its peers: less churn reaches the decision process, and fewer forwarding changes consume resources. Stable alternatives may also shield traffic while an unstable path is suppressed. But the cost belongs to the prefix being damped and to users who may lose a viable path. A penalty is based on recent transitions, not a diagnosis of intent, fault or future stability.
That distinction became central after deployment experience showed that traditional values were too aggressive. RFC 7196 cites a one-week experiment in which 3% of prefixes produced 36% of messages at a router with Tier-1 and Internet Exchange feeds. With a suppress threshold of 6000, the experiment measured a 19% update-rate reduction compared with no damping and 90% fewer damped prefixes than with a threshold of 2000. Those are historical measurements from a particular experiment, not a forecast for every network or the present Internet.
The standards guidance follows the distributional problem. An internal maximum-penalty constant MUST be raised to at least 50000. Yet existing implementations SHOULD NOT change their configurable defaults automatically, because doing so could break existing operational configurations. Operators wanting less destructive but still somewhat aggressive damping SHOULD set the suppress threshold to no less than 6000; conservative operators SHOULD use no less than 12000. These are recommendations, not guarantees that either number is correct for every topology.
Observation can precede suppression
RFC 7196 allows implementations to offer a calculate-but-do-not-damp mode. That MAY-level option is strategically important: the operator can see which prefixes a parameter set would suppress without actually removing reachability. It creates a boundary between evidence gathering and enforcement.
The resulting operating sequence is stronger than enabling a historical default. Measure the candidate population, identify which changes reflect normal convergence, compare alternate-path availability, and model how long the reuse threshold would keep routes out. Only then should the operator decide whether the reduction in churn justifies the suppression cost.
The security boundary is equally explicit. An attacker can generate false flapping in an effort to cause a victim prefix to be damped. RFC 7196 says conservative parameter changes should slightly mitigate that risk; it does not say damping authenticates updates, identifies the attacker or eliminates the attack. A deliberately induced penalty still looks like an instability history to the local algorithm.
Evidence and limits
RFC 2439 defines the damping model, its per-route memory, thresholds, decay and scope. RFC 7196 supplies later measurements, revised parameters and the calculate-only option. RFC 4271 provides the underlying BGP exchange and decision context. The assessment of power, authorization, beneficiaries, cost and control is analysis derived from those documents.
The sources do not reveal the current settings of a named network, prove that a flapping route is malicious, establish a universal safe threshold or guarantee that a particular deployment preserves reachability. Sampling, vendor implementation, topology and alternate paths all affect the outcome.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance