
Summary
- RFC 5217 describes a case in which PKI1 can build a certification path through dual-member PKI2 to PKI3, yet validation under PKI domain 1 must not succeed because PKI1 and PKI3 do not share that domain. A path proves that certificates can be connected; it does not prove that the connection is authorised for the requested policy.
- The operative evidence sits in trust anchors, policy mappings, name and policy constraints, domain-membership state, revocation information and the relying party's completed validation. Cross-certification and bridge connectivity are inputs to that decision, not substitutes for it.
The rejection that showed the boundary was working
The incident record looked like a validation failure. The application had found every certificate it needed. Every signature on the candidate chain checked out. The sequence ran from its chosen trust anchor, through an intermediate PKI, to the subscriber certificate at the far end. Then the validator rejected it.
That result may be the most accurate record in the system.
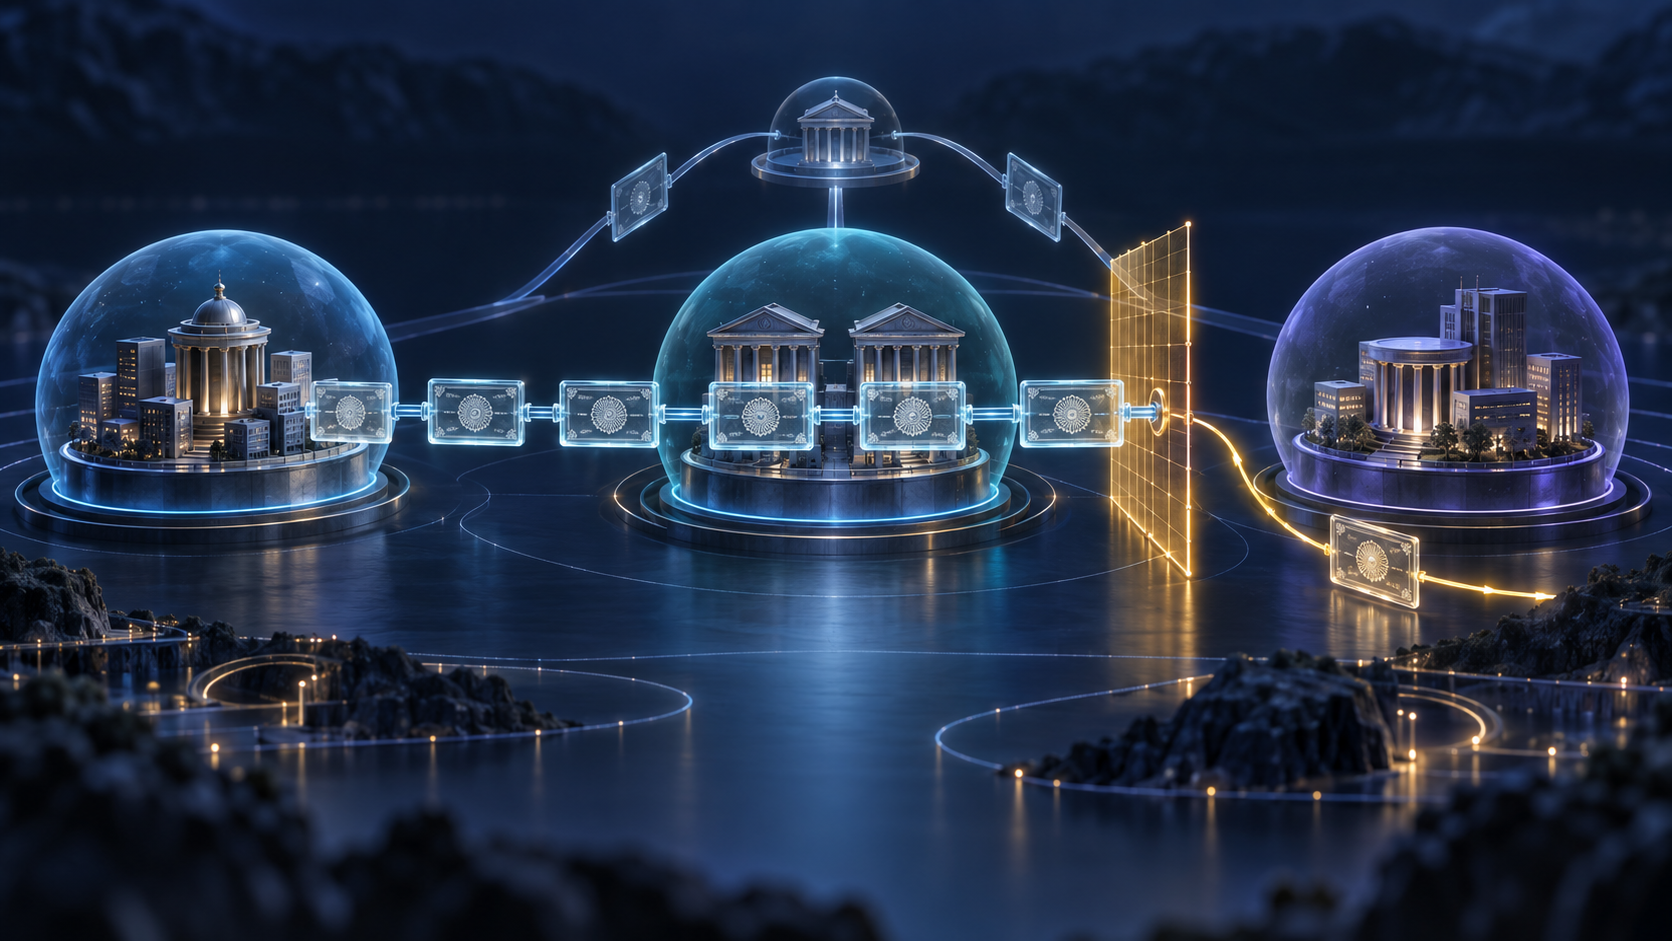
RFC 5217 supplies a deliberately sharp example. PKI2 belongs to two PKI domains. A certification path exists from PKI1 to PKI2, and another exists from PKI2 to PKI3. Graphically, PKI1 can therefore reach PKI3. But PKI1 and PKI3 do not share membership in domain 1. Validation of that path under domain 1's policy must not succeed.
Nothing in this scenario requires a broken signature, a forged certificate or a missing file. The path is technically constructible and normatively inadmissible. The failure is the control.
Path building answers the wrong question first
Certificate processing contains two tasks that dashboards often collapse. Path building asks whether the software can discover an ordered sequence from a trust anchor to an end-entity certificate. Validation asks whether that candidate satisfies the intended policy, constraints, purpose and time conditions.
The distinction is not cosmetic. A bridge, a mesh or a dual-domain member expands the graph that a builder can search. It may reduce the number of bilateral cross-certificates and make distant issuers reachable. None of that says that every reachable certificate should be accepted for every application.
RFC 5217 preserves that separation in its architecture. Each participating PKI keeps its own Certificate Policy OIDs and its own Principal CA. It enters an external relationship after a business decision and review of the other PKI's policy and governance documents. The cross-certificate formalises a relationship; it does not erase the policy work that gave the relationship a scope.
A useful operational sentence follows: path construction is discovery, not delegation.
The middle domain can leak reachability
The three-PKI example matters because transitivity is easy to overstate. PKI2's membership in two domains creates a route between worlds that did not directly authorise each other. If constraints are absent or weak, software may discover a chain that appears to inherit trust across the join.
RFC 5217 puts the boundary into signed material. Cross-certificates should carry policy mappings or name constraints that prevent validation outside the relevant domain. When a domain wants a path restriction to hold, it should not merely assume every relying party has configured an equivalent local rule. The constraint belongs in the cross-certificate where it can travel with the relationship and be verified.
This is also why membership changes are operational events, not directory housekeeping. A PKI joining or leaving another domain can alter the set of constructible paths. Members must disclose those memberships and changes. The affected domain must review its cross-certificate constraints; if the new graph changes what should be allowed, the certificate must be revoked and reissued with the correct boundary.
The certificate is signed, but the world described by it can change.
A bridge is not a universal root
RFC 5217's Bridge model reduces the number of direct cross-certifications needed among domains. The Bridge CA sits in a neutral position and maps policies across relationships. Crucially, it must not be used as the trust anchor CA of any participating domain, and it does not issue ordinary end-entity certificates.
That design prevents a coordination point from silently becoming the sovereign root of every participant. A relying party still starts from its domain's chosen anchor. A path may pass through the bridge, but the validation state must carry the applicable mappings and constraints to the other side.
The architecture therefore resists a familiar governance inflation. Central usefulness is not central authority. The bridge can make relationships manageable without acquiring the right to define every participant's acceptable risk.
Trust lists make the principal visible
RFC 5217 also describes trust models outside CA-to-CA relationships. A Local Trust List is maintained by one relying party for its own use. It is simple and can avoid complex cross-certification, but its maintenance burden stays local. A Trust Authority instead maintains a list for one or more relying parties, centralising the work.
Neither model makes trust automatic. Before including a PKI, the relying party or Trust Authority is responsible for reviewing its Certificate Policy, deciding whether the assurance is acceptable, understanding obligations imposed on relying parties, evaluating warranties and revisiting policy, revocation and compromise notices over time. If it does not want to inherit trust in other members of a domain, it must inhibit policy mapping.
These duties expose the real principal. The party that will rely on the certificate—and bear the loss if that reliance is misplaced—must have an attributable acceptance rule. A list entry is not clerical decoration. Adding a CA can authorise certificates that were previously refused; removing one can deny service.
Record an acceptance-authority receipt
Most systems retain enough evidence to reconstruct a chain but not enough to reconstruct the authority for accepting it. Leadership should require an acceptance-authority receipt for consequential uses of cross-domain certificates.
The receipt should bind the relying party and application, decision time, validation-engine version, trust-anchor fingerprint and installation source. It should retain the exact candidate path, initial policy set, explicit-policy and inhibit-mapping settings, each processed policy mapping and name constraint, the relevant domain-membership snapshot, and the current status of every cross-certificate.
It should also record the Trust List or Trust Authority version, the freshness and result of CRL or OCSP retrieval, the final validation outcome, the precise rejection reason and the downstream action actually allowed or denied.
The rejected path deserves preservation too. If a path was buildable but correctly failed at the policy boundary, deleting it as noise destroys evidence that the control worked.
What this evidence does not claim
RFC 5217 is an Informational memorandum, not a claim that every PKI uses one architecture. A path that fails in one policy context may be valid under another trust anchor, community or application purpose. Nor does this analysis allege a defect in any named CA, bridge, vendor or deployment.
The narrower point is enough. Signature validity, path existence, domain participation and application acceptance are separate facts. Treating the first available green signal as the final decision converts interoperability into accidental authority.
Sources
- RFC 5217: Memorandum for Multi-Domain Public Key Infrastructure Interoperability
- RFC 5280: Internet X.509 PKI Certificate and CRL Profile
- RFC 4158: Internet X.509 Public Key Infrastructure—Certification Path Building
- RFC 3647: Certificate Policy and Certification Practices Framework
- Lu Heng: Running-Code Primacy
Additional standards record
- RFC 5217 plain text
- RFC 5217 information record
- IETF Datatracker record
- IETF Datatracker history
- RFC 4949: Internet Security Glossary
- RFC 5914: Trust Anchor Format
- RFC 5934: Trust Anchor Management Requirements
- RFC 6024: Trust Anchor Management Protocol Requirements
- RFC 5055: Server-Based Certificate Validation Protocol
- RFC 6818: Updates to RFC 5280
- RFC 6960: Online Certificate Status Protocol
- RFC 5019: Lightweight OCSP Profile
- RFC 6962: Certificate Transparency
- RFC 7030: Enrollment over Secure Transport
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance