Summary
- RFC 2369 standardised where a mail client could find list commands; it did not make a rendered button proof that a subscription, unsubscription, post or archive operation succeeded.
- Its ordered alternative URLs, confirmation requirement and nested-list rules reveal an evidence chain: advertised route, client choice, user authority, transport, server mutation and later mail flow are different receipts.
A command hidden in plain sight
Before the list headers, users met a different command language on every mailing list. One system wanted a message to a -request address. Another expected a word in the subject. A third parsed the body. A web form might exist, but a mail-only user could not assume access to it. The list worked, yet the interface had to be rediscovered each time.
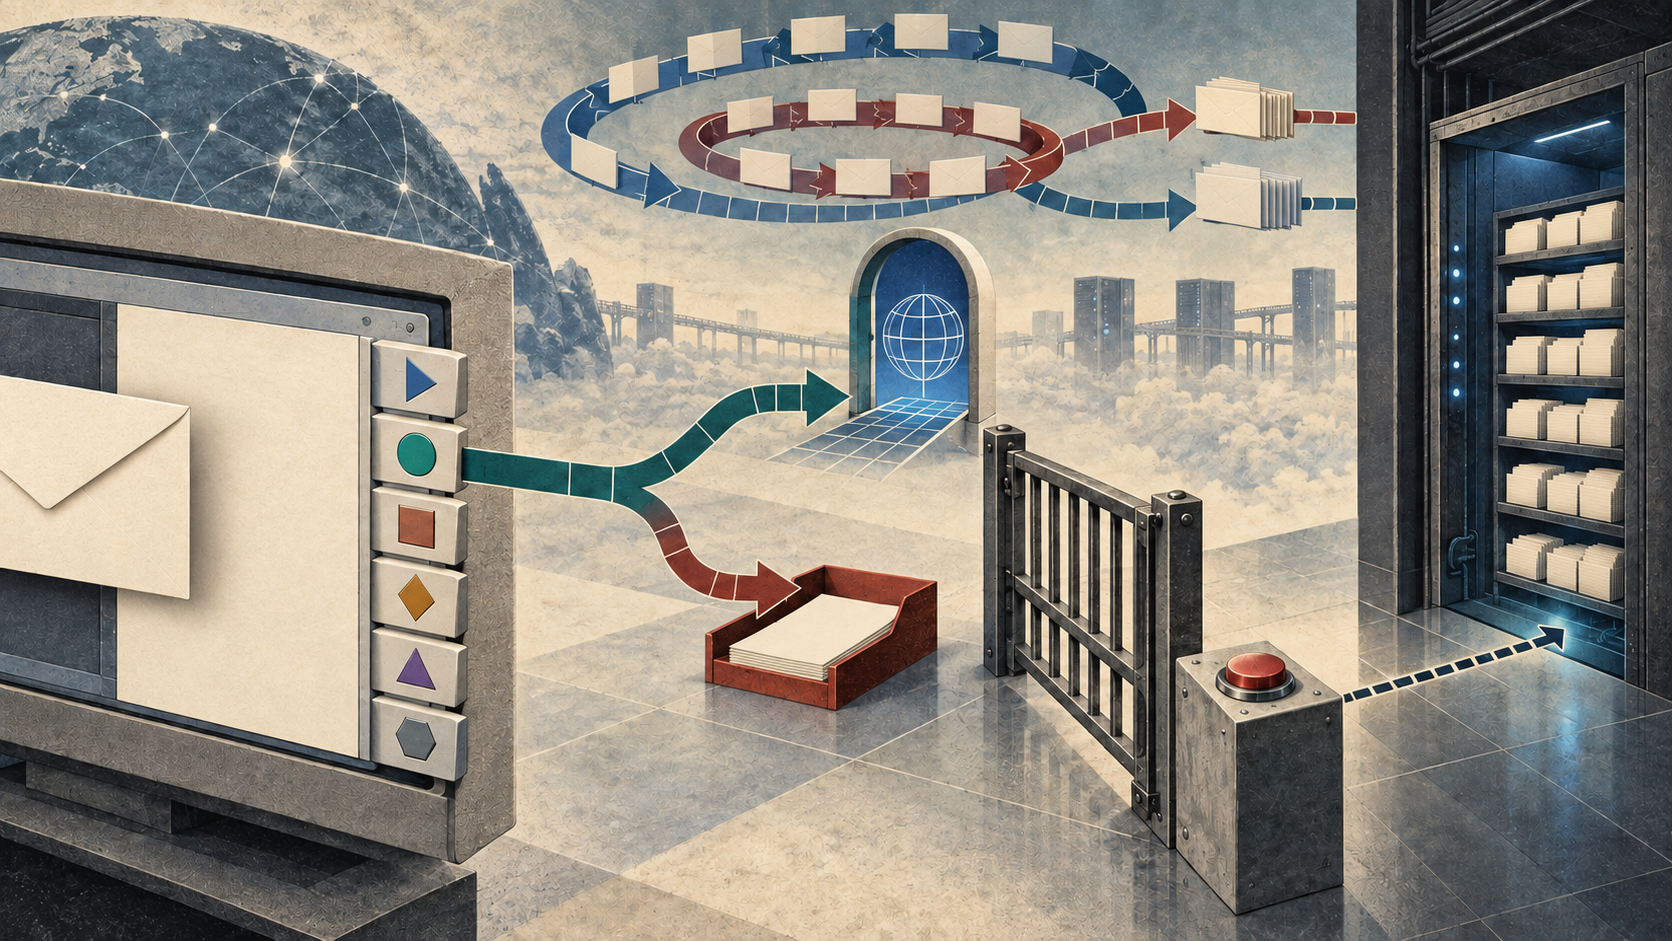
RFC 2369 did not abolish those systems. It placed a small map in each distributed message. List-Help, List-Unsubscribe, List-Subscribe, List-Post, List-Owner and List-Archive could carry URLs that located information or invoked the relevant command. A client that understood the fields could turn them into a menu or button. The cryptic machinery remained behind the message; the reader saw a common surface.
That surface was a projection. The header did not itself remove anyone from a list. It described a command route, preferably a mail route, that a client might know how to use. The distinction matters because a neat control can feel more authoritative than the evidence beneath it.
One field, several routes
The RFC allowed multiple angle-bracketed URLs in one field. Their order expressed preference from left to right. A client was supposed to choose the first protocol it supported and try another only after failure. An HTTP route could lead, while a mailto route remained available to readers without web access.
This design exposed three different facts. The list operator advertised a route. The client knew how to open some subset of the routes. The chosen service might or might not complete the command. None implied the next.
Even the first failure was not fully specified as an end-to-end observation. A browser could open a page that demanded another step. A mailto URL could prepare a message that the user never sent. A request could reach the list manager and still be rejected because the address was wrong, confirmation was required or the list state had already changed. The ordered URLs were a recovery policy for locating an interface, not a transaction log.
Why mailto preserved a human boundary
RFC 2368, published in the same month, described the unusual semantics underneath the common fallback. Resolving a mailto URL did not immediately contact the target. It created a draft with address, subject or body defaults. The user could edit it, send it unchanged or abandon it.
RFC 2369 turned that property into a safety boundary. A client had to give the user a chance to confirm an action. For a mail command, the RFC suggested composing the correctly formatted message without sending it, so the user could inspect, approve or discard it. The header could prefill intent; it could not borrow the user's authority silently.
The design also refused variable substitution. If a command required the client to insert the user's address or another dynamic value, the header could not express it. List-Help or a structured form had to carry the remaining interaction. This was deliberate restraint: a smaller feature that ordinary clients might implement was more valuable than an expressive language few could safely execute.
The list that rewrote the map
Nested lists made provenance visible. A sublist was expected to remove the parent's help, subscribe, unsubscribe and owner fields and insert its own. Archive and post fields followed different inheritance rules. The message a reader received could therefore have crossed several list processors, each with a different claim about which action belonged to which administrative layer.
The RFC said end users must not generate these fields and list processors should not pass user-originated versions through. That was an important defence, but not authentication. In 1998, the specification acknowledged forged or duplicated headers as a property of Internet mail. A client still needed to treat the header as input from the message path, not as independent proof of the list operator's identity.
Six labels, six bounded claims
The field names invited convenient overstatement. List-Post did not mean a post would be distributed; it could identify a moderator or another submission path, and NO meant posting was unavailable. List-Archive pointed toward an archive but did not attest its completeness. List-Owner exposed a contact path, not a promise of reply. List-Subscribe described a request for addition. List-Unsubscribe described a route intended to remove a user.
The correct evidence chain was longer:
- the message contained a syntactically usable field;
- the field survived the list and mail path without misleading alteration;
- the client supported one advertised scheme;
- the user confirmed the action;
- the client transmitted the request;
- the target service accepted and applied it;
- later membership or delivery behavior reflected the new state.
A product could truthfully display a button after step three. It could not truthfully display “unsubscribed” on that evidence alone.
The later one-click lesson
RFC 8058, published in 2017, illuminates rather than erases the old boundary. Automatic scanners had begun fetching unsubscribe URLs and could trigger unintended removal. The later RFC introduced a distinct HTTPS POST signal, required user consent, required DKIM coverage of the relevant headers and constrained the request context. It did not update RFC 2369; ordinary list URLs retained their older semantics.
The historical comparison is revealing. Making a command easier for humans created pressure for automation. Automation then needed stronger provenance and action semantics because a fetch was no longer safely equivalent to a deliberate request. The original button was a useful view. It was never a receipt.
What RFC 2369 actually standardised
RFC 2369 made list operations discoverable across incompatible managers. It preserved email-only access, allowed partial adoption, kept help as a universal escape hatch and offered clients a stable vocabulary for interface design. That was a substantial interoperability gain.
It also left the decisive work outside the header. A list generated the map. A mail system carried it. A client interpreted it. A user authorised a choice. A separate service changed state. Only later observations could show whether messages stopped or membership changed. The standard's durability lies in that modest division of labour.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance