
Summary
- For a candidate datagram of at least 21 bytes, a final-16-byte match to a token associated with the connection tells the receiver to terminate; it does not authenticate who sent the datagram.
- It does not identify why connection state vanished, which backend was responsible or when loss occurred.
- Incident response needs routing, key-epoch and last-good-state evidence alongside the packet.
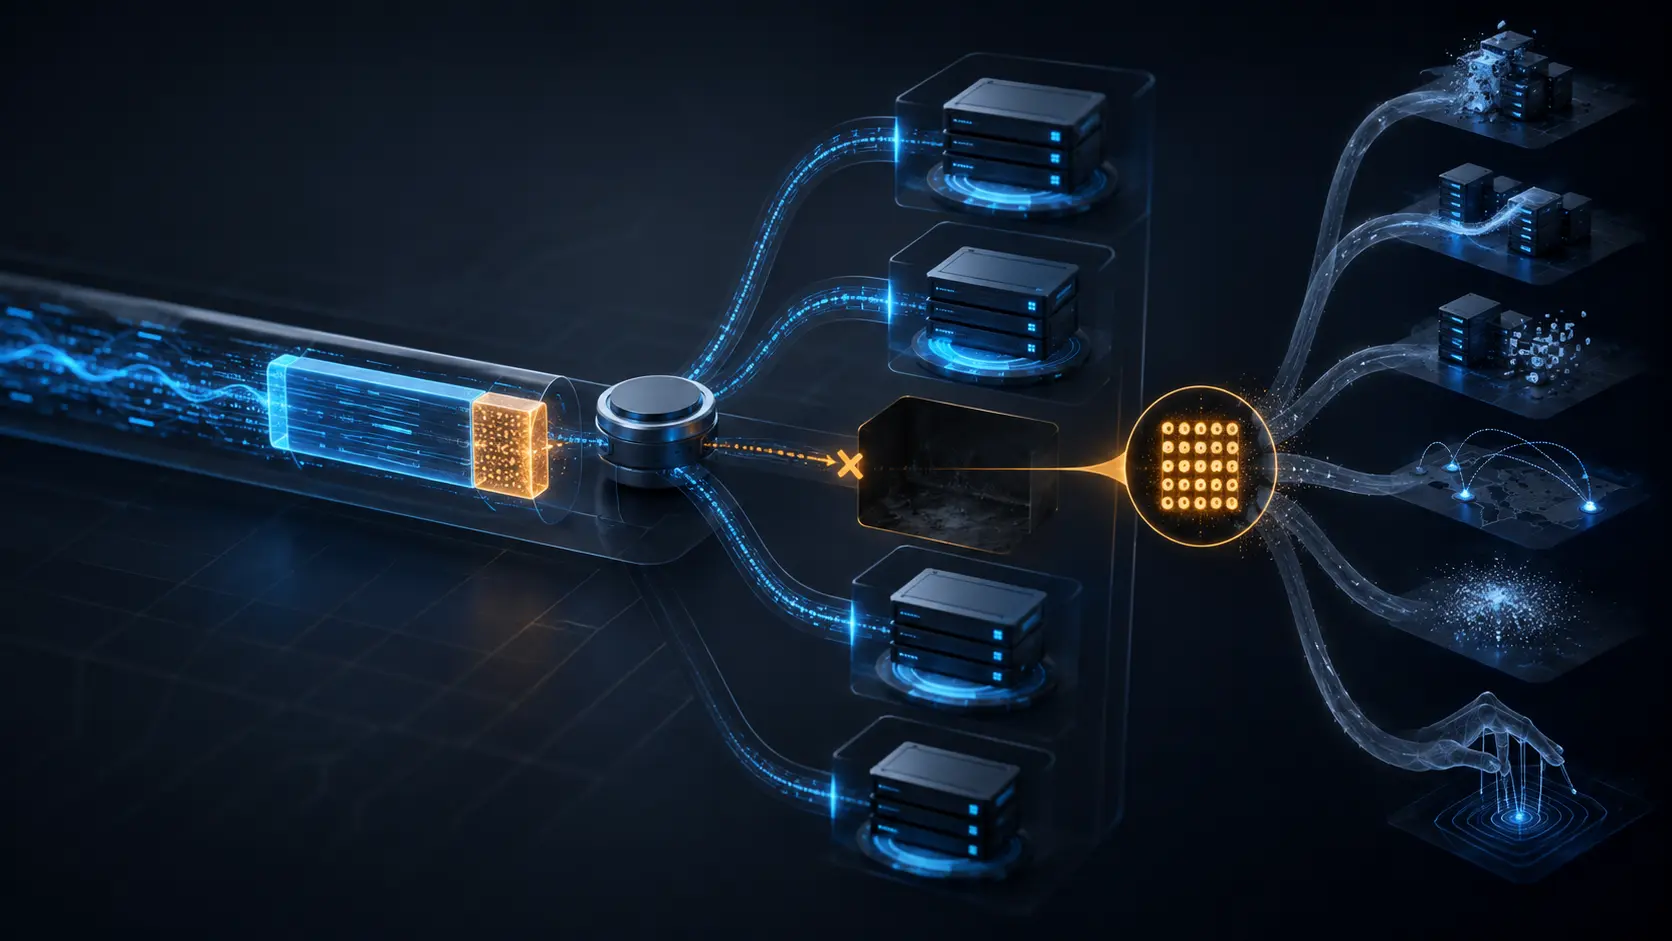
A load balancer shifts traffic between backends. Moments later a client receives a packet whose final bytes match a stateless-reset token and immediately abandons the connection. The signal is meaningful, but narrower than the incident label “server lost state”.
RFC 9000 §10.3 reserves Stateless Reset for an endpoint that cannot access connection state. Under QUIC v1's defined AEAD functions, a short-header packet smaller than 21 bytes is never valid and must be discarded. For a candidate datagram of at least 21 bytes, the receiver tests the final 16 bytes against tokens associated with active connection IDs. A match causes immediate teardown, but it neither authenticates the sender nor carries a reason code, backend identity or timestamp for the original loss.
The packet is deliberately shaped so it cannot be easily distinguished from an ordinary short-header packet. Size rules reduce loops and accidental disclosure, while random-looking bytes hide the signal from observers. That design also means a passive trace cannot safely label every similar packet a reset.
Section 10.3.1 permits deriving tokens from a static key and connection ID. That construction can help a routing tier generate a matching token without connection state, but the match alone does not reveal the key epoch, component that generated it, or whether a failover preserved connection state.
Section 10.3.2 makes collision handling a severe boundary: two connection IDs must not receive the same token, because a false match can terminate the wrong connection. Stateless Resets have no cryptographic protection. Security considerations in §21.11 further constrain token exposure and reuse, so a match alone cannot attribute an attack or rule out operational failure.
As an editorial operational recommendation, preserve an incident receipt containing observation time, address tuple, packet length and shape, CID and token fingerprints, matching sequence, issuing key epoch and backend, routing decision, last known good packet, deployment or failover events, and independent state-store evidence. The reset closes the connection; the joined evidence explains why.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance