
Summary
- Ofcom opened two separate investigations on 24 September 2026 into possible misuse of numbers allocated to Vonage Business Limited and Voxbone SA; neither opening notice makes a finding of breach.
- The underlying control question is whether customer checks, risk reviews and incident response remain accountable after a number leaves the original provider’s hands.
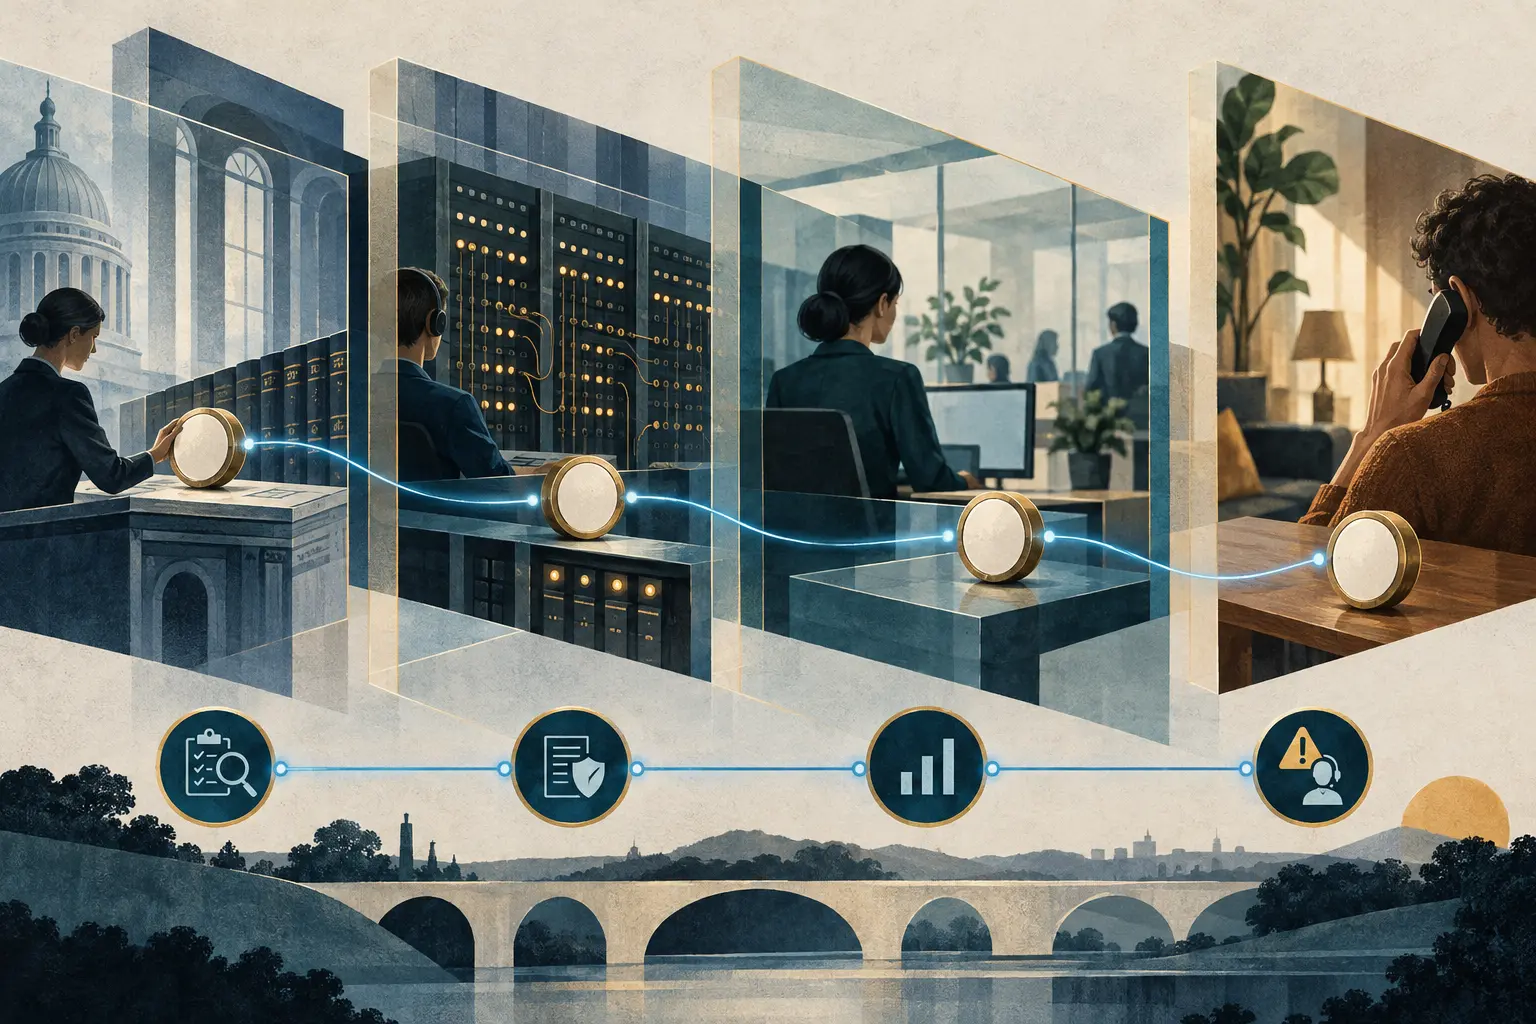
The credibility of a call can depend on a number that the recipient already recognizes. That makes a telephone number more than an address in a routing table: it is also a trust cue. Ofcom allocates numbers, usually in blocks, to communications providers, which may then transfer them to businesses or individuals. Each handoff creates a practical question: who still knows how the number is being used, and who can act when that use becomes suspect?
On 24 September 2026, Ofcom opened separate investigations into Vonage Business Limited and Voxbone SA. The regulator says it received information raising concerns about numbers allocated to each company being misused, including to facilitate scams. The case pages identify the same three General Conditions: B1.6, B1.8 and B1.9(c). They say the inquiries will establish facts and assess whether there are reasonable grounds to believe the rules were or are being breached. They do not identify the customers, number ranges, incidents or losses involved.
That absence matters: an investigation is a request for evidence, not a verdict about either company.
The three conditions describe related but distinct parts of the control surface. B1.6 requires a communications provider to secure that numbers allocated to it are adopted or otherwise used effectively and efficiently. B1.8 requires all reasonably practicable steps to secure that its customers use numbers in line with applicable numbering rules. B1.9(c) limits a transfer of use to numbers that will be used effectively and efficiently. The provisions do not say that a provider can hand a number to a customer and then forget it.
But they also do not convert the provider into a guarantor of every downstream act regardless of what it could know or reasonably do.
Ofcom’s 2022 Good Practice Guide makes the timeline more concrete. It separates checks before a transfer from continued compliance afterward and incident response. The right level of scrutiny depends on the relationship and intended use: a reseller asking for a large range may warrant different checks from a familiar business requesting one line. Additional requests can trigger renewed assessment. After transfer, the guide points to clear contractual terms, customer-specific risk reviews and monitoring proportionate to the risk. If a problem is reported, the response needs a path from signal to decision.
The guide clarifies the existing conditions; it is not itself an exhaustive statutory checklist.
That lifecycle makes the 2026 cases different in emphasis from the earlier BTW report on Ofcom’s Primo Dialler inquiry. The earlier story concerned a dialler firm and the alleged misuse of sub-allocated numbers. The Vonage and Voxbone notices put providers to whom Ofcom allocated numbers under scrutiny. The distinction is not a conclusion that one layer is more culpable. It is a test of whether safeguards remain legible across the chain, including where a provider’s customer may itself transfer or assign numbers.
Ofcom’s 2025 programme update had already described inquiries into Tismi and Primo Dialler; the 2026 notices add two more named cases, without announcing their outcomes.
For operators, the useful question is not whether a policy says “know your customer.” It is whether the records connect the customer, the requested number volume, the stated use, any further allocation, changing risk signals, complaints and the actions taken. A defensible file should show who reviewed the risk, when it changed, what options were considered and why access was continued, limited or stopped. Those are analytical evidence tests derived from Ofcom’s guide, not disclosed demands in these cases.
The balance is difficult. Weak checks can leave valid numbers available to callers who exploit the trust attached to them. A blanket response can interrupt legitimate services, misclassify unusual but lawful traffic or impose disproportionate monitoring. Ofcom’s guide calls for risk-based scrutiny and reminds providers to observe data-protection and investigatory-powers duties. That makes privacy, false positives and the route back to service part of the control design, not afterthoughts.
The cases are also distinct from caller-ID spoofing. Spoofing falsifies the number displayed to a recipient; Ofcom’s opening notices concern potential misuse of numbers allocated to the named providers. The public record does not yet reveal whether a particular scam call involved a genuinely allocated number, a transferred number, a false display, or a combination of mechanisms. Treating all scam calls as one technical problem would obscure the evidence Ofcom says it is gathering.
The next useful update will explain the chain, not just repeat the allegation: what numbers or customer relationships were examined, what controls the providers had, how risk was reassessed, and how reports were handled. Until those facts appear, the strongest conclusion is narrower. A number’s handoff is a control event; whether the control worked is still under investigation.
Sources
- Earlier BTW report on Primo Dialler
- Heng Lu Note 73 (editorial lens, not case evidence)
- General Conditions overview
- Vonage case page
- Voxbone case page
- Ofcom announcement: two separate investigations
- Phone and text scam enforcement programme
- Scams and caller-ID spoofing guidance
- Good Practice Guide on sub-allocated and assigned numbers
- General Conditions consolidated text (in force 8 April 2026)
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance