
Summary
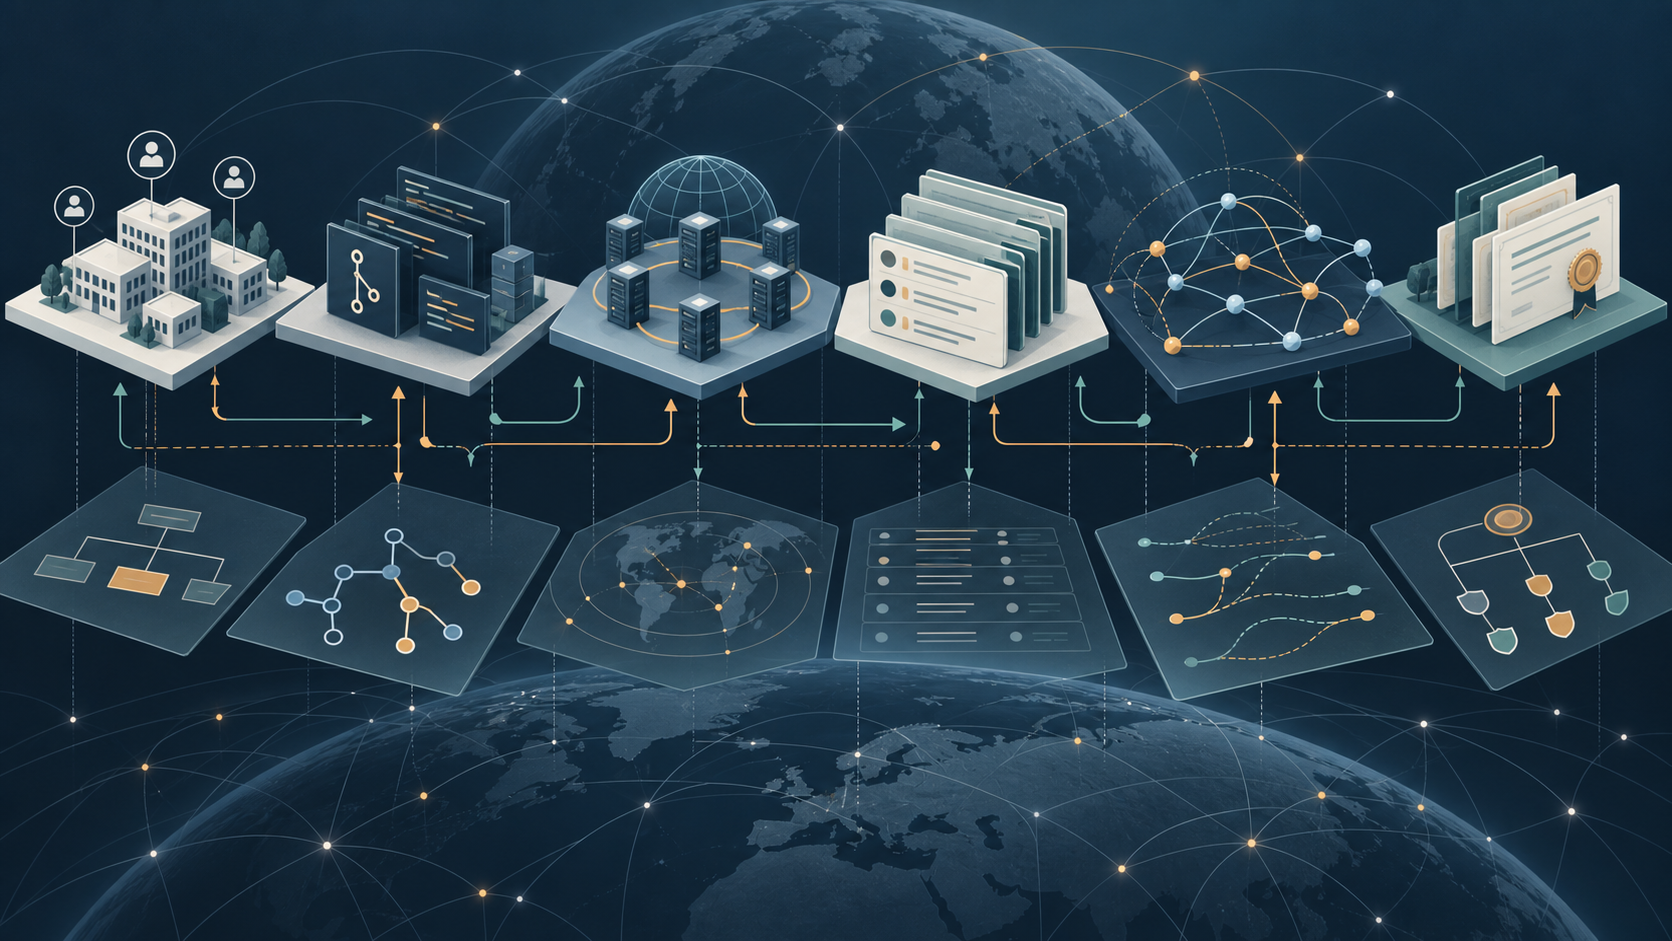
- ISC’s corporate identity, BIND and Kea stewardship, F-root operation, registry records and observed routing are separate control surfaces. A record in one surface does not automatically confer authority in the others.
- The practical accountability question is not who is named in a database, but which instrument permits a decision, who can challenge it, and which institution can correct, transfer or replace the relevant object.
The name is a clue, not a complete authority chain
Internet Systems Consortium appears in public infrastructure records in several roles. Its official materials describe a nonprofit public-benefit corporation focused on open-source Internet infrastructure software and services. ISC presents BIND 9 as a software project it stewards and maintains, and Kea as an open-source DHCP project associated with its engineering and support work. It also describes its role in operating F-root, one of the DNS root-server services listed by IANA.
Those descriptions establish useful organizational facts. They do not establish that ISC possesses one undivided authority over DNS policy, the root zone, Internet number resources, autonomous-system routing or every deployment of software carrying the BIND or Kea name. The distinction matters because each surface has a different source of authority and a different failure or remedy path.
The first analytical mistake is to treat the organization’s name as the connecting instrument. A corporate page can establish how an organization describes itself. It cannot, by itself, prove control of an autonomous system. A software project page can establish stewardship of source code and releases. It cannot prove that every operator using that software follows ISC’s instructions. A root-server listing can corroborate a service role. It does not disclose every contractual term governing that role or establish ownership of unrelated routing objects.
The authority chain must therefore be reconstructed one surface at a time.
Corporate identity supplies capacity, not every operational power
ISC’s “About” material is strongest as evidence of self-described institutional identity and mission. It places the organization in the category of an infrastructure-software developer and service operator. Its contact material can help correlate domains, public contacts and organizational representations. Neither source is a substitute for the registry or contractual instrument that gives effect to a particular operational decision.
That limitation is not a criticism of ISC. It is a basic feature of distributed Internet governance. A corporation may have the legal capacity to enter agreements, employ staff, hold assets and publish software without thereby controlling every external system that uses those assets. Corporate governance determines who can act for the corporation. It does not automatically determine who can edit a Regional Internet Registry object, authorize a route origin, change a root-zone delegation or compel an independent network operator to deploy a release.
For readers assessing accountability, this creates a simple test: identify the decision at issue, then identify the instrument that makes the decision effective. If the question is whether ISC may publish a BIND release, the relevant evidence is project stewardship and release practice. If the question is whether a route may be originated by AS210764, the relevant evidence moves to number-resource registration, routing authorization and observed routing state.
If the question is whether a root-server service is operated, the relevant evidence includes the operator’s public description, IANA’s root-server information and any applicable operational agreement.
A corporate identity can be present at the beginning of each inquiry without being the answer to each inquiry.
Software stewardship ends at the deployment boundary
ISC’s BIND and Kea pages support a software-stewardship role. They show that ISC is publicly associated with the development, maintenance or support of infrastructure software. That role can be consequential: upstream code, security notices, documentation and release processes influence what distributors and operators can deploy.
But the control boundary changes when software leaves the upstream project. A distributor decides how and when to package a release. An operator decides whether to test and install it. A service owner decides how to monitor production behavior and whether to roll back. A network team may operate a DNS or DHCP service without any direct corporate relationship with the upstream maintainer.
The result is a chain of dependencies rather than a single command structure. ISC may control the upstream publication of code or guidance while lacking direct control over the timing, configuration and recovery of downstream deployments. Public documentation can show that a fix was released; it cannot, without additional evidence, show that every affected operator received it, installed it or restored service successfully.
This distinction has a direct governance consequence. When a failure occurs, the responsible remedy depends on where control was lost. A project issue may be addressed through a release or advisory. A packaging issue may require a distributor response. A configuration problem belongs to the operator. A service outage may require an operational recovery process that is not visible in the upstream project record. Treating all four as “ISC’s control” would obscure the actual party able to act.
F-root is an operational role, not a universal infrastructure title
ISC’s F-root page supports a role in operating F-root infrastructure. IANA’s root-server information provides an independent descriptive reference for root-server identities and operator information. Together, these sources can corroborate that ISC is publicly associated with an important root-server service.
They do not turn F-root operation into a general title over the DNS root, Internet number registries or every network identifier associated with ISC. Root-server operation is a defined service role within a wider coordination system. Its authority is bounded by the technical and institutional arrangements governing root-server operation. The public listing explains what service is being identified; it does not necessarily expose the full agreement, governance structure, replacement mechanism or operational escalation path.
That boundedness is central to a fair assessment of institutional legitimacy. A service operator can be highly important without being sovereign over the surrounding system. Its authority may be real, technically significant and contractually defined while still depending on other institutions for coordination, delegation, allocation or dispute resolution.
What the RIPE record can establish about ISC-AGP1
The RIPE Database query for AS210764 is the appropriate public starting point for examining the relevant autonomous-system object, maintainer references, administrative fields, routing policy and related registry attributes. A registry object can provide evidence of what is recorded, who is named, which contacts are published and what policy statements are associated with the object at the time of inspection.
That is important evidence, but it is registration evidence. A database entry does not by itself prove that the named organization currently operates routers, originates a particular prefix, controls every route associated with the ASN or maintains a continuing production service. Registry data can be updated, transferred or corrected. Administrative identity and technical activity may diverge in time or in substance.
The proper conclusion is therefore narrow: a RIPE record can connect an identifier to a recorded organization and expose the administrative and policy claims attached to that identifier. It cannot, standing alone, settle current operational control or the legal relationship between the organization and every observed route.
RIPE NCC’s documentation describes the RIPE Database as a system for Internet number-resource and routing-related objects, with procedures for managing and updating records. That documentation is valuable precisely because it makes the remedy question visible. The relevant question is not only “what does the record say?” but also “who is authorized to change it, under what object-specific rules, and what happens when the record is disputed?”
Routing observation is behavior, not title
RIPEstat’s route-originations view can provide observations about prefixes associated with AS210764. Its API documentation explains how routing, ASN, prefix and related measurement data can be retrieved. These observations are useful for testing whether a route was visible from the measurement system and how the routing state changed over time.
Observed BGP behavior is not the same as corporate ownership. A route announcement may show that an autonomous system appeared as an origin in a given observation window. It does not, without more evidence, prove who operated the originating equipment, whether the announcement was authorized by the resource holder, whether the route was stable or whether the named organization controlled the surrounding network.
This is where RPKI adds a different kind of evidence. RPKI validation can show whether an observed origin is covered by a valid Route Origin Authorization, or whether the route is invalid or not found under the relevant data. That is cryptographic authorization concerning route origin. It is not a corporate identity system and does not explain every registry relationship.
The layers should be read together but not collapsed:
- The RIPE object records an administrative and policy representation.
- RIPEstat records observed routing behavior from available measurement vantage points.
- RPKI records cryptographic authorization by the holder of relevant number resources.
- Corporate and official pages describe the organization’s identity and public roles.
- Operational evidence would be needed to demonstrate who detects failures, changes equipment, deploys remedies and sustains service.
Agreement across these layers strengthens a bounded account. It still does not create a universal proof of control.
The remedy depends on the surface where the error occurs
The most useful addition to prior coverage is the remedy map. When identity, authorization and observed behavior diverge, the correction path depends on the type of divergence.
If the problem is an inaccurate RIPE Database field, the first route is the applicable RIPE Database management or update procedure, involving the relevant maintainer, account holder or responsible party. If a number resource is transferred through an organizational change, RIPE NCC’s resource-transfer and merger procedures become relevant. Those procedures explain how resources may be managed during transfers or mergers; they do not prove that any particular transfer involving AS210764 occurred.
If the problem is an unauthorized or incorrectly originated route, the response may involve the resource holder, the originating network, upstream providers, Internet Routing Registries, RPKI authorization and operational filtering. A valid RPKI authorization can constrain acceptable origin behavior, but it does not replace the administrative process for correcting an organization’s identity or contact details.
If the problem concerns F-root service operation, the relevant remedy is not a RIPE Database edit. It belongs to the operational and coordinating arrangements governing root-server service. IANA’s listing can help identify the service and operator context, but the public listing is not itself a complete dispute-resolution agreement.
If the problem is a BIND or Kea vulnerability, the remedy begins with the software-maintenance and disclosure process, then moves through distributors and operators. A patch can be authoritative as an upstream release while remaining ineffective on systems that have not deployed it.
The accountability principle is therefore procedural: send the dispute to the institution that controls the instrument capable of changing the disputed state. A corporate board cannot edit a registry object merely because the organization is named in it. A registry maintainer cannot guarantee that an operator installed a software update merely because the operator appears in a record. A route authorization cannot establish who holds a corporation’s legal authority.
A bounded conclusion about ISC-AGP1
The public evidence supports a layered description of ISC-AGP1 and Internet Systems Consortium, Inc. ISC is publicly associated with infrastructure software, F-root operation and a recorded network identity. RIPE records can establish what is registered about AS210764 and related identifiers. RIPEstat can provide evidence of observed routing behavior. RPKI can test cryptographic route-origin authorization. None of these sources, alone or automatically, proves a single institution-wide command over all of those surfaces.
The more defensible account is also more useful. ISC’s authority is real where a specific instrument gives it effect: project stewardship for upstream software, operational arrangements for F-root, and registry or routing mechanisms for number-resource and route-origin questions. The boundaries matter because they identify who can challenge a decision and who can repair it.
For network operators, lawyers and governance practitioners, the practical lesson is to preserve the chain of evidence. Record the exact registry object, observation window, authorization state, organizational representation and operational consequence. Then identify the institution empowered to change each state. That method avoids both overclaiming and underestimating the organization’s role.
The unresolved question is not whether ISC appears in several infrastructure systems. It does. The harder question is whether a particular decision can be traced from ISC’s institutional capacity to an effective control action, and whether an independent remedy exists when the record, authorization and live operation no longer agree. Public sources map that question clearly. They do not yet answer every operational detail.
Sources
- ISC About
- ISC Contact
- ISC F-Root
- ISC BIND 9
- ISC Kea DHCP
- RIPE Database query for AS210764
- RIPEstat route originations for AS210764
- RIPEstat Data API documentation
- RPKI resources
- IANA Root Servers
- RIPE Database services and documentation
- RIPE NCC resource transfers and mergers
- ISC-AGP1 directory entry
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance