
Topic
RPKI and Route Security
Within the Topic facet, RPKI and Route Security topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Story
LACNIC’s Security Demo Stops at Brazil’s Platform Border
At LACNIC 46, ASPA, delegated RPKI and incident reports shared one teaching deck. The member portals did not share one route.
IETF
The Link Fails. A Legacy Router May Keep the Redirect.
A revised FlowSpec draft gives routers a bit that ties a traffic detour to the life of a direct link. Its new deployment section admits the catch: a router that does not understand the bit must ignore it and may keep steering packets after that link is gone.
Story
RIPE Put the ROA Dashboard and Its Login Path on Two Clocks Again
On 3 November, both maintenance windows start at 21:00 CET. One is scheduled for ten minutes, the other for thirty. October's paired run shows why a member needs more than two completion stamps.
Leaders
Aftab Siddiqui Took the Bad ASN Out of APNIC's ROA Form
APNIC had told members not to put private or unallocated ASNs into route records. They kept appearing. Aftab Siddiqui's prop-150 moved the rule from advice into the registry's admission desk, with one deliberate exception: AS0.
Leaders
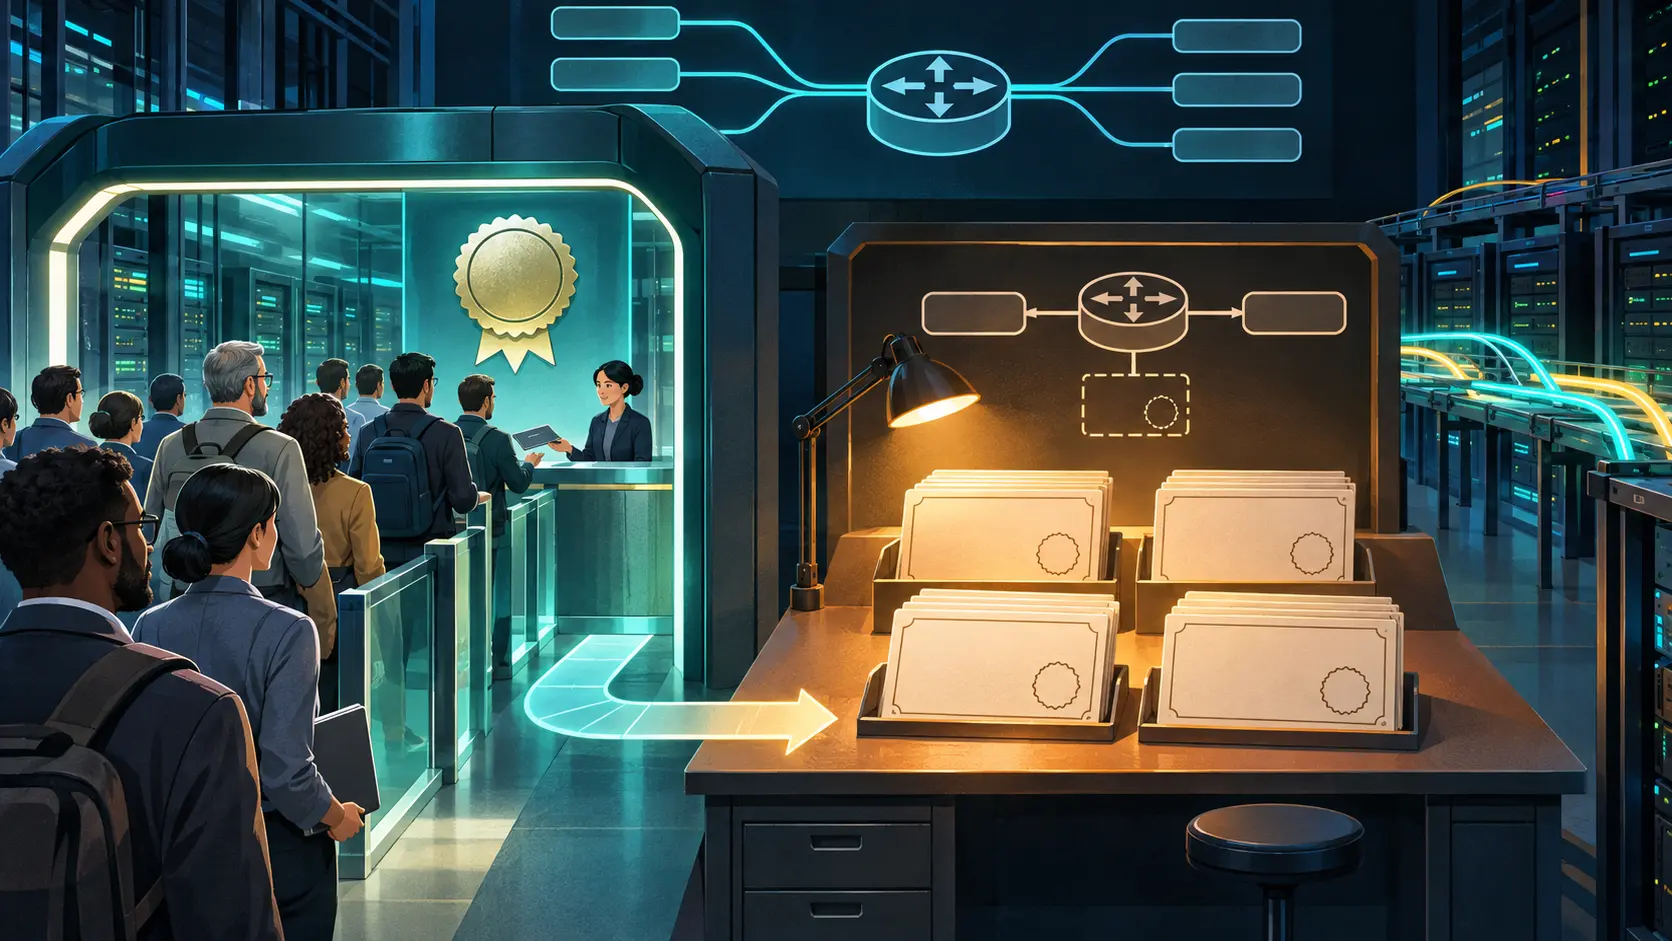
Nathalie Trenaman Put a Lock on the Door to the Locksmith
RIPE NCC wanted to reject invalid routes on its own network. Nathalie Trenaman had to answer the awkward question first: what happens when the member locked out is trying to reach the portal that fixes the mistake?
Story
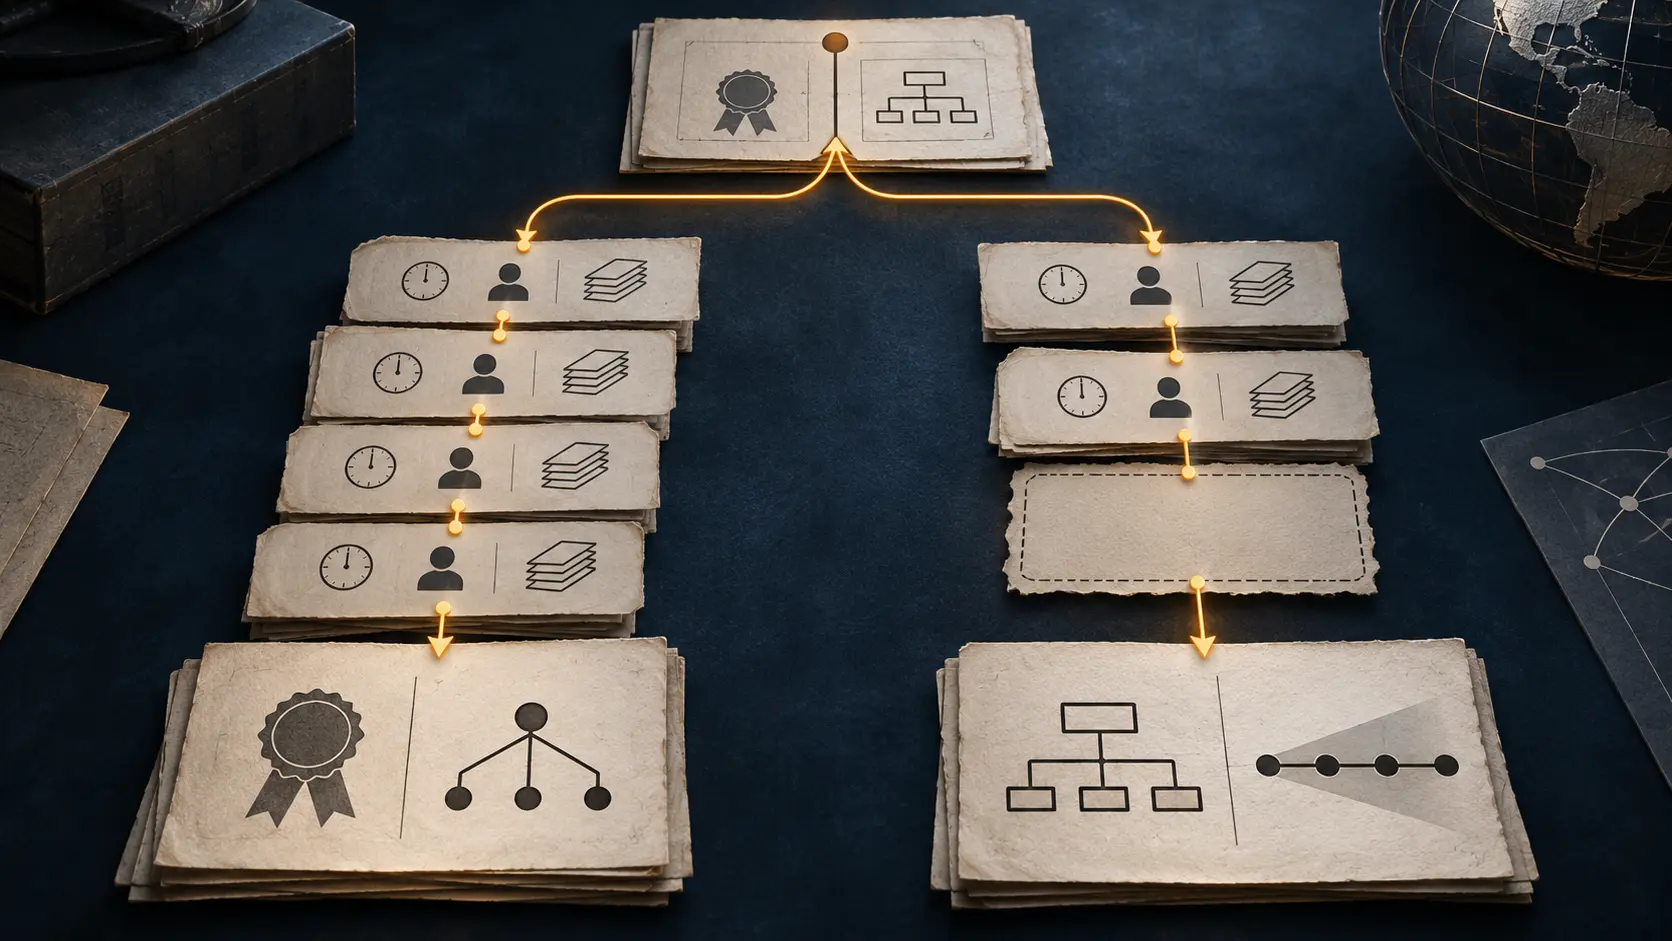
ARIN Enrolled 9,673 in RPKI. About 1,195 Hosted Orgs Had No ROA.
ARIN’s October routing-security presentation carried two different scoreboards. Registration climbed 27% in a year. Roughly one in seven organizations using its Hosted RPKI service had still published no route-origin authorization. The distance between those numbers is where a…
Story
ARIN Can Show Who Changed a ROA. The IRR Object Still Has No Matching Receipt.
ARIN gave a route-origin authorization a 365-day change history. An operator asked for the same trail on the routing-policy entity that can sit beside it. The request entered a roadmap and the public ticket closed, leaving incident responders to read the current entity while its…
Story
ARIN Closed the Request. The ROA Key Stayed at Org Level.
A resource technician asked for permission to fix route-origin records on the prefixes they manage. ARIN acknowledged the case, put it in an internal queue and closed the public suggestion. The organizational handoff remains the first step before the routing clock even starts.
Story
RIPE Lets PI Holders Manage ROAs on Screen. Its API Still Sends Them Away.
RIPE NCC gives sponsored resource holders a Dashboard for routing certificates and ROAs. Its automation interface refuses their certificate authorities. The promised replacement for an old, never-expiring key could finally bring those holders through the API door, but the public…
NANOG
RPKI Drops the Route. The Owner Gets No Receipt.
At NANOG 98, KAIST’s iROV proposal asks a pointed operational question: when origin validation rejects a route, why should the network that owns the prefix learn nothing about where the route died or what it cost?
Leaders
Daria Shantalova: The BGP Community Was Valid. The Route Still Had No Pass.
At RIPE 93, Daria Shantalova traced an internal backbone failure to a filter that trusted a permitted community but never checked whether each prefix was authorised at that boundary.
Leaders
MANRS Wants a Valid ROA for Every Route. Legacy Networks Will Test the Rule.
At RIPE 93, Andrei Robachevsky described a proposed RPKI floor for network operators. The hard part sits beyond the router: who can publish the authorization for a legacy or customer-held prefix?
Story
RIPE Found 37% of ROA Definitions Off BGP. Who’s Cleaning Up?
RIPE NCC says about 37% of AS-prefix definitions in ROAs were not seen in BGP. Some are deliberate backups. Others may be old permissions that outlived the route, and the incentive to create them is stronger than the incentive to retire them.
Europe and Middle East Institutional
Netnod Runs a Nordic Exchange and I-root. Its Registry File Says It Is a Membership Row.
Netnod Runs a Nordic Exchange and I-root. Its Registry File Says It Is a Membership Row. intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…
Story
APNIC’s China ROA Score Clears 80%. Its Q2 Report Says 68%.
One APNIC Executive Council packet gives China two first-half ROA endpoints: above 80% in the Director General’s update and 68% in the attached Q2 report. The higher figure has no stated measurement date or denominator.

Story
Two Upstreams, Two Clocks: Multi-Homing Speeds the Rescue and Delays the Cutoff
A RIPE 93 measurement found that extra upstreams helped a route recover faster after its ROA became valid, but kept it reachable longer after the ROA turned it invalid. The same spare path can be a rescue line in one direction and an unwanted encore in the other.
IETF
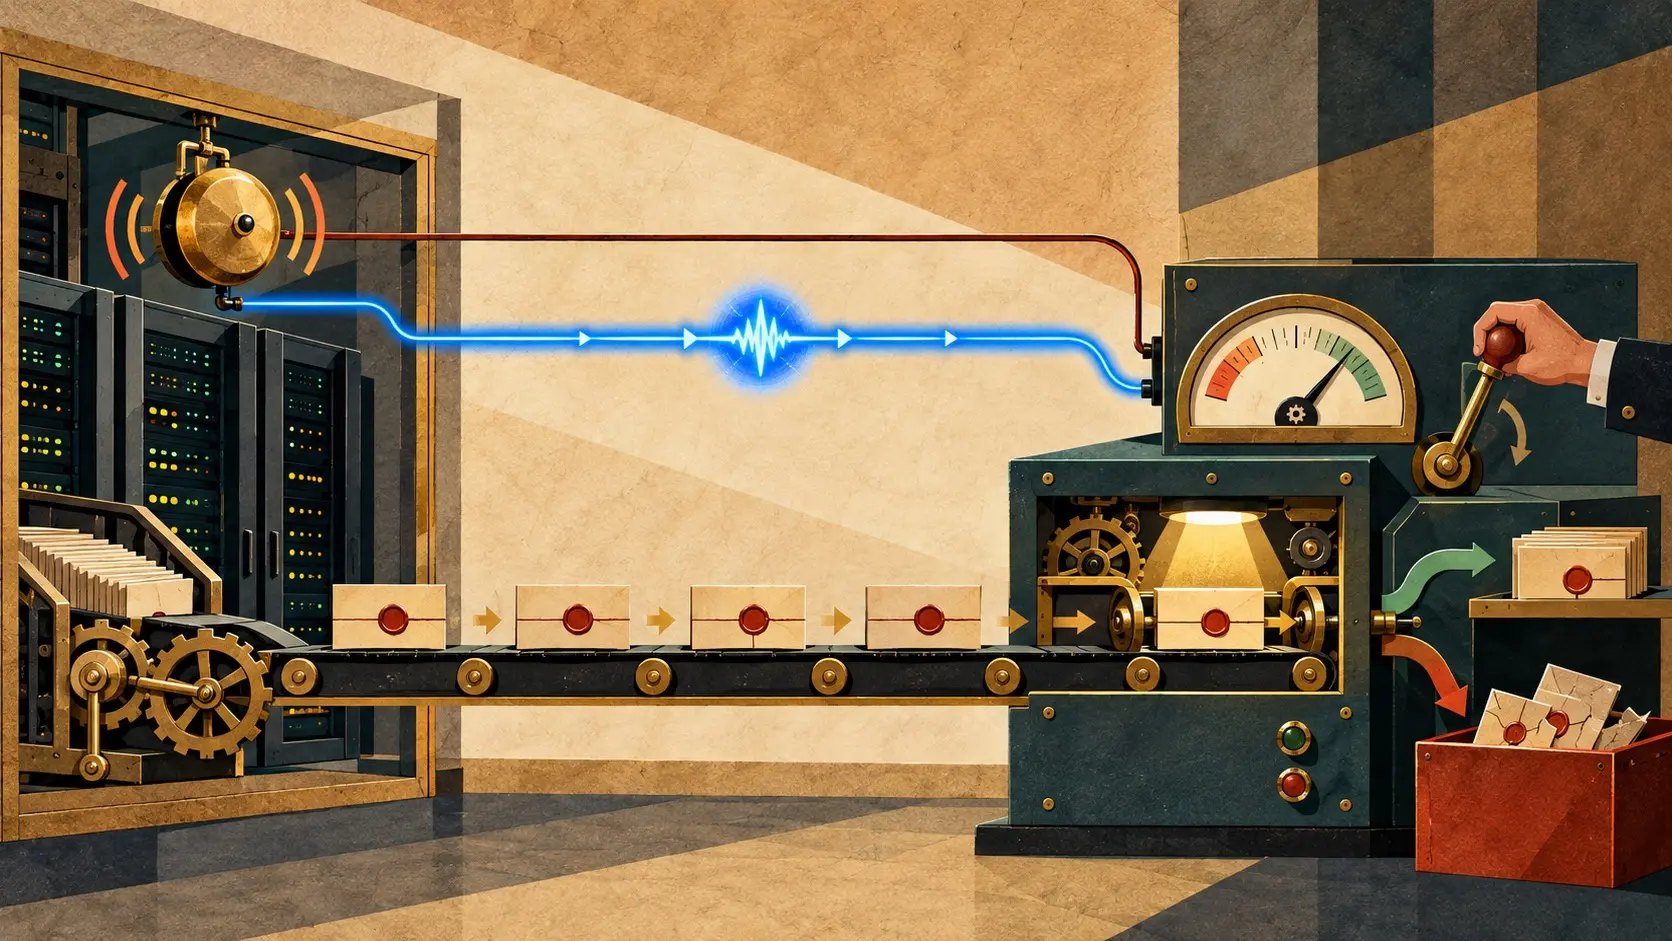
RPKI's New Push Alarm Rings. The Data Still Takes the Slow Lane
A 28 October Internet-Draft promises faster delivery of route-security changes. Its urgent message contains a serial number and a warning, while the packet that actually carries changed data runs on a negotiated schedule. The existing RTR protocol already has an unsolicited…
Story
The Security Budget Said No. APNIC Opened the Workshop Door
One APNIC 62 entity said commercial security tools were beyond the reach of many subsidiaries. APNIC’s answer begins in a classroom, then branches into training, member assistance and network monitoring.
Story
RIPE’s ASPA Lists May Miss Up to 9% of Provider ASNs. The Signature Still Checks.
RIPE NCC’s preliminary analysis has found missing upstreams in signed routing declarations. A neighbour labelled “peer” can carry traffic like a provider; the holder can faithfully sign the wrong list.
Story
BGPsec Key Rotation Takes Five Acts. RIPE NCC Has Published Its First API Certificate
BGPsec Key Rotation Takes Five Acts. RIPE NCC Has Published Its First API Certificate intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…