
Summary
- RFC 3041 addressed a narrow IPv6 privacy problem: a link-layer-derived interface identifier could remain visible in addresses even after a device moved to a new network prefix.
- Temporary addresses could make straightforward address-based correlation harder, but they did not hide the prefix, erase application identifiers, or make a host anonymous.
IPv6 Stateless Address Autoconfiguration (SLAAC) let a host form an address from information available locally and a prefix advertised by a router. In the address architecture RFC 3041 discussed, the prefix described the network location; an interface identifier filled the remaining part. Early interface identifiers could be derived from an IEEE or link-layer identifier. If that value stayed constant, changing the prefix changed the address but preserved a recognizable component.
That mattered because an address travels in packet headers. The payload could be encrypted while a visible source address still helped an observer join transactions. A laptop might appear on different networks with different prefixes, yet an identifier embedded in each address could suggest continuity. RFC 3041 treated that as a correlation risk—not proof that the observer had identified a person, or even that every device used the same generation method.
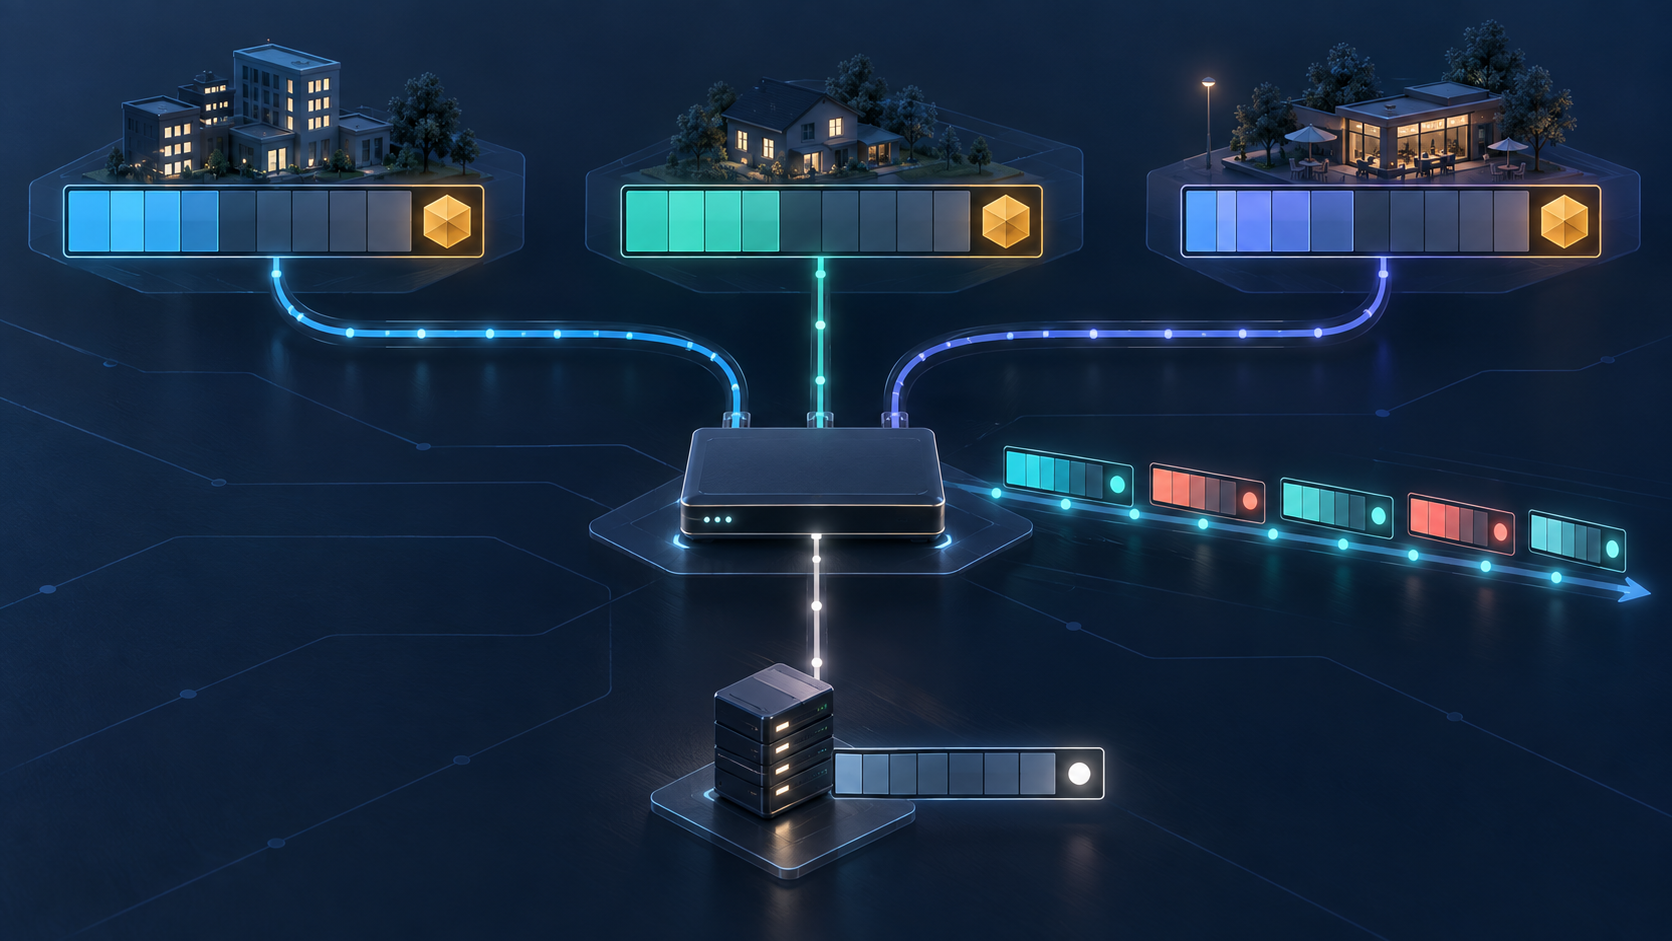
The proposal did not replace SLAAC with a new addressing system. It added temporary global-scope addresses alongside ordinary addresses. For outgoing connections, a host could prefer a temporary source address. A stable address could remain useful for a machine that accepted incoming connections, appeared in DNS, or needed an address that administrators and applications could recognize. This two-address model made source selection the operational hinge: privacy-oriented outbound use and stable inbound reachability were different jobs.
RFC 3041 described randomized interface identifiers derived from changing history state, then used them to construct temporary addresses for advertised prefixes. Its suggested defaults were a preferred lifetime of one day and a valid lifetime of one week, subject to user or implementation policy and the prefix's own lifetimes. A replacement could be generated before the old address was deprecated. A deprecated address could remain valid for an existing connection, while new connections should use a preferred address. Rotation therefore meant managing overlapping address states—not changing the source on every packet.
The design targeted a specific join key: reuse of the same address component across separate transactions. It did not remove the network prefix, which could still reveal topology or group activity by location. Nor did it change DNS names, cookies, account logins, application behavior, traffic timing, or other identifiers. A server could still recognize a logged-in user; an on-path observer could still compare traffic patterns. A temporary address could also be revealed by communication and remain usable during its valid lifetime. Less address reuse is not the same as anonymity.
The separation between temporary and stable addresses also imposed costs. Rotating sources complicates packet-trace attribution, access-control lists, reverse-DNS expectations, troubleshooting and some long-lived connections. An application may need a stable destination identity, while an administrator may prefer predictable logs. RFC 3041 therefore left room for applications, implementations and trusted administrators to affect whether temporary addresses were used. The network did not make that choice for every application.
Its history is a sequence of revisions, not a claim that the 2001 details remain current. RFC 4941 obsoleted RFC 3041 in 2007; RFC 8981 later obsoleted RFC 4941 in 2021. The current line retained temporary-address generation while revising algorithms and guidance. RFC 7217 and RFC 8064 address a related but different choice: stable interface identifiers that are not simply exposed hardware identifiers. A temporary address changes over time; a stable opaque identifier can vary across networks yet remain stable within one network.
RFC 3041's lasting question was not “Can IPv6 addresses be made private?” It was more precise: when a network prefix changes, what else in the address continues to make activity linkable, and who controls which source address an application presents? Temporary addressing narrowed one observation window. It did not settle identity, reachability, or every other way of correlating a device.
Sources
- RFC 3041 — Privacy Extensions for Stateless Address Autoconfiguration in IPv6
- RFC 4941 — Privacy Extensions for Stateless Address Autoconfiguration in IPv6
- RFC 8981 — Temporary Address Extensions for SLAAC in IPv6
- RFC 7217 — Semantically Opaque Interface Identifiers
- RFC 8064 — Recommendation on Stable IPv6 Interface Identifiers
- RFC 7721 — Security and Privacy Considerations for IPv6 Address Generation
- RFC 4862 — IPv6 Stateless Address Autoconfiguration
- RFC 4861 — Neighbor Discovery for IPv6
- RFC 6724 — Default Address Selection for IPv6
- RFC 4291 — IPv6 Addressing Architecture
- RFC 7934 — Host Address Availability Recommendations
- RFC 7258 — Pervasive Monitoring Is an Attack
- RFC 2464 — IPv6 over Ethernet
- RFC 7841 — RFC Streams, Headers, and Boilerplate
- RFC Editor information page for RFC 3041
- RFC Editor information page for RFC 4941
- RFC Editor information page for RFC 8981
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance