
Summary
- The IOTOPS IoT DNS guidelines draft, revision 06, updated 2 November 2026, remains an Internet-Draft in working-group revision. Section 4.3 identifies excessive DNS queries despite record TTLs and predictable, fixed-interval queries for the same names as separate device behaviors.
- A manufacturer's authoritative-zone TTL controls how long an answer may be reused. The draft tells manufacturers to balance query load against management-server changes; device caches must process records according to TTL unless configured minimum or maximum cache values apply.
- When critical domains require periodic revalidation, the draft says the interval should be non-deterministic. On resolution failure, devices should back off; RFC 9520 limits repeated queries to one server and requires at least one second of failure caching.
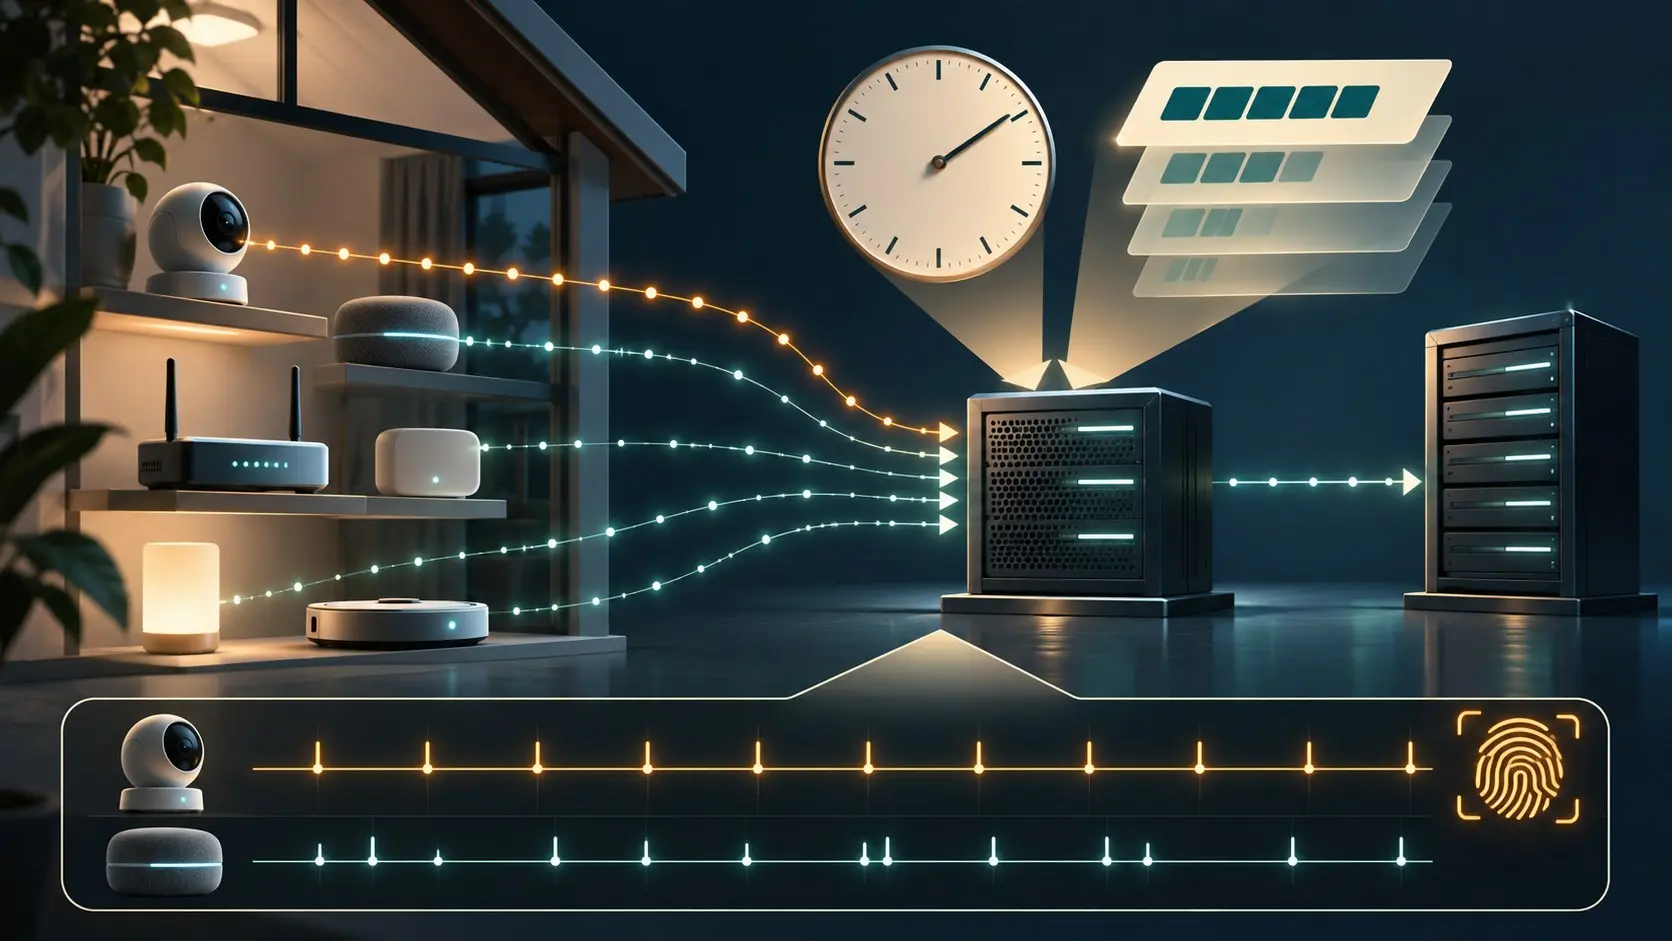
Imagine a fleet of cameras checking the same management name every sixty seconds, whether the DNS answer has a short or long lifetime. A network observer sees the beat; a firmware update changes it to every ninety seconds. The observer can now sort devices by timing without reading a product label. This is a hypothetical test of the draft's risk mechanism, not a measured fleet or a claim that either interval identifies a real model.
The draft is concerned with the DNS stub resolver built into a device and the management zone run by its manufacturer. Those two components hold different clocks. A DNS record's TTL, as defined in RFC 1035, is the answer's permitted cache lifetime. A device may also have a business reason to recheck a critical management domain. A failed resolution introduces a retry and backoff clock. A vendor that collapses all three into one timer creates unnecessary traffic and a remarkably legible behavior pattern.
A regular heartbeat can become a product label
Section 4.3 describes devices issuing fixed, highly predictable queries for the same domains regardless of TTL or operational change. The draft links that behavior to fingerprinting risk: an observer profiling query timing may distinguish models or firmware versions. The same repeated traffic burns power on constrained devices and consumes resolver capacity. A clean-looking cron schedule on the manufacturer's side becomes an invitation to classify the installed fleet from the network side.
The authoritative zone is part of the problem. If the manufacturer sets a TTL too low, devices ask more often than needed. Too high a TTL can delay a management-server address change or software-update path. The draft requires the manufacturer to choose TTLs appropriate to each record's use. Devices should cache responses when their resources permit. When they cache, they must expire or otherwise process records according to TTL unless explicitly configured bounds apply. Minimum and maximum cache settings, where supported, should be manageable rather than burned into firmware.
A record cannot govern device behavior if the device treats it as decoration.
Sometimes a management name really does need a periodic fresh look. The draft permits that requirement, then asks for non-deterministic spacing between repeated checks. The manufacturer must also account for the legitimate bound: randomizing the interval should not leave a device indefinitely attached to an obsolete management address. The useful test is a scheduled address change: record the old answer's TTL, the cache's expiry, the next query and the first successful connection to the new endpoint. The observation has to include actual device traffic, not merely a configuration file that says “jitter enabled.”
Failure is a second test. When a resolver stops answering, a fixed timer can turn every device into a synchronized retry engine. The draft calls for backoff and points to RFC 9520: the same query to the same server address over the same transport cannot be retried more than twice before treating that address as unresponsive, and a resolution failure must be cached for at least one second. RFC 8767 offers a separate option for serving previously valid stale data under certain failures. The operator needs to know whether a device is using a cached answer, retrying a failed lookup or receiving stale data from a resolver. All three can keep a screen green for different reasons.
The manufacturer's timer reaches into the operator's network
The draft also says the device's DNS resolver must be configurable through applicable network protocols or authorized management, and must not fall back to a hard-coded public resolver. It recommends manual configuration first, authorized device management next, then network-provided configuration. That order matters when a local operator needs to move DNS service or inspect the traffic burden. An undocumented public fallback would export the device's queries and bypass the operator's resolver policy just when a failure makes them most urgent.
The proposed guidance does not provide a measured fingerprinting success rate, a fleet census or a power-loss figure. A packet capture from controlled devices across firmware versions, TTL changes, management cutovers and resolver failures would establish the actual timing signature and its operational cost. Until then, the draft's useful instruction is concrete: manufacturers should stop treating DNS as a metronome. Publish a sensible TTL, cache it correctly, vary necessary rechecks and back off when the resolver fails. The device should follow the authority of the answer while leaving as little rhythm as its job permits.
IOTOPS draft · RFC 1035 · RFC 9520 · RFC 8767
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance



