
Summary
- The IAB’s 24 August statement gives policymakers a serious architectural test: minimise disclosure, prevent cross-site linkage and central stores, protect encryption, preserve interoperability and avoid premature lock-in.
- A public mandate-to-mechanism record should separately name who defines the lawful outcome, advises on architecture, issues and verifies the signal, controls retained data, audits performance and provides correction and redress.
The citation chain that hides authority
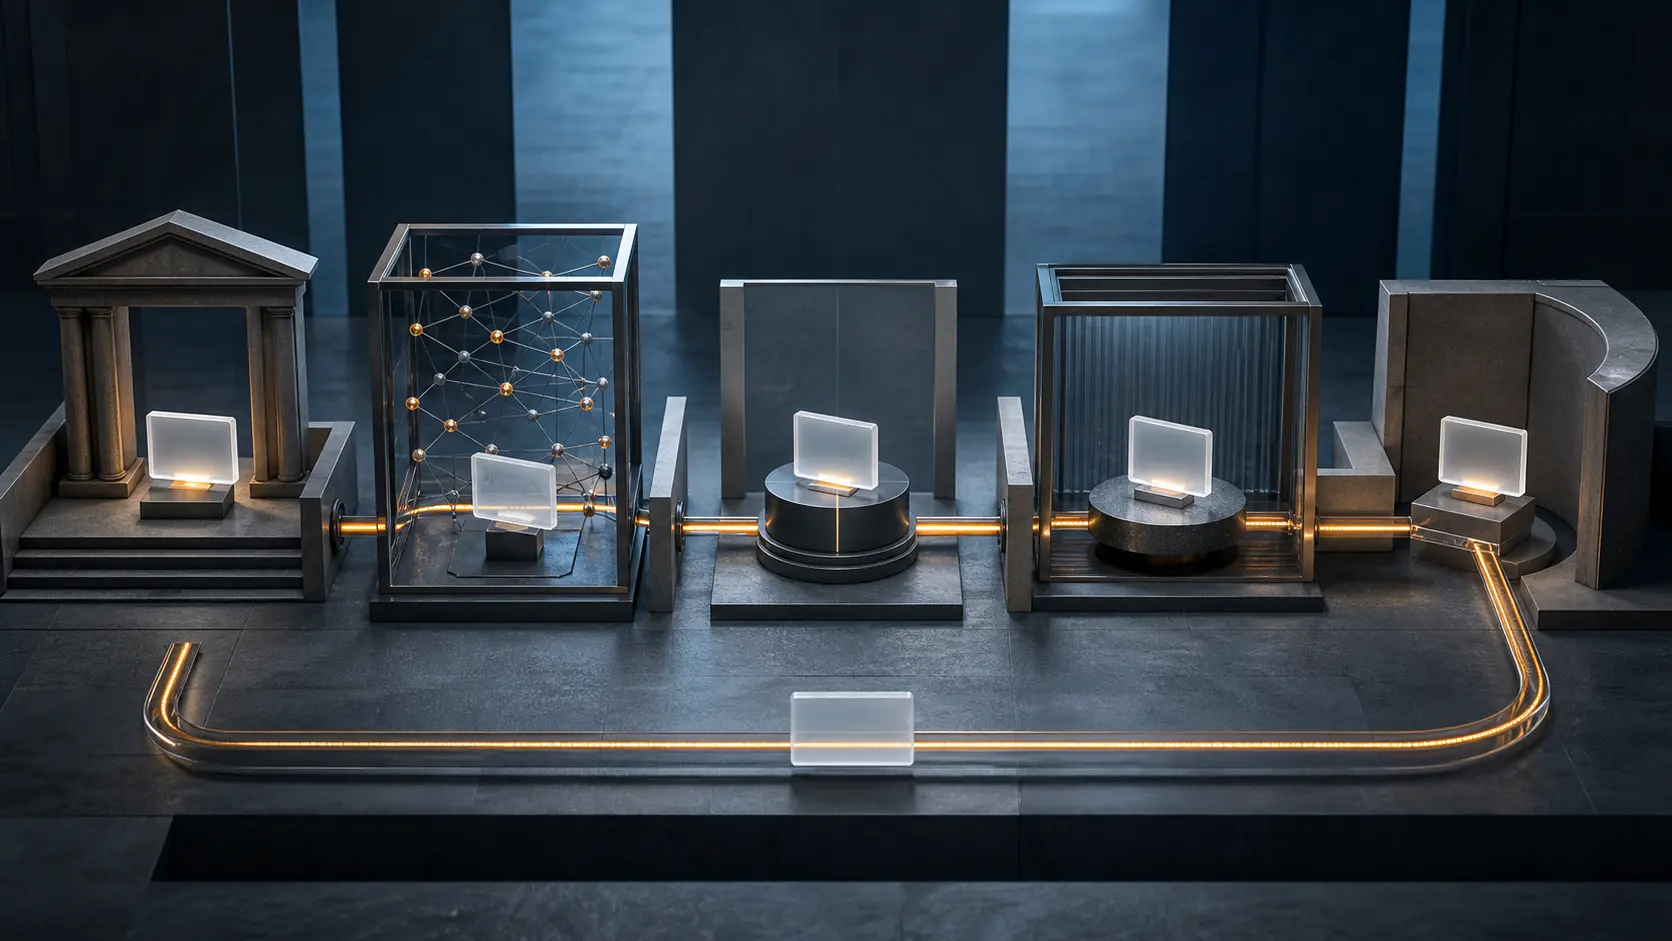
An age check is often discussed as a product feature. In governance terms it is a chain of decisions. A public institution defines which people, content, functions and jurisdictions fall within a rule. An architecture body identifies properties that an implementation should preserve. An issuer establishes an age attribute. A device, browser or service presents and verifies a signal. A regulator assesses compliance. A person needs somewhere to challenge a false result.
These are at least five control surfaces: law, architecture, implementation, assurance and redress. Collapsing them into “the solution” makes authority easy to misstate. Law appears to implement itself. A vendor’s design appears legally inevitable. A service treats outsourcing as a transfer of responsibility. A technical recommendation is cited downstream until it sounds like approval of a coercive outcome.
On 24 August 2026, the Internet Architecture Board published its Statement on Age-Based Restrictions and Online Safety. It begins with a point that should not be discarded: the IAB shares the aim of protecting children and recognises the urgency families and policymakers feel. It then warns that current proposals can concentrate sensitive information, reduce privacy, pressure encryption, encourage hazardous circumvention, entrench gatekeepers and fragment access across jurisdictions.
That is architecture advice doing necessary work. It reveals system costs before procurement, certification and compliance deadlines turn them into dependencies. It is not a statute, regulatory order or judicial finding. Saying so does not diminish the statement. It identifies the evidence it supplies and the decisions for which other institutions remain answerable.
Seven properties are not a product approval
The IAB describes seven properties for a workable mechanism. It should reveal no more than a purpose-specific age signal, report no user activity, prevent signals from being linked across sites, hide visited sites from the party that established age, avoid a central store of sensitive information, avoid other significant harms or burdens and operate through open interoperable interfaces developed in a multistakeholder process.
Together, those properties draw an architectural boundary. They do not certify a provider, prove a deployment, select a legal threshold or demonstrate that one intervention makes children safer. A system can offer a binary answer and still fail on a shared device. It can publish an interface while making issuers practically impossible to replace. It can hide a name from a website while excluding people who lack accepted identity documents. It can achieve laboratory accuracy and offer no usable correction when deployed.
The statement calls mechanisms built into an end user’s device the most promising at current maturity. The qualification matters. Promising is not complete, and being on a device is not the same as being under the user’s control. The IAB expressly acknowledges the leverage that device and operating-system vendors would gain. It also identifies robust multi-user support on shared devices as necessary.
Moving a check from a specialist server to a handset may reduce some disclosure and correlation risks. It may also move dependency toward mobile platforms, app distribution, hardware trust roots, account recovery and update policies. Governance improves when that move is recorded as a transfer of control. It weakens when the intermediary is said to have disappeared merely because it changed form.
The IAB has a real, bounded mandate
RFC 2850 gives the IAB architectural oversight and long-range technical responsibilities. That makes it a relevant adviser when a public rule affects encryption, naming, routing, application interfaces or the Internet’s end-to-end properties. The same charter does not make the Board a legislature, identity authority, sector regulator or court.
The boundary cuts both ways. Policymakers cannot reduce architecture to an implementation detail settled after the political decision. A rule can be lawfully adopted and still create surveillance, concentration, security and fragmentation risks. Technical expertise is not a veto, but those consequences are evidence about whether the intervention can achieve its purpose proportionately.
Architecture bodies should likewise resist having competence converted into implied public mandate. RFC 9998 reports a joint IAB and W3C workshop. Its technical experts, child-safety specialists, civil-society participants and policymakers can expose trade-offs. Their meeting does not authorise coercive scope on behalf of children, parents, schools, online services or national electorates.
The legitimate chain therefore has two independent tests. Policy must originate with an institution authorised to define the outcome and accountable for rights, proportionality and enforcement. The mechanism must also survive scrutiny for privacy, security, resilience, interoperability and circumvention. Passing either test cannot waive the other.
The European design exposes the remaining joins
The European Commission’s age-verification blueprint shows that public policy and data minimisation need not begin as enemies. Its published flow allows a person to obtain proof from recognised sources and later present an anonymous age proof to an online service. The Commission says the link between user and proof provider is cut after issuance, the service receives no identifying information and the issuer does not learn where the proof is used.
Those are important design claims. The Commission also says the solution became feature-ready in April 2026, can be customised by Member States and market participants and supports implementation of the Digital Services Act. It plans an EU Age Verification Scheme with a governance and trust model and lists of trusted proof providers and solutions.
The public object is therefore larger than open-source code. Someone must decide who may issue a trusted proof, who validates an implementation, how national versions remain interoperable, how a provider enters or exits the trust framework and how a user corrects an error in the underlying source. Published code improves inspectability. It does not allocate those authorities.
Ofcom makes a related allocation explicit. It says regulated services remain responsible for highly effective age assurance even when a third-party vendor performs the work. Its framework looks for technical accuracy, robustness, reliability and fairness, while treating privacy and data-protection compliance as mandatory rather than a trade-off.
That rule prevents outsourcing from dissolving responsibility. It does not remove a service’s dependence on an issuer it cannot govern, a mobile platform it cannot quickly replace, evidence methods accepted by the regulator or data held under a different legal regime. The public needs to see both the responsible service and the dependencies that constrain its options.
Blocking creates another principal
The IAB also examines an alternative in which networks block services that do not perform age assurance. It warns that identifying targets can require traffic visibility, put pressure on encryption and fragment access when jurisdictions impose incompatible duties. RFC 7754 provides the wider technical context for blocking and filtering.
The governance conclusion is not that a network can never execute a lawful order. Intervention adds another principal and another set of failure modes. Who identifies the target? Who translates an order into an address, name, application or traffic rule? How are shared infrastructure and overblocking handled? Who can suspend an erroneous rule? How does a user learn why access failed? Where can a misclassified service appeal?
Calling the act compliance does not answer those questions. Calling it technical implementation does not remove the public power exercised at the point of denial. If an operator can affect unrelated resources or expose protected traffic characteristics, it needs a bounded mandate, an inspectable record and a correction route proportionate to that power.
The missing joined record
The checked sources contain principles, specifications, regulatory criteria and deployment reporting. They do not form one joined record showing how a particular public mandate becomes a particular signal in a particular service. No misconduct follows from the absence. Institutions publish for different purposes, and a sensitive system should not expose identities, histories or security secrets.
A compact mandate-to-mechanism record could connect the chain without building another identity database. For each material deployment, it should state:
- the lawful outcome owner and legal basis;
- the population, content or function, jurisdiction, threshold and exceptions in scope;
- the architectural adviser and the status of its advice;
- the exact signal requested and disclosures expressly prohibited;
- the permitted issuer, wallet, device, browser, verifier and service role classes;
- the controller and retention boundary for every retained record;
- evidence for accuracy, robustness, reliability, fairness, accessibility and security;
- interoperability requirements and the path for switching provider or platform;
- the audit owner, review date and published performance measures;
- correction and appeal routes for users and services; and
- expiry, suspension and supersession state.
The record must never contain a child’s identity, browsing history, reusable credential, biometric template, document image or security secret. Its purpose is not to reveal who passed. It is to show that every institution around the gate acted within a visible role.
Urgency requires governed transition
The strongest objection to architectural caution is time. Children face harms now. Families can reasonably reject a standards timetable that treats present exposure as an abstract cost. The IAB recognises that urgency.
The answer is to govern transition rather than abandon the architecture test. An interim measure can be narrow, time-limited, independently measured and equipped with a sunset or replacement trigger. A regulator can require outcomes while allowing better mechanisms to enter. A service can deploy controls while publishing error and appeal evidence. Standards bodies can distinguish properties available now, features still experimental and dependencies that threaten lock-in.
The IAB warns about ossification: weak systems become difficult to dislodge after incentives and dependencies grow around them. This is not merely an engineering preference for elegance. Once governments certify providers, services integrate interfaces, platforms mediate credentials and enforcement relies on those connections, replacement becomes an institutional negotiation. The lasting cost of a weak design is not only the first deployment. It is the coalition that later benefits from continuity.
Sources
- IAB Statement on Age-Based Restrictions and Online Safety
- IETF announcement archive copy of the IAB statement
- RFC 9998: Report from the IAB/W3C Workshop on Age-Based Restrictions on Content Access
- RFC 2850: Charter of the Internet Architecture Board
- RFC 7754: Technical Considerations for Internet Service Blocking and Filtering
- RFC 8890: The Internet is for End Users
- The EU approach to age verification
- Blueprint for an age verification solution to help protect minors online
- Ofcom: Age assurance duties under the Online Safety Act
- Ofcom: Use of Age Assurance Report 2026
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance