
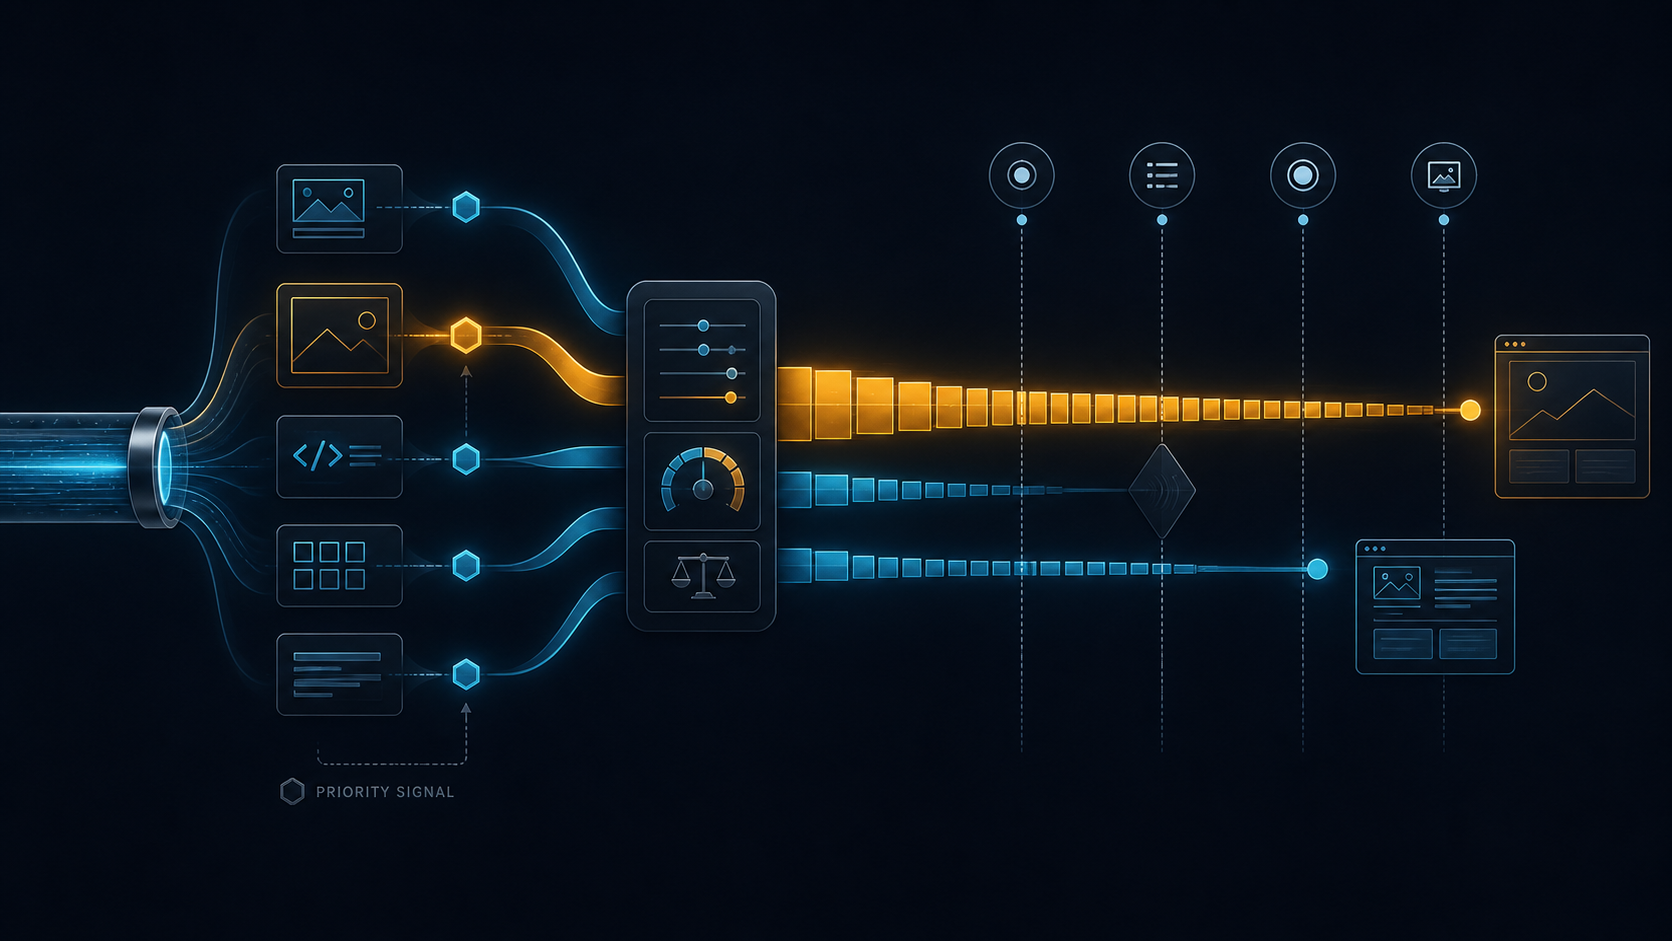
Summary
- RFC 9218 makes HTTP priority a suggestion and one input to scheduling; it does not guarantee processing, transmission or completion order.
- A defensible rollout record must connect the signal seen at each hop to merge policy, scheduler state, byte allocation, timing and the user-visible result.
Imagine a shared delivery edge serving a page, a critical stylesheet and several images. The browser marks the stylesheet u=0. A dashboard records the header and declares that the critical resource was protected. Yet the edge combines a response-side signal from the origin with local fairness and capacity rules. A smaller image finishes first, while the stylesheet waits for origin work. Nothing in the captured header proves the order that the dashboard has claimed.
This is a hypothetical operating case, not a report about a named provider. Its value is the separation it forces. The client can express a preference. An intermediary can preserve, consume or add to that signal. An origin can express its own view. A scheduler can combine those inputs with information that never appears in the header. The wire value and the delivered result are related, but they are not the same fact.
RFC 9218 defines an extensible prioritization scheme for HTTP responses. The Priority header field carries an end-to-end signal. HTTP/2 and HTTP/3 PRIORITY_UPDATE frames can carry initial or changed priority information on one hop. Both use structured priority parameters, but their scopes differ. A trace that shows a header at the browser does not prove which frame reached an upstream hop or which values entered the final scheduler.
The initial parameters are deliberately small. Urgency, u, ranges from 0 through 7; a smaller value means higher precedence and the default is 3. Incremental, i, says whether partial chunks can provide useful output and defaults to false. These values describe an endpoint’s view. They do not define a universal queue, bandwidth share or completion-order algorithm.
The standard states the boundary directly: priority signals are suggestions. They do not guarantee a particular processing or transmission order between responses. Server scheduling has many inputs, including implementation choices and deployment conditions. Size, cache state, application knowledge, compute readiness, congestion and multiplexing can all affect what bytes leave next. Even faithful attention to urgency need not make the highest-urgency object complete first.
Completion order is especially misleading. A small lower-priority response can finish before a large high-priority response while the latter still receives preferential bandwidth. An incremental response may share capacity because early chunks are useful, whereas a non-incremental response at the same urgency may be sent serially. First byte, useful byte, completion and rendering are four different outcome measures. A priority dashboard should not collapse them into one green indicator.
Signals can also change after the request. A browser might begin a prefetch at background urgency and then raise it when navigation makes the resource immediately relevant. A PRIORITY_UPDATE frame conveys a complete current set of parameters and can race with stream creation. The most recently received update can become the scheduler’s latest input. Evidence therefore needs ordering: request header, response header, update frames, receipt times and the scheduler snapshot that acted on them.
Intermediaries add another boundary. They may combine the client’s request priority with an origin’s response priority, and RFC 9218 leaves the merge policy to the implementation. An intermediary that coalesces many client requests onto one backend connection also faces fairness risks. Treating every self-declared u=0 as absolute can let one client delay others. Local policy may spread bandwidth or cap preferential treatment. That choice can be reasonable while still breaking a simplistic prediction derived from the original header.
RFC 9113 documents that the earlier priority signaling scheme from RFC 7540 was not uniformly implemented and is deprecated in current HTTP/2. It recommends an alternative such as RFC 9218 when priority signaling matters. That history is operationally relevant: a capture labelled “HTTP/2 priority” is incomplete unless it identifies the signaling scheme, negotiated settings and implementation behavior.
A useful priority-effect receipt should therefore preserve seven joins. Record the request and response identity; the exact Priority values; every relevant PRIORITY_UPDATE with hop and arrival order; the intermediary’s merge result; the scheduler policy and competing work; bytes allocated over time; and first-byte, useful-byte, completion and rendering outcomes. Keep cache status, object size, origin readiness and connection sharing beside those measurements. The receipt is an editorial operating synthesis, not a protocol object defined by the IETF.
This evidence line keeps R066 distinct from nearby work. BGP Add-Path concerns whether advertised routes represent independent failure domains. RFC 8097 concerns the provenance and interpretation of an origin-validation state. R065 concerned certificate-backed authority for origins on one connection. Here the question is narrower: did an HTTP scheduling suggestion produce the delivery behavior attributed to it?
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance