
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,464 articles
IETF
CATS OAM Can Verify a Steering Policy. It Cannot Choose a Remedy.
The active CATS OAM draft is trying to close a real visibility gap. A service instance can remain reachable at the network layer while the application behind it is slow, exhausted or unavailable. A system that steers traffic only by network reachability may therefore send clients…

IETF
Wassim Haddad and the Prefix That Did Not Yet Authorize Forwarding
A mobile router can have a home-agent registration before it knows which mobile-network prefix it may use. RFC 6276, co-authored by Wassim Haddad, makes the next boundary explicit: only a valid DHCPv6 Prefix Delegation lease allows that prefix into the home agent's binding cache…

IETF
IETF's Survey Can Diagnose a Governance Problem. It Cannot Ratify a Repair.
The IETF Community Survey 2025 gives the organisation a more useful picture of itself than a slogan ever could: a large but imperfect sampling frame, a modest voluntary response, a clear account of what was counted, and a set of concerns that should not be wished away. That is…
IETF
Thomas Graf and the MPLS Label Number That Did Not Identify Its Control Plane
An MPLS label can look like an answer: a compact number at the top of a stack, captured in an export record and ready to be counted. Thomas Graf’s RFC 9160 begins with the smaller, more useful proposition. The number alone does not reliably tell an observer which control-plane…

IETF
SCITT Can Log a Statement. It Cannot Authorize a Release.
RFC 9943 gives software-supply-chain evidence a useful public property: a signed statement can be recorded in a transparency service and accompanied by a verifiable receipt. That can make an issuer’s assertion easier to inspect and harder to rewrite quietly. It does not answer…

IETF
IETF Separates Training Scripts From Slides. Now Test the Handover.
The IETF's latest training-procurement answers make captions, transcripts and narration scripts separate source assets. That is a useful move toward maintainable course material. Its value will become visible when someone other than the original producer has to correct a module.
IETF
Tommy Pauly and the QUIC ACK That Did Not Reach the Application
A QUIC acknowledgement can close one precise transport question while leaving the question an application actually cares about open. RFC 9221, co-authored by Tommy Pauly, makes that seam unusually visible for DATAGRAM frames: the receiver's transport processed a frame, but the…

IETF
DNSOP Can Recommend a Domain-Control Check. It Cannot Govern an Application Identity’s Lifecycle.
The DNSOP working group is in Last Call on a useful document about applications that use global-DNS names as identifiers. Its central discipline is easy to miss. A service may need proof that a registrant or an authorized party controls a domain when an integration is…
IETF
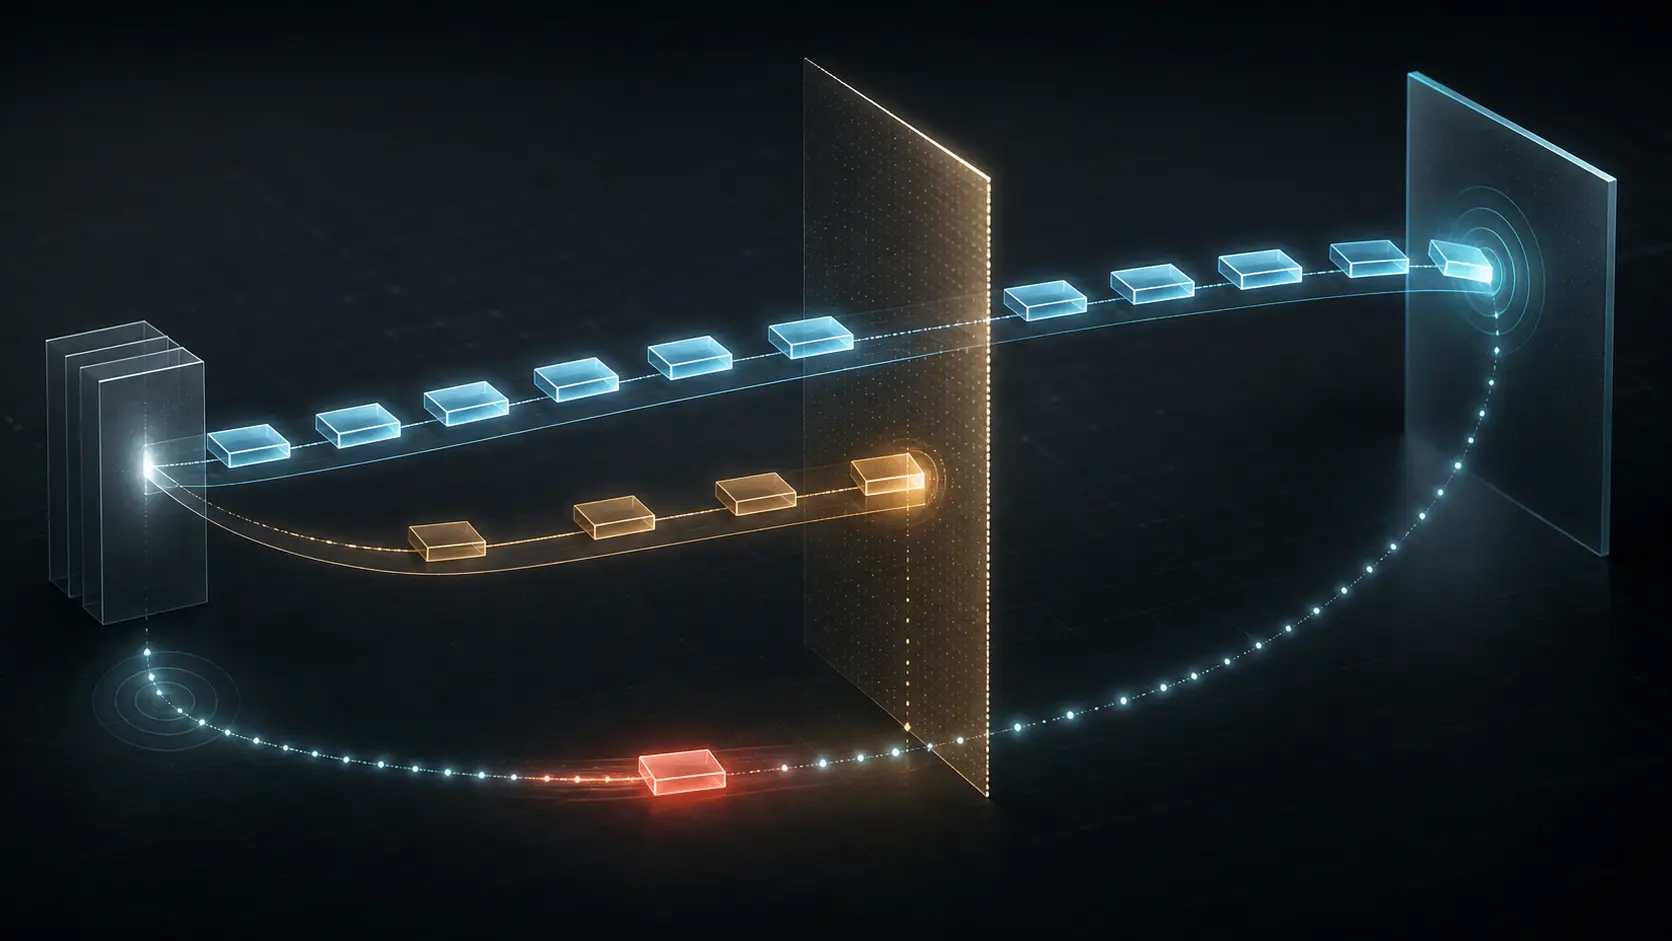
The Newer Packet Arrived First: How TCP RACK Used Time to Find Loss
RACK changes the evidence TCP can use when looking for loss: not only sequence-space gaps, but also the transmission times of data known to have arrived.

IETF
Gorry Fairhurst and the Circuit Breaker Trip That Did Not Name the Fault
A transport circuit breaker is useful precisely because it knows less than an incident report. RFC 8084, written by Gorry Fairhurst, defines a way to halt or sharply reduce traffic after a configured measurement has remained beyond its threshold. It does not turn that reaction…

IETF
A Device-Assignment Token Can Carry Evidence. It Cannot Carry a Relying Party’s Decision.
RATS is asking whether it should adopt a draft that describes an EAT profile for assigning a device to a confidential virtual machine. The question is useful and bounded. It concerns a text, `draft-poirier-rats-eat-da-10`, and the possibility of working-group work. It does not…
IETF
IETF 126’s Highlights Need a Claim-Level Source Key
The IETF’s new account of its Vienna meeting begins with an unusually useful caveat: no one can follow everything, so the recap draws on agendas, descriptions written before the meeting and materials posted afterwards. That honesty solves the first provenance problem. A compact…
IETF
Colin Perkins and the Sent Event That Did Not Say Transmitted
A local transport API can report that it has finished with a message while the network has not yet made the message observable anywhere else. RFC 9622, co-authored by Colin Perkins, makes that boundary unusually explicit: a `Sent` event marks a handoff below the API, not a…
IETF
IETF’s Living Case for Support Needs a Public Adoption Ledger
The IETF has begun turning protocol success stories into a continuing case for financial support. That is a sensible way to explain why an institution matters, but it creates a new governance obligation. When an adoption claim travels from deployment evidence into sponsorship…
IETF
Marco Tiloca and the Revocation Notice That Did Not Withdraw Access
An authorization server can place a token on a revocation list and send a notification while a constrained resource server has not yet learned the change. RFC 9770, co-authored by Marco Tiloca, creates a disciplined way to distribute that information in ACE. It does not collapse…

IETF
FANN Has Adopted a Problem Statement. It Has Not Coordinated a Network Action.
FANN’s chairs have closed an adoption call by saying that the Fast Network Notifications Problem Statement will become a working-group document. That is a meaningful process event: it gives a defined group a text to improve and asks its authors to carry adoption-call feedback…

IETF
Lucas Pardue and the Priority Signal That Could Not Schedule the Page
A web request can carry a highly specific expression of urgency and still leave the page’s fate open. RFC 9218, co-authored by Lucas Pardue, gives HTTP/2 and HTTP/3 a common way to express response-priority preferences. It does not turn that preference into a command over the…

IETF
MLS Can Reopen a Call for Adoption After an IPR Disclosure. It Cannot Turn Disclosure into a Verdict.
An IPR notice is a change to the information set, not an oracle. The MLS chairs have extended a Call for Adoption for the two-party MLS profile after a third-party disclosure arrived. That extension is useful precisely because it gives entities a new opportunity to state a…

IETF
Eric Rescorla and the Encrypted Hello That Could Not Name the Server
An encrypted ClientHello can make a familiar public clue disappear from the first TLS flight. That does not turn the remaining handshake into an identity ledger. RFC 9849, co-authored by Eric Rescorla, specifies a carefully bounded privacy envelope: it can hide the private…
IETF
DNSOP Can Signal a Zone Cut to Nowhere. It Cannot Publish a Private Namespace.
DNSOP is considering a modest DNS mechanism for a difficult operational fact: a child zone can exist for one network while being deliberately unavailable through the public namespace. The proposed parent-side signal could help a resolver avoid confusing that fact with public…
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance