
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,159 articles
IETF
RFC 10011 Brings the TLS Terminator Inside the Security Boundary
RFC 10011 allows a RESTCONF service to sit behind an external TLS terminator. That is not a relaxation of the security model. It is a relocation of the place where encrypted transport and authenticated identity become an administrative claim—and a warning that the terminator, the…

IETF
Joyce Reynolds and the Assigned-Numbers RFC That Stopped Being the Registry
In 2002, Joyce Reynolds gave an old standards document a more honest job. RFC 1700 would remain a durable record of what the Assigned Numbers tables looked like in 1994, but it would no longer impersonate the changing registry that engineers actually needed.
IETF
A Diagnostic Plan Is Not a Root Cause: Eight Receipts for Scheduled OAM
`draft-ietf-opsawg-scheduling-oam-tests-07` makes network diagnosis programmable as timed, ordered test sequences. The discipline begins when operators refuse to let a stored plan, a green status or a returned metric stand in for the execution, causality, authority and outcome…

IETF
An IETF Draft Names a Conflict-of-Interest Gap. Authority Should Trigger the Safeguard
Revision 07 of an individual IETF process draft adds only one short paragraph on conflicts of interest. The paragraph is enough to expose a larger design problem: the IETF has several concrete conflict policies, but each belongs to a defined body or corporate role. A general…

IETF
The color matched. The proof did not: RFC 9832’s transport-class evidence chain
Three BGP fields can carry the same 32-bit value and still answer different questions. RFC 9832 supplies an ordered mechanism for classful transport; operators still need a chain of receipts proving which namespace, attribute, database, fallback and forwarding state actually…

IETF
RFC 9983’s Anycast Flag Marks Intent, Not Service Health
A single bit can remove ambiguity from routing data without proving that a single request will succeed. RFC 9983 gives OSPFv2 an explicit way to mark a prefix as anycast, but it also draws an unusually useful governance line: the mark states how the prefix is intended to be…

IETF
Paul Mockapetris and the Authoritative Bit That Did Not Cover the Whole Reply
One DNS response can carry an authoritative alias, a cached destination and helpful address records under a single AA flag. The bit has done its job; the database that stamped the whole packet “authoritative” has not.

IETF
The watts fell. The proof did not: RFC 9845 and the green-network control loop
A power graph can move down while the network’s carbon cost, workload allocation and service risk remain unknown. RFC 9845 makes visibility useful; it does not let one meter speak for the whole system.
IETF
A Workload Credential Is Not the Workload: Eight Proofs Between Bootstrap and Outcome
The WIMSE practices draft shows how platforms can replace embedded secrets with short-lived workload credentials. Its harder lesson is that every safer credential still sits inside a longer chain of facts that must not be compressed into one green authentication event.
IETF
RFC 9991 Made Failure Detail Conditional, Not Owed
A failed email can be both a diagnostic clue and somebody else's private correspondence. RFC 9991 does not solve that tension by awarding the domain owner every available header and body. It standardizes a request and a report while leaving the receiving operator responsible for…
IETF
DNS Types 69 and 70 Delegate Meaning but Do Not Name the Registry Version
A signed DNS record can preserve every octet and still leave one historical question outside the signature: which edition of an external registry gave those octets meaning? Two newly assigned resource-record types make that boundary concrete. UNECE is now type 69 and ISO is type…

IETF
Jim Schaad and the Key ID That Was Only a Hint
Two keys sit in the same verifier under the same short label. The message supplies that label, the first key is tried, and a dashboard turns the result into the name of a device. Jim Schaad’s COSE specification draws a harder boundary: the label is a search hint; identity and…

IETF
RFC 9990 Counted the Receiver’s Claims, Not the Mailstream Itself
A dashboard can show 240,000 messages, three alignment rates and a red segment labelled as a policy override. The numbers may be perfectly formed and genuinely useful. They still do not let the domain owner walk back through 240,000 individual decisions. RFC 9990 standardizes…
IETF
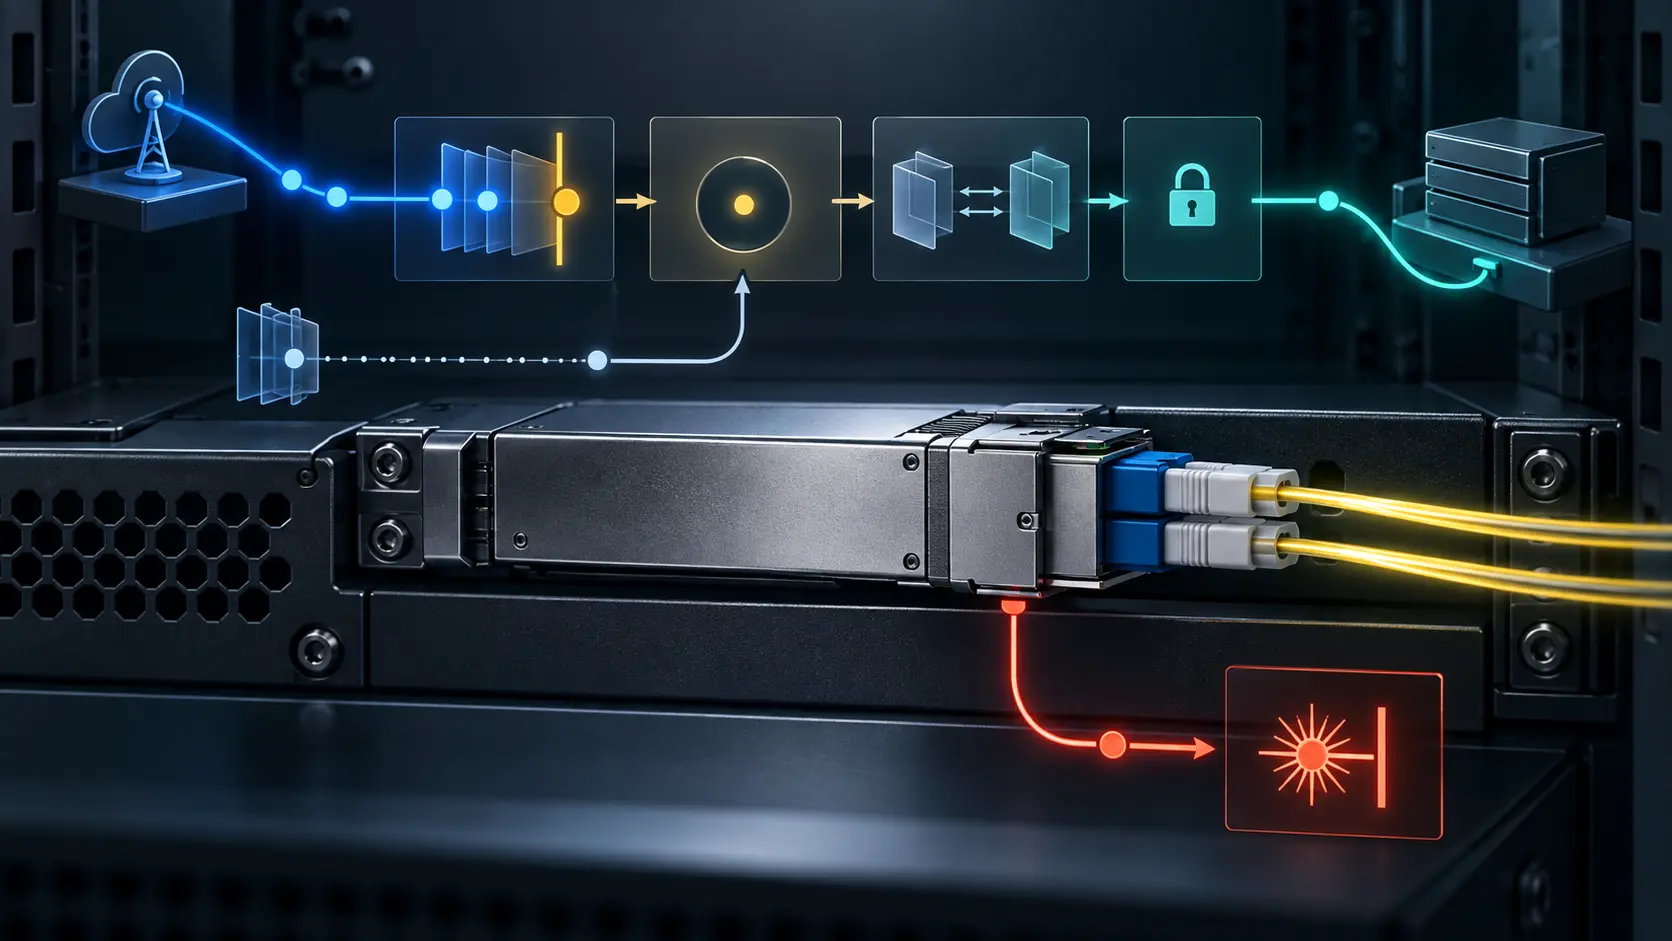
CMIS Revision 04 Adds Control Handover but Leaves the Last Write Unsettled
Imagine a remote optical controller starting a three-register tuning sequence. Before the final write lands, the host removes that CMIS page from the remote-write allowlist and restores its own configuration. Which system owns the half-finished state? Revision 04 of a new IETF…
IETF
Donald E. Eastlake 3rd and the RBridge Nickname That Could Not Be a Permanent Identity
Two TRILL campuses join, and the same 16-bit nickname suddenly has two claimants. The number has not lied; the inventory that treated it as a permanent device identity has asked it to carry evidence it was never designed to hold.

IETF
RFC 9996 Registered the Media Type, Not the Schema Version
A label can tell a receiver what kind of parcel arrived without telling it which rulebook gives the contents meaning. RFC 9996 gives Protocol Buffers two proper media types and draws useful boundaries around binary and JSON handling. It does not place the Protobuf schema, its…

IETF
Patrik Fältström and the ENUM Answer That Did Not Complete the Call
The number resolved. A signed DNS answer yielded a URI. The phone still never rang. Patrik Fältström’s work on ENUM is most useful when those three facts remain separate.

IETF
Revision 04 Promises UUID Identity, but Its Energy Schema Still Points to a Local Name
A data model can be syntactically valid and still give readers two different answers to the same governance question. Revision 04 of the IETF GREEN power-and-energy YANG draft says its component reference is bound to a globally unique UUID. The module printed a few pages later…

IETF
RFC 9997's PEN-Derived SID Range Is Not a Provenance Stamp
A number can be globally unique and still tell the wrong story about its origin. RFC 9997 gives eligible Private Enterprise Number holders a deterministic block of YANG Schema Item iDentifiers, eliminating a central allocation round trip. That is useful coordination. It is not an…

IETF
David Harrington and the SNMP Context That Did Not Identify the Operator
The command named an engine, a context and an entity with precision. None of those fields said which human had chosen the change. David Harrington’s SNMP architecture makes that absence visible rather than filling it with an assumption.
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance