
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,290 articles

IETF
The Origin Published a Knowledge Map. It Did Not Authorise the Agent to Obey It.
An agent can discover a file, verify its bytes and still have no permission to act on a sentence inside it. The proposed `knowledge-linkset` well-known URI makes that distinction operationally urgent rather than philosophical.

IETF
The Composite Signature Passed. The Envelope Named a Different Algorithm.
Composite ML-DSA combines post-quantum and traditional signatures behind one interface. Its CMS profile shows why that single verdict still depends on several algorithm identifiers, exact encoded bytes and a content digest agreeing across the envelope.
IETF
OSPFv3 Cannot Retire AH One Router at a Time
A new proposal would remove an old authentication choice from OSPFv3. Its operational test is less about selecting a replacement than about getting every router on a link to accept the same protected packets throughout a change.
IETF
The Capsule Recorded a Disagreement. It Had No Right to Block Anything.
A new SCITT profile proposes an immutable third-party comparison between what a subject declared and what an observer found. Its most important design choice is not the hash or the Merkle tree, but the refusal to let measurement quietly become authority.
IETF
The Final Filter Was Correct. The Update Still Leaked a Route.
Revision 03 of an IETF GROW draft turns BGP security from a static configuration question into a transaction question. A router may begin and end with the intended policy while briefly enforcing something else between commands.

IETF
The Tool Knew the SID. It Still Did Not Own the Actuator.
CORECONF-M2M proposes a compact route from YANG models and SID identifiers to MCP tools that an AI agent can call. The route can remove bespoke serialization without removing the harder boundary: who may act, what the device accepted and whether the physical world actually…

IETF
The Issuer Signed the Envelope. It Still Could Not Swap the Agent Key.
Revision 02 of the AIC JSON Web Token profile places a principal-signed delegation inside an issuer-signed credential. The nested design matters because an issuer may certify the carrier without acquiring the right to substitute the agent key chosen by the principal.

IETF
The Agent Signed the Challenge. Its Embedded Key Still Wasn't Authority.
OpenA2A AIP revision 03 separates a mathematically valid response from an authenticated agent. The decisive control is not whether the supplied key verifies the signature, but who is entitled to bind that key to the claimed identity.
IETF
The Agent Went Silent. The Trust Score Punished What the Verifier Could Not See.
The proposed Network Behavioral Trust Protocol turns missing heartbeats and co-silence into score decay, SUSPECT and QUARANTINED states. That may be useful operationally, but an absence first describes a verifier's observation surface—not an agent's character.

IETF
Every Link Verified. The Timeline Could Still Be Shorter.
AER-1 revision 09 gives an AI-agent job a verifiable internal history. Its more important contribution is admitting why that history still needs a witness outside itself.

IETF
The Key Changed. The Instance Stayed the Same Because Someone Kept the Ledger.
OAuth attestation can prove that a client instance holds a current key. A new profile tries to preserve that instance's identity when the key changes. The continuity does not live in the identifier string: it lives in an attester's enrollment records, lifecycle rules and custody…

IETF
The Chain Proved a Clock Was Wrong. It Did Not Name the Culprit.
Roughtime can seal an inconsistency into portable evidence without pretending that cryptography has already decided whom to distrust.

IETF
The ICV Was Valid. The Path Record Could Still Be False.
IOAM can carry a cumulative integrity chain across the network and let a Validator confirm that protected fields were not modified. That is valuable evidence. It is not the same as proving that every expected record arrived, every participating node told the truth, or the…

IETF
No One Reported Progress. Why Did the Task Look Complete?
A task with entities but no progress reports should preserve the absence of evidence, not turn an empty column into a green completion state.
IETF
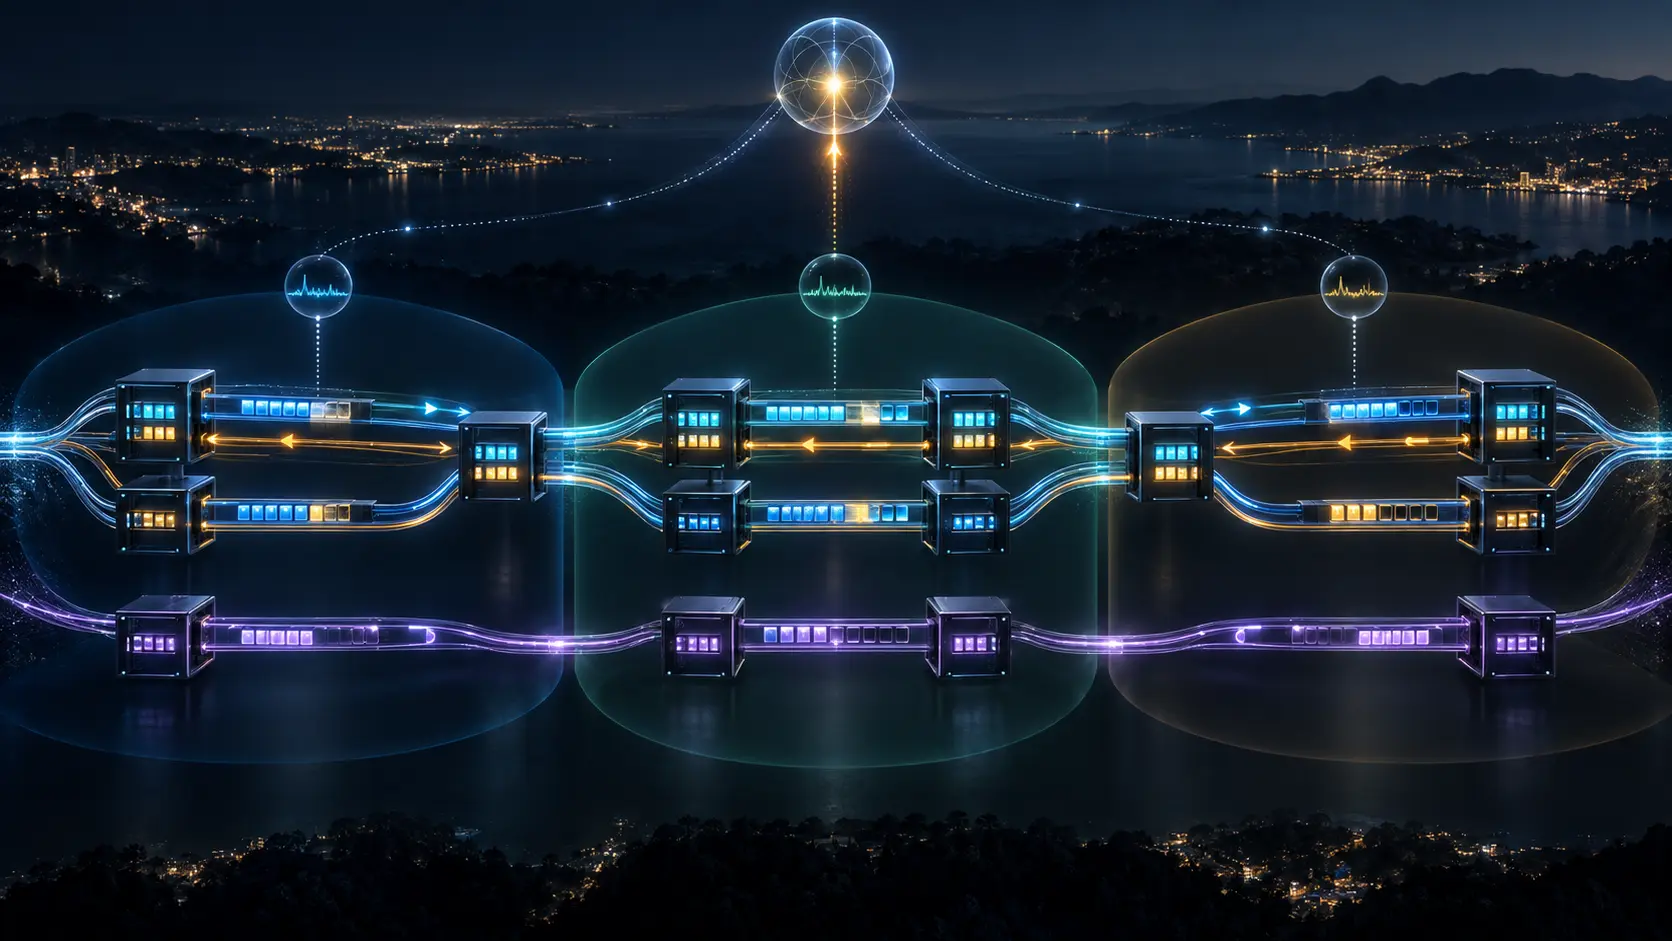
The Controller Reported Both Directions Done. The Network Had Not Proved Hitless
Fine-grain optical transport can change a low-rate service’s bandwidth without a planned interruption. Yet the green completion event at the multi-domain coordinator is only one controller’s conclusion. It is not a receipt for every direction, domain, protection path, tributary…
IETF
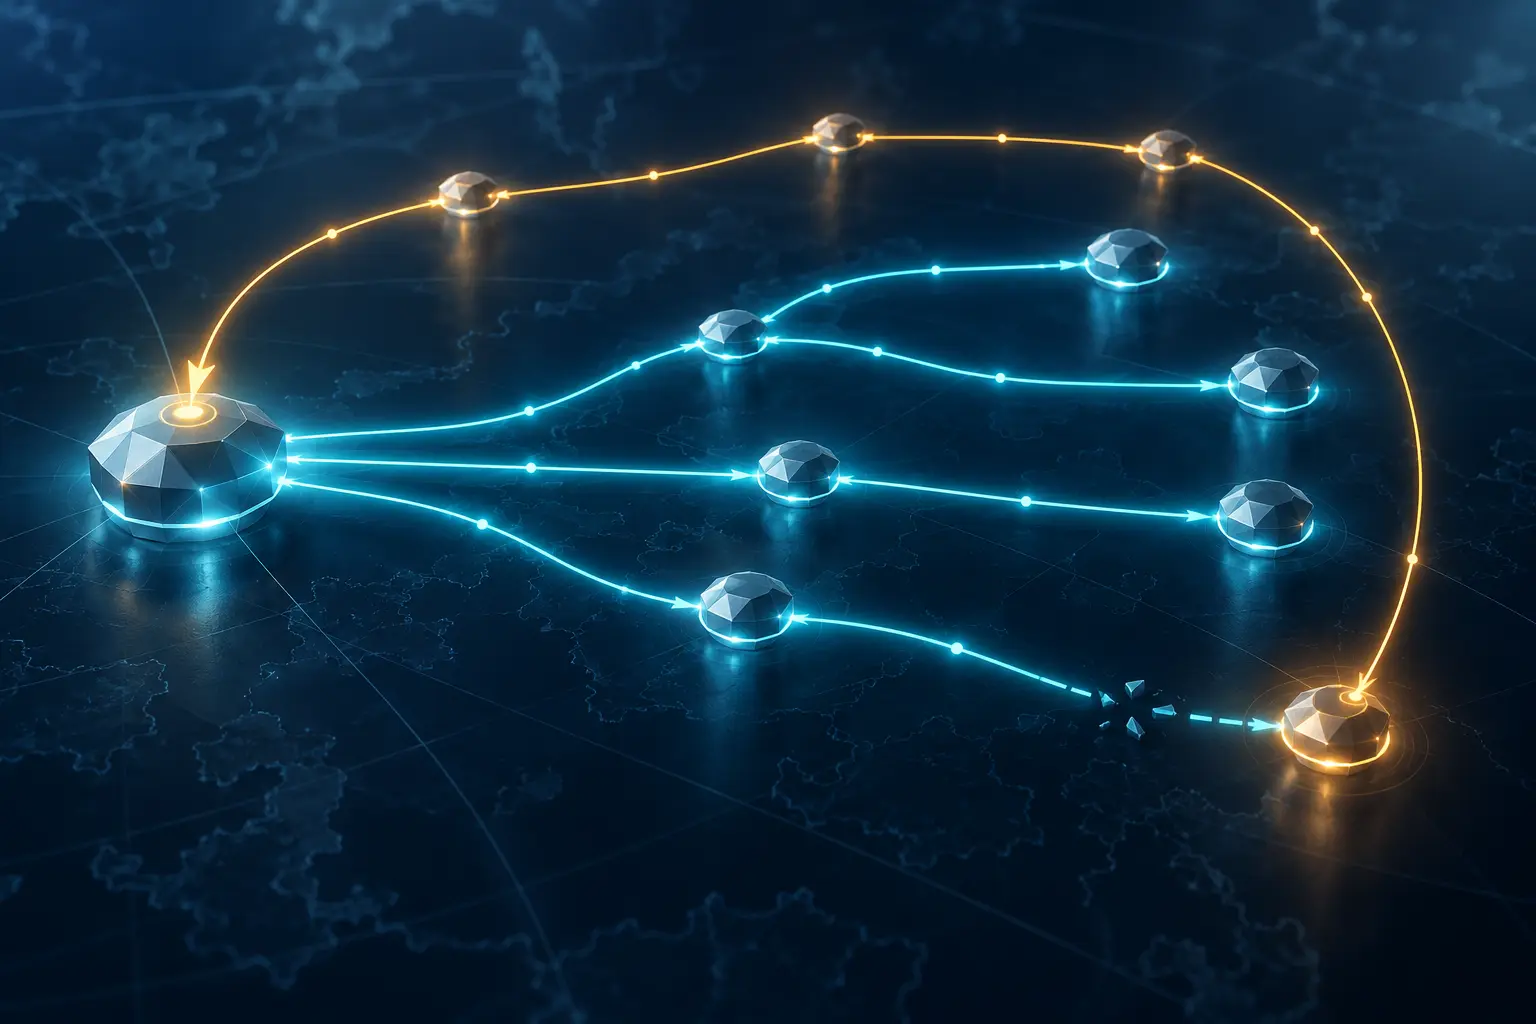
The Receiver Saw the Failure. Did the Multicast Head Hear It?
In a multicast network, the receiver that notices silence is not necessarily the node that can act on it. The latest BIER BFD draft makes the route back to the sender—and the proof that an alert was matched to the right session—a separate operational question.

IETF
The Payment Legs Agree. The Delivery Leg Is Still Empty.
Two agents can hold matching records of money movement while the evidence for what was promised in return remains on a different, empty track.

IETF
The Batch Proof Passed. How Many Privacy Pass Tokens Did You Actually Get?
Batched Privacy Pass issuance can cut proof overhead and round trips, but it also creates a new place for operational truth to disappear. One verified proof or one successful HTTP response is not yet a receipt for the number of tokens that survived finalization, entered durable…
IETF
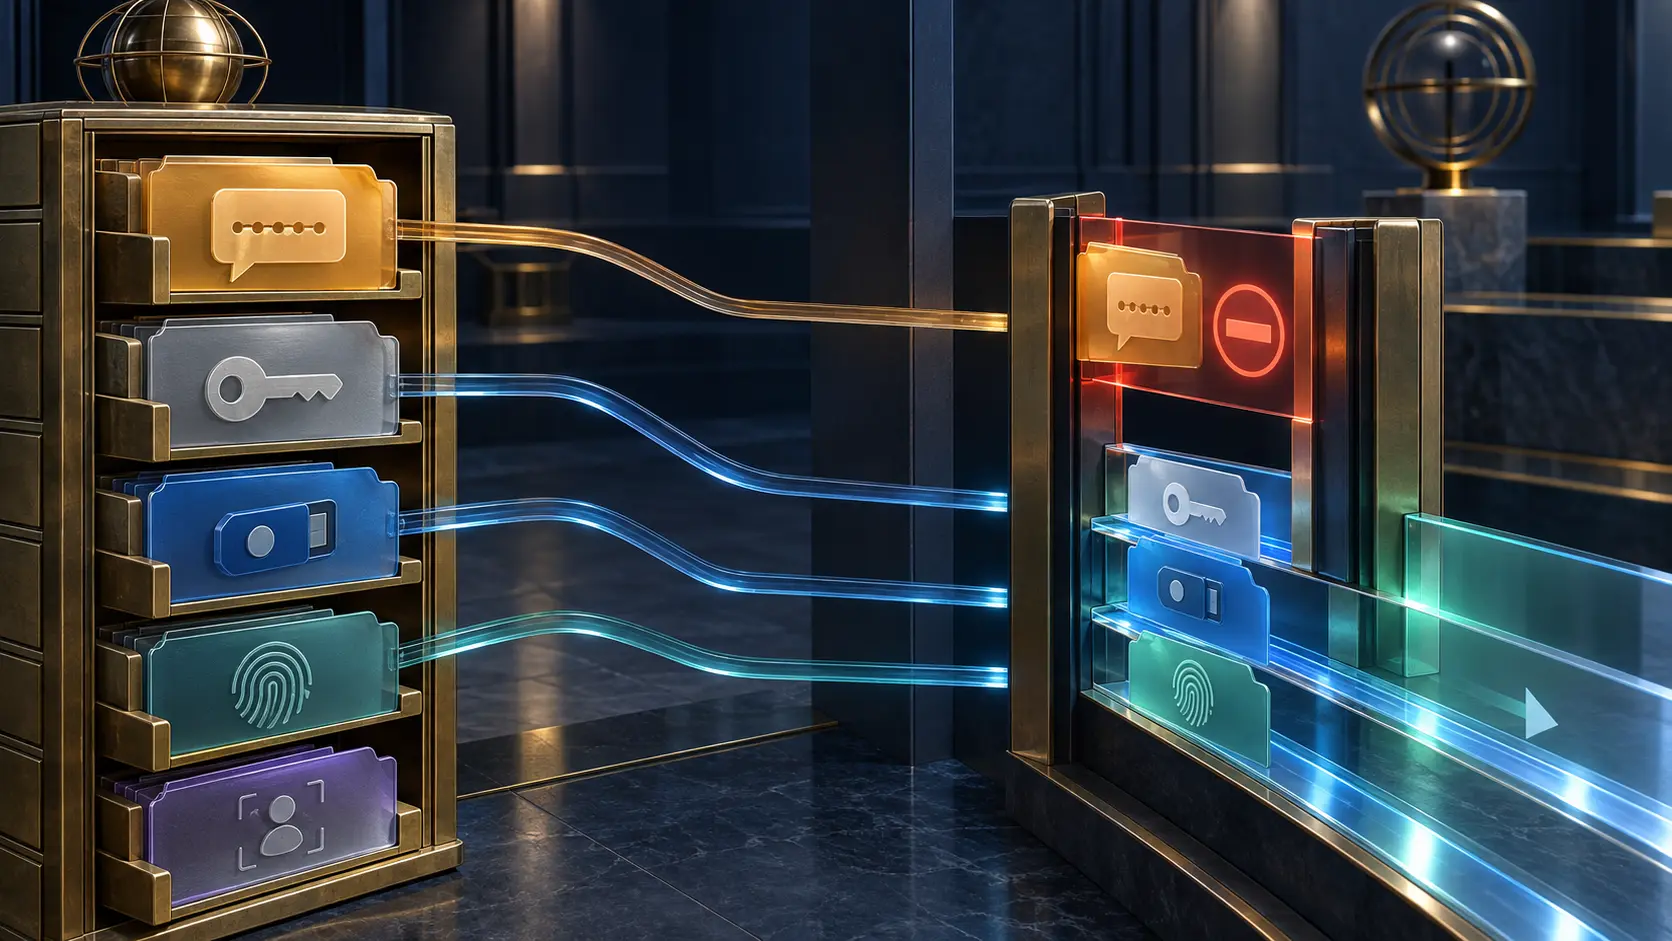
The Registry Can Name the Security Question. It Cannot Make It Acceptable.
An authentication-method label can improve interoperability while leaving the relying party entirely responsible for deciding whether that method is safe enough to use.

IETF
MOQT's New Filter Type Puts Relay Compatibility on the Wire
The latest Media over QUIC Transport draft makes a small but consequential change to a request's shape. A location filter now identifies its form explicitly, rather than asking a receiver to infer it from the number of encoded bytes. For relays and clients built against different…
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance