
Topic
Registry Governance
Within the Topic facet, Registry Governance topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

ICANN
ICANN’s Replacement String Option Expires After 14 Days
Under the 2026 Applicant Guidebook, a replacement string is designated with the application, elected during a 14-day period after Reveal Day, and cannot be reversed once the switch is made.

Story
AFRINIC Invited Hosts for Future Meetings. The Published Call Does Not State a Submission Deadline
AFRINIC has described what prospective meeting hosts should provide, but its frozen Call for Hosting page does not say when proposals close or when selection decisions will be made.
ICANN
Winning an ICANN Auction Does Not Guarantee Delegation
An auction result decides which directly contending application may advance. It does not itself award a delegated gTLD.
Story
AFRINIC Appointed a Five-Member Appeal Committee Through 2026. The Notice Does Not Show the Board Decision Record
AFRINIC has published who will hear policy-process appeals through the end of 2026, but the frozen notice does not show when or how its Board reached the appointment decision.

Story
APNIC prop-175 Moves the IPv6 Evidence Test to the First Request
APNIC prop-175 would let an eligible organisation justify an initial provider-independent IPv6 assignment larger than `/48` when the operational requirement is already documented. The proposal is still only on the Policy SIG mailing list. Its promise is less duplicated procedure…

Story
RIPE Database Now Composes Unicode. The Text Chain Needs a Normalisation Receipt
One visible name can arrive as two different code-point sequences. RIPE Database release 1.123 deliberately makes those sequences converge before the value passes through its remaining UTF-8 controls. That is good interoperability. It is also the moment when an evidentiary chain…

ICANN
Reveal Day Does Not Finalize an ICANN Contention Set
Reveal Day starts the contention record; it does not freeze it.

Story
AFRINIC Named a PDWG Co-Chair by Consensus. The Published Notice Does Not Show the Consensus Record
AFRINIC recorded the name, method and duration of a 2026 PDWG leadership selection, while leaving the underlying consensus determination outside the two frozen public pages reviewed here.

ICANN
Private Deals Cannot Resolve an ICANN Contention Set
From Reveal Day, applicants in the same contention set enter a communication boundary that covers private talks, public disclosures and indirect intermediaries.

ICANN
A .Brand String Change Can Add Words, But Cannot Create or Expand Contention
ICANN’s 2026 Round gives a qualifying .Brand applicant a narrow way to change a string when contention arises. It is not a general opportunity to rename an application.

Number Resource Society
An ASPA Is Not a Complete AS-Path Attestation
An ASPA can help an operator test whether an AS path is consistent with published customer-to-provider authorizations. That is valuable route-leak evidence. It is not a signature over every hop, a proof of route origin, a commercial contract, or a guarantee that the published…

ICANN
A Material Change to Public Application Content Opens 30 Days of Comment, Not Automatic Approval
When ICANN finds that a requested change materially affects public application content, the request enters a 30-day comment process but has not crossed the approval line.

Story
AFRINIC Offered In-Person Registry Checks at AfPIF. The Frozen Page Does Not Report Outcomes
AFRINIC promoted face-to-face help with registry records, identity checks and open requests at AfPIF 2026; the frozen source set does not show what was completed.

Number Resource Society
An RPKI Cache Serial Is Not a Freshness Timestamp
Two RPKI caches can report perfectly accurate serial numbers and still tell an operator nothing about which cache holds newer global data. RFC 8210 scopes a serial to one cache session and protocol version. Treating the larger number as the fresher view manufactures a chronology…

ICANN
GAC Consensus Advice Starts a 21-Day Response Record, Not an Automatic Board Outcome
Formal GAC Consensus Advice changes the applicant's procedural position, but it does not itself supply the ICANN Board's decision.

IETF
When a Drone ID Becomes a DNS Delegation: RFC 9886 and the Registry Chain Behind Remote ID
A Broadcast Remote ID can carry a compact DRIP Entity Tag (DET), while the public evidence needed to authenticate registry inclusion is distributed across reverse-DNS delegations, HHIT and BRID records, and a certificate chain. The practical question is therefore not only whether…

Number Resource Society
A ROA maxLength Is Not a Traffic-Engineering Policy
A route can be RPKI Valid because a ROA’s maxLength admits its prefix length. That result proves a bounded origin authorization. It does not prove that the more-specific route was planned, approved, currently announced or preferred by the operator. Those are separate facts, and…

Story
LACNIC’s IPv6 allocation rules make scale plannable
**BTW analysis:** IPv6 offers a vast address space, but abundance alone does not tell a network operator what it may request, how need will be assessed, or what obligations follow an allocation. In Latin America and the Caribbean, those practical questions meet LACNIC’s published…

Leaders
Artem Izbaenkov and the Cost of Representation at RIPE NCC
Artem Izbaenkov’s 2024 campaign for a seat on the RIPE NCC Executive Board turned an operator’s career in DDoS defence and cloud security into a wider argument about who can participate effectively in registry governance—and what language, fees and institutional attention have to…
Number Resource Society
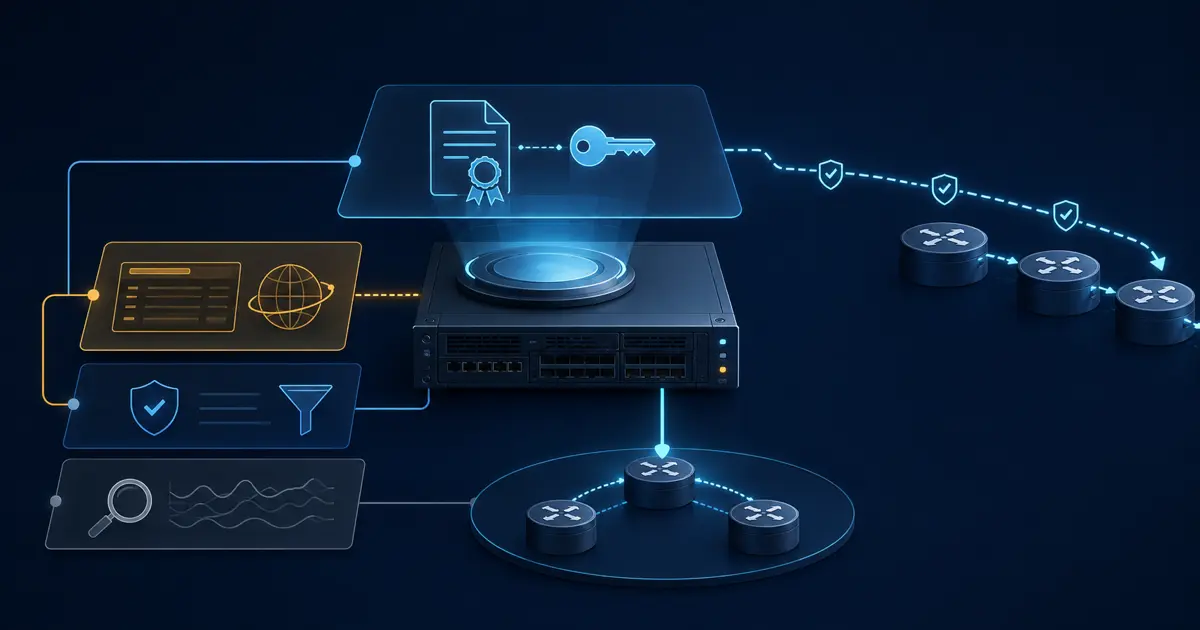
A BGPsec Router Certificate Is Not Route-Origin Authority
A BGPsec Router Certificate Is Not Route-Origin Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…