
Topic
Peering and Transit
Within the Topic facet, Peering and Transit topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Leaders
John Moy and the Operational Record Behind OSPF State and Graceful Restart
John Moy's documented OSPF work offers a restrained account of routing reliability: topology state has to be explicit and synchronized, protocol cost has to be measured, standardization has to rest on implementation experience, and forwarding continuity during restart has to end…
Global Cloud Services
Cloudflare's 2026 BYOIP Outage Made Prefix-State Control an Accountability Test
A control-plane change withdrew customer-owned prefixes and exposed why address authority, service bindings, route intent, deployed configuration and public reachability need separate, continuously reconciled evidence.

Leaders
Ross Callon and the Operational Transition from Dual Routing to MPLS Labels
Ross Callon's dated standards record shows that network transitions endure when capabilities, compatibility, and forwarding identity are made explicit, first for IP and OSI coexistence and later for traffic classes bound to locally meaningful MPLS labels.
Global Institutional
The 2015 Root DNS Flood Made Cross-Operator Telemetry an Accountability Test
Two concentrated query floods exposed the difference between root-system continuity and localized saturation, making shared, layer-specific telemetry the basis for judging operator preparedness and response.
Europe and Middle East Institutional
Spamhaus's 2013 DDoS Made Open DNS Recursion a Network Accountability Test
The March 2013 campaign showed how exposed recursive DNS, source-address spoofing and shared interconnection paths could turn individually small configuration failures into a large external cost. Accountability depends on proving which operator controlled each executable step and…

Leaders
Dave Oran and the Operational Boundaries from IS-IS to IP Anycast
Dave Oran’s shared technical record shows how dependable forwarding begins with a clear account of identity: which routing domain, service instance, name, or piece of state a system is actually using, and where continuity can break when that identity changes.

Leaders
Peter Psenak and the Link-State Decisions Behind Segment Routing and Flexible Algorithms
Peter Psenak's attributed IETF record offers a practical way to examine how routing policy becomes operational state. The relevant standards do not promise an automatically optimal network. They define identities, constraints, participation rules, forwarding bindings, and failure…

Global Cloud Services Trends
Cloudflare’s 15-minute Istanbul network incident left a precise window but almost no diagnosis
Cloudflare says elevated latency and connection errors affected Istanbul for 15 minutes on 1 August. The unusually exact interval is the firmest part of a record that identifies no product, route, cause or scale—and whose only visible notice appeared after the reported impact had…

Leaders
Hannes Gredler and the Failure Boundaries Behind IS-IS and BGP-LS
Hannes Gredler’s co-authored standards work offers a practical lesson in routing automation: useful decisions begin with records that identify topology precisely, state their scope, and remain honest about what they cannot authorize or prove.

Asia-Pacific National Telecom
KT's 2021 Routing Error Made Protocol-Boundary Validation a National Network Accountability Test
KT's nationwide Internet disruption showed why a carrier cannot treat an approved maintenance plan or two layers of manual review as proof that a live routing change is safe: accountability depends on the exact commands routers execute, the protocol boundaries they preserve, the…

Global Cloud Services
GitHub's 2015 Great Cannon DDoS Made On-Path Code Injection a Network Accountability Test
The 2015 attack on GitHub showed that network accountability begins with the bytes a user actually receives, not merely the address, certificate, contract or status page associated with a service.

Leaders
Yakov Rekhter and the Operational Boundaries Built into BGP and Private Addressing
Yakov Rekhter's public standards record shows how inter-domain routing and address scope became manageable through explicit permissions, visible protocol state, bounded uniqueness, and honest accounting for the cost of later change.
Europe and Middle East National Telecom
LINX's 2023 LON2 Incidents Made Lab-to-Production Network State an Accountability Test
When a router moves from a laboratory into a live Internet exchange, a clean configuration file is not enough. LINX's public account of its 2023 LON2 incidents shows why operators must verify the identity and forwarding state that the device is actually running, especially when a…
Global Cloud Services
Akamai's 2004 Network Attack Made Distributed Edge Failover an Accountability Test
Akamai's bounded account of a 2004 denial-of-service incident shows why a distributed edge network must prove customer impact, destination capacity and failover behavior from the running network rather than architecture claims alone.

Global Cloud Services Trends
Cloudflare’s IAD 5XX episode lasted 256 minutes but was disclosed in one retrospective update
Cloudflare says an increased level of HTTP 5XX errors affected Ashburn, US (IAD), from 18:45 to 23:01 UTC on 31 July. Yet the public incident contains only one visible update, timestamped more than two hours after that interval ended. The fault is closed; the operational…

Global Cloud Services Trends
Cloudflare’s us-east-1-aws path returned intermittent 5xx errors for 138 minutes
Cloudflare resolved a minor incident involving intermittent HTTP 5xx responses for customers using the label us-east-1-aws at 04:19:32.991 UTC on 31 July. A fix had entered monitoring 10 minutes and 51.068 seconds earlier. The operator disclosed the request outcome and…
Global National Telecom Trends
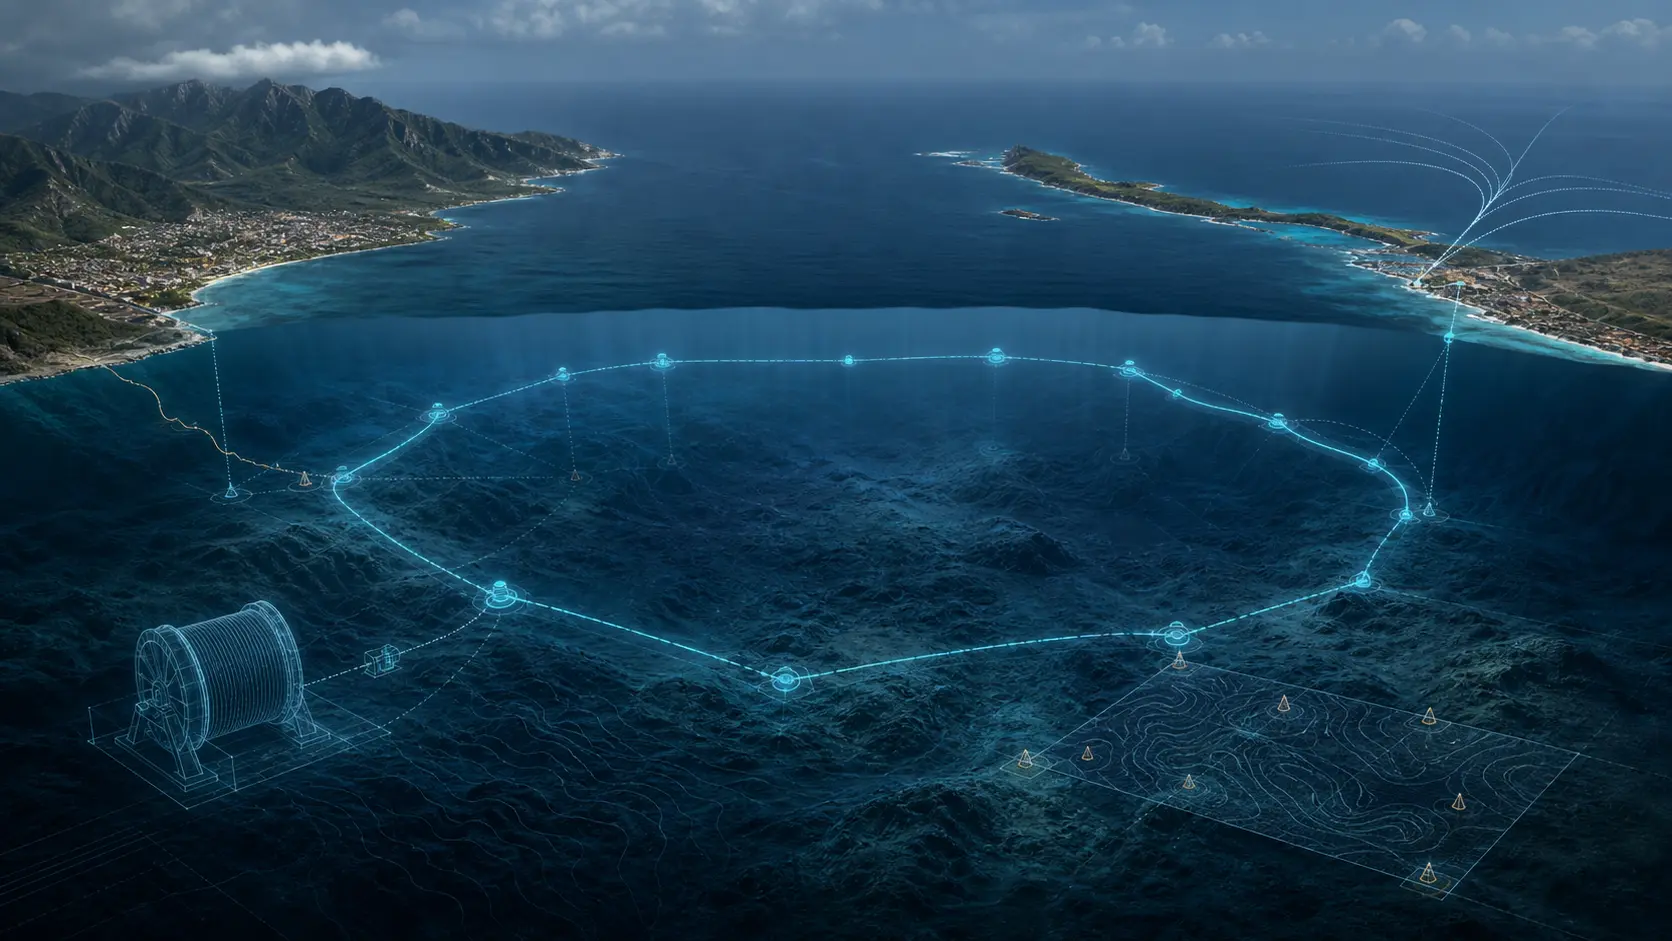
Fénix promises a 14 Tbps Venezuela–Curaçao ring, but the cable is still an announced project
Liberty Networks and CANTV announced Fénix on 31 July as a 378-kilometre submarine cable system between Camuri in Venezuela and Willemstad in Curaçao, with a stated minimum ring capacity of 14 Tbps. The design would connect Venezuela to a broader Caribbean hub. The release is…
Global Cloud Services
OVH's 2016 Mirai Attack Made DDoS Scrubbing Capacity an Accountability Test
OVHcloud's report of traffic above one terabit per second during the first Mirai wave turned a spectacular attack number into a practical network question: could a hosting operator measure the flood, activate mitigation, preserve clean traffic and show customers that the service…
Global Cloud Services
GitHub's 2018 Memcached Attack Made Anti-Spoofing and Mitigation Handoff an Accountability Test
GitHub's response to a 1.35-terabit-per-second attack showed that DDoS resilience depends on more than buying bandwidth: operators must detect abnormal traffic, move routing authority safely, preserve clean delivery and reduce the spoofing conditions that make reflection…

Europe and Middle East Cloud Services Trends
Cloudflare’s London HTTP-error incident was still at the first diagnostic stage
Cloudflare opened a minor incident at 19:06:19.068 UTC on 31 July after detecting increased HTTP errors affecting a subset of customers. Fourteen minutes later, at the Wave 46 cutoff, the public record still said only that the company was investigating, analysing and mitigating…