
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

History
The Global Registry Held the Service Map: RFC 3650
The Handle System’s “global” namespace did not require every resource record to live in one central store. RFC 3650 placed a registry at the root of a service hierarchy: clients could ask it where a naming authority’s handles were served, then go to that service for resolution.

IETF
The Member Was Removed. The Group Key Still Worked.
A clean roster can conceal a live capability. RFC 5275 makes the uncomfortable distinction explicit: removing a member changes who should belong, while rekeying changes who can decrypt. Between those states lies the control surface that leaders must govern.

IETF
The Watcher Returned 200 OK. Its Presence State Was Not Proved.
RFC 5263 makes a final SIP response the gate before a Presence Agent sends the next partial notification. That response closes one transaction. It does not, by itself, prove that the watcher applied the delta, committed the reconstructed state, exposed it downstream or obtained…

IETF
The Strongest Pilot Pointed to a Sector. It Did Not Name the Next Router.
A radio can know which signal is winning before the network knows what that observation means at the IP layer. RFC 5271 turns 3G CDMA pilot, sector and access-network evidence into a fast-handover candidate. Its most useful lesson is not the speedup. It is the point at which a…

IETF
The Deltas Arrived in Order. Presence Was Still Only a View.
RFC 5262 gives a presence recipient a versioned chain of full and partial XML documents. A contiguous chain can prove that this feed was reconstructed in order. It cannot prove that the initial view was complete, that another watcher saw the same facts, or that the person or…

History
The Query Crossed IPv4. Its Answer Could Still Name IPv6: RFC 3596
DNS did not need an IPv6 road in order to talk about an IPv6 address. RFC 3596 kept the packet carrying a question separate from the record the question asked for—a small design boundary that let one naming system span a mixed-version Internet.
IETF
The Key Authorized One Route Change. It Did Not Authenticate the Handover.
Cryptography can make a narrow fact extremely strong and still leave the larger story unproved. RFC 5269 provisions a shared key so a previous access router can reject an unauthorized Fast Binding Update. The resulting MAC answers one precise question: may this sender change…

IETF
The Patch Applied. It Did Not Prove the Base Was Right.
RFC 5261 can locate one XML node and mutate it deterministically. That is valuable execution evidence. It does not identify the intended base revision, prove that the selector names a durable business entity, or show that the resulting document was authorized, committed and…

History
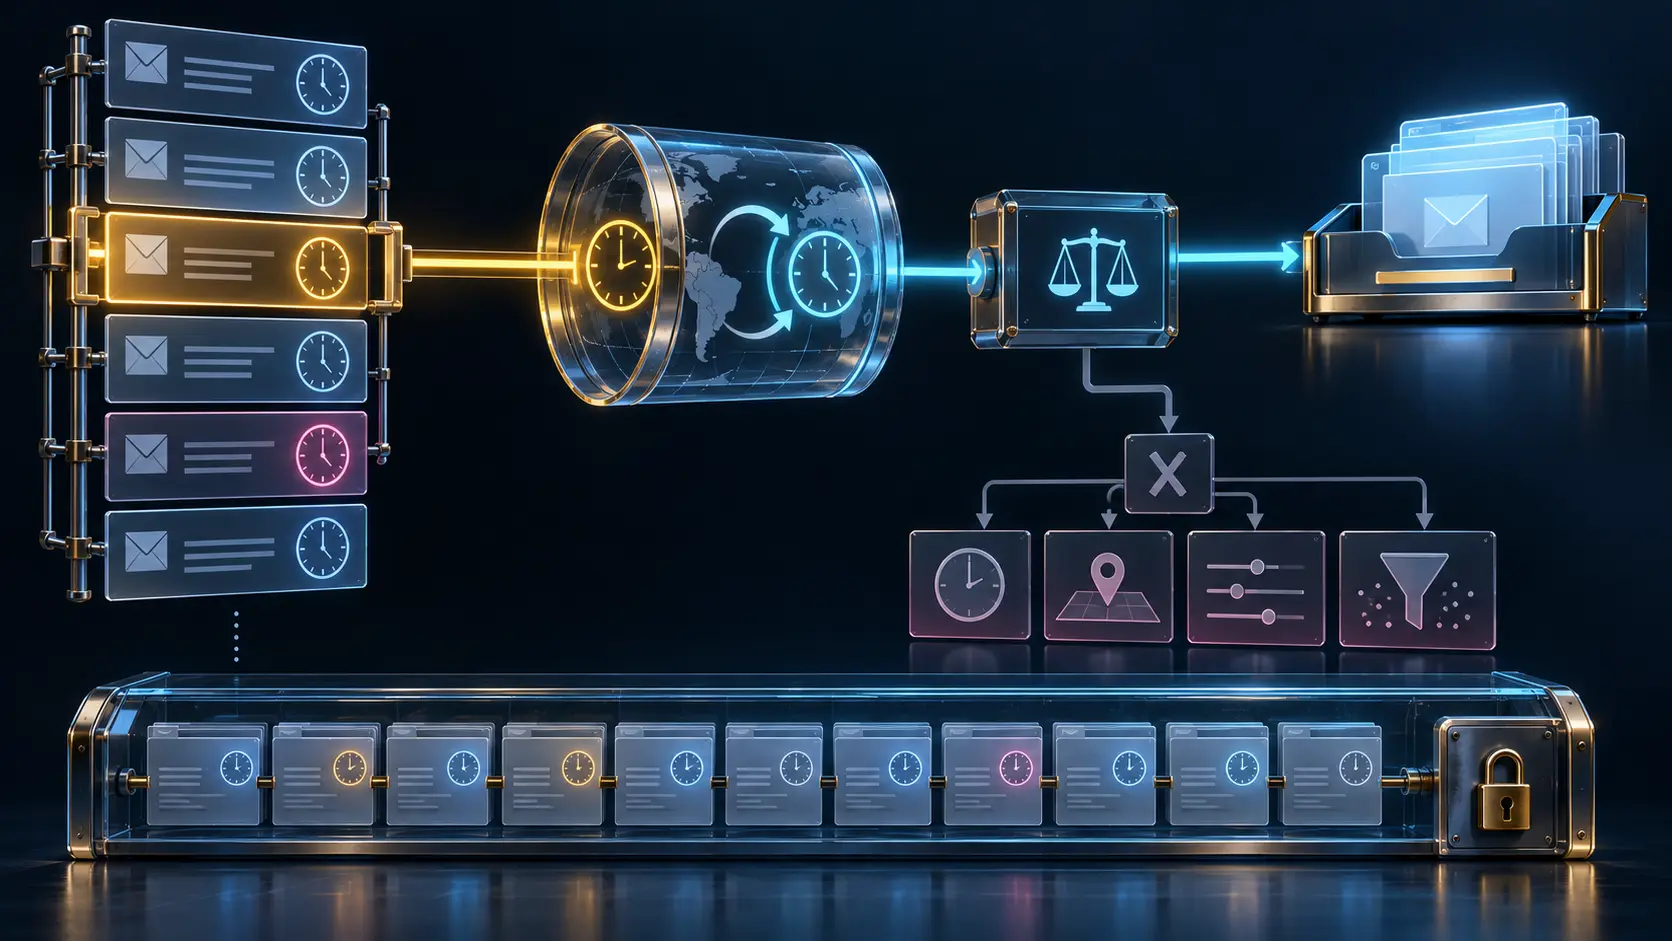
TCP Delivered the Trap. It Still Did Not Confirm the Operation: RFC 3430
TCP can deliver every byte of an SNMP message in order and still leave the sender without an answer to the question it actually cares about: did the management application receive, process or queue this operation? RFC 3430 made that boundary explicit. It offered a reliable stream…
IETF
The Rule Matched a Date. It Did Not Prove When the Event Happened.
RFC 5260 gives Sieve a disciplined way to compare a timestamp from one selected header occurrence—or the script’s own execution clock. That result can route mail reliably. It does not authenticate the timestamp, reconstruct the transit history, or prove that the selected action…

IETF
The New Route Was Ready Before the Device Arrived. Arrival Still Had to Be Proved.
Fast handover is designed to prepare forwarding before a mobile device changes links. That lead is useful, but it creates a precise control risk: an accepted Fast Binding Update, a prepared tunnel and a buffered packet queue can all exist while the device is still somewhere else.…

IETF
The Attachment Opened. Its Signature Did Not Travel.
RFC 5259 lets an IMAP server adapt an attachment for a client that cannot readily use the stored format. The result can be smaller, more compatible and immediately useful. It is still a derivative selected and produced under a conversion policy—not the signed source, not a…

IETF
The Live Search Kept Updating. It Was Never a Snapshot.
An IMAP search that changes on screen can look more authoritative than a static answer. RFC 5267 gives it a narrower meaning: one baseline, followed by an ordered stream of additions and removals, within a context that can be refused, cancelled or ended. Motion is not continuity…

IETF
The Note Traveled With the Message. Its Authority Did Not.
RFC 5257 lets a mailbox attach durable metadata to a message: a private reminder, a shared assignment, an alternate subject or a label on one body part. The design is careful about who may read, write and copy those values. It does not say that the message sender wrote them…
History
The OAM Label Survived PHP. The Endpoint Still Had to Understand It: RFC 3429
In 2002, the Internet’s MPLS architecture had an awkward edge case: a network could remove the last forwarding label to save work at the destination hop, yet still need a special packet to reach that destination as OAM rather than ordinary user traffic. RFC 3429 assigned one…

IETF
The Parent Appeared in the List Because Its Child Matched.
RFC 5258 can return a mailbox-tree node that did not satisfy the requested subscription test and may not exist as a mailbox at all. The node is present to explain a matching descendant. A reliable client must preserve that cause instead of turning one query projection into the…

IETF
The Thread Looked Like History. It Was a View.
An email client can make a conversation look settled: one root, several replies, a clean order from first to last. RFC 5256 explains why that confidence must be earned. The server does not uncover a conversation. It selects messages, normalizes their fields, resolves…

History
The First Common AAL2 Profile Still Needed a Service Map: RFC 3441
Two gateways could agree on an AAL2 profile list and still not agree which rows inside the selected profile should carry voice, voiceband data or fax. RFC 3441 kept profile intersection, service preference, ATM bearer setup and a completed call as separate decisions.

IETF
The Interface Changed Language. The Mailbox Did Not Change Identity.
RFC 5255 lets an IMAP session change the language of explanations and the comparator behind search, sort and thread. Neither choice rewrites the mailbox or message. The operational burden is to remember which presentation and matching rules produced what the user saw.
IETF
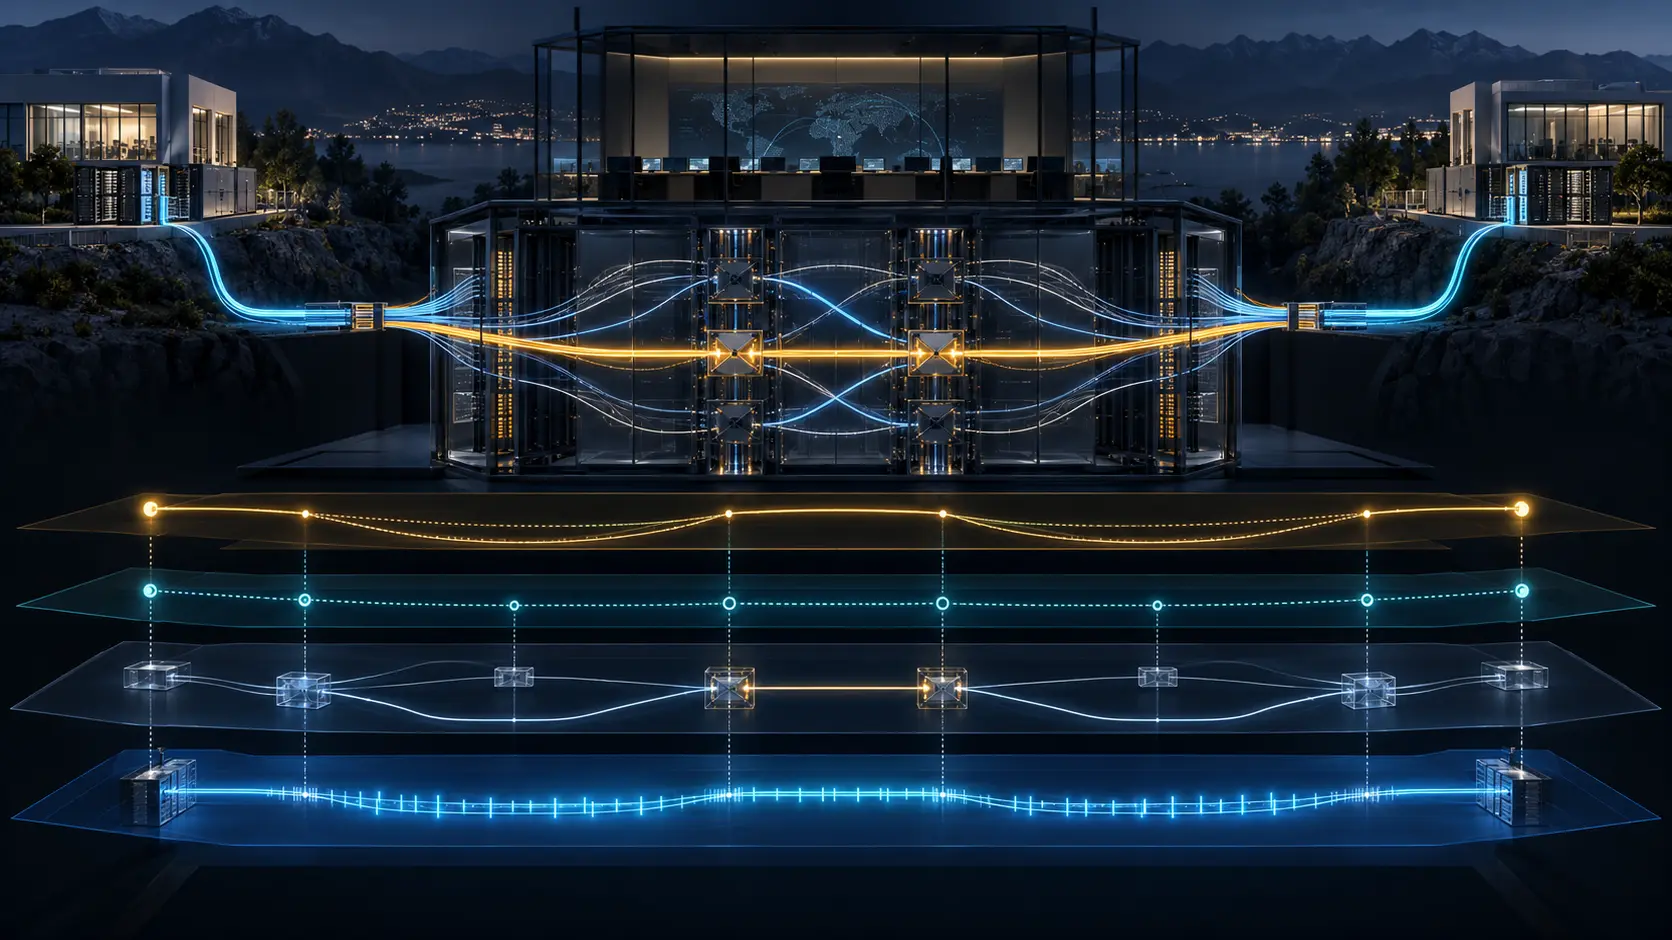
The Customer Chose the Endpoints. The Provider Chose the Path.
RFC 5253 gives an L1VPN customer a meaningful control: ask for a connection between two eligible customer edges. It gives the provider a different and deeper control: decide whether that request is permitted, which internal path carries it, which resources it consumes and how…