
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

History
The Save That Left the Page Intact: HTTP 204
HTTP 204 says an action finished without replacing its active view. Status marks completion, while headers carry post-action identity without response content.

History
The Connection That Was Not Authority: Why HTTP Needed 421
HTTP learned to save time by letting several named origins share one authenticated connection. Status 421 preserved the limit of that bargain: a channel can be reachable, secured and reusable in principle without being the connection context through which a particular origin is…
History
The Copy That Arrived as a Difference: HTTP 226
HTTP 226 lets a changed representation travel as instructions for a cached base. Base, delta message and reconstructed result retain separate identities.
CASE FILE
The Reflector Chose from the Wrong City: BGP ORR and the Authority to Compute Another Router’s Best Exit
A centralized route reflector can make a path decision from a place where no customer traffic ever flows. BGP Optimal Route Reflection lets it calculate from a client’s logical position instead. The mechanism restores a missing perspective, but it also creates a new delegated…

History
The Alias That Did Not Need a Second Walk: HTTP 208
WebDAV could expose one collection through two paths. HTTP 208 keeps the second path visible while omitting descendants already reported through the first.
CASE FILE
The Route Reflector Hid the Choice: BGP ADD-PATH and the Authority to Expose Alternatives
A route reflector can make a large network easier to operate by showing each client only the route it selected. That economy also removes choices. ADD-PATH creates a way to carry several paths for one prefix, but the protocol does not decide which alternatives deserve exposure…

CASE FILE
The Route Was Valid. The Reflector Called It a Loop: BGP Cluster IDs and the Authority to Discard Reachability
Every BGP session was Established. The customer prefix was valid at its source. Yet a regional reflector refused the route because a four-octet value in `CLUSTER_LIST` matched its own. The protocol had done exactly what it was told: an identity meant to stop loops had been reused…

History
The Preference Allowed to Lose: How Happy Eyeballs Races Paths
A valid IPv6 answer can still lead nowhere. Happy Eyeballs lets IPv6 start first, then allows observed reachability to win before the user pays a long timeout.

CASE FILE
The Policy Changed; the Routes Did Not: BGP Route Refresh and Re-evaluation Authority
Editing an inbound BGP policy changes a rule, not the routes already judged under the old one. To apply the new rule, a router needs the inputs again. Route Refresh lets it ask a capable neighbor to re-advertise the neighbor's current export set without destroying the session—but…

History
The Connection Beyond Its Address: Why QUIC Uses Connection IDs
Addresses and UDP ports can change while work remains. A QUIC Connection ID preserves continuity, but path validation and fresh identifiers bound trust.

CASE FILE
The Route Carried a Request, Not a Restraint: BGP NO_EXPORT and the Authority to Propagate
A route can arrive carrying `NO_EXPORT`, a name that sounds like a lock. It is nothing of the kind. The community tells a receiving network where the route is meant to stop, but the receiver's running policy still decides whether the value survives and whether the route leaves…

History
The Name Created by a Question: How DNS Wildcards Stay Bounded
A DNS wildcard can synthesize a name never stored in the zone. Exact nodes, empty non-terminals and delegation still decide when that default may answer.

CASE FILE
The Neighbor Suggested a Door; We Chose Whether to Enter: BGP MED and Advisory Authority
The Neighbor Suggested a Door; We Chose Whether to Enter: BGP MED and Advisory Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…

History
The Name the Connection Could Not Carry: Why HTTP Needed Host
TCP reached an address and HTTP named a path, but a shared server still lacked the site name the user chose. HTTP/1.1 made that authority explicit in `Host`.

CASE FILE
The Route Chose Three Times, the Neighbor Heard Once: BGP MRAI and Temporal Authority
A BGP router can change its mind several times while saying nothing new to one neighbor. The silence is not indecision. MRAI deliberately separates local route selection from external disclosure, trading the peer's freshest possible view for bounded UPDATE traffic and processing…

IETF
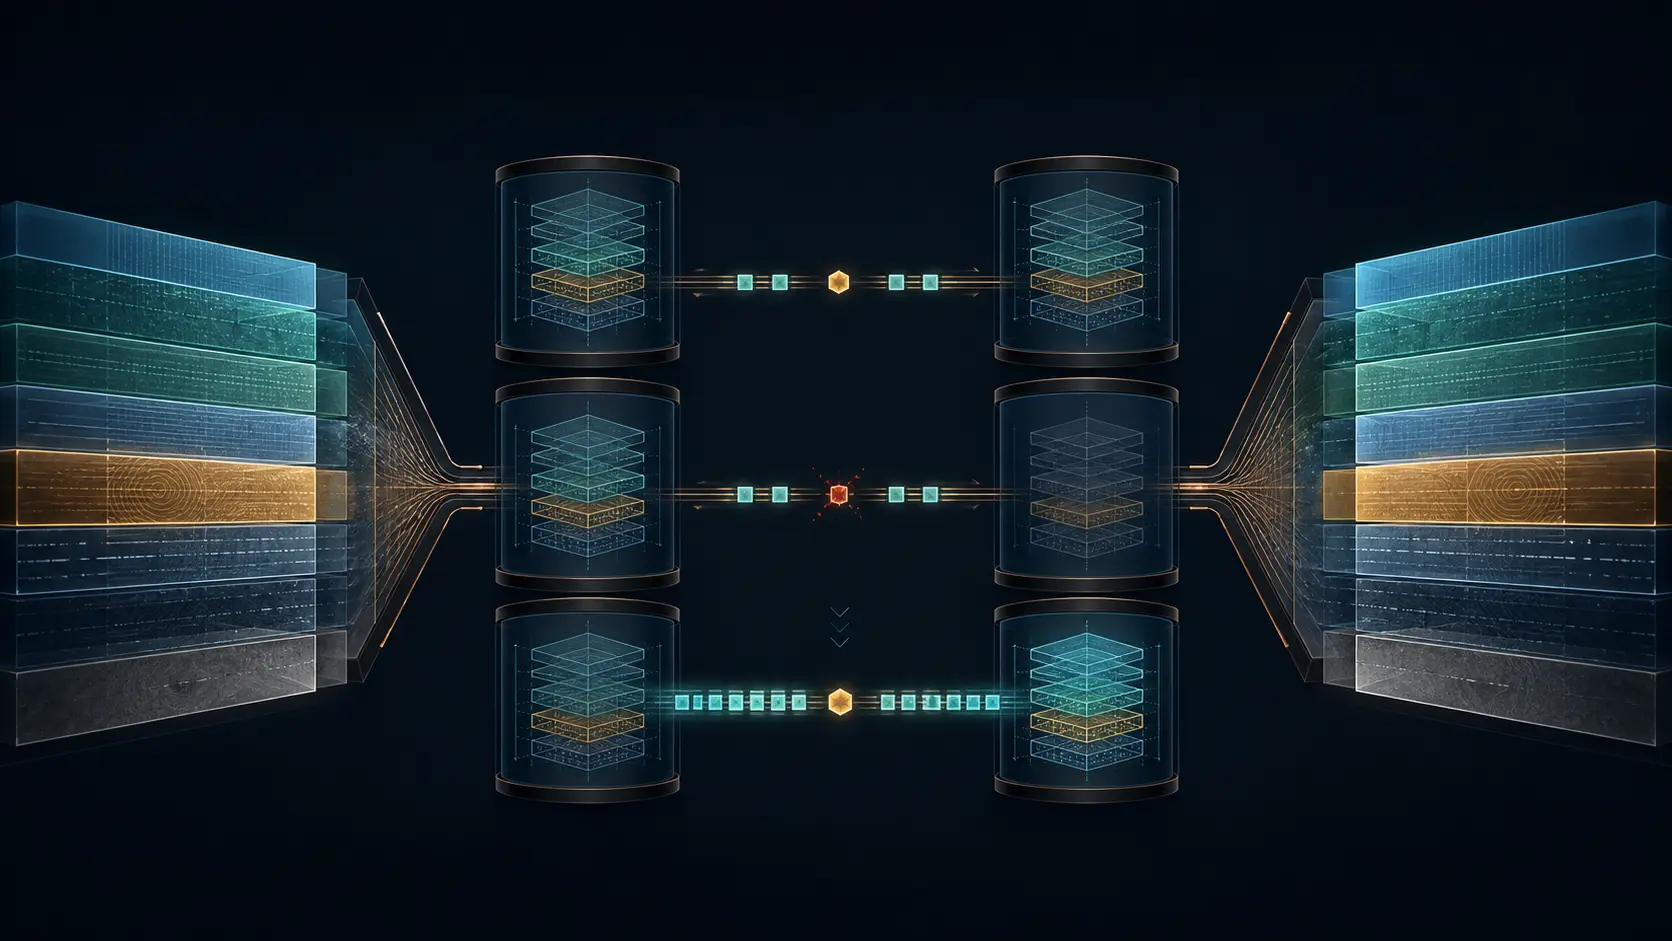
Ketan Talaulikar and the Prefix That Kept Its First Router's Name
An OSPF prefix can cross an area boundary without losing reachability and still lose part of its history. The new LSA names the Area Border Router that relayed it, not necessarily the router that first originated it. RFC 9084, edited by Ketan Talaulikar with four co-authors, adds…
History
The Header That Disappeared Between Packets
RFC 1144 made a 40-byte TCP/IP header nearly vanish on slow serial links by letting adjacent endpoints remember shared state and send only changes.
History
The Line That Looked Like the End in SMTP
SMTP ended unknown-length mail with a one-period line. Dot stuffing made that sentinel reversible; CHUNKING later moved the boundary to exact octet counts.

CASE FILE
The Server That Remembered Nothing: SYN Cookies and Stateless Admission
A listening server usually spends memory after the first knock and before it knows whether anyone can hear the answer. A SYN cookie changes that order. The server places a compact receipt for the unfinished connection inside its own sequence number, then waits for the requester…

History
Permission Was Not Acceptance: Why HTTP Added 100 Continue
HTTP 100 Continue let a server reject from headers before a large body crossed the network, while keeping interim permission separate from final acceptance.