
Topic
DNS Delegation Power
Within the Topic facet, DNS Delegation Power topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Global Regional ISP Trends
An NSEC3 Opt-Out Proof Does Not Secure the Delegation
A DNSSEC response can be correctly signed and still leave a child delegation insecure. Under NSEC3 Opt-Out, the signed proof says something precise about a hashed interval; it does not grant every delegation inside that interval a chain of trust.

Global Cloud Services Trends
Encrypted DNS Moves the Policy Boundary
Encrypting DNS closes a familiar surveillance gap, but it also changes which component gets to choose the resolver, apply local policy and explain a failure. The useful control is a resolver-policy map, not a transport checkbox.

Global Cloud Services Trends
The Four Clocks of a DNSSEC Key Rollover
A DNSSEC key rollover succeeds only when authoritative publication, resolver caches, the parent delegation and any configured trust anchors reach compatible states. A ceremony can finish while validation is still exposed.
IETF
RDAP Dropped Two DELEG Fields. Its Referenced Write Model Still Carries Them
Registration data moves through more than one protocol before it reaches a public query. A 4 September revision of the proposed RDAP extension for DNS DELEG has caught its read model up with DELEG-11 by removing two old fields. The EPP provisioning draft it cites still includes…

CASE FILE
The Parody Began After the Address Bar: PETA v Doughney
A joke can be obvious on a page and absent from the address that brought the reader there. That timing problem sat at the centre of *PETA v Doughney*. Michael Doughney said his “People Eating Tasty Animals” site parodied People for the Ethical Treatment of Animals. The Fourth…

Story
LACNIC WHOIS nslastaa Records the Last Successful Check, Not Current DNS Health
A date in a registry response can look like a present-tense assurance. LACNIC gives `nslastaa` a narrower meaning: it is the last date on which a correct reverse-DNS configuration was observed on a listed server. That historical success is useful evidence, but it is not a promise…
Global Cloud Services Trends
A DNS Cookie Is Not Client Authentication
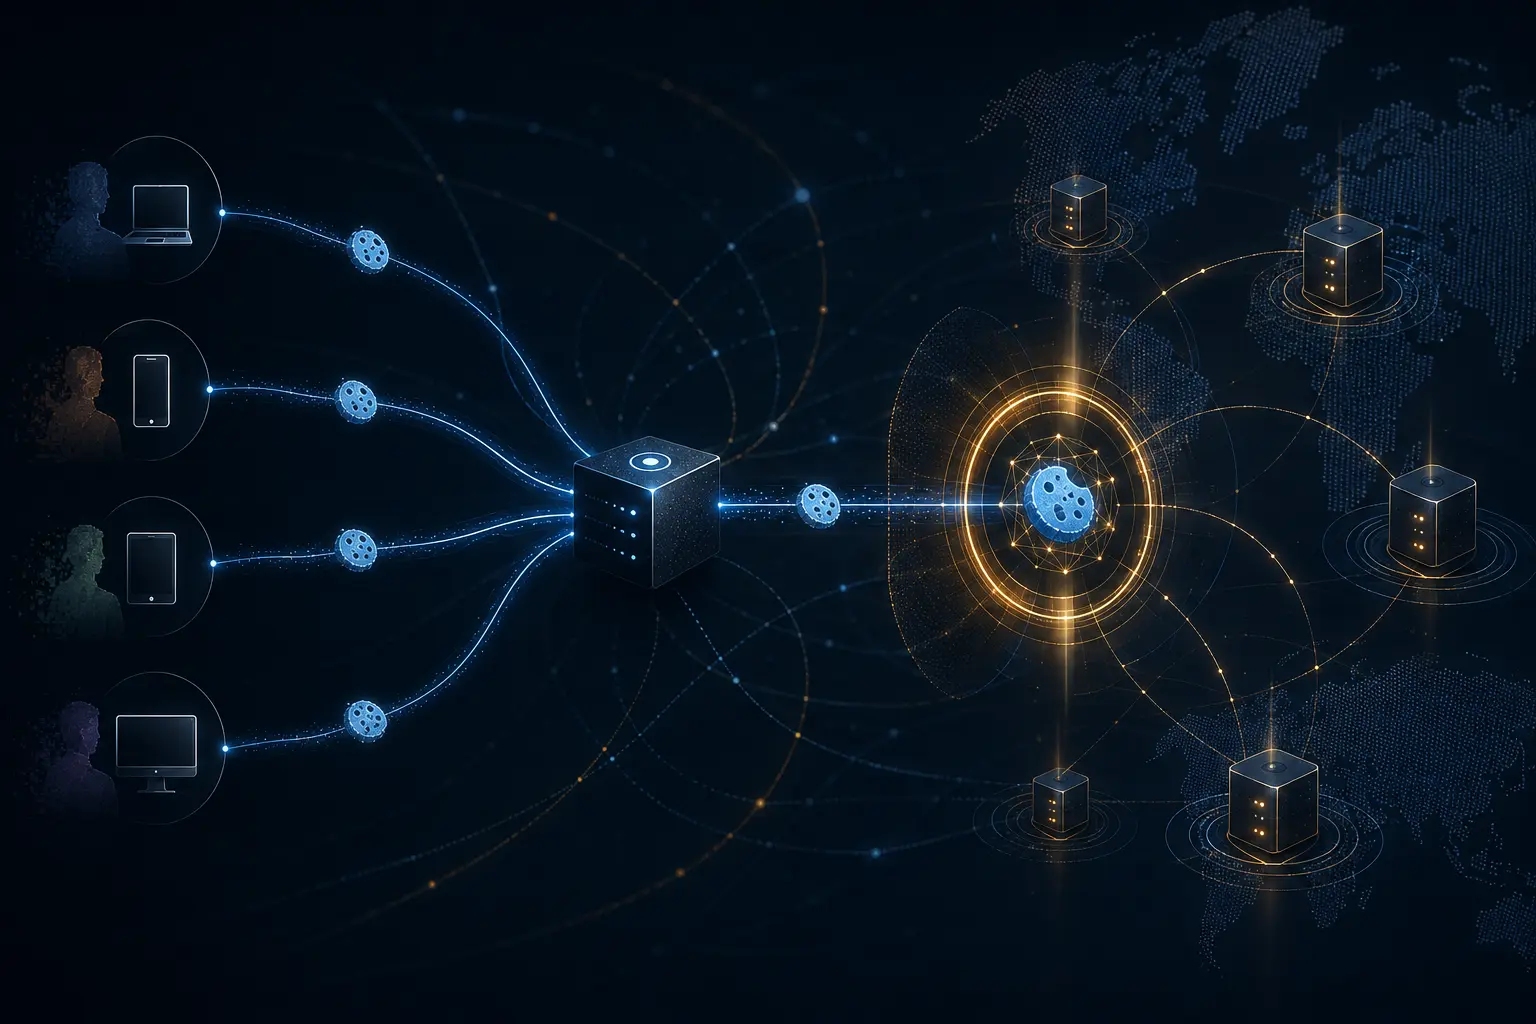
A DNS Cookie can help a server distinguish a request that carries previously issued protocol state from one that merely claims a source address. That is useful against several off-path attacks. It does not identify the person, subscriber or device behind a recursive resolver, and…

Story
APNIC Counted 9.7 Billion DNS Queries. It Still Cannot Name the Retry Layer
APNIC Labs changed only the answer and watched the traffic change with it. Silence brought 9.69 billion queries to an authoritative server; a positive answer brought far fewer per test. The ratio is startling and reproducible. The identity of the system that repeated the work is…

Story
The root KSK rollover makes resolver readiness the real continuity test
A DNS service can be healthy while users behind a stale validating resolver see failure. That is the operational paradox of a root key-signing-key rollover: the cryptography changes centrally, but continuity is decided across distributed resolver fleets.

CASE FILE
The Two Letters Were Not the Whole Case: Virtual Works v Volkswagen and the Call About `vw.net`
A two-letter domain can look like a conclusion. `vw.net` resembled Volkswagen's famous mark, and short addresses were scarce. But the Fourth Circuit refused to make resemblance do all the work. Its judgment followed a sequence: what Virtual Works' principals discussed when they…
Story
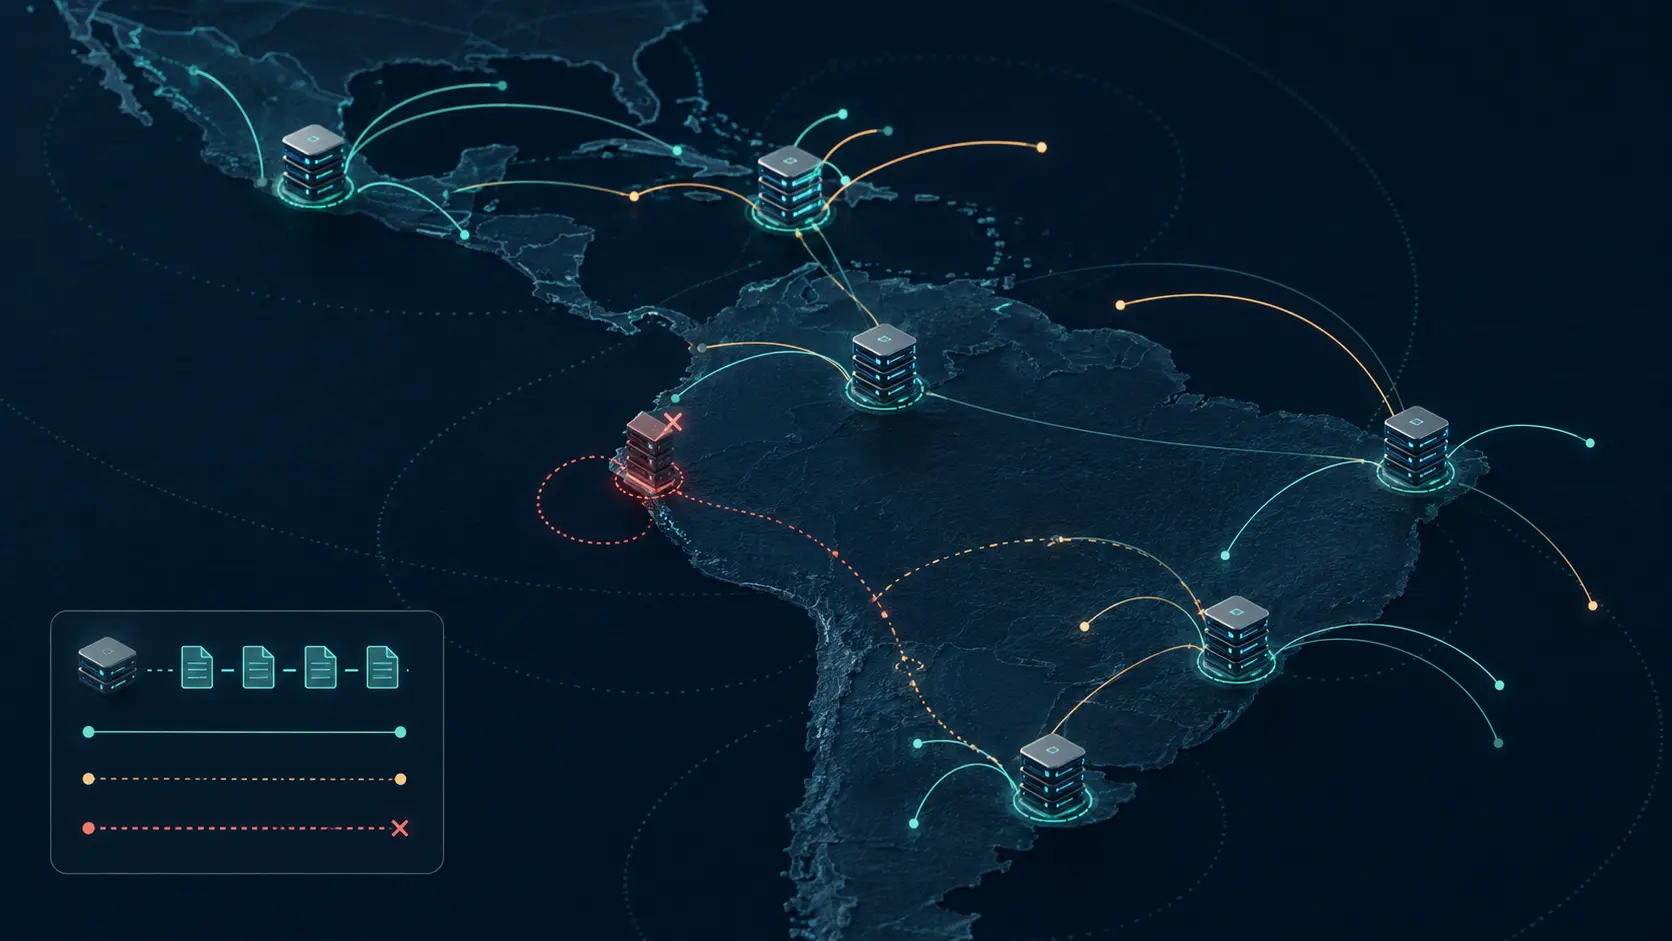
LACNIC’s reverse-DNS anycast turns registry continuity into a distributed control
Reverse DNS is easy to overlook until it stops answering. LACNIC’s use of anycast for delegated reverse zones shows why registry continuity is not a single-server property, but an operating discipline built from placement, routing, synchronization and observation.
IETF
An Extended DNS Error Explains Failure Without Authorizing a Different Answer
A DNS failure can be technically correct and operationally opaque. RFC 8914 lets a responder attach a more precise explanation to the result, but it deliberately leaves the result itself unchanged. That separation gives operators a useful observability channel—and creates a…

IETF
When a Drone ID Becomes a DNS Delegation: RFC 9886 and the Registry Chain Behind Remote ID
A Broadcast Remote ID can carry a compact DRIP Entity Tag (DET), while the public evidence needed to authenticate registry inclusion is distributed across reverse-DNS delegations, HHIT and BRID records, and a certificate chain. The practical question is therefore not only whether…
IETF
A Local Root Makes DNS Resilience an Operator-Controlled Failover Decision
RFC 8806 lets a recursive resolver answer root-zone questions from a complete local copy. The design can reduce dependence on a reachable remote root server and keep root queries off intervening networks. It also moves a consequential decision inside the operator’s own system…

CASE FILE
The Header Said NOERROR. The Signed Body Said the Name Did Not Exist: RFC 9824
A security pipeline closed a nonexistent-domain alert because the DNS header said `NOERROR`. The validating resolver had reached the opposite conclusion from the signed NSEC evidence: the queried name did not exist. Neither observation was fabricated. One component had read the…
History
The Name Existed in .US. That Did Not Mean the Zone Had Been Delegated: RFC 1480
Two names could appear equally real beneath `.US` in 1993. One might be a direct MX entry for a UUCP host; another might sit inside a branch whose manager ran its own name servers. The resolver made both names visible. RFC 1480 did not give them the same authority, network…

History
The TXT Record Carried an Attribute. DNS Did Not Supply Its Meaning: RFC 1464
RFC 1464 made an elegant bargain: put `name=value` inside a DNS TXT record and old name servers could carry a new attribute without learning a new resource-record type. The bytes became easy to publish and parse. The authority to define the name, interpret the value, trust its…

Story
A Locally Served DNS Root Has a Refresh Bill
Serving the root zone beside a recursive resolver removes many outward queries, but it does not remove network traffic. A new measurement highlighted by APNIC shows that the bill moves into the update loop—and that software behaviour can matter more than the name of the…

CASE FILE
The Registrant Was Abroad; the Dot-Com Registry Was in Virginia: CNN v CNNews.com
The Registrant Was Abroad; the Dot-Com Registry Was in Virginia: CNN v CNNews.com intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

IETF
A Resolver Can Choose Encryption Before DNS Operators Coordinate
Encryption between a user and a recursive DNS resolver does not protect the next hop. The resolver may still send the resulting query in cleartext to an authoritative server, exposing another part of the path to passive observation. RFC 9539 proposes an experimental compromise…