
Topic
DNS Delegation Power
Within the Topic facet, DNS Delegation Power topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Global Regional ISP Trends
A DNS NOTIFY Acknowledgment Is Not Proof the New Zone Is Being Served
The primary raises the SOA serial and sends DNS NOTIFY. Every listed secondary answers quickly, so the notification dashboard clears. Minutes later, one authoritative address still returns the old record. The acknowledgments were genuine; the conclusion drawn from them was too…

ICANN
Allison Mankin and the Name-Collision Sample That Could Not Prove Its Cause
A root server can record a query for a private-looking name with great precision. The record still cannot say which application produced it, who owns the broken dependency, how many users rely on it or what a future delegation would harm. Allison Mankin’s work on RFC 8023 helps…

CASE FILE
The Key Was Known. It Was Not Yet Trusted
A self-signed DNS update arrives at a parent carrying a new key and an instruction to delete the old one. The signature proves that somebody holds the new private key. It does not prove that this somebody may change the child's delegation. As DNSOP's 7 September Last Call reaches…

CASE FILE
The Final Dot Vanished. The Trust Boundary Moved with It
Two hostnames can lead DNS to the same node and still lead an application to different security decisions. As the DNSOP Working Group closes its 7 September Last Call on guidance for bringing domain names into applications, a recent curl flaw gives the abstract warning a concrete…
CASE FILE
The Relay Appeared on the Local Network. Who Authorized the Advertisement?
A MOQT client can now be told how to find a nearby relay, which protocol label to offer and which name to check in its certificate. The new draft is precise when DNS moves the socket. It is not yet precise about who may put the local relay in front of the client.
Europe and Middle East Cloud Services Trends
Genesis Cloud’s Network Control Plane: What AS209045 Records Can—and Cannot—Prove
A provider’s registry, peering and DNS records describe different layers of control. For Genesis Cloud, the useful question is not whether one record looks authoritative, but whether declared configuration, DNS authority, observed BGP activity and application reachability align.
History
The Name Looked Complete. The Resolver Still Rewrote It: RFC 1535
`UnivHost.University.EDU` looks like an address already supplied. To one 1993 resolver, it was only the beginning of a search. Before asking for the rooted name the user appeared to mean, the software could manufacture three longer candidates, cross from a locally managed suffix…

Leaders
Warren Kumari and the Design of DNS Failure You Can Survive
Warren Kumari’s standards work shows that resilient DNS is not the absence of failure. It is the disciplined design of limited continuity, explicit freshness, fallback and legible error signals.

Global Regional ISP Trends
A Published TLSA Record Is Not a Certificate-Acceptance Guarantee
A TLSA record can be present in DNS while a client still cannot use it, cannot match it, or is required to reject the connection. DANE assurance emerges only when DNSSEC state, record parameters, the served certificate chain, client policy and time all agree.
Global Regional ISP Trends
An NSEC3 Opt-Out Proof Does Not Secure the Delegation
A DNSSEC response can be correctly signed and still leave a child delegation insecure. Under NSEC3 Opt-Out, the signed proof says something precise about a hashed interval; it does not grant every delegation inside that interval a chain of trust.

Global Cloud Services Trends
Encrypted DNS Moves the Policy Boundary
Encrypting DNS closes a familiar surveillance gap, but it also changes which component gets to choose the resolver, apply local policy and explain a failure. The useful control is a resolver-policy map, not a transport checkbox.

Global Cloud Services Trends
The Four Clocks of a DNSSEC Key Rollover
A DNSSEC key rollover succeeds only when authoritative publication, resolver caches, the parent delegation and any configured trust anchors reach compatible states. A ceremony can finish while validation is still exposed.
IETF
RDAP Dropped Two DELEG Fields. Its Referenced Write Model Still Carries Them
Registration data moves through more than one protocol before it reaches a public query. A 4 September revision of the proposed RDAP extension for DNS DELEG has caught its read model up with DELEG-11 by removing two old fields. The EPP provisioning draft it cites still includes…

CASE FILE
The Parody Began After the Address Bar: PETA v Doughney
A joke can be obvious on a page and absent from the address that brought the reader there. That timing problem sat at the centre of *PETA v Doughney*. Michael Doughney said his “People Eating Tasty Animals” site parodied People for the Ethical Treatment of Animals. The Fourth…

Story
LACNIC WHOIS nslastaa Records the Last Successful Check, Not Current DNS Health
A date in a registry response can look like a present-tense assurance. LACNIC gives `nslastaa` a narrower meaning: it is the last date on which a correct reverse-DNS configuration was observed on a listed server. That historical success is useful evidence, but it is not a promise…
Global Cloud Services Trends
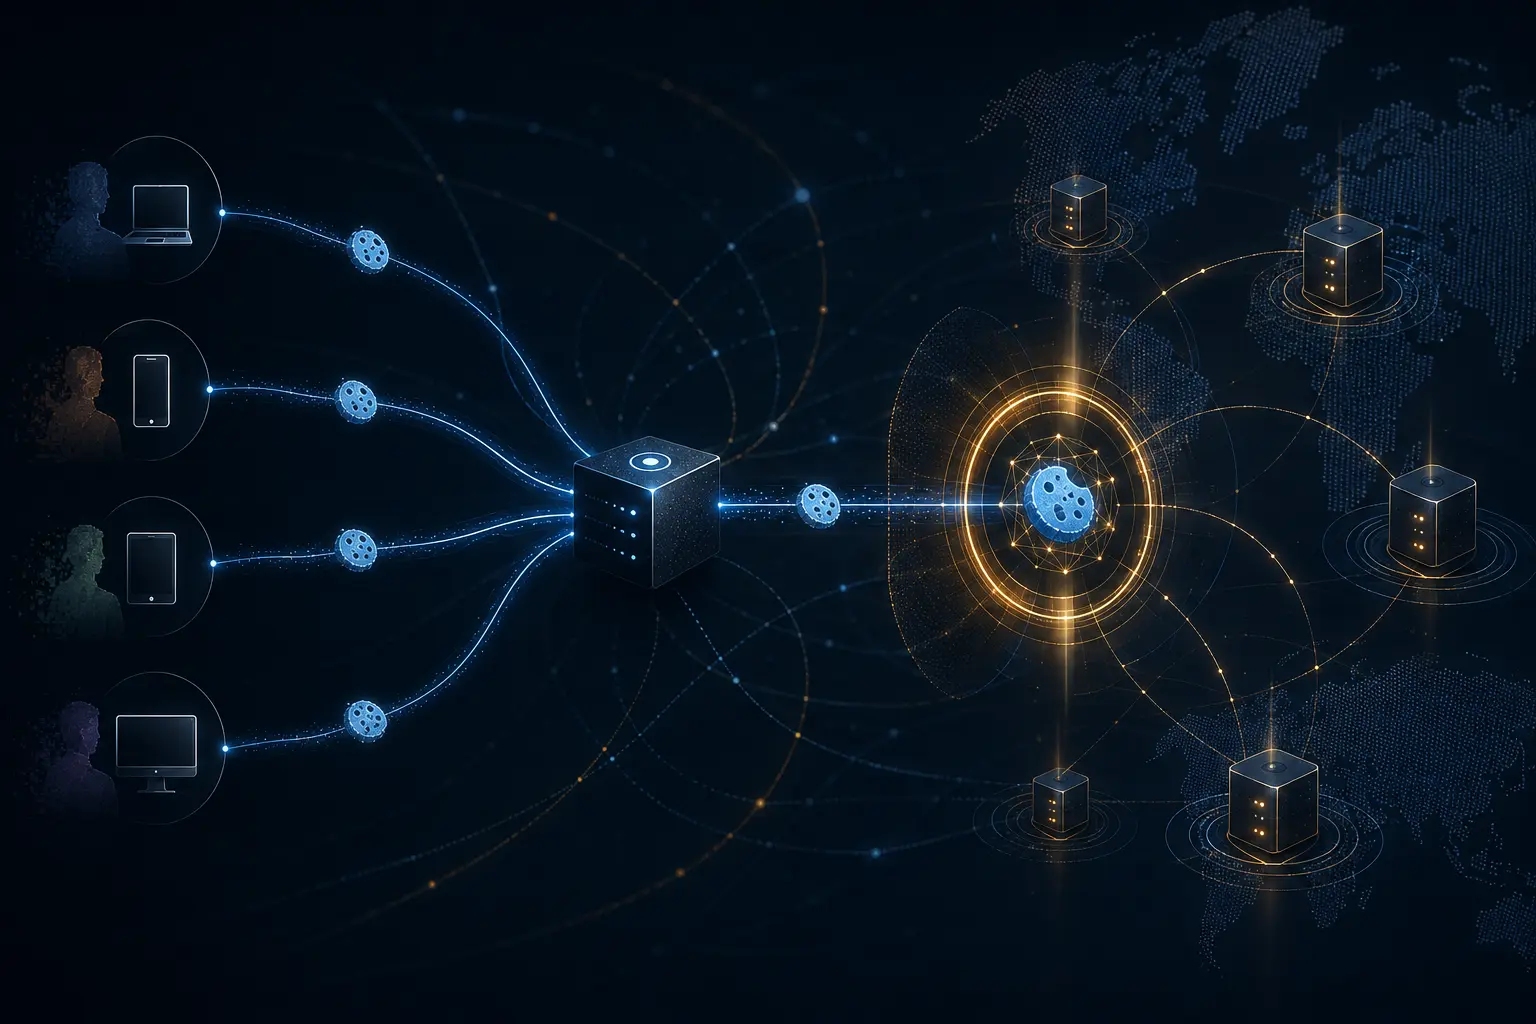
A DNS Cookie Is Not Client Authentication
A DNS Cookie can help a server distinguish a request that carries previously issued protocol state from one that merely claims a source address. That is useful against several off-path attacks. It does not identify the person, subscriber or device behind a recursive resolver, and…

Story
APNIC Counted 9.7 Billion DNS Queries. It Still Cannot Name the Retry Layer
APNIC Labs changed only the answer and watched the traffic change with it. Silence brought 9.69 billion queries to an authoritative server; a positive answer brought far fewer per test. The ratio is startling and reproducible. The identity of the system that repeated the work is…

Story
The root KSK rollover makes resolver readiness the real continuity test
A DNS service can be healthy while users behind a stale validating resolver see failure. That is the operational paradox of a root key-signing-key rollover: the cryptography changes centrally, but continuity is decided across distributed resolver fleets.

CASE FILE
The Two Letters Were Not the Whole Case: Virtual Works v Volkswagen and the Call About `vw.net`
A two-letter domain can look like a conclusion. `vw.net` resembled Volkswagen's famous mark, and short addresses were scarce. But the Fourth Circuit refused to make resemblance do all the work. Its judgment followed a sequence: what Virtual Works' principals discussed when they…
Story
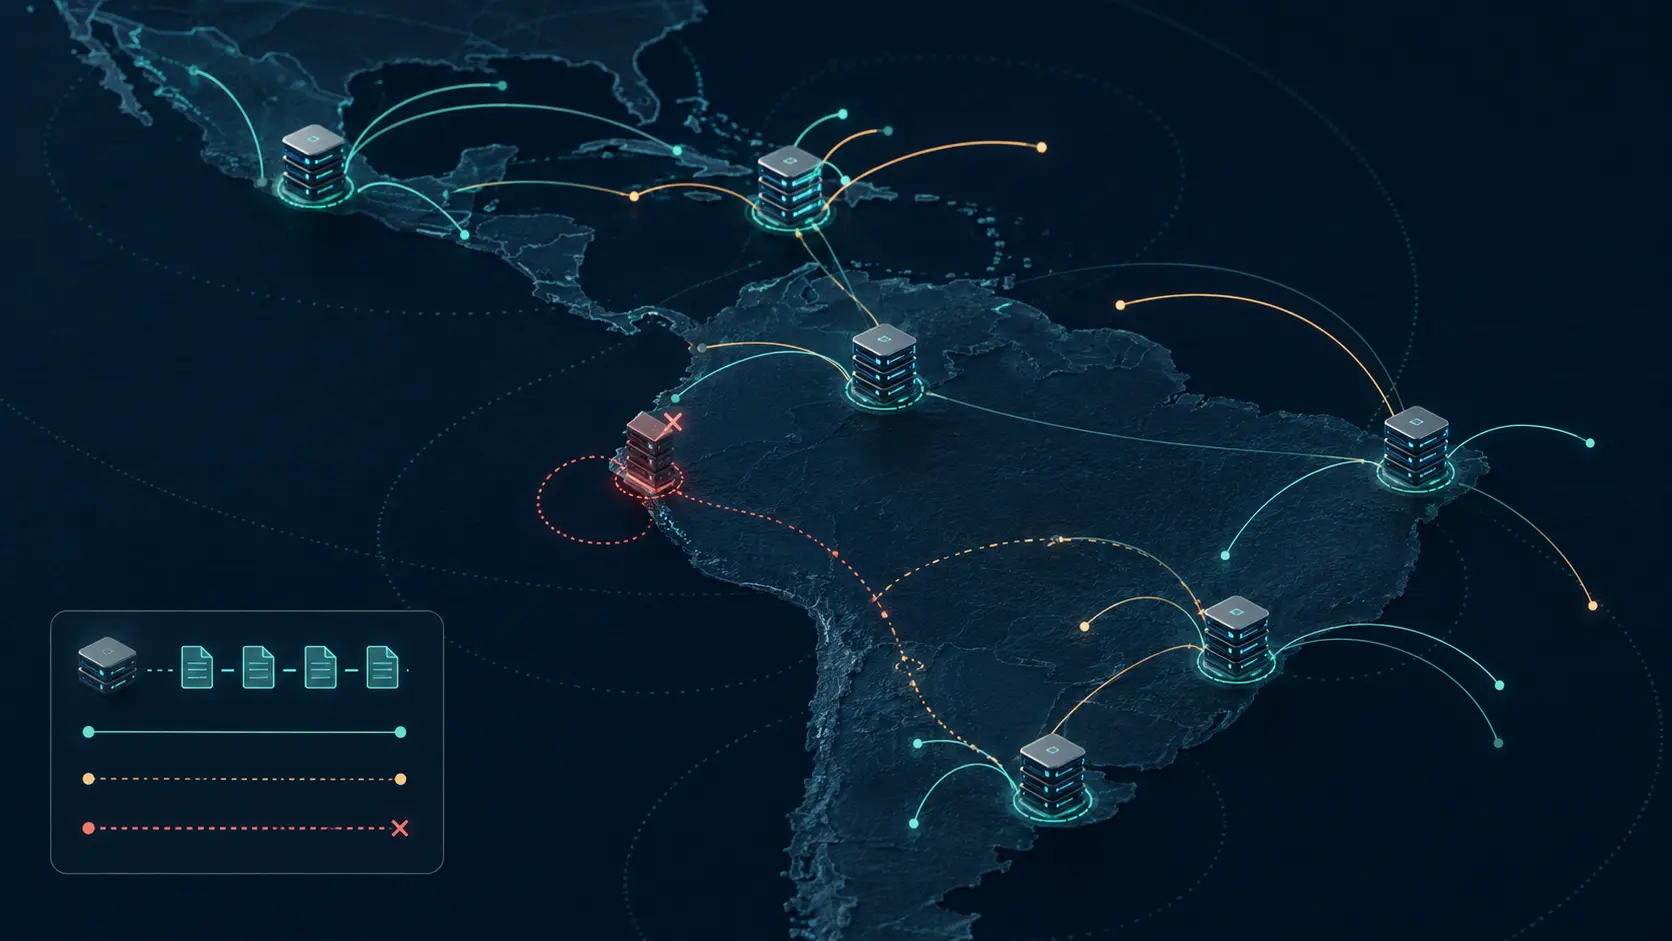
LACNIC’s reverse-DNS anycast turns registry continuity into a distributed control
Reverse DNS is easy to overlook until it stops answering. LACNIC’s use of anycast for delegated reverse zones shows why registry continuity is not a single-server property, but an operating discipline built from placement, routing, synchronization and observation.