
Topic
Digital Identity and Credentials
Within the Topic facet, Digital Identity and Credentials topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
History
DoubleClick Put Your Refusal in a Cookie. Blocking Cookies Could Erase It.
DoubleClick offered an opt-out cookie to remember that a browser did not want its tracking. A browser setting meant to reject cookies could remove that very marker. In January 2001, the Federal Trade Commission made the company promise to explain the trap: if a user later…
IETF
The Agent Had a Mandate. Its Identity Expired at the Gate.
A cross-domain software agent can carry a valid delegation and still lose the right to act in the time between checking its papers and issuing an access token. A 1 November Internet-Draft revision puts the agent instance's own identity expiry on the final authorization clock.
IETF
A Trusted Root Does Not Give a Bad Certificate a Second Turn
A TLS draft now draws a line through its own recovery mechanism: a certificate rejected for expiry, revocation or the wrong name cannot borrow the reputation of its root to claim a retry with that same trust-anchor ID.
History
The Browser Counted the Port and Ignored the Path
A web page needed a border. RFC 6454 drew it around scheme, host and port, leaving every path inside the same browser security unit.
IETF
A Vendor’s Subdomain Can Bless the Parent’s From Address
DKIM2’s new draft gives a parent domain a switch to stop its delegated subdomains authenticating the name readers see in From. The switch starts in the permissive position.
History
The @Handle Traveled; the Domain Kept the Address Book
WebFinger let software turn a familiar account name into a useful link. The domain behind the name still answered the question—and controlled the map.
IETF
The Prefix Asked for Every Track. The Token Covered Only Some.
MoQ's new Privacy Pass draft has a blunt answer for broad media requests: the credential must cover the whole branch, or the relay must keep every item it sends inside the smaller grant.
Europe and Middle East Institutional Trends
Finland Calls the Sender “Spam.” Your Restaurant May Still Have the Table.
Finland has tightened the identity check on business messages. A failed check can now erase a sender's name and replace it with “Roskaposti”, even when the message confirms a real booking.
IETF
The Attestation Trigger Lost Its Own Registry Label
An IETF draft has cut its proposed EDHOC remote-attestation labels from four to two. The trigger now travels under the same label as the evidence it requests, making message position and value do the distinguishing work.
Global Cloud Services Trends
Twilio's fraud refund promise has a Safe List trapdoor
Twilio offers to credit fees when Verify Fraud Guard misses SMS pumping. The promise has switches: Max protection must stay on, a claim has a short clock, and the affected numbers cannot use certain controls meant to prevent false positives. The settings panel is part of the…
Europe and Middle East Institutional Trends
One App, Three Age Ratings: Ofcom Finds the Store Gate Cannot Agree
An app can be 13+, parental guidance and suitable from age three depending on which store sells it. Britain’s regulator found that the same stores often decide who can download by asking users to state their own age.
IETF
The Authorization Server Delivers the Token. Who Gets the Trail?
An ACE draft shortens the route from permission to device. Its 2 November revision adds an operational ledger—and asks where a useful audit record becomes a map of clients.
IETF
One MLS Leaf Can Hide Several Devices. One Stolen Device Can Speak for All.
The latest MLS virtual-client draft offers a smaller, quieter group tree. Its bill comes due when a device is lost: every group behind the shared identity needs fresh keys.
IETF
The Quantum-Safe Password Still Introduces You in Plain Sight
A new experimental EAP proposal protects a recorded password exchange against future quantum attacks. Its first message still tells an observer who is talking, and its server keeps a verifier that becomes dangerous when stolen.
History
HSTS Guarded the Return Visit. Chromium Took the First.
A website could tell a browser to use HTTPS every time, but the instruction arrived in a response. On a first visit over HTTP, an attacker could reach the conversation before the rule did. Browser preloading moved that choice into the software shipped to the user.
IETF
Selo Lets Agents Bargain. Humans Must Move the Bank Details.
Two companies can let software negotiate access to their systems. When the supplier asks to change where the money lands, a new Internet-Draft puts people back between the request and the first payment.
CASE FILE
One Agent Holds the Key. Another Issuer Can Sign the Next Link.
Two proposed agent-delegation chains agree that a child should receive no more power than its parent. They disagree on the hand that signs the child into existence. A new independent implementation report makes that difference visible: in one model the parent holder must sign; in…
CASE FILE
The Agent Was Suspended. Who Told the Key Cache?
A provider can mark a hosted AI agent as suspended and strip its public identity document down to three facts. The agent's old signing key may still sit in a verifier's cache. A 31 October Internet-Draft revision addresses that awkward second half: make a fresh request for the…
History
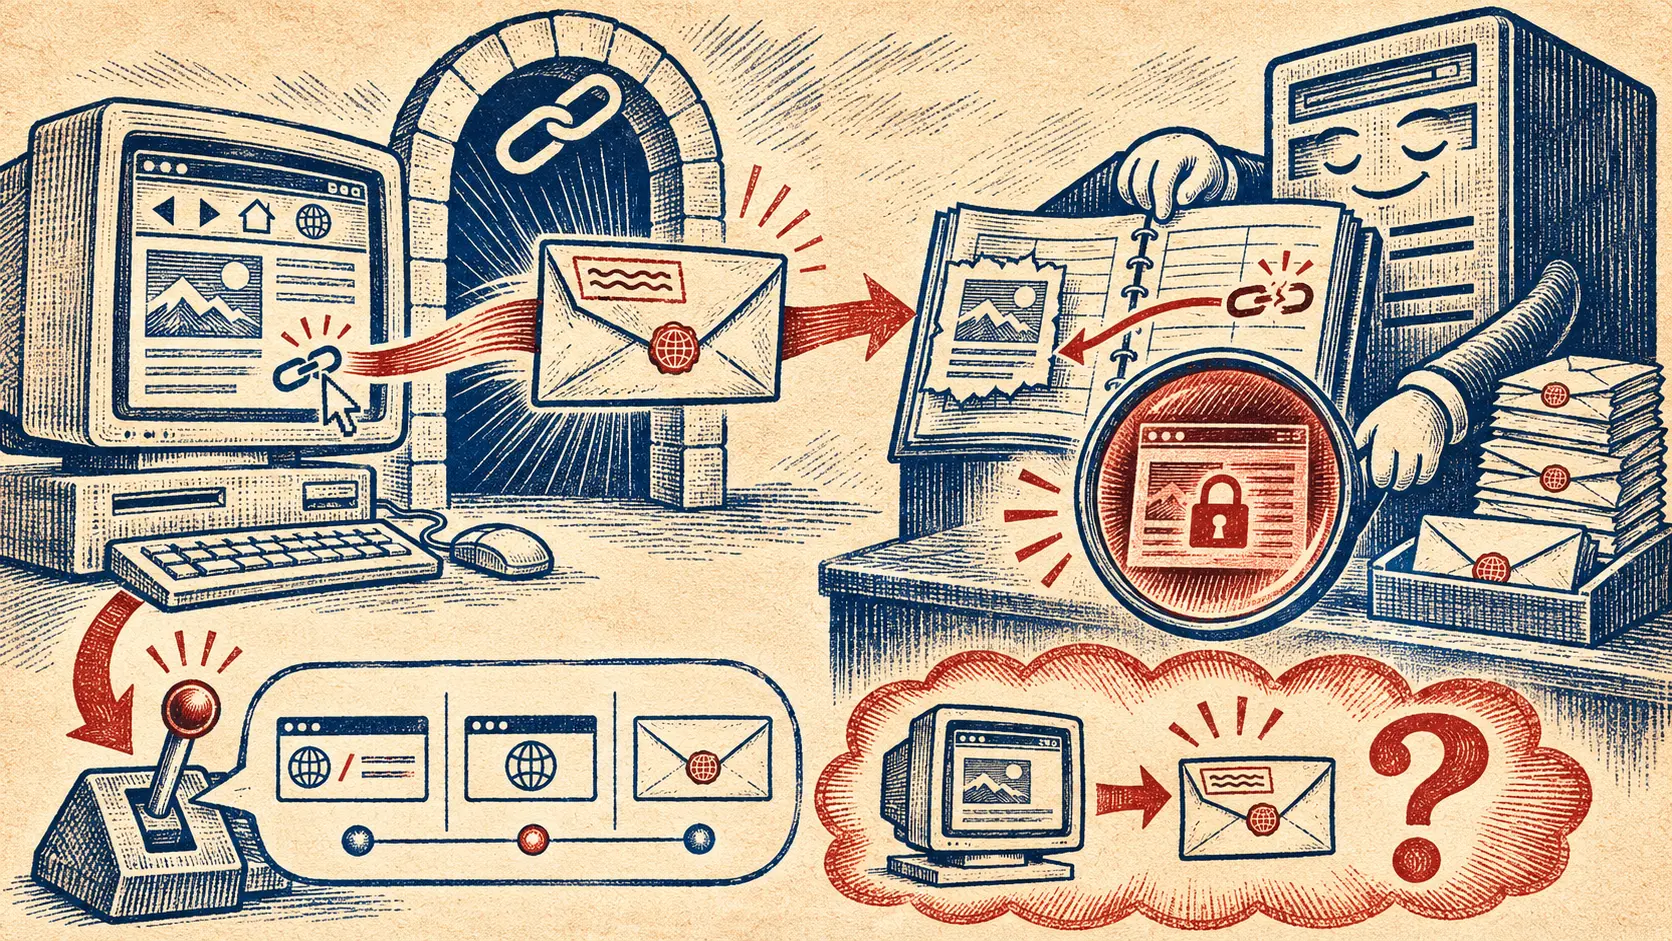
HTTP Gave Servers a Backlink. The Backlink Could Name a Private Page.
A click can arrive with a return address. In 1996, HTTP's `Referer` header let the receiving server learn which page supplied the link. That helped operators repair broken links and see how readers reached a document. The same specification warned that the source could be…
Story
RIPE Replaced the Database Cookie. Then the Web App Ran Out of Sockets.
The new login reached the RIPE Database website in September. A connection leak then stopped its web application for minutes while neighbouring database services kept running.