
Topic
Digital Identity and Credentials
Within the Topic facet, Digital Identity and Credentials topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Africa National Telecom Trends
Who opens Nigeria’s SIM outage lane? The rule gives two answers
Nigeria’s 2026 subscriber rules set a 10-minute probe, a one-week failure threshold and a 14-day limited-access window. One appendix gives the trigger to the Nigerian Communications Commission; another assigns approval to an unnamed “relevant governance body.”
History
The 90-Day Certificate Was a Bet on Automatic Renewal
In November 2015, Let’s Encrypt capped its certificates at 90 days and recommended renewal at day 60. The shorter clock was meant to limit damage from a compromised key or mistaken issuance. It also put recurring renewal on software’s schedule, while leaving administrators time…
History
The Empty Kerberos Field That Still Crossed a Border
In September 1993, RFC 1510 gave Kerberos V5 a way to carry authentication across administrative realms. Its `transited` field records intermediate realms; separate ticket fields identify both ends of the exchange. A direct hop between two realms can leave that field empty. The…
Global Cloud Services Trends
ServiceNow gives AI agents a passport. The border guard still works for the customer.
An open credential can name an agent and stop it. The published first draft cannot tell the agent which invoice, database or workflow it may touch. That is where the market for control begins.
Story
AI Agents Want IDs. ARIN Asks Who Gave the Registry the Job.
At ARIN 58, a call to watch new agent identifiers met a sharper question from the registry's chief: when does a number become an RIR's business?
IETF
The Group Can Grant Access. Can Its API Show the Guest List?
A door can record every new badge and still fail the head count. An individual IETF draft published on 28 October tackles that awkward case in SCIM: a client can change group membership while the service's group response may be too unwieldy to reveal the whole roster. The…
IETF
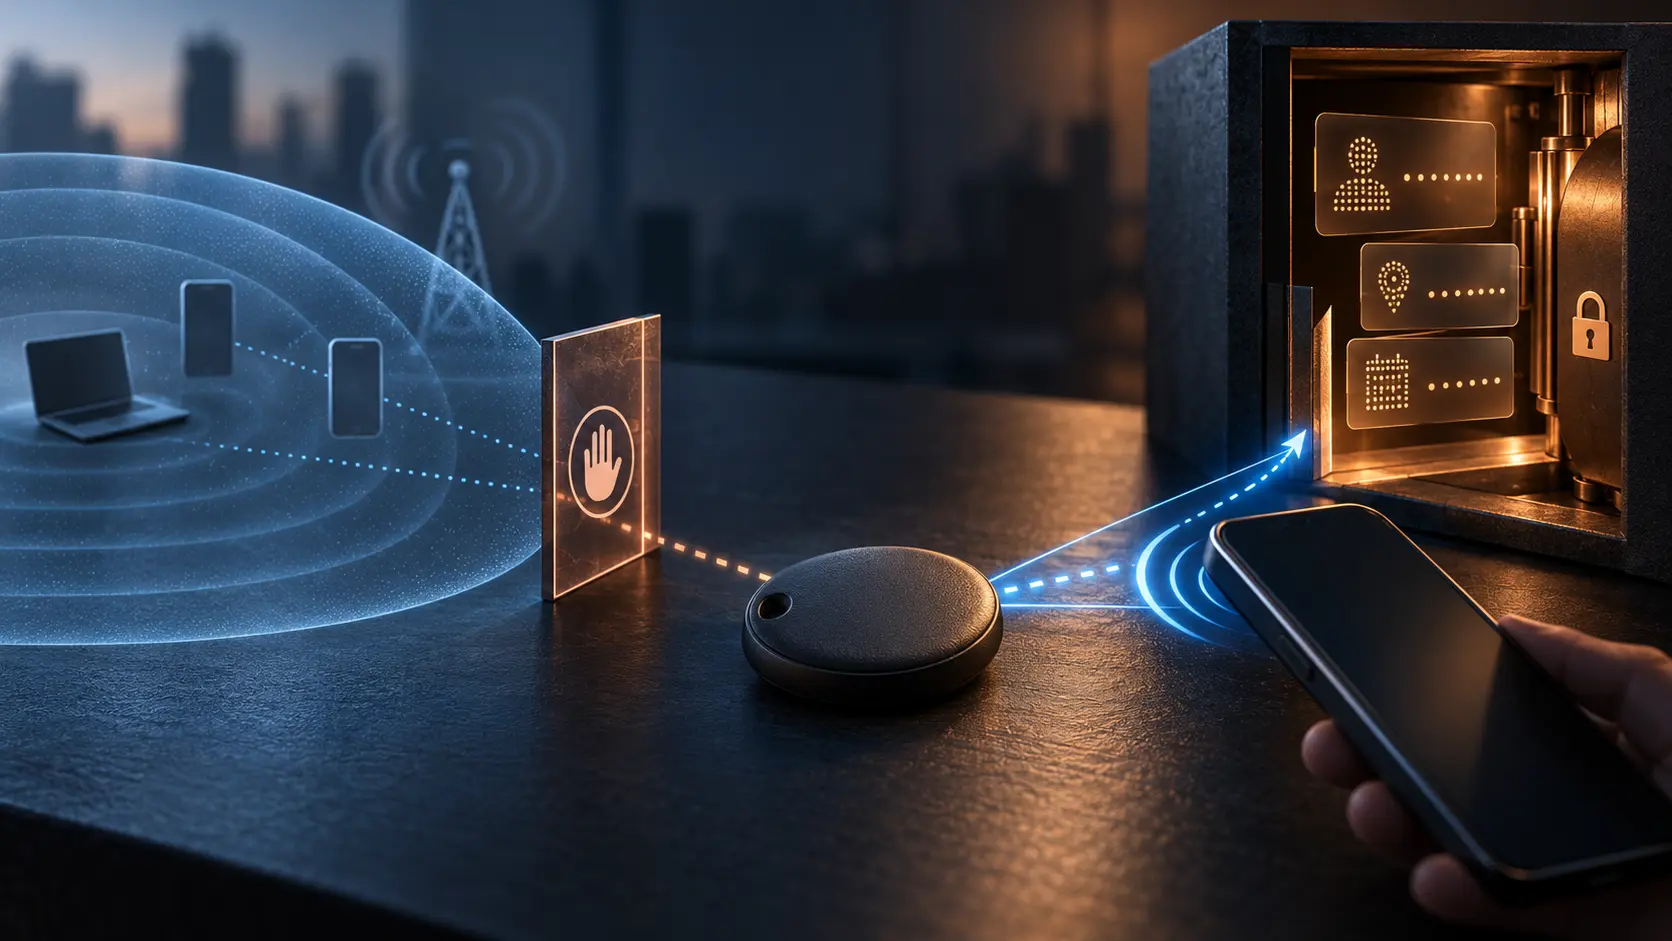
The Tracker Knows Its Owner. Who Gets the Last Four Digits?
A stranger's tracker turns up in a bag. The person holding it needs a usable clue; the owner of an innocently lost tracker needs protection from strangers harvesting clues. An IETF working-group draft tries to put a gate between those two needs. Its sharpest distinction is plain…
IETF
The Agent List on Your Office LAN Is Written by Everyone in the Room
A new IETF proposal makes nearby software agents discoverable without a central directory. The catch is sitting at the same table: any host on that local link can put a name in the list. A client that treats the list as an invitation to trust has already handed the wrong machine…
IETF
Two Clones Enter TLS. Who Gets a Name That Survives the Key?
An attestation can show that a confidential workload runs the approved image. Put two copies of that image online and the measurement gives them the same face. A new IETF individual draft asks whether a peer needs to recognize a particular copy—and who gets to give it a name that…

IETF
Two Keys Can Land on One IPv6 /64. Who Gets the Address?
A 27 October IETF proposal would derive a workload’s IPv6 subnet from its public key. It sounds like an address that carries its own identity card. The draft says a different key can match the same /64 subnet bits in about 2^16 trials under a /48 aggregate. The operator still has…
IETF
The Agent Got a Fast Lane. The User’s Approval Was on a List
A 27 October IETF proposal would let a personal AI agent get access to a service without interrupting its user each time. The switch is a pre-approved list held by an Agent Authorization Center. The service can receive a valid token even when the token does not say whether a…
IETF
Oblivious CoAP Hides the Sender. The Proxy Can Still Press Send Twice
A 28 October IETF proposal would let small devices make protected CoAP requests without telling the destination which device sent them. Its relay cannot read the payload, but it can repeat the envelope. The draft puts the replay decision at the receiving server—precisely where a…
IETF
Erase the Agent’s DNS Badge. Its OAuth Client Is Still the Off Switch
An October IETF proposal would let a service check whether an agent’s operator still stands behind it. The public DNS record points to an OAuth client; the operator’s authorization server issues the proof. Removing the pointer can make a new receiver ask fewer questions.…
IETF
Platform Support Is a Name Anyone Can Type. Who Gets to Wear It?
A new Internet-Draft brings sender impersonation inside job boards and marketplaces, where the platform controls the inbox and the trust label. Its two sharpest traps are technical: a Unicode skeleton match can miss a lookalike, and a validator can return a host name with an…
IETF
TLS Changed Its Key Schedule. The Authenticator Next Door Needs the Memo
A TLS cipher suite can keep its familiar hash label while a separate extension chooses a different key schedule. The 27 October XOF draft revision makes the resulting handoff explicit: an identity check running outside the TLS library needs to know which KDF was negotiated, and…
IETF
The Server Wants a Drawer in Your Device
A revised QUIC proposal lets your device carry a server's network memory into the next connection. The awkward questions are whose drawer it is—and whether “clear cookies” empties it.
IETF
The Terms Can Change. Yesterday’s Copy Needs a Witness.
A company controls the page where it posts its rules. An individual IETF draft proposes a way to keep the previous version visible after the page moves on: seal the exact text, publish the seal in a monitored log, and leave the old file where readers can retrieve it.
IETF
The Robot Recommended It. Who Said the Company Decided?
A new draft draws four lines through an agent's confident story: suggestion, organizational decision, real action and observed result. The dangerous shortcut is the missing signature between the first two.
IETF
Three Shops, One $100 Limit. Who Holds the Calculator?
An agent can buy dinner, book a ride and order supplies under one daily grant. The new draft's awkward question: which independent checkout knows what the others spent?
IETF
The Agent Reads Your Wish. The Checkbox Holds the Keys.
A new agent-credential proposal lets the user write down what they want. The system enforces the boxes they tick, the clock they set and the calls they allow.