
Time Horizon
Multi-year
Within the Time Horizon facet, Multi-year time-horizon intelligence organises articles by the period over which a signal is expected to matter. The page helps readers distinguish immediate operational changes from longer-cycle governance, investment, standards, and infrastructure shifts that may unfold across quarters or years. It connects timing assumptions with public evidence, related actors, market context, customer exposure, policy pressure, and infrastructure planning so readers can judge whether a development is urgent, strategic, or still waiting on confirming evidence. The page also explains how time horizon changes the meaning of a signal, which organisations may be exposed, and which infrastructure decisions require short-term action or long-cycle monitoring.

History
The Command That Gave Away the Connection: Why SMTP Replaced TURN with ETRN
A mail host called its provider and asked the line to turn around. The server could then send queued messages back over the same connection. The convenience hid an authority transfer: the caller had spoken a host name, but the protocol had not proved that it was entitled to…
Global Cloud Services Trends
Encrypted ClientHello Is Becoming a DNS-to-Edge Configuration Contract
A DNS operator can publish a fresh ECH public key in seconds. The matching private key may reach five edge clusters in seconds too, and the sixth after a maintenance window, a stalled secret distributor or the discovery that clocks remain an optional feature of distributed…

History
The Deadline the Relay Could Not Reset: How SMTP DELIVERBY Made Time Travel with the Message
A page that is useful at 16:58 can become an intrusion at 17:01. SMTP knew how to retry, but not why a message's value might expire. DELIVERBY let the sender attach a shrinking time obligation without buying priority or commanding another operator's queue.

History
The Identifier That Outlived Its Number: How POP3 UIDL Let a Client Remember Across Reconnection
On Monday a retained message is number 2. By Tuesday the message ahead of it has disappeared, so the same item is number 1. POP3 could name the position needed for this session, but an intermittently connected client needed something else: evidence that the message it saw after…
History
The Error Code That Asked the Blocker to Identify Itself
HTTP 451 could make a legal obstacle visible and name who enforced it. It could not compel disclosure, validate the demand or expose a block below HTTP.

Global Cloud Services Trends
A billion-dollar security alliance still needs an evidence ledger
NTT DATA and Palo Alto Networks have set a large commercial ambition for a deeper global alliance. The useful test is not the headline value but whether customers can see where platform responsibility ends, managed-service responsibility begins, and an outcome becomes measurable.
Global Institutional Trends
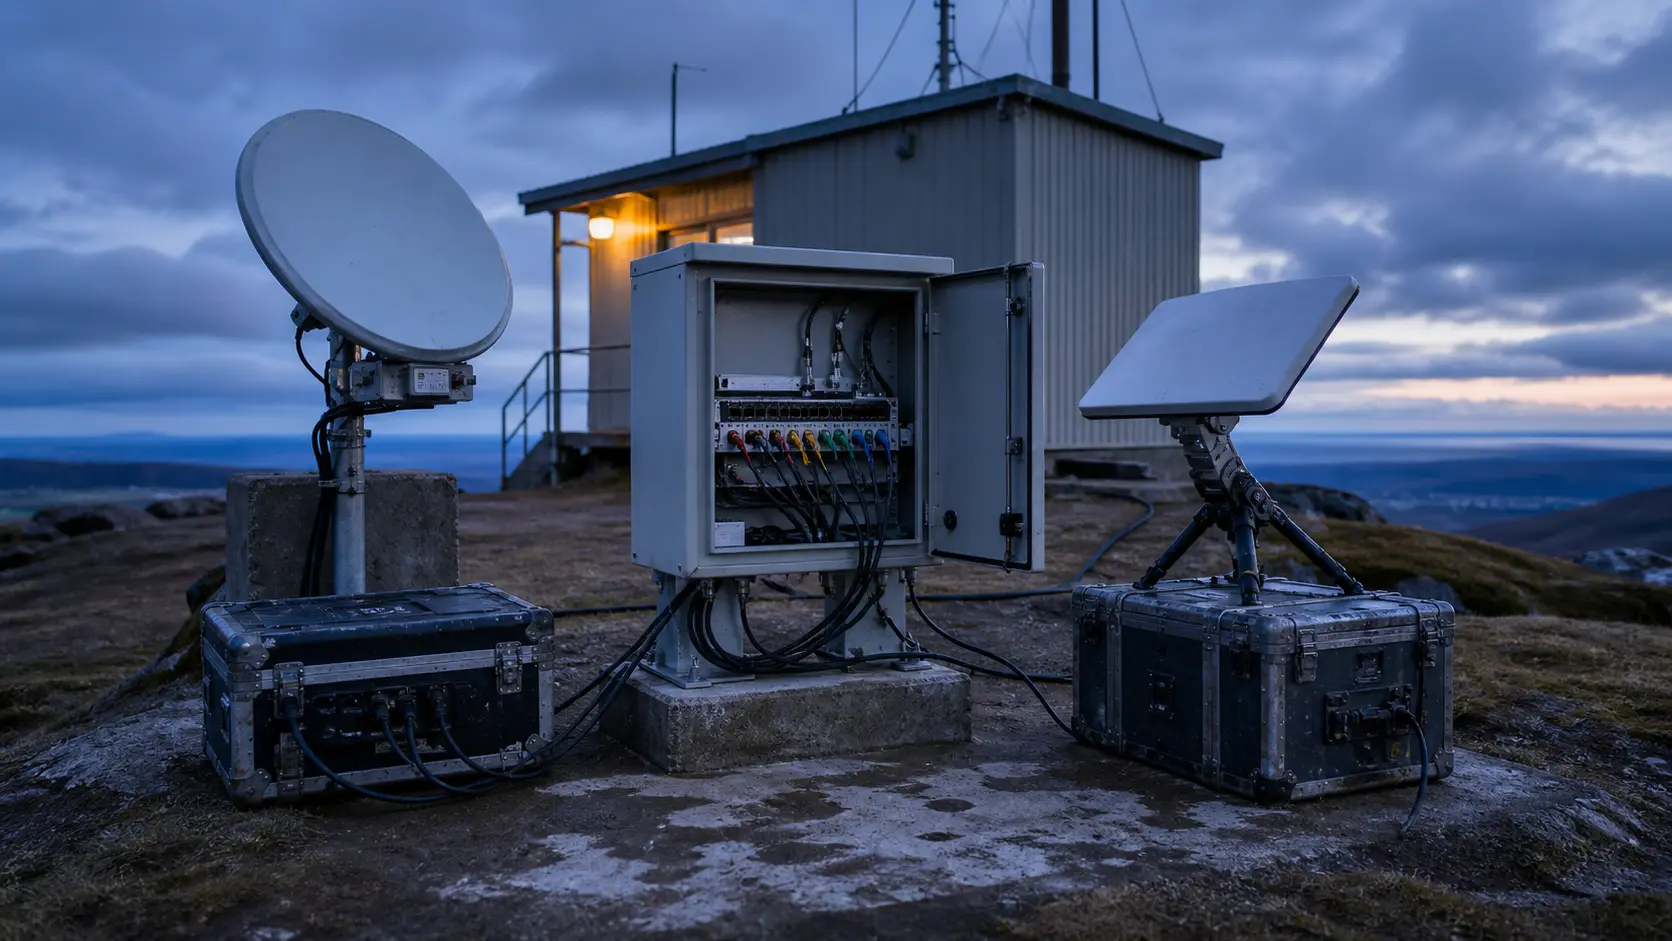
A satellite terminal is not public infrastructure until the buyer can leave
A dish on a roof is visible, countable and easy to photograph at launch. The harder public asset is the right to keep that site connected when the account holder changes, the subscription ends, a licence moves or the original supplier is no longer the right one.

History
When the Warning Reached the Wrong Server: The History of Path MTU Discovery
In 2015, Cloudflare found that a TCP flow and the ICMP warning meant to repair it could enter the same data centre and still reach different machines. The path had stated its limit. The server handling the connection never heard it. That incident exposed the institutional bargain…
Global Regional ISP Trends
IPv6 Extension Headers Are Becoming a Path-Compatibility Tax
The address answers. Ping works. Then the transport header moves 64 bytes deeper into an otherwise valid IPv6 packet, and the path goes quiet. Basic reachability survived; optional capability met the smallest parser on the route. It is a compact demonstration of how a protocol…
Asia-Pacific National Telecom Trends
Y.3335 standardizes the path, not the service
ITU-T has approved a common framework for low-latency, energy-efficient communication across operator domains. Y.3335 can align how networks describe the problem, but it does not yet prove that a multi-operator path will meet a latency target, consume less energy or survive a…

CASE FILE
The Public Path Looked Cleaner. Its History Had Been Rewritten: BGP Private-AS Removal and the Authority to Erase a Hop
The customer route arrived with three private autonomous systems in its path. At one public exit they vanished. At another, one survived. At a third, all three returned wearing the provider's number. Each operator had configured something called private-AS removal. The public…

History
The Last Uncompressed Line: How IMAP COMPRESS Changed Every Byte That Followed
The server's answer looked ordinary: a tag, `OK`, a short confirmation, then CRLF. That line was ordinary for the last time. If the client had asked for IMAP compression, the next server octet no longer belonged to the visible command language at all. A single successful reply…

CASE FILE
Trusted channels, no command: who can speak for FIRST in a cyber crisis?
A warning enters a trusted channel during a cross-border incident. Three decisions follow, and they do not belong to the same institution: who may enter the room, who may speak for the network, and who may act on an affected system. FIRST has substantial control over the first…

History
The Greeting That Had to Be Repeated: How STARTTLS Reset SMTP Trust
The first greeting crossed the network in the clear. So did the client's name and the server's list of abilities. When SMTP added encryption without abandoning its old port, the protocol could not simply wrap that conversation and pretend it had always been protected. It had to…

CASE FILE
Empowered without a vote: what the IGF Leadership Panel can actually command
The IGF Leadership Panel was designed to carry messages, recruit senior attention and find resources. Appointment by the UN Secretary-General gives that work institutional access. The operative rules still leave the annual programme with the MAG, execution with the Secretariat…

ICANN
The drafting room behind root advice: who controls the RSSAC Caucus pipeline?
Most RSSAC reports are built in a body far larger than the committee that formally approves them. The current rules make that division visible: experts may propose, research and draft; root server operator representatives keep the gates for admission, scope, amendment and…
ICANN
The security advisers the Board appoints: where SSAC authority stops
Three dates describe the gate. On 25 November 2025, an internal membership committee recommended three candidates. On 10 December, SSAC approved them by consensus. On 25 January 2026, the ICANN Board appointed them. Expertise entered through a committee of incumbents and acquired…

CASE FILE
A database governed by its entries: who gets a vote in PeeringDB?
A legal business entity can cross PeeringDB's membership threshold with two credentials: an active account and a representative or role subscribed to the governance list. The vote that follows is real. It is also only the first layer of authority over a database whose daily…
History
The Credential That Could Not Sign the Message: How SMTP AUTH Bounded Submission Identity
A password could open a mail submission gate. It could not sign the letter that passed through it. SMTP AUTH became useful precisely because the protocol kept those propositions apart: this client authenticated here; this account may act in certain ways; this message claims a…

Global Cloud Services Trends
The Denominator Behind the Uptime Promise
Cloud uptime percentages look like simple guarantees. They are not. As of 22 August 2026, the major public cloud SLAs examined here show something more precise: a bounded mechanism for allocating a narrow slice of outage risk, defined by what is measured, how the service must be…