
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

CASE FILE
A DNS Failure Drew 51 Queries. The Cause Was Still Unresolved
APNIC Labs sent several kinds of “no” from an experimental authoritative DNS service. Definitive negatives drew roughly four queries per test. `SERVFAIL` drew 51.73 and silence 83.46. Those are measurements of received traffic—not a verdict on which resolver layer multiplied it.
IETF
A captive portal needs an expiry date for its idea of a device
An address can legitimately pass from one terminal to another. The access system has to retire the old association, not merely recognize the address again. That small distinction connects network admission, accounting and privacy.
IETF
A Self-Signed Delegation Update Proves a Key, Not Its Authority
A DNS message can prove that its sender holds a private key and still leave the decisive question unanswered: who entitled that key to alter a child’s delegation? A DNSOP proposal for rapid child-to-parent updates makes that distinction explicit. Its lasting value will depend on…

CASE FILE
The Purge Was Accepted. The Downstream CDN Still Said No
Revision 20 of an IETF working-group draft follows a cache-control request past the reassuring `201 Created` response. In a CDN cascade, a later rejection has to return as data inside another provider’s status resource—and the provider that refused may remain unnamed.

IETF
A firewall’s speed belongs to a particular configuration
Two reports can describe the same appliance without showing that its protection and performance were achieved together. The missing connection is often the configuration between the tests.

CASE FILE
A Registry-Lock Quorum Counts Approvals, Not Independent Authority
Two approval messages can look like two-person control while both are recoverable through the same compromised mailbox. A proposed EPP registry-lock extension can count authorising contacts; the harder task is proving that the authorities behind those contacts were genuinely…

CASE FILE
The ICMP Error Named a Node. It Did Not Prove Which One
Revision 05 of an IETF draft makes node context harder to omit when an ICMP source address cannot do the diagnostic job alone. It also exposes a less comfortable truth: a more informative error can carry less of the packet that triggered it, and neither piece is authenticated.

IETF
Why a routing delay metric leaves the queue out
A network can need a stable signal for choosing paths and a sensitive signal for judging service. Trouble begins when a low-latency promise quietly treats them as the same measurement.

CASE FILE
An EPP Balance Can Gate Transactions Without Exposing the Ledger
A registrar can be told exactly how much spending room it has and still be unable to explain why the next domain command was refused. The emerging EPP balance mapping makes funding state operational; it does not turn that state into an accounting record.

CASE FILE
A Holder-Designated RDAP Referral Extends Discovery, Not Registry Authority
A Holder-Designated RDAP Referral Extends Discovery, Not Registry Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

Leaders
Mohamed Awang Lah and the Problem of Making Internet Capability Survive Institutional Change
The most revealing question about Mohamed Awang Lah is not whether he was important to Malaysia’s early internet development. The public record makes his importance difficult to dispute. The harder question is what, precisely, survived his successive roles: a person’s authority…

CASE FILE
A Successful EPP Server Validation Is a Dated Policy Verdict, Not a Health Certificate
The word “success” can survive on a dashboard long after the observation that produced it has expired. A new EPP proposal would make the result portable; governance begins by refusing to make it timeless.

CASE FILE
The EPP Same-Entity Set Turns an External Policy Into an Atomic Boundary
A registrar can submit a command naming one domain while the repository must decide whether that command reaches a set too large to list. The protocol message is visible; the rule that draws its boundary may sit somewhere else.
History
The Broadcast Packet That Carried Its Own Guest List
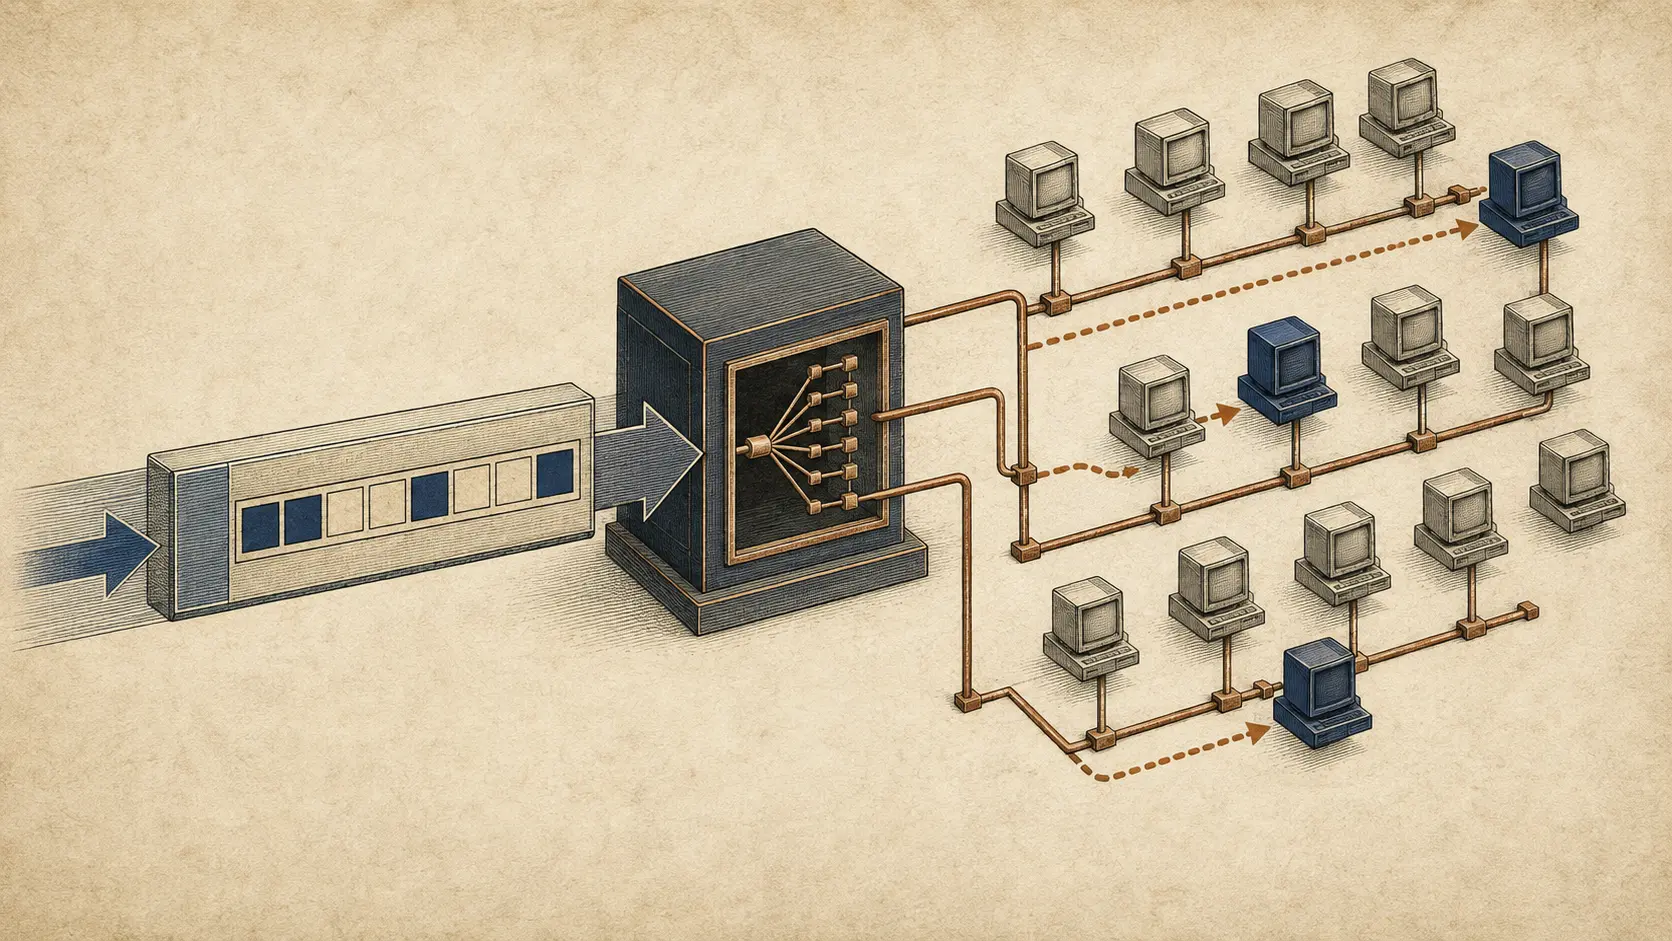
One UDP datagram approached a remote subnet as a broadcast, yet it carried a private instruction inside its IPv4 header: these hosts may listen; the others must stop. Selective Directed Broadcast Mode tried to make the packet itself serve as a temporary membership list.

IETF
One CA Name, Several Ways to Issue
A buyer reviewing certificate operations asks a simple question: if DNS authorizes one certification-authority name with an account and a validation method, does that restriction govern every issuing system behind the name? RFC 8657 makes the answer consequential. A shared CA…

CASE FILE
The EPP Extension Registry Records Coexistence, Not a Winner
Two extensions can solve much the same provisioning problem, use different XML namespaces and both deserve a place in the same public registry. That is not a defect in the catalogue. It is the governance fact the catalogue must preserve.

IETF
The Price of Keeping Only the Latest Notification
Web Push can spare a returning device a backlog of obsolete updates. The difficult decision is not how to replace a waiting message, but which information the business can afford to leave behind.

CASE FILE
Every Outer Bundle Was Delivered. The Inner Bundle Still Had Not Been Received
Bundle-in-Bundle Encapsulation gives a delay-tolerant network two journeys to observe. The outer bundles can reach their configured endpoint one by one, each with a valid delivery report, while the bundle carried inside them never reaches the Bundle Protocol Agent. The new DTN…

CASE FILE
A DNS Filtering Notice Is a Chain of Three Decisions, Not One Explanation
A link that explains why a name was filtered looks like a simple act of transparency. By the time it reaches a user, however, a resolver, an application and the user have each made a different decision. The record must preserve all three.

IETF
The Mount Point Changes What a Valid Configuration Means
A reusable network model carries its rules with it. It does not necessarily carry all the data against which those rules will be judged. YANG Schema Mount makes that distinction an operational responsibility.