
Primary Domain
Internet Infrastructure
Within the Primary Domain facet, Internet Infrastructure intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.

History
The Server Returned the New Name: How UIDPLUS Made IMAP Mutation Verifiable
The upload had succeeded. The message was in the mailbox. Yet the client still lacked the one fact it needed for its offline ledger: which UID had the server assigned? Before UIDPLUS, a positive result could confirm the mutation while withholding the durable local reference…

History
The Command That Gave Away the Connection: Why SMTP Replaced TURN with ETRN
A mail host called its provider and asked the line to turn around. The server could then send queued messages back over the same connection. The convenience hid an authority transfer: the caller had spoken a host name, but the protocol had not proved that it was entitled to…

History
The Deadline the Relay Could Not Reset: How SMTP DELIVERBY Made Time Travel with the Message
A page that is useful at 16:58 can become an intrusion at 17:01. SMTP knew how to retry, but not why a message's value might expire. DELIVERBY let the sender attach a shrinking time obligation without buying priority or commanding another operator's queue.

History
The Identifier That Outlived Its Number: How POP3 UIDL Let a Client Remember Across Reconnection
On Monday a retained message is number 2. By Tuesday the message ahead of it has disappeared, so the same item is number 1. POP3 could name the position needed for this session, but an intermittently connected client needed something else: evidence that the message it saw after…
History
The Error Code That Asked the Blocker to Identify Itself
HTTP 451 could make a legal obstacle visible and name who enforced it. It could not compel disclosure, validate the demand or expose a block below HTTP.

History
The Last Uncompressed Line: How IMAP COMPRESS Changed Every Byte That Followed
The server's answer looked ordinary: a tag, `OK`, a short confirmation, then CRLF. That line was ordinary for the last time. If the client had asked for IMAP compression, the next server octet no longer belonged to the visible command language at all. A single successful reply…

History
The Greeting That Had to Be Repeated: How STARTTLS Reset SMTP Trust
The first greeting crossed the network in the clear. So did the client's name and the server's list of abilities. When SMTP added encryption without abandoning its old port, the protocol could not simply wrap that conversation and pretend it had always been protected. It had to…
History
The Credential That Could Not Sign the Message: How SMTP AUTH Bounded Submission Identity
A password could open a mail submission gate. It could not sign the letter that passed through it. SMTP AUTH became useful precisely because the protocol kept those propositions apart: this client authenticated here; this account may act in certain ways; this message claims a…
Global Institutional
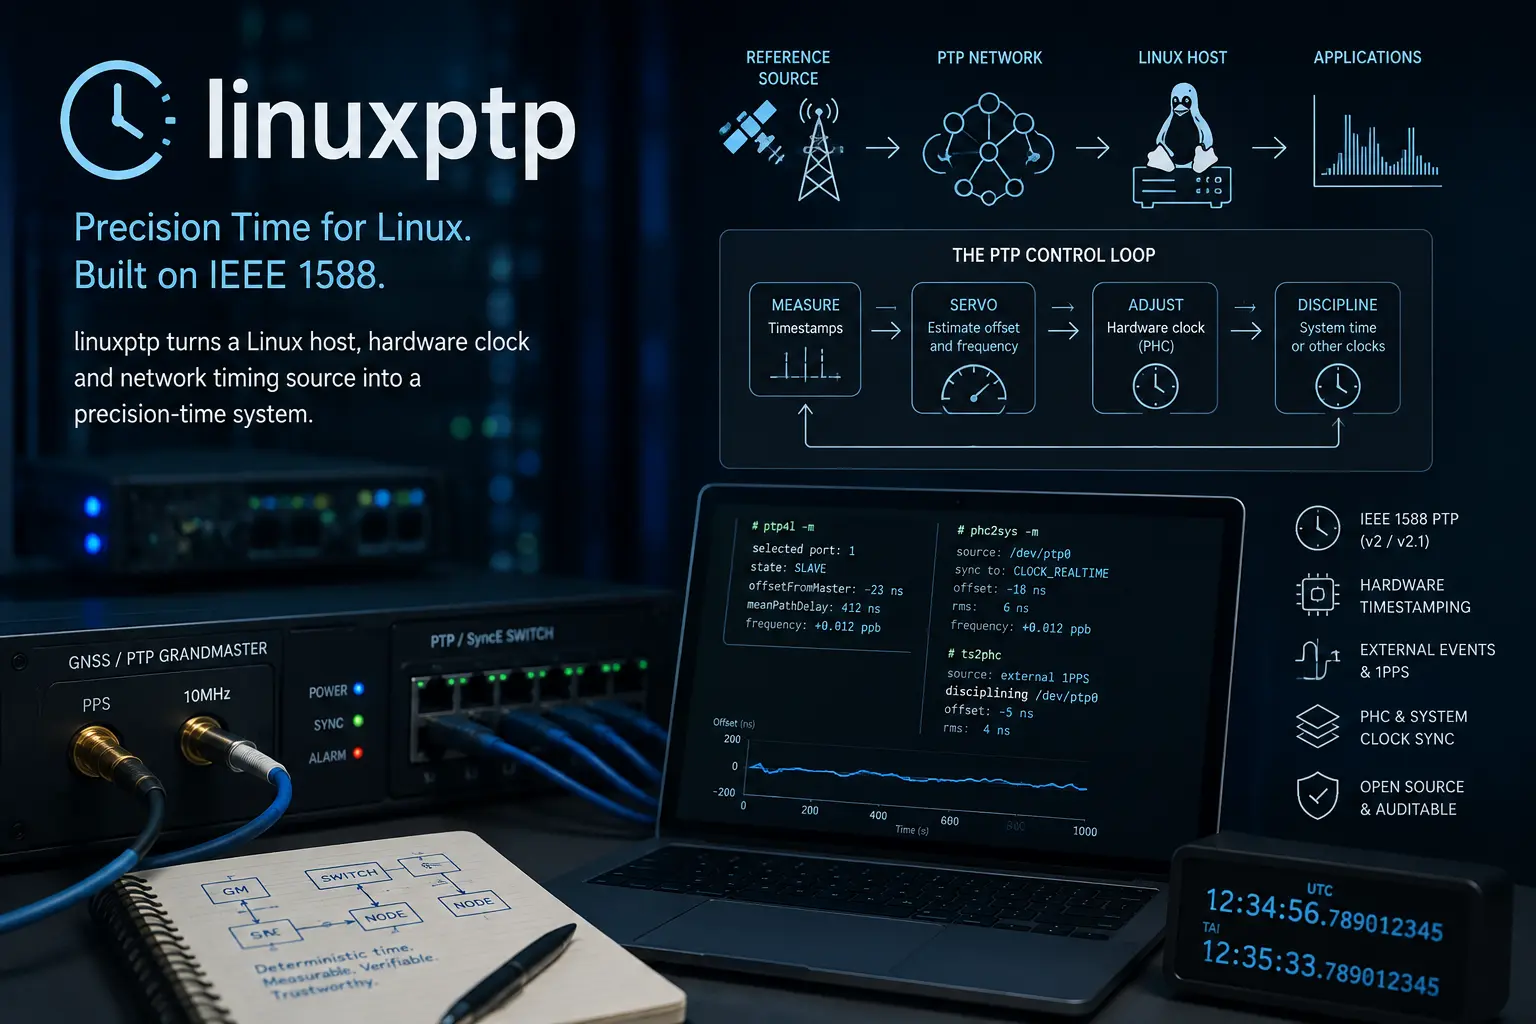
linuxptp and the control loop behind precision time
linuxptp turns a Linux host, hardware clock and network timing source into a precision-time system. Its daemons coordinate IEEE 1588 state, packet timestamps, servos and system clocks, but software alone cannot manufacture accuracy: the result still depends on NICs, oscillators…

Academics
Laurent Vanbever and the network that must be tested while it changes
Laurent Vanbever’s work treats network configuration as executable software whose failures can emerge before, during or after deployment. From safe routing migrations and configuration synthesis to runtime BGP detection and energy-aware operations, his research at ETH Zurich asks…

History
The Address That Could Not Be Downgraded: How SMTPUTF8 Made the Route Part of the Name
An accented display name could cross old email systems because it was decoration around an ASCII address. A non-ASCII mailbox name was different: it was the destination itself. SMTPUTF8 made every relay prove that it could carry that identity without inventing another one.
Academics
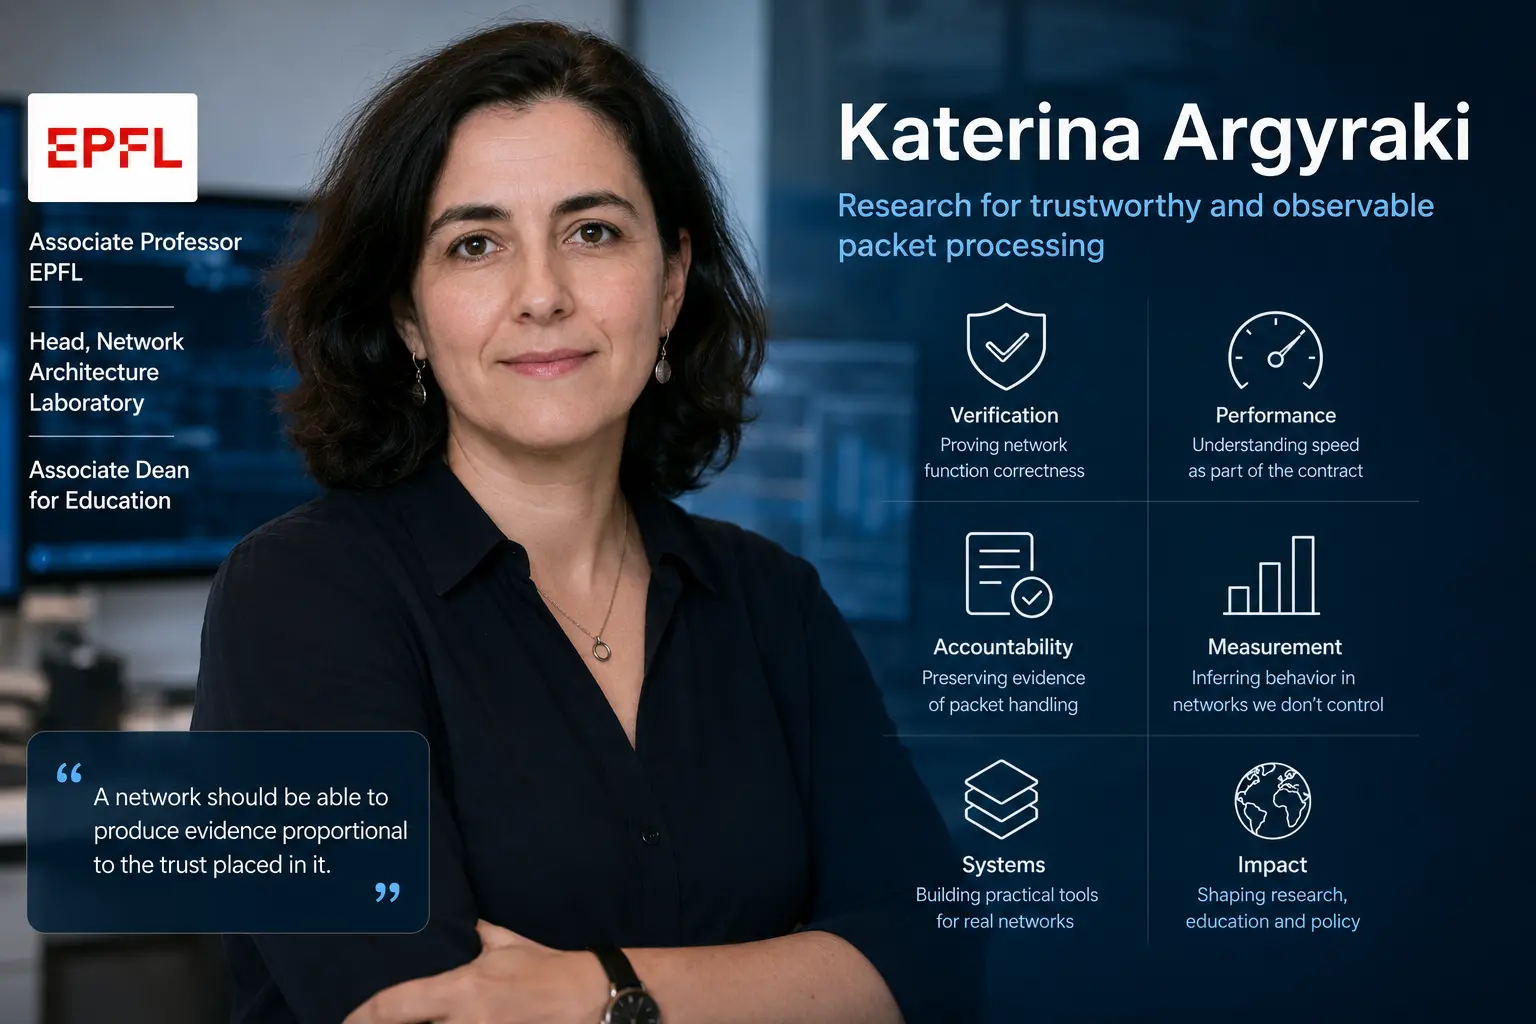
Katerina Argyraki and the search for proof in packet forwarding
Katerina Argyraki’s research follows a problem that becomes harder as networks become more programmable: a packet-processing system may be fast and flexible, yet operators and users often have little evidence that it behaved correctly. Her work at EPFL connects software-router…

Global Institutional
FreeRADIUS and the trust decisions behind network access
A network login may be decided in a few packets, but the trust behind it can span certificates, directories, access devices, roaming partners and accounting systems. FreeRADIUS makes that policy inspectable and programmable, while leaving operators responsible for the legacy…

Creators
Dave Maltz and the operating stack behind Azure networking
Dave Maltz’s role at Microsoft is best understood through the breadth of the organisation he leads. Azure Networking spans customer-facing services, DNS, security, distributed control, host offload, switch software, data-centre fabrics, wide-area links and optical systems. That…

History
The Receipt That Could Not Promise Delivery
SMTP DSN turned the bounce into structured evidence while preserving a crucial limit: a sender could request a report, but no receipt could promise more than the reporting system had observed.
Global Institutional
BIRD and the routing policy engine behind internet exchanges
The BIRD Internet Routing Daemon grew from a Czech university project into a control-plane system used in demanding routing environments, including internet exchanges where policy is concentrated and operational mistakes can spread quickly. Its history shows how open routing…

History
The Eighth Bit Needed Permission at Every Hop: How 8BITMIME Changed SMTP
Email could describe an accented character long before every relay could carry its bytes unchanged. 8BITMIME made that mismatch visible: a server had to promise capability on this hop, and acceptance created a duty to keep every bit.

History
The Commands Sent Before Their Answers Arrived: How SMTP PIPELINING Changed the Wait
Early SMTP made a sender pause after nearly every command. On a distant link, the message could spend more time waiting for permission to continue than moving. PIPELINING shortened that silence, but only by making order—not wording—the ledger of unfinished work.

History
The Method That Refused to Be Misunderstood: Why HTTP 510 Existed
RFC 2774 tried to stop servers returning success after ignoring mandatory HTTP extensions. The fate of 510 shows the cost of verifiable semantics.
History
The Message Measured Before It Moved: How SMTP SIZE Made Refusal Early
Early SMTP could carry a large message all the way to a server before learning that the server would never keep it. The SIZE extension did something narrower than guaranteeing delivery: it let two relays compare a declared load with local capacity before paying the full transfer…