
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

IETF
RFC 9996 Registered the Media Type, Not the Schema Version
A label can tell a receiver what kind of parcel arrived without telling it which rulebook gives the contents meaning. RFC 9996 gives Protocol Buffers two proper media types and draws useful boundaries around binary and JSON handling. It does not place the Protobuf schema, its…
Leaders
From Registry Association to Operational Authority: What AS211867 Records Can—and Cannot—Show
From Registry Association to Operational Authority: What AS211867 Records Can—and Cannot—Show intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…

IETF
RFC 9997's PEN-Derived SID Range Is Not a Provenance Stamp
A number can be globally unique and still tell the wrong story about its origin. RFC 9997 gives eligible Private Enterprise Number holders a deterministic block of YANG Schema Item iDentifiers, eliminating a central allocation round trip. That is useful coordination. It is not an…

IETF
RFC 9979’s `$istrusted` Badge Needs a Correction Record
A green check can outlive the judgment that painted it. A mail server marks a message `$istrusted`; several clients synchronize the shared keyword; a reader acts because the interface presents the sender as verified. Later, the server discovers that its evidence or policy was…

IETF
An SSH Agent Signature Is Not a Consent Receipt
A private key never left its protected agent, the requested bytes were signed correctly, and the remote service still received an act that nobody had meaningfully approved. Those facts can coexist. Keeping a key non-exportable answers where the secret stayed. It does not answer…

IETF
The manifest followed the telemetry. The verdict did not
Revision 14 gives collected network data a companion record of its platform, schema and collection conditions. That makes a datapoint easier to read later; it does not make the datapoint complete, the clock trustworthy or the resulting decision correct.

IETF
The log line parsed. The authority to read the connection did not: RFC 9850
RFC 9850 gives diagnostic tools a common way to read TLS connection secrets. The grammar is small; the authority it can transfer is not. A usable key-log record proves neither permission nor safe closure.

IETF
Set-Cookie Is Not a Storage Receipt
A response crossed the network with a valid `Set-Cookie` field, and the release dashboard marked the session step complete. The next request arrived without the cookie. Nothing in those two observations is contradictory. RFC 10025 gives the server authority to issue an…

IETF
A CoAP Group Address Is Not a Security Membership Roster
RFC 10020 separates three groups that operational dashboards often collapse: endpoints listening on a multicast address, servers exposing a common application function, and devices holding shared security material. A packet can cross the first boundary and authenticate at the…

IETF
The verifier subscribed. The evidence chain still had seven tests
An IETF draft turns device attestation from a polling exercise into a stream. That is a useful change in tempo, but a signed notification is still only one link between a measurement and a decision.
Story
RIPE NCC Says Its 2027 Invoicing Changes Are Complete. The Bill Still Waits for 31 December
RIPE NCC has finished the applications work for its 2027 charging scheme before the data that will determine the first bills exists. That is sensible project management. It is also why “complete” needs a second, more operational meaning in January: can each charge be reproduced…

CASE FILE
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating?
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating? intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

ICANN
ICANN’s Authority Is a Chain, Not a Sovereign Grant
ICANN can shape the global identifier system without possessing a general public-law mandate over the internet. Its authority changes form as it moves from corporate purpose to Bylaws, from multistakeholder policy to contractual obligation, and from contract to technical…

Number Resource Society
AS210837’s Continuity Question Is an Evidence-Chain Problem
AS210837’s Continuity Question Is an Evidence-Chain Problem intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Global Institutional Trends
ISC’s control chain: what public evidence shows about prevention, detection and durable repair
ISC’s public record presents a recognizable operational control chain: vulnerability information is coordinated, supported software releases are published, high-availability behavior is documented and tested, service status is exposed, and F-Root operations are described across…

Number Resource Society
AS210057’s visible network footprint still stops short of proving who operates it
AS210057’s visible network footprint still stops short of proving who operates it intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…
IETF
A Read-Only `<system>` Datastore Is Not an Immutable Effective Setting
RFC 10016 makes system-provided configuration visible inside NMDA. That visibility solves a provenance problem; it does not turn a device default into operator approval or a read-only datastore into an immutable outcome. The effective value can still change when hardware…
IETF
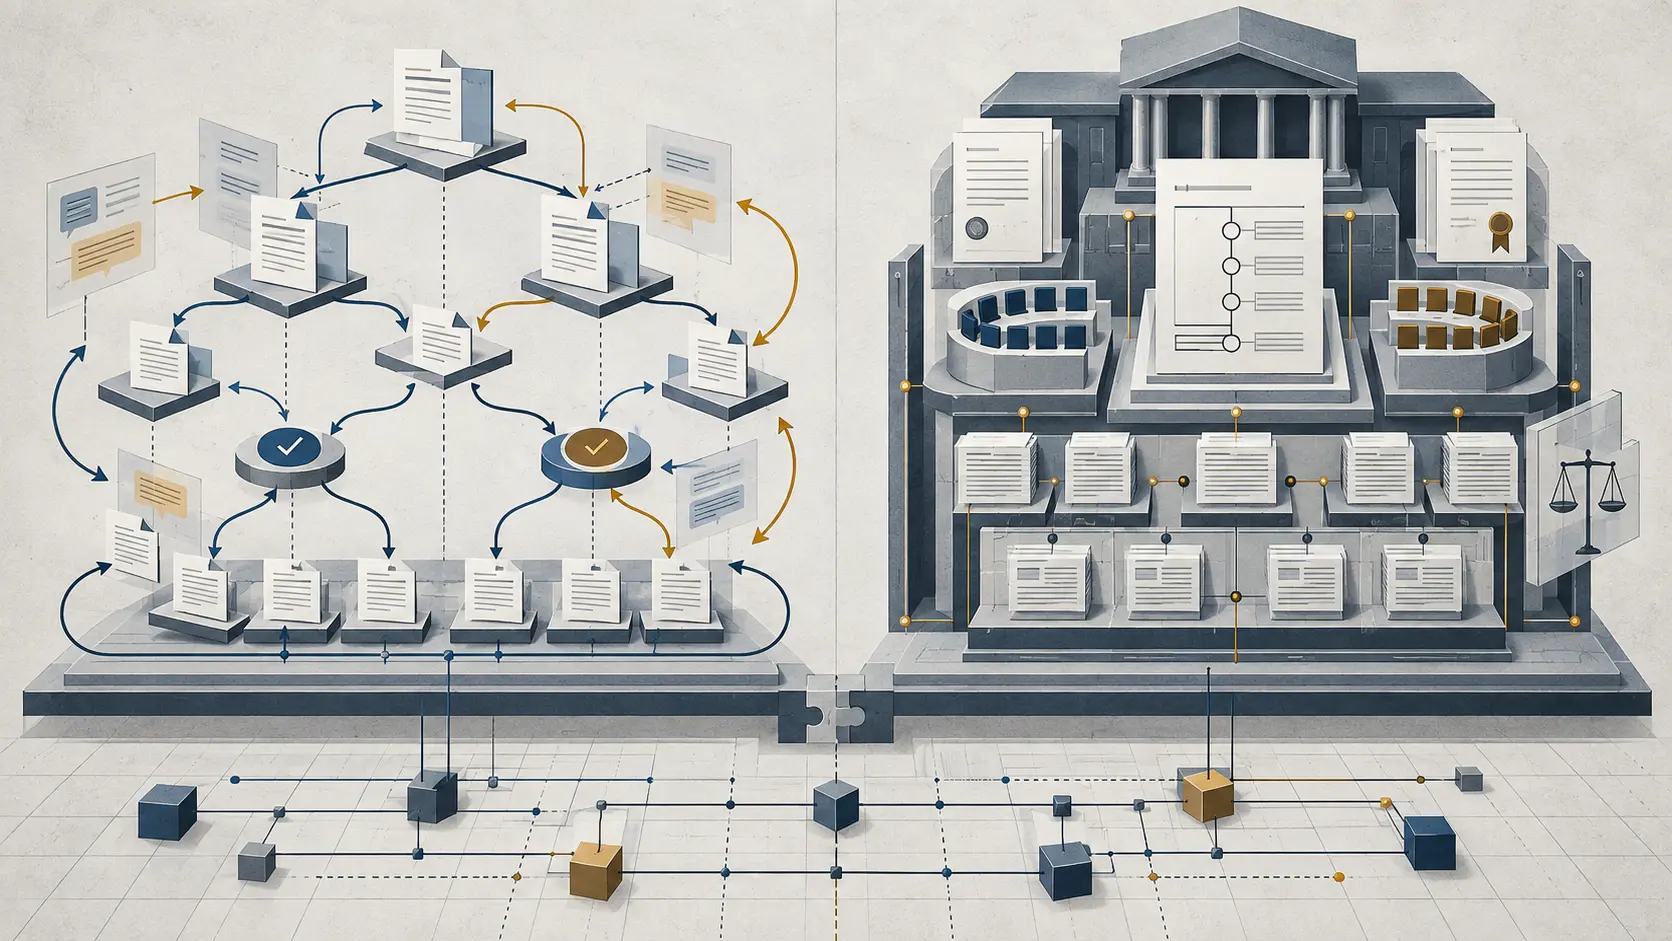
IETF-W3C Is Not One Institution: Authority Depends on the Instrument
The label IETF-W3C suggests a single governance center. The public record describes something more fragmented: the IETF standards process, the IETF Administration LLC, and W3C’s technical and membership structures assign different powers to different bodies. That distinction…

Story
ARIN’s Open 1,024-Character Ticket Is Really About a Private Routing Grammar
An open ARIN suggestion asks for more room in an IRR remarks field. Its motivating case is not really about storage. Lumen documents a parser that can turn a marked remark into the effective membership of an AS-SET, overriding the field that ordinary RPSL readers expect to carry…
Story
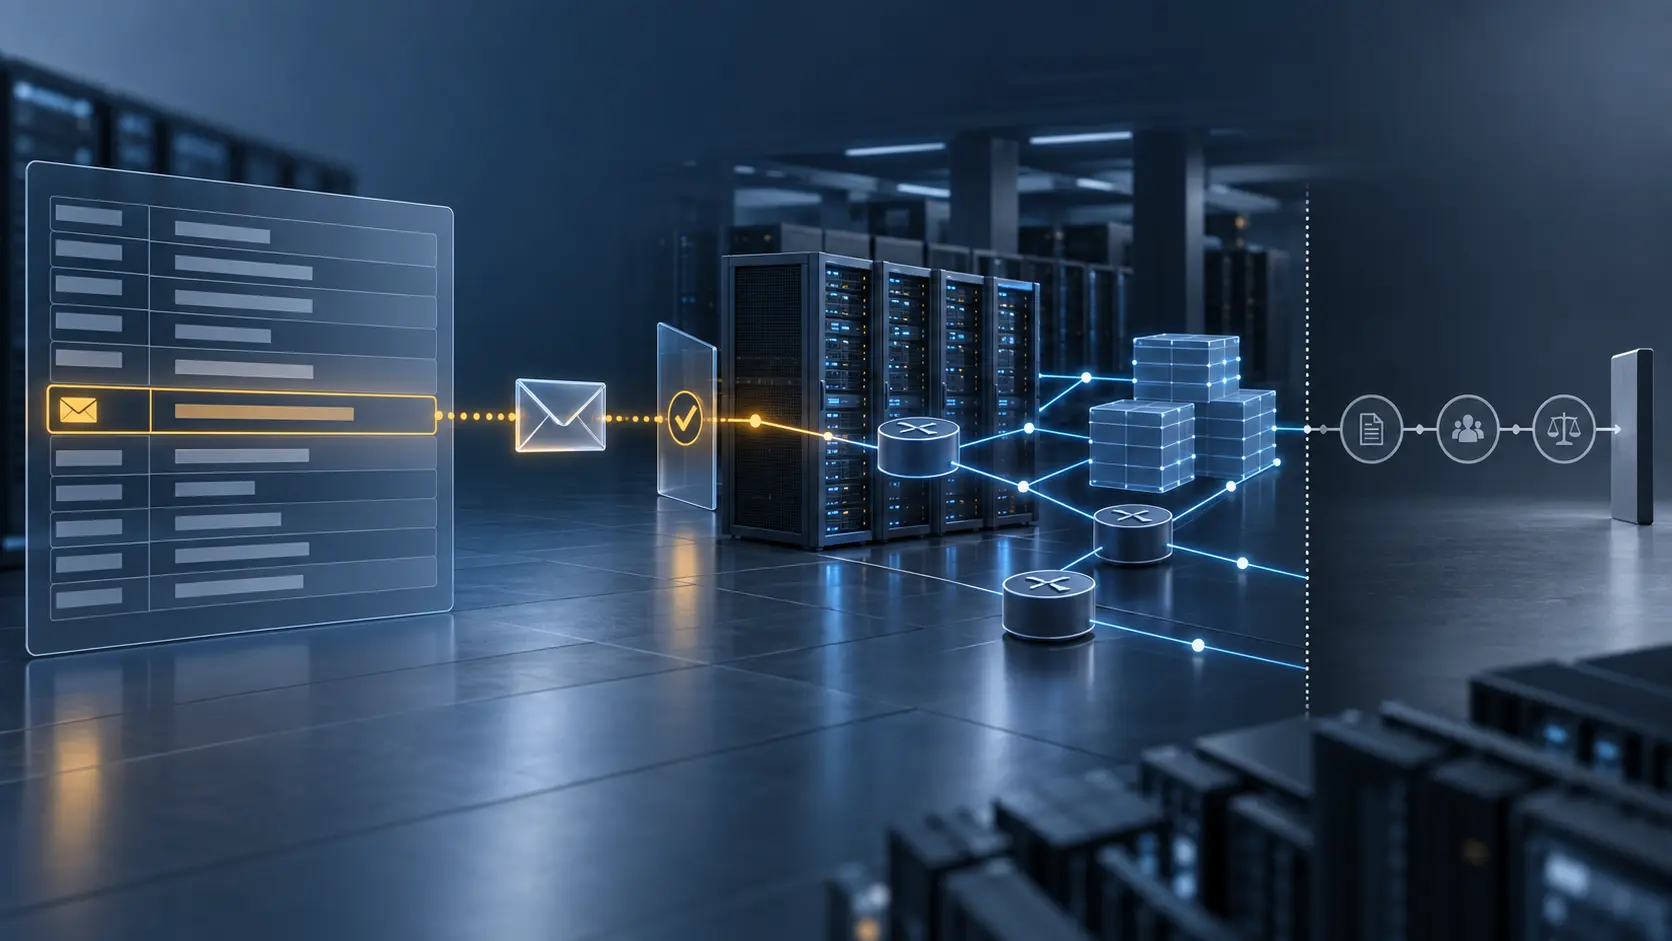
RIPE ABUSE: Who Controls the Next Step After a Report?
RIPE ABUSE is often described as a contact point. That is accurate, but incomplete. The published abuse-c field creates a route into a responsibility chain: a report can be addressed to a resource holder or designated organisation, the mailbox can be tested by RIPE NCC, and a…