
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

IETF
The Port Won the Election. Its Services Still Owed Receipts: RFC 9786
A single access interface can carry bridging, routed VPNs, IRB state and customer expectations at once. RFC 9786 deliberately elects that interface as one Port-Active unit. The gain is deterministic active/standby control; the liability is equally concentrated. A common…

IETF
RFC 9945’s Moderator Team Is Not Its Activation Receipt
The RFC is published. The team exists. A public repository contains procedures. None of those facts, taken alone, answers the question RFC 9945 itself makes decisive: which exact procedures did the IESG approve, and when did the new moderation regime take effect?

IETF
The Interface Still Said Up While the Carrier Was Down
A quiet status light can be the most dangerous signal in a recovery room. Revision 19 of the IETF's common interface-extension draft deliberately permits an interface to remain reported as up while a short down timer is running beneath it. That is useful engineering, not…

Global Institutional
Where ISC’s Control Ends—and the Evidence of Recovery Begins
Where ISC’s Control Ends—and the Evidence of Recovery Begins intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Global…

IETF
The Preference Won the Election. It Did Not Prove the Forwarder Was Ready: RFC 9785
An operator can make one EVPN Provider Edge router the obvious administrative favourite. RFC 9785 gives that intention a precise place in the DF election. What it does not give is a shortcut from “preferred” to “safe to carry traffic”. The standard opens a control surface…
IETF
The XML Matched. The Network Did Not
Two configuration documents can be well formed, stable under XML canonicalization and accepted by a validator, yet still fail to describe the same effective YANG data—or any change that a device actually applied. The first NETMOD draft dedicated to YANG’s XML encoding makes the…

History
Dave Täht and the Result That Had to Be Reproducible
A failed run can be more valuable than a beautiful graph. Dave Täht’s work on network latency made that unsettling proposition practical: if the apparatus cannot expose why a result is invalid, the result is not yet evidence.

IETF
DetNet’s ‘Optimal Path’ Is a Governance Decision Before It Is a Calculation
A DetNet controller may be able to calculate several feasible routes and install one of them precisely. The difficult question arrives earlier: who was entitled to decide that latency mattered more than spare capacity, that protection justified duplicated resources, and that…

History
The Message Had an Address, Not the Object: RFC 2017
In October 1996, RFC 2017 gave MIME mail a way to point at an external entity with a URL. Its economy was the point—and the trap. A locator could arrive intact while the content stayed elsewhere, retrieval still needed permission, and neither a declared type nor a matching digest…
Global Institutional
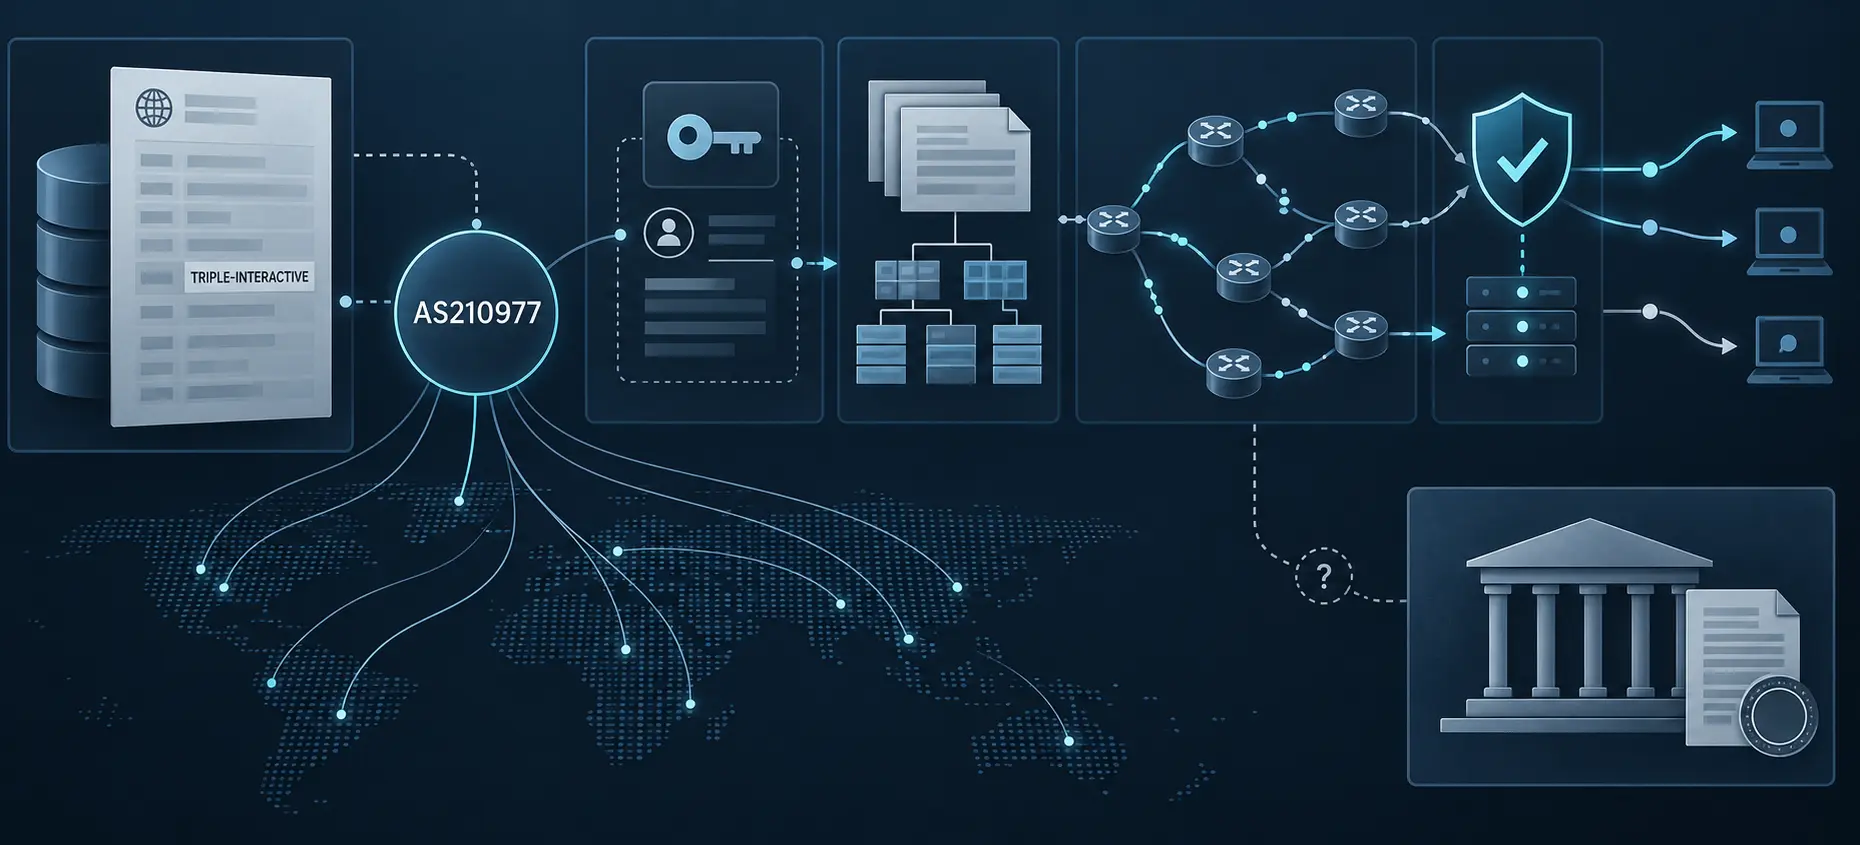
What AS210977’s Registry Record Can—and Cannot—Prove
What AS210977’s Registry Record Can—and Cannot—Prove intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Global…

Global Institutional
What AS210764 Can—and Cannot—Prove About ISC’s Operational Control
What AS210764 Can—and Cannot—Prove About ISC’s Operational Control intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

Number Resource Society
Florian Bauer and AS210833: What the Public Record Can Test About Network Stewardship
Florian Bauer and AS210833: What the Public Record Can Test About Network Stewardship intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…

Europe and Middle East Cloud Services
Genesis Cloud’s Public Control Chain Cannot Be Read From One Network Record
Public records can describe a cloud provider’s identity, domain, autonomous-system registration and reported interconnection. They cannot, by themselves, prove that one operator controls every layer or that a service is reachable worldwide.
IETF
The Message Had One Security Badge. Its Layers Did Not Share One Status: RFC 9787
The comforting part of an encrypted-mail interface is the badge. The difficult part is deciding exactly which bytes are entitled to it. RFC 9787 makes that boundary explicit: one received message gets one cryptographic summary, calculated only from the contiguous protection…
Global Regional ISP
AS210833 and the evidence gap between registration and stewardship
AS210833 and the evidence gap between registration and stewardship intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…
IETF
A Valid ECH Key File Does Not Prove the Right Privacy Boundary
RFC 9934 gives operators a portable way to place an Encrypted ClientHello private key beside the public configuration that uses it. The match is valuable, but it is smaller than the decision a privacy service must make: which names, DNS records, servers, retry paths and time…

History
David Clark and the Reliability the Network Could Not Finish
A subsystem can be flawlessly honest about the work it completed and still be unable to answer the question its user actually asked. David Clark’s end-to-end reasoning begins in that gap.

Global Institutional
DFINFRA and AS210860: The Evidence Stops Before Operational Control
DFINFRA and AS210860: The Evidence Stops Before Operational Control intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

Europe and Middle East Cloud Services
AS210775 Is a Registry Endpoint, Not Yet a Running Network
AS210775 Is a Registry Endpoint, Not Yet a Running Network intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Europe…

IETF
The Route Policy Can Change While Its SR-Algorithm Number Stays the Same
RFC 9933 lets a path request name an SR-Algorithm. For a Flexible Algorithm, however, the number is only a handle: the policy that actually selects a route lives in a winning definition, a metric dictionary, a topology snapshot and an ordered evaluator that can all change…