
Summary
- DNSViz is an open-source DNS and DNSSEC diagnostic, visualisation and measurement project created and maintained principally by Casey Deccio. DNS-OARC operates the public instance at dnsviz.net, but hosting the service does not equate to controlling all software decisions.
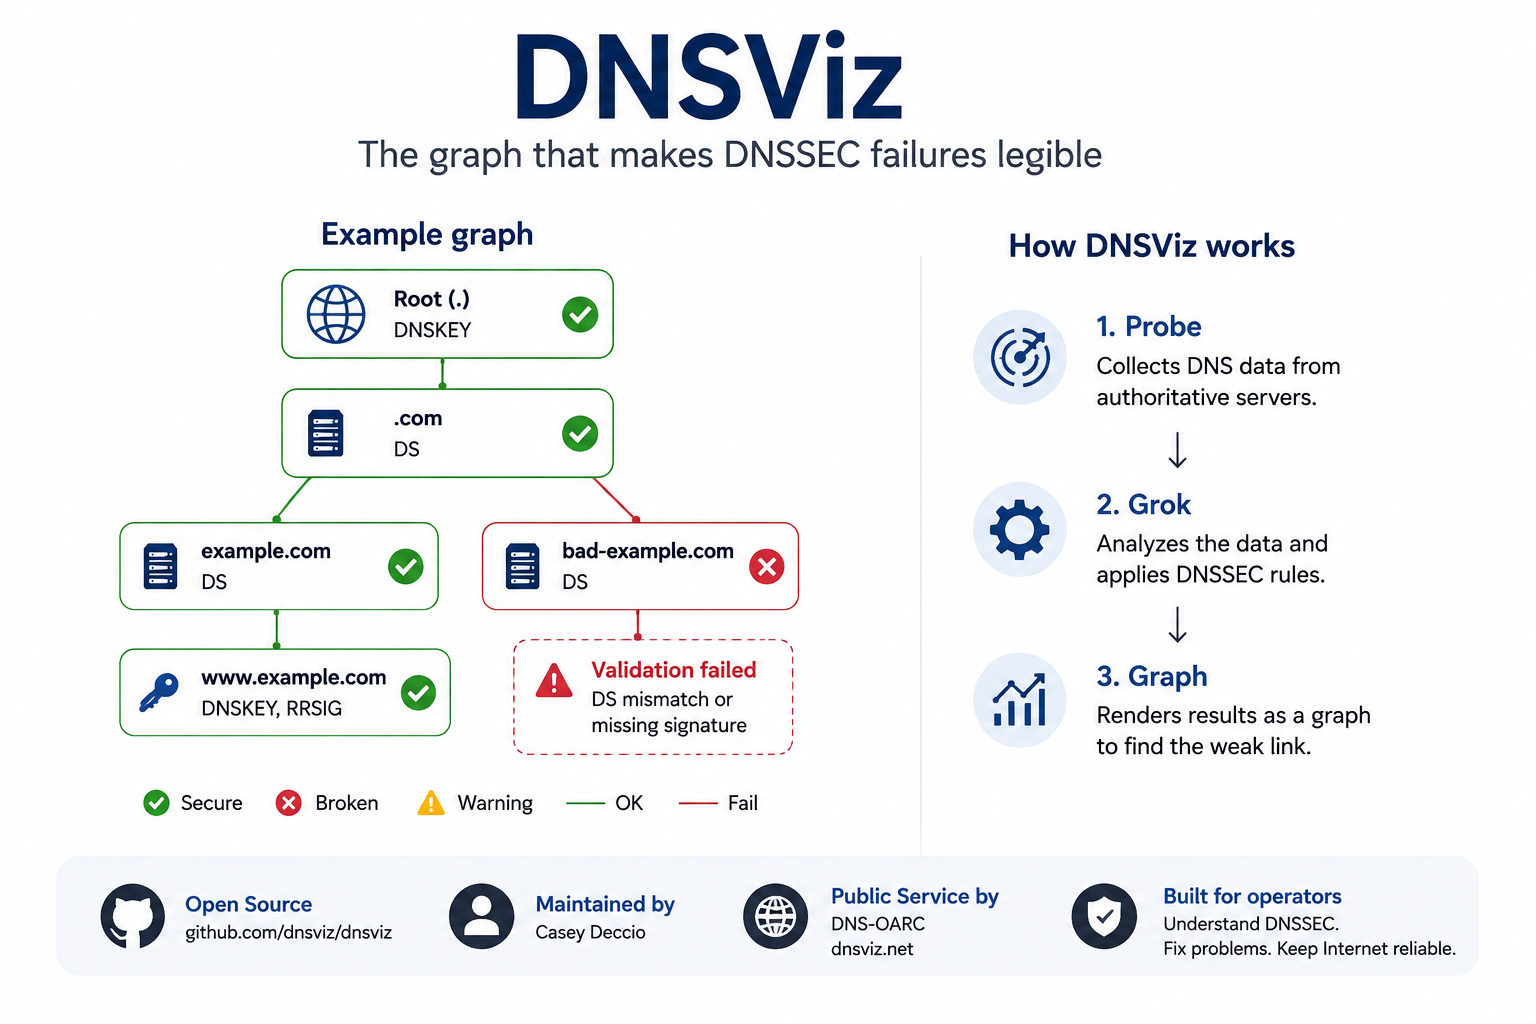
- Its characteristic output is a graph of authentication and delegation relationships. It connects the parent's DS records, the child's DNSKEYs, RRSIG signatures and NSEC or NSEC3 proofs to show which link appears missing, outdated, inconsistent or cryptographically invalid.
- DNSViz is a suite, not just a website. Its command-line workflow separates collection, analysis and rendering through
probe,grokandgraph, allowing observations to be preserved, checks to be automated and work to be carried out from private or controlled vantage points. - A result is evidence of a specific place and moment, not a universal certificate. Anycast, split-horizon DNS, caches, trust anchors, algorithm policies, transient packet loss and rapidly changing rollover states can produce a different observation elsewhere.
- DNSViz does not repair a zone automatically, and a warning does not by itself determine business impact. A green graph does not guarantee success for every resolver; a red one describes a technical condition, not malicious intent.
- The April 2025 release expanded analysis of multi-signer deployments, CDS and CDNSKEY signals, negative-answer consistency and other modern operational cases. Those changes reflect the growing complexity of provider migrations and parent–child automation.
- Repeated public diagnostics have also generated a research source. A 2025 academic study used a large collection of DNSViz snapshots from 2020 to 2024 to study DNSSEC errors at scale, although the corpus remains conditioned by the names submitted, scan scheduling and retention.
- DNSViz matters because it offers domain operators, authoritative providers, registrars, registries and resolver teams a shared explanation of failure. Its long-term value will depend on continued releases, maintainer succession, transparent service policies and its use alongside resolver logs, detail tools and change records.
When a supposedly secure domain suddenly appears as “bogus”
A DNSSEC failure usually reaches the operator as a compressed verdict. A validating resolver marks the response as bogus, an application stops resolving a name or monitoring announces that a signed domain is no longer reachable. The message may be technically correct and yet unhelpful: it says that a chain of proofs failed to validate, but does not immediately identify which organisation, record or moment of change caused the break.
The difficulty stems from distributed responsibility. The parent zone publishes information about the child; the child publishes keys and signatures; authoritative servers deliver the data; and recursive resolvers apply trust anchors and local policy. An old DS at the parent can invalidate a well-signed child; an expired signature can ruin a correct delegation; even a negative answer can fail although the name genuinely does not exist.
DNSViz expands that verdict into an inspectable explanation. It gathers authoritative data, reconstructs relationships and marks the points where the observed chain appears to fail. It does not simplify the protocol until its technical and administrative boundaries disappear; it makes enough complexity visible to decide what should be checked next.
DNSSEC shares a decision among several organisations
DNS resolution already crosses several systems, but DNSSEC adds a cryptographic dependency to the administrative dependency. Parent and child do not merely delegate authority: they must publish entities whose mathematical relationship remains coherent during key changes, provider migrations and cache lifetimes. No single party necessarily controls the entire path, so a failure can persist even though each organisation believes its component is correct.
The parent usually expresses its role with a DS that identifies the digest of a child key. The child publishes DNSKEY and signs its record sets with RRSIG. The validating resolver follows those proofs from a configured anchor to the requested name. The distribution is deliberate, and its reliability depends as much on cryptography as on day-to-day operational coordination.
That is why DNSSEC incidents often become disputes over responsibility. The registrar may have submitted a change, the registry may not yet have published it, the provider may have introduced new keys and the resolver may retain previous data. DNSViz does not settle the contract between them, but it places the observed records and their relationships in a single framework, more useful than exchanging isolated command outputs.
The protocol is already a graph, even though tools print it as lines
Traditional DNS tools are indispensable because they show exact records and details. Their output, however, is usually linear: one query and one response at a time. The operator must mentally reconstruct the dependency between delegation, keys, signatures and non-existence proofs. During a rollover or a migration between several providers, that reconstruction becomes difficult.
DNSViz treats dependency as the main entity. Names, keys, record sets and trust relationships become nodes and edges, and warnings are attached to the relevant link. The visual layer is not decoration: it represents the protocol in the way validation progresses and shows why a record that is valid in isolation may not form a complete path.
The graph also changes the conversation between specialists and generalist operators. It offers a common entity that can be opened down to detail without requiring everyone to start from cryptographic notation. There are limits: complex zones produce dense diagrams and colour should never order a production change. The gain is not eliminating expertise, but directing it more precisely.
A DS record is the parent’s promise about the child
The DS is one of the smallest and most decisive entities in DNSSEC. It is published in the parent zone and identifies a digest derived from a child DNSKEY, linking the parent’s authenticated information with the child’s signing material. If the digest, key tag or algorithm stops matching, the chain can break even though both zones continue to answer normally.
The mismatch appears during key replacements, migrations or incomplete rollbacks. The child may retire a key before the parent removes the DS; the parent may publish the new DS before all authoritatives expose the expected keys. Propagation and caching make each observer see a different phase. DNSViz compares DS and DNSKEY to show whether the parent’s promise corresponds to the child’s current state.
The graph does not know the operator’s intended schedule. A temporary overlap may be deliberate and a persistent mismatch may be an error. DNSViz shows what the published data imply, but it does not deduce every maintenance plan or registrar process. That is why it should be read alongside the change ticket, provider documentation and the expected rollover time.
DNSKEYs distribute signing roles without removing operational risk
A signed zone may publish several DNSKEYs for different roles or phases of a rollover. Some keys sign the data and others protect the DNSKEY set, depending on the model. Multiplicity is not suspect by itself: it separates functions and allows keys to be replaced without abruptly breaking trust.
The challenge is keeping all related entities coherent. Signatures must come from the expected keys, validators must accept the algorithms and the parent’s DS must retain a valid path. Old keys and signatures need to overlap long enough for remote caches to expire. DNSViz brings those entities together in a single model instead of requiring manual comparison across several queries.
The feature is especially useful when the zone does not depend on a single platform. The graph can reveal different sets on different servers, but it does not always know whether the difference is intentional. The same evidence can describe a staged migration, a synchronisation delay or a genuine failure. Operational context separates diagnosis from judgement.
The validity of an RRSIG depends on the clock, coverage and the right key
An RRSIG declares that a particular record set was signed with an algorithm and a key, and includes start and expiry times. Validation is not just a calculation: the signature must cover the expected data, the key must be available and connected to trust, and the observation must fall within the time window.
Time makes DNSSEC depend on rigorous discipline. An incorrect clock produces signatures that are not yet valid or already expired; a delayed publication leaves new data without its signature; a rollover may show signatures from a key absent on some servers. DNSViz checks those relationships and places the temporal evidence alongside the authentication path.
The timestamp of the result is part of the diagnosis. A graph before expiry and one after can be two correct descriptions of different states. Operators should keep the time, compare it with signing and deployment records and repeat the analysis before acting on an old snapshot.
NSEC and NSEC3 make absence provable and failure harder to explain
DNSSEC must also authenticate the claim that a name or type does not exist. NSEC and NSEC3 do so by describing intervals or encrypted relationships within the signed space. Without that proof, a negative answer could be forged to hide a real record. It is an essential part of the protocol and, for many operators, one of the least familiar until it fails.
The proof can be incorrect because the interval does not cover the query, a signature is missing, the NSEC3 parameters do not match or opt-out interacts with delegation in an unexpected way. The symptom looks like a simple “does not exist”, but the validator classifies it according to the evidence. DNSViz analyses those records in the same graph as positive authentication.
The visualisation helps because the error lies in the relationship between the query and the covered name space. Even so, it does not remove all policy decisions. Opt-out and certain delegations create legitimate complexity, and validators may impose different rules. The correct response is to inspect, not to assume that every negative-answer warning requires the same correction.
Casey Deccio built DNSViz where protocol theory met operational confusion
DNSViz grew out of Casey Deccio’s work in a security research environment at Sandia National Laboratories. The need was practical: the standards explained how trust should be established, but operators needed to know why a real deployment satisfied or violated those rules. The 2012 report documented a visual model, not merely an additional validation command.
The project should not be reduced to Deccio’s whole career, nor confused with every later institution. At the same time, its architecture and maintenance are closely associated with a principal creator. The DNS-OARC directory still distinguishes Deccio’s development and maintenance from the organisation’s operation of the service.
That concentration is both strength and risk. A coherent model benefits from continuous knowledge and a maintainer who understands its historical assumptions. But a tool used by third parties needs documentation, review and paths for others to understand the code. The story is also that of a small research project acquiring obligations that were not formalised at birth.
Sandia’s 2012 work turned validation into an explanatory model
The Sandia report fixed the central editorial idea: a secure or insecure result is worth less than an explanation of the proofs that produced it. The project represented components and relationships so that the analyst could move from the general chain to the records that support each judgement. That allowed it to serve incidents, teaching and measurement at the same time.
Prototypes usually demonstrate a concept without becoming operational software. DNSViz had to support more environments, changing algorithms and repeatable collection. The original interface was a beginning, not a frozen specification. Later work separated observation, analysis and representation so they could be reused.
Sandia provided the initial context, but it does not sponsor or control the project today. Later, a public operator, academic affiliations and an open repository entered the story. The accurate account is a continuous software line through different institutional contexts.
Portability turned a web page into reusable infrastructure
A public website eases access, but it does not cover every use. Internal zones are not visible from the internet, pipelines require automatable outputs and research may need raw data before applying a new rule. Portability turned DNSViz from a destination into a toolkit.
Between 2013 and 2014 the project was rebuilt to be more portable and extensible and was presented at a DNS-OARC workshop. The command-line package allowed the workflow to run off-site and separated software, public service and data from an observation more clearly.
Portability does not guarantee reproducibility. Versions change rules, dependencies alter rendering and observations age. Reproducing requires preserving version, vantage point, time and data. The modular architecture makes this possible, but it does not replace the user’s discipline.
proberecords what the authoritative system actually says
Collection queries the delegation and authoritative servers to gather NS, DS, DNSKEY, RRSIG, NSEC, NSEC3 and related responses. It does not start only from a resolver’s verdict; it retains the elements needed to explain the observed trust path.
Every active measurement depends on server selection, routes, loss, timing and views. DNSViz can show inconsistency between responses, but it does not guarantee that every absence is a persistent state. The lack of a datum in one run is not by itself proof that the datum does not exist on any instance.
Separating collection and analysis allows a snapshot to be saved and reviewed after the zone has already changed. It also makes it possible to apply several analyses to the same evidence. For it to remain meaningful, the snapshot must keep enough context about the time and manner of collection.
grokconverts observations into a reasoned model of dependencies
Analysis does not classify isolated records. It connects delegations, keys, signatures and negative proofs and checks whether the relationships satisfy the rules implemented in that version. The result indicates not only that validation fails, but which link does not hold up with the observed data.
The logic incorporates technical decisions. Supported algorithms, rollovers, multi-signer rules and handling of inconsistencies evolve. An old version may interpret the same snapshot differently. Credibility improves when rules, versions and test cases are visible.
The model does not reproduce every resolver. Resolvers may have different anchors, disable algorithms or retain caches not present in the authoritative observation.grokoffers a coherent reading; the operator must compare it with the relevant resolver and policy.
graphallows the chain to be inspected without hiding the records
The rendering phase transforms the analysis into a navigable or saveable graph. Good visualisation reduces the effort of following the chain and retains enough detail to verify the judgement. DNSViz links both levels instead of replacing the evidence with a simplified note.
Nodes and edges show which entities authenticate or delegate; annotations direct attention to the problematic link. The operator can start from the break and then open records, keys and signatures. This is useful when several plausible causes produce the same symptom.
Graphs can be dense. Multi-signing, overlapping rollovers and inconsistent servers generate real complexity. The aim should not be to hide it in order to beautify the image, but to help traverse it and keep open the conclusion that evidence is missing.
DNS-OARC maintains the public service without owning the whole project
A public diagnostic becomes infrastructure only if someone keeps it accessible, updates dependencies and responds to abuse and failures. DNS-OARC provides that home for dnsviz.net and connects the tool with the community that operates authoritative servers and resolvers.
The governance boundary is well documented. DNS-OARC says Casey Deccio develops and maintains DNSViz while the organisation operates the public instance. A 2021 discussion repeated the separation when talking about support and algorithms. Hosting, maintenance and standards authority belong to different actors.
The separation avoids misattribution and creates coordination needs. A code change requires updating the service; a service incident may reveal a software bug. No dedicated budget, complete SLA or succession plan is published. The value of the endpoint shows that those tasks are performed, even though their institutional conditions are barely visible.
The public endpoint and the local suite answer different questions
The web offers a quick external view, with no installation, and a graph that can be shared between organisations during an incident. That simplicity also has pedagogical value and brings the DNSSEC chain closer to people who would not run several manual queries.
A local run works within private networks, in pre-deployment checks, on repeatable schedules and for preserving raw data. It also allows fixing the version and integrating the result with change logs. PyPI and the documentation make that use possible without turning DNSViz into a paid service.
It is not merely convenience versus sophistication. The public endpoint provides independence from one’s own environment; the local probe sees names and paths inaccessible from outside. A solid investigation can use both and compare them with the real resolver. Differences may point precisely to the boundary that should be studied.
A DNSViz result belongs to a place and a moment
Every active measurement has an observation point. The probe queries from a specific network, reaches certain instances and records responses under the routes of that moment. DNS distributes the service and DNSSEC adds temporary signatures and cached delegations. The graph has coordinates even though it is shown as a single image.
The limitation honestly defines the scope. DNSViz explains why the observed chain appears valid, insecure or broken according to its rules, but it does not certify that every resolver or region saw the same. The result is more reliable when time and context are preserved.
Operators should gather comparative evidence: another network, authoritative logs, resolver traces and a fresh run after the cache expires. That distinguishes a local, transient or widely published state. The graph starts that comparison; it does not finish it.
Anycast can make an authoritative service look like several systems
Many providers announce the same address from several locations. Routing directs users and probes to different sites, improving resilience and latency, but it can expose unsynchronised versions, data or conditions. A single service name can produce several operational realities.
DNSViz compares responses, but the public probe only reaches the instances chosen by routing. Another user may reach another site, and loss or filtering can make a healthy instance look absent. These are limits inherent to measurement, not exceptions.
If a key or signature appears on some servers and not on others, the operator should review synchronisation between locations and test from several networks. DNSSEC makes disagreement especially dangerous because the validator requires a valid chain for the response it receives.
Split-horizon DNS marks the limit of any public diagnostic
Split-horizon DNS provides different answers depending on the network. Internal clients can see private names and addresses that do not exist externally. The design may be legitimate, but a public analyser does not describe the internal view unless it is run with authorisation inside it.
An external green result may say nothing about an internal application; a red one may be irrelevant for a name intended only for the inside. The local suite allows the same diagnostic model to be moved to the place where the private view is visible.
There is also a security question. Internal names, topology and keys can be sensitive and should not be sent to a public service for convenience. Local analysis keeps queries and evidence under control, although permissions and data handling remain the operator’s responsibility.
A green graph is evidence, not a universal availability certificate
A correct graph shows that the observed relationships appear coherent. It is solid evidence about the authoritative data collected, but it does not prove that every resolver reaches the domain. Other routes, caches, anchors, algorithm policies or network failures can produce a different experience.
Resolvers also apply local restrictions: they can disable an algorithm, retain an old negative answer or fail to reach a site. Applications fail because of transport, certificates or configuration. DNSViz should narrow the failure domain, not dismiss reports that do not match the graph.
The precise formulation is that the observed chain validated from that point, with that analysis and at that time. That preserves the value of the result without turning it into a non-existent guarantee, especially when the graph is used in a dispute between providers.
A red graph identifies a condition, not an attacker
DNSViz exposes missing, outdated, inconsistent or invalid material, but it does not determine the motive. A broken chain can come from a rushed rollover, a registrar delay, an incomplete migration, a defect or an attack. The protocol evidence says what failed, not who wanted the outcome.
Security teams should not confuse visual severity with attribution. An invalid signature may have expired; an unexpected DS may correspond to an authorised change. Histories, registrar records, authoritative logs and responsible humans are necessary before classifying the incident.
The distinction protects accuracy and recovery. Assuming attack can freeze a legitimate migration; assuming error can hide a hostile change. DNSViz provides a structured technical finding to correlate with other evidence and reduce speculation.
Multi-signer DNS makes provider choice easier and diagnosis denser
A zone can use more than one signer or authoritative provider to gain resilience, support a migration or reduce dependency. Entities must publish compatible keys, signatures and delegation. The commercial advantage can be significant, but the cryptographic state becomes more distributed and legitimate intermediate states multiply.
The April 2025 release added or improved multi-signer analysis to compare signature sets and authoritative responses. The feature does not make all architectures equivalent; IETF models coordinate keys and signatures in several ways.
A dense graph does not prove the design is wrong. It shows that resilience requires more coordination. Operators need documented functions, tested rollovers and a clear way to distinguish planned overlap from a stalled transition. DNSViz exposes the state; the team provides the intent.
Provider migrations create legitimate states that look like failures
Changing authoritative or signing provider is rarely atomic. New servers and keys can appear before the old ones are retired, and the parent’s DS can change at a different pace from the child zone. During the transition several sets coexist. A tool that expects only the final state may mark a safe overlap as an error.
The opposite risk is that a temporary state becomes stuck. A provider may continue serving an old key, the registrar’s update may not reach the registry or a rollback may retire entities in the wrong order. The graph shows the complete relationship instead of hiding transient entities behind a single label.
Interpretation must follow the migration plan. Expected stages can be recorded, DNSViz run before and after each step and outputs kept. A warning accepted for a particular phase becomes grounds for escalation when it outlives the expected deadline. Linking diagnosis to change governance makes it safer.
CDS and CDNSKEY automate delegation, but shift risk to policy
CDS and CDNSKEY allow the child zone to signal the parent about desired changes to its DS material. The mechanism reduces manual work and can make rollover more reliable at scale. It also shifts trust to an automatic relationship: the parent or registrar must decide when and how to accept the signal.
DNSViz compares those records with the child’s DNSKEYs and the parent’s published DS. The April 2025 release expanded the analysis to show whether an update appears coherent or incomplete. The tool implements protocol relationships, but it does not force a registry to apply a particular policy.
Automation removes one kind of delay and creates control questions: who authorises the initial trust, how deletion signals are handled or what happens after an unexpected publication. DNSViz makes the evidence visible, but security depends on the parent’s policy, the child’s key management and the ability to investigate before the change becomes an outage.
The April 2025 release incorporated modern patterns into the graph
A tool ages when infrastructure changes faster than its rules. DNSSEC now uses newer algorithms, several providers, automatic signalling and more complex negative answers. The April 2025 release addressed part of that distance with multi-signer analysis, CDS and CDNSKEY checks and improvements to negative-answer consistency.
Release notes show that code exists, not that every environment is updated or that every edge case is solved. dnsviz.net may run one version, local packages may lag and distributions may follow another schedule. It is worth recording the version of each result, especially when comparing a historical snapshot with a current diagnosis.
The publication shows why relevance depends on continuity. DNSSEC continues to change as an operating system even with stable central standards. The tool must translate the models actually adopted into diagnostic logic, and that translation is maintenance work, not an automatic effect of the original design.
Longitudinal snapshots turn fault resolution into measurement
A graph helps in an incident; a series shows how long an error lasts, how a rollover progresses or how long repair takes. When many names are observed repeatedly with a coherent model, the collection becomes a research corpus and not just a query history.
DNSViz favours that transition because it collects and analyses in a structured way with associated time. Researchers can group conditions, compare states and examine recurring failures. The public service and automated runs thus create secondary infrastructure: a memory of how DNSSEC works in practice.
Historical data demand care. A snapshot can capture a rollover corrected minutes later, and the most queried names can be over-represented. Retention decides which stories survive. The consistency of the method is valuable, but it does not turn sampling into a representative census.
The 2025 study shows what a coherent corpus can reveal
The 2025 research used a large collection of DNSViz results from 2020 to 2024 to study DNSSEC errors at scale. Its value is to go beyond the isolated anecdote: a common analyser identifies recurring categories and allows asking how long they last and whether they return.
It also shows that the public service is measurement infrastructure. What matters is not just the number of snapshots, but the attached explanation. A set of success or failure labels would say less about delegation, signature, non-existence or coherence. DNSViz provides a taxonomy grounded in the graph.
The study does not automatically describe all signed domains. Sampling decisions define the population. Names submitted after a failure may contain more errors than a random sample, and scheduled scans introduce another bias. The numbers are only defensible when how they entered the corpus is explained.
Anycast and the vantage point can make two honest observations disagree
Authoritative providers usually announce the same address from several places. Two observers can reach different instances even when querying the same IP. If the sites are out of sync, one probe can see different keys or signatures from those received by a resolver on another network.
Filtering, fragmentation and transient loss also vary. A system can retry and collect metadata, but it does not claim a view of all paths. The external result should be treated as a controlled observation compared with other evidence, not as an omniscient window.
The lesson is especially strong in DNS because the measured service is distributed and the measurement system lives in another distributed network. A difference should open questions about place, time and server reached before becoming an accusation against a tool or an operator.
Caches retain old truths after the authoritative configuration changes
Resolvers store records to reduce latency and load. During a rollover, the authoritatives may already publish a new, coherent chain while some resolvers continue using previous DS, DNSKEY or RRSIG until the TTL expires. DNSViz can show the current state without reproducing what a user behind an old cache sees.
The opposite can also happen: the cache serves a valid chain when the authoritative state is already broken. The outage appears gradually as data expires, so elapsed time and TTLs are as important as the graph of the moment.
Investigation should combine authoritative analysis and resolver traces. Flushing a cache tests a hypothesis, but it does not repair the world. Operators must plan for the period when old and new states coexist and avoid presenting the “current” result as immediate universal experience.
Resolver policy and anchors define a result the graph does not fully predict
DNSViz reasons with the collected data and the rules of its version. A production resolver may have another trust anchor, reject an algorithm, use aggressive validation or keep a previous cached state. Two systems can treat the same data differently without either having collected the information wrongly.
The distinction is crucial in algorithm migrations or failures affecting a specific population. A coherent authoritative chain does not guarantee that an old implementation or a stricter policy will accept it; a cache can keep answering when the published state is already incorrect.
DNSViz is a reference point, not a universal emulator. When the graph and the resolver disagree, the investigation should locate the anchor, algorithm, cache or path that explains the difference.
Protocol severity and business impact are different measures
A warning describes a technical relationship, not the number of people affected or the importance of the service. A failure in a rarely used name can have little immediate effect; the same defect in an authentication domain can block an organisation. The colour does not include that context.
An apparently minor warning can anticipate an outage when a signature expires or the last valid object disappears from a cache. The condition may be mild today and severe tomorrow. That is why protocol evidence should be related to inventory, traffic, dependencies and schedule.
Separating the two measures avoids minimising a problem because it still works, or overreacting because the graph is red. DNSViz classifies the condition according to its model; the organisation translates that condition into risk.
DNSSEC validity does not check the rest of the application path
A domain with a perfect chain can still be unreachable because of filtering, a down server, an expired TLS certificate or bad application configuration. DNSViz does not test those layers; it determines the coherence of the observed DNS authentication.
Conversely, an application may work temporarily with broken DNSSEC if the resolver does not validate or uses cache. That apparent success does not prove security, only an uneven propagation of the failure.
The graph should be part of an investigation that also reviews connectivity, effective resolution, TLS, application health and user experience. Its strength lies in limiting its scope well, not in claiming end-to-end availability.
The graph belongs to change review before crisis calls
The most valuable use is usually before and after planned changes. A rollover, registrar transfer, provider migration or multi-signer deployment can be rehearsed with the local suite, the expected graph saved and acceptable intermediate states defined. Each production step is checked against that plan.
Diagnosis thus becomes change control. It can verify that the new key is published, that signatures exist, that the link with the parent is coherent and that the old is retired only after overlap. A failure pauses the operation before users notice. Project documentation eases automated use, but each entity must design its own approval and recovery.
It is not advisable to reduce everything to a red or green gate. Some transitions are deliberately mixed. The safest control records the specific rule, the observed entities and the reason why the responsible person considers the state acceptable.
Incident response improves when all parties point to the same broken edge
An incident can involve the domain owner, DNS provider, registrar, registry, resolver and application. Each sees a part and can claim its component is healthy. The graph creates a common entity: it can show correct keys with an old DS or a server without the signature present on the others.
Shared evidence does not remove authority limits. The registrar can update the parent without controlling the signer; the provider can publish correctly delivered data incorrectly; the resolver can detect first without being able to repair. The process must map the broken relationship to who can act and verify afterwards from the user’s path.
Keeping the initial observation, the change, the recovery moment and the cache duration produces a better post-mortem than saying “the DNS went down”. It identifies the mechanism and the control that failed.
Safe automation needs evidence, approval and rollback
Connecting diagnosis and correction is tempting: remove a DS, re-publish a key or revert a provider when the graph turns red. Some tasks can be automated safely in well-controlled environments. DNSViz, however, does not present itself as automatic repair, a prudent boundary.
Changes cross systems that rarely share an atomic transaction. An API accepts before all parents publish, a platform deploys by regions and a rollback meets caches already containing the new state. Checkpoints, deadlines, explicit authority and proof that the previous state remains usable are needed.
A sensible design lets DNSViz observe and another flow decide. High-risk actions require approval and low-risk checks can be continuous. The goal is not to confuse a technical classification with permission to modify infrastructure across several organisations.
Open source makes the method inspectable, not its continuity automatic
Public code allows the analysis to be installed, adapted and run locally without buying a service. It lowers barriers, opens the logic to examination and offers an alternative if the public endpoint is unavailable.
But code does not maintain dependencies or interpret new rules. Python, libraries, renderers and DNSSEC practices change. Someone must update tests, resolve issues and publish releases. The 2025 release and availability in August 2026 demonstrate activity, not indefinite capacity.
The distinction sums up the project’s philosophy: visibility makes it possible to act with knowledge, but it does not act by itself. The repository makes stewardship observable; people and institutions must sustain it.
A small maintainer base concentrates knowledge used by many operators
Governance revolves around Deccio, repository contributors and DNS-OARC’s operation. No dedicated foundation, council or commercial product solely for the project was identified. The light structure has worked for more than a decade, but it does not publish a complete maintainer census or a succession plan.
The risk matters because quality depends on accumulated judgement. A new algorithm or a multi-signer case requires deciding representation, severity and compatibility, not just programming. That knowledge can be documented and spread, but it remains concentrated when review depends on very few people.
There is no evidence of imminent failure. The risk is that operational importance grows faster than governance and resources. That is why versions, contribution, DNS-OARC support and clarity of roles should be watched alongside technical developments.
DNSViz has no single competitor because DNS failures have several layers
Operators can use dig, drill or delv for exact records; Zonemaster for broader zone tests; Internet.nl for compliance; RIPE Atlas for distributed measurement; and resolver logs for real behaviour. DNSViz distinguishes itself by graphically explaining DNSSEC authentication and delegation relationships.
Each tool answers a different question. Commands show details, broad suites detect transport or policy problems, probes add geography and logs reveal concrete cache and policy. DNSViz occupies the intermediate space: it turns the cryptographic chain into an entity that teams can discuss.
The choice is cumulative. A warning is followed by direct queries, traces and registry checks. The graph works best as an investigation map rather than an argument for discarding other instruments.
The project makes cryptographic infrastructure legible without claiming its control
DNSSEC promises authenticated data through distributed decisions: generate and protect keys, renew signatures, publish correct DSs, synchronise servers and validate in resolvers. A distributed protocol also distributes its failure modes.
DNSViz makes that distribution legible. It does not operate the root, a registry, a registrar, an authoritative fleet or the user’s resolver. It observes published evidence and explains how it fits from its point. It can shorten the incident by indicating where to look, but another party must repair.
It is a more modest and durable claim than an automation slogan. Infrastructure improves when it distinguishes observation from authority, diagnosis from remediation and model from reality. DNSViz endures because it shows those boundaries alongside the chain.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance