
Summary
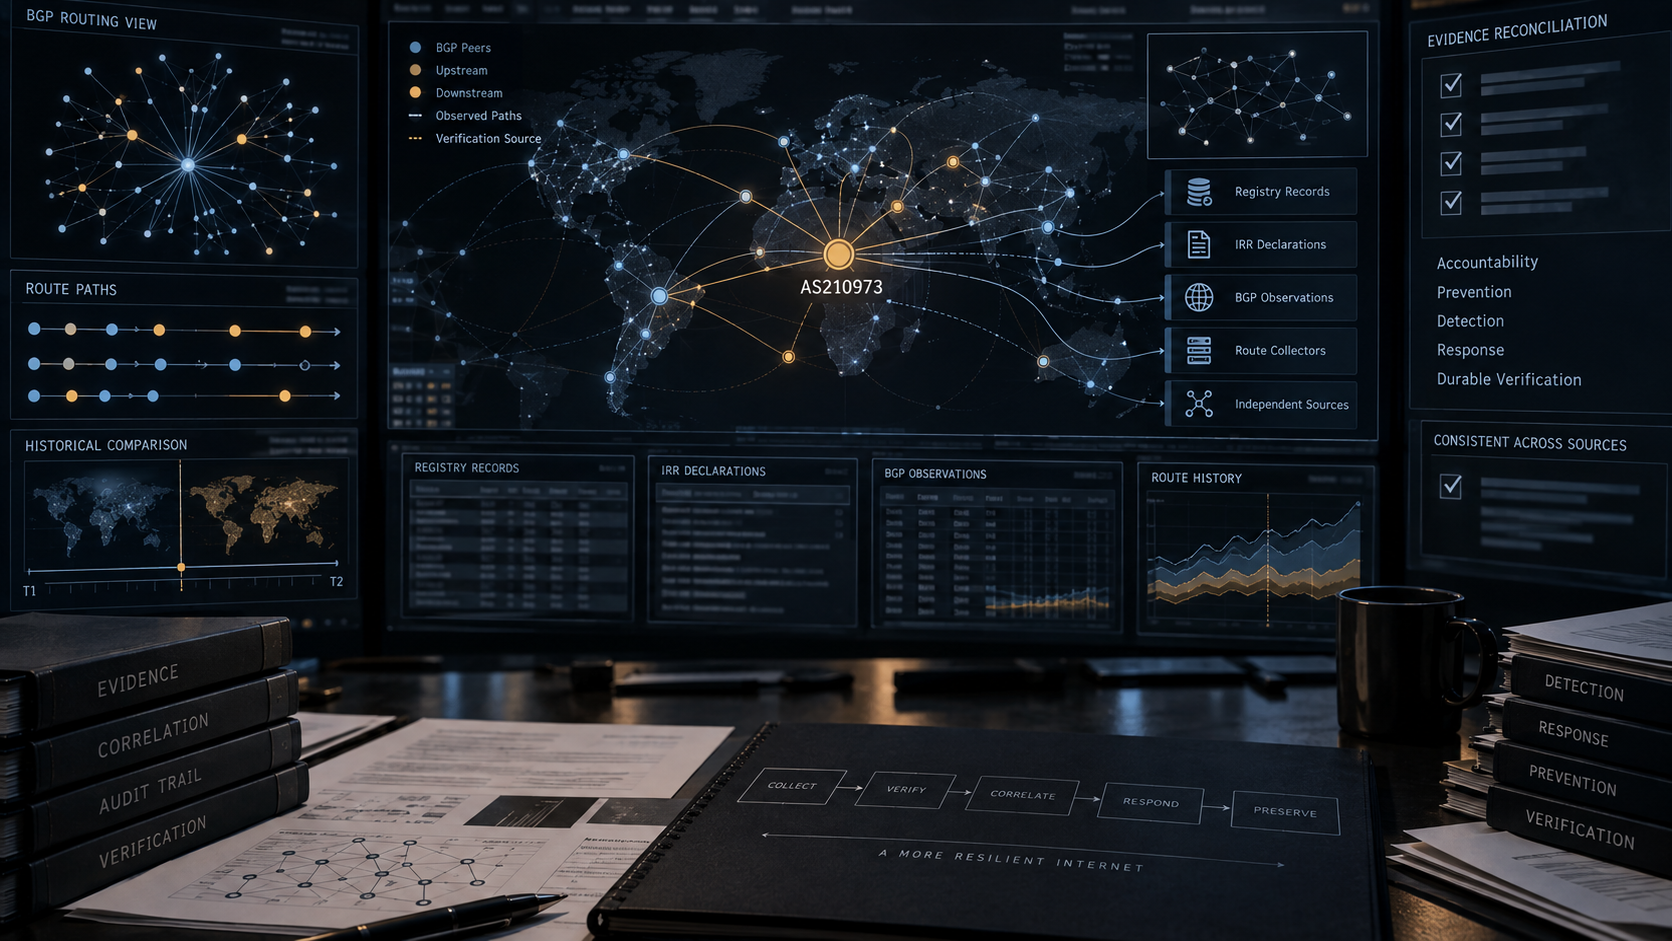
- The public evidence stack for AS210973 contains several distinct layers: a registry record, IRR declarations, RIPEstat observations, third-party BGP summaries and a PeeringDB entry. Each layer answers a different question.
- Those records can support an evidence-bound account of registration and observed routing activity, but they do not independently establish legal ownership, authorization, exclusive operational control or uninterrupted continuity.
- The practical accountability test is not whether an ASN appears in public systems. It is whether the responsible party, prevention controls, detection process and durable remedy can be verified across time and across independent evidence sources.
The question behind the records
The starting point for this investigation is narrow. DATAMATIX is the frozen Directory subject associated with AS210973. The research question is not whether public records exist. They do. It is whether those records can establish a defensible picture of control and continuity rather than merely showing that a number, a policy object or a technical signal appears somewhere on the internet.
That distinction matters because network evidence is easy to overread. A registry record is often treated as an identity document. An IRR route object is treated as authorization. A BGP announcement is treated as proof of possession. A peering-directory record is treated as proof of operational scale. None of those inferences is safe without qualification.
The preserved evidence set includes the RIPE Database aut-num record for AS210973 (RIPE NCC registry record); RIPE IRR inverse-origin results for route and route6 objects (IRR declarations); RIPEstat registry aggregation and ASN overview (WHOIS aggregation, ASN overview); announced-prefix and routing-status observations (announced prefixes, routing status); and an ASN-neighbour view (neighbours). It also includes a PeeringDB network record (PeeringDB) and external summaries from bgp.tools, BGP.HE.NET, IRR Explorer and BGPView (bgp.tools, BGP.HE.NET, IRR Explorer, BGPView).
The evidence package preserves the endpoints and their runtime captures. It does not, in the form available for this article, verify every payload-specific value that a reader might want: the exact registered name, status, organisation, contacts, route objects, prefixes, current routing state, neighbours, PeeringDB fields or timestamps. That is not a minor caveat. It defines what can responsibly be claimed.
Five layers, five different questions
The registry layer. The RIPE Database aut-num object is a formal record in the Regional Internet Registry environment. It can identify an autonomous-system number and associate fields with that number. It is evidence about what the registry records. It is not automatically evidence of the person or company exercising day-to-day operational control, nor is it a title document proving legal ownership of every resource that may be associated with the ASN.
The registry layer is therefore the right place to ask: what does the responsible registry publish, under what object type, and with what maintenance structure? It is not enough to ask whether the object exists. A control analysis must also examine the strength and currency of the organisation, maintainer and contact relationships, and whether independent evidence connects those records to a functioning accountable operator.
The IRR layer. Route and route6 objects express routing-policy declarations. The inverse-origin query preserved in this investigation searches for objects associated with AS210973. Such objects can explain what routing policy a maintainer declares or has declared. They do not by themselves prove that the holder of an address block authorised the declaration, that an announcement was accepted by every network, or that the party maintaining the object is the same party operating the relevant infrastructure.
IRR data is valuable because it makes policy legible. It is limited because policy declaration and legal authority are different relationships. A route object may be stale, incomplete, duplicated across registries or maintained under a relationship that requires separate verification. The correct conclusion is therefore conditional: an IRR object can support a claim about a recorded routing-policy declaration, not a categorical claim about ownership or lawful control.
The BGP observation layer. RIPEstat announced-prefix, routing-status and ASN-neighbour endpoints, along with third-party monitors, provide observations of routing behaviour. They can show what collectors saw at a given time and through which visible paths. They are important for detecting activity, change, withdrawal, reachability and path relationships.
But observation is not possession. A BGP view is a measurement made from particular vantage points, with particular collection limits and timing. It cannot establish uninterrupted operation between observations. It may not identify the commercial or legal party responsible for a route. It can indicate that a network signal was visible without proving why it was visible, who authorised it, or whether the signal represented a stable service rather than a transient configuration.
The same discipline applies to external summaries. bgp.tools, BGP.HE.NET, IRR Explorer and BGPView are useful comparison points because they are independent of the RIPE registry interface and may expose differences in collection or presentation. They should not be collapsed into one synthetic fact. Agreement among monitors strengthens confidence that a signal was observable; it still does not convert observation into proof of ownership or continuity.
The peering-directory layer. PeeringDB is a self-reported directory used by networks and exchange communities. A record can provide operational context such as stated facilities, exchanges or contacts. It is not equivalent to a registry adjudication. Its evidentiary value depends on the field, the date, the maintenance history and corroboration from other sources.
Self-reported operational information can be useful precisely because it describes how a network presents itself to peers. It must remain labelled as self-report. Treating it as independent confirmation would erase the distinction between an operator’s representation and an external observation.
The accountability layer. The final layer is not another database. It is the practical question of who can prevent, detect and repair a failure. Public records may identify possible control points: registry maintainers, routing-policy maintainers, contacts, upstreams, peers and monitoring systems. They do not, without additional evidence, establish which party can make a decision, which party bears a duty to act, or whether a remedy will survive staff turnover, ownership change, insolvency or loss of access to a maintainer account.
Why continuity is harder than visibility
Continuity claims require a time dimension. A single current observation can establish that a signal was captured. It cannot establish that the signal was uninterrupted. A series of observations can show persistence across the sampled period, but even then the strength of the conclusion depends on the intervals, vantage points and consistency of the underlying identifiers.
For AS210973, the preserved research package establishes that public endpoints were captured for registry, IRR, RIPEstat, PeeringDB and third-party routing evidence. It does not supply a verified longitudinal series from which uninterrupted operation can be inferred. The responsible description is therefore that these sources define a method for checking continuity; they do not, on the available receipt alone, prove durable continuity.
That limitation is operationally significant. Network failure is often not a single event. It can begin with an expired contact, an inaccessible maintainer account, a stale route object, a mismatch between registry and routing policy, or a monitoring blind spot. If an organisation cannot show who owns prevention and detection, a public record of past visibility does little to reduce future risk.
A durable continuity case would require more than one snapshot. It would need dated evidence showing the relevant registry and policy relationships, repeated independent routing observations, clearly attributable contacts, incident or change records where material, and a demonstrated process for correcting stale or conflicting information. It would also need to distinguish technical persistence from institutional persistence. A route may remain visible while the accountable organisation changes; a registry record may remain online while the operational capability behind it degrades.
The control question
The strongest conclusion supported by this evidence is methodological: public network records can be combined into a layered control-and-continuity assessment, but no single layer should be treated as dispositive.
The registry can establish the existence and shape of a record. IRR data can establish a declared routing policy. BGP collectors can establish observed announcements, paths or withdrawals at specified vantage points. PeeringDB can establish self-reported operational context. Cross-source comparison can identify alignment, inconsistency or gaps.
What remains unproven without additional evidence is equally important: legal ownership; beneficial ownership; the identity of the current operator; authority to originate every observed prefix; exclusive control of the ASN; uninterrupted operation; and the durability of any repair. Those are not semantic refinements. They are different propositions requiring different proof.
The distinction also protects against unfair blame. If a route is observed, it is not necessarily fair to attribute every related decision to the Directory subject. If a registry field is stale, that does not by itself prove misconduct. If public sources disagree, the disagreement is a detection signal, not a verdict. Forensic reporting should identify the control gap and the evidence needed to close it without converting uncertainty into accusation.
What would make the conclusion stronger
A stronger accountability finding would require a verified current registry payload, including the relevant status, organisation and contact relationships, with dates. It would require the actual route and route6 objects returned for AS210973, together with their maintainers and authorisation context. It would require the precise announced prefixes, routing state and neighbour observations, again with timestamps and collection limits. It would require comparison across independent monitoring systems and an explanation for material differences.
The operational side would need evidence of control: a responsible organisation willing and able to confirm the records, a monitored abuse or operations contact, documented change and incident procedures, and proof that stale routing or registry data can be corrected. Continuity would be more credible if these controls remained functional through repeated dated checks and if the responsible party could explain how it would respond to a loss of access, an unauthorised route, a registry discrepancy or a prolonged outage.
This is the practical prevention-detection-remedy chain. Prevention means maintaining accurate registry and policy records and limiting who can change them. Detection means comparing registry declarations with observed routing and investigating divergence. Remedy means correcting the record, withdrawing an unauthorised route where appropriate, restoring service and documenting the decision. Durability means demonstrating that the process still works after the immediate incident has passed.
Conclusion: visibility is evidence, not accountability
DATAMATIX and AS210973 illustrate a general rule for internet-infrastructure investigations. Public data is most useful when its layers remain separate. Registration, policy declaration, observed routing and self-reported peering are not interchangeable facts. Together they can reveal a network of relationships and expose questions that require follow-up. They cannot, without corroboration, answer every question about control, authority, ownership or continuity.
The defensible conclusion is therefore bounded. The available research establishes a public evidence trail around AS210973 and provides the sources needed to examine its registry, policy and routing context. It does not establish, on its own, who legally owns the resources, who currently controls the operation, whether every observed route was authorised, or whether service and accountability persisted without interruption.
For boards, operators, regulators and affected communities, that boundary is not a weakness. It is the beginning of a better control system. The relevant test is whether a named responsible party can connect public records to working prevention, detection and repair—and demonstrate that those controls remain effective over time.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance