
Summary
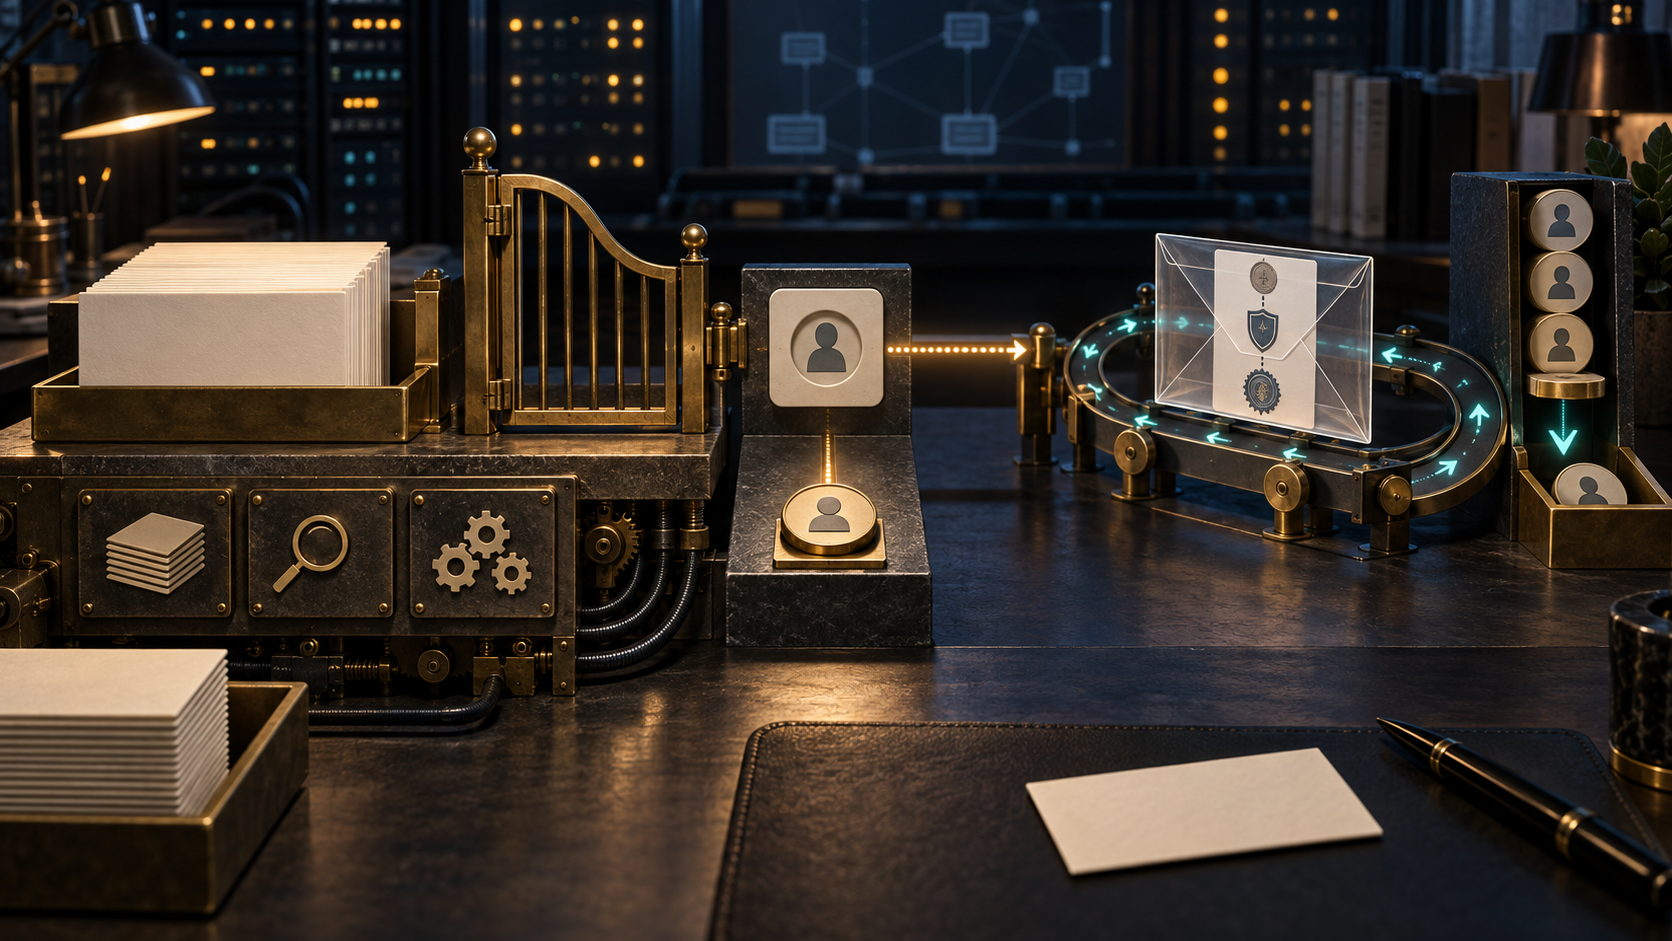
- RFC 3098 treated unsolicited advertising as cost shifting across a shared network. Its answer was an advertiser-controlled list of willing recipients, with non-subscription as the default.
- An immediate confirmation carried the address, submission route, time, source host, headers, advertiser identity and removal instructions. That made a request contestable, not automatically genuine.
Cheap sending moved the bill
Electronic mail changed the marginal economics of distribution. A sender could reach another address for almost no additional postage, while the receiving side paid through access time, storage, administration, filtering and attention. RFC 2635 described this inversion bluntly: in bulk electronic communication, recipients bore much of the cost. Providers then absorbed volume, abuse handling and equipment expenditure and passed those costs to customers.
By April 2001, RFC 3098 approached advertising from inside that cost model. Its opening assertion that the Internet was not a free resource was not a metaphor about manners. An advertisement traversed privately operated systems, occupied recipient resources and used community spaces whose participants had expectations. The ease of transmission did not make those inputs ownerless.
The document did not ban commerce from the network. It tried to define a boundary at which an advertiser could seek attention without making strangers finance the search. That required more than a polite subject line. It required the advertiser to research appropriate venues, display a real identity, obtain permission for the systems used and accept responsibility for the recipient list.
A purchased list did not purchase legitimacy
RFC 3098 devoted unusual attention to compiled mailing lists. Third-party inventories could contain scraped addresses, guesses produced by dictionaries, records copied from old archives and people who had changed jobs or providers. Some vendors, it warned, even recycled removal requests into lists sold as prospects.
The structural lesson was sharper than “buy carefully.” Purchasing a file could not outsource responsibility. Targeting, identity disclosure and list maintenance remained with the advertiser who used it. The party expecting commercial value also bore the work of validating addresses, respecting the owners of other systems and handling complaints.
The document carried that rule forward to data resale. An advertiser that had built a list of willing recipients was not to sell it. Permission given for one relationship did not silently become permission for a business partner. The list was not merely a transferable asset; it represented a bounded expectation between a recipient and a named sender.
The default determined who had to act
The famous checkbox in RFC 3098 appeared inside a larger privacy design. A person submitting information had to know that collection was occurring. If the data would be used for mailings, that intention needed clear disclosure. A person also had to be able to provide the underlying information without accepting advertising.
The RFC recommended configuring collection so that opting out of mail was the default. Joining the advertising list should require a concerted act, such as selecting a box asking for product announcements. In modern language, the interface placed inertia on the side of non-subscription.
That arrangement shifted acquisition cost back toward the advertiser. The business had to earn an affirmative choice rather than benefit from a preselected box, an obscure notice or a form whose unrelated purpose quietly enrolled the visitor. The list might grow more slowly, but every entry had a stronger connection to a stated request.
A box was not magic. It did not prove that the text was understood, that a person rather than automation acted, or that the choice met every jurisdiction's legal standard. RFC 3098 itself warned that privacy rules differed and placed the burden of checking applicable law on advertisers. The historical importance of the checkbox is the default and control it represented, not the shape of the widget.
Confirmation turned a claim into a contestable record
Public forms created another problem: anyone could submit someone else's address. RFC 3098 therefore separated data about a request from the genuineness of the subscription. It said only the owner of the submitted email address could attest to the act of subscribing and recommended that every submission be confirmed immediately.
The confirmation was not meant to be an empty “welcome.” It was to show the subscribed address, how the request arrived, its date and time, the source host's IP address, full request headers where applicable, the advertiser's name and contact points, and instructions for permanent removal. If a third party had entered the address, the owner could see the event and respond.
This was an early provenance bundle for a commercial relationship. It made the advertiser's account of enrolment inspectable. A dispute could refer to a time, route and origin record rather than an unexplained row in a marketing database.
The evidence still had limits. An IP address did not identify the human at the keyboard. A confirmation delivered to an inbox did not prove that the address owner had initiated the form. Headers could assist investigation without turning a request into authorization. The design supplied notice and a challenge path; it did not manufacture certainty.
Removal completed the control loop
Permission can expire. RFC 3098 required advertisers to tell recipients how to remove themselves and urged them to keep list data private. The same relationship that began with an affirmative choice needed a reachable exit.
Other RFCs supplied adjacent machinery. RFC 2369 defined List-Unsubscribe and related header fields so list controls could be exposed in a standardized form. RFC 2142 recorded conventional operational mailbox names such as ABUSE and POSTMASTER. RFC 2505 and RFC 3013 addressed relay control and operational responsibility. Together they show different layers: sender practice, recipient control, machine-readable commands and infrastructure defence.
None of those layers proved that a removal request was honored. A header can advertise a mechanism that fails; an abuse mailbox can go unread; a confirmation can arrive after an unwanted enrolment. The relevant evidence is the complete sequence: the request, the notice, the response, suppression of later sends and retention or deletion policy for the address.
Advice, operations and law remained different authorities
RFC 3098 was Informational and carried the FYI 38 designation. It was not a Standards Track protocol and did not make its ethics legally binding. It also did not report an adoption census. Its recommendations describe what responsible advertisers should control; they do not prove that advertisers did so.
The U.S. CAN-SPAM Act arrived in 2003. FTC material describes legal requirements including identification and a means to opt out. That later legal regime should not be projected backward as if RFC 3098 enacted it, nor should the RFC be presented as the statute's origin without legislative evidence. The two belong to different authority chains.
RFC 3098's durable contribution was operational. It translated responsibility into observable decisions: who selected the default, who held the list, who documented the request, who revealed an identity, and who honored departure. Its answer consistently kept control and cost with the actor seeking the commercial benefit.
That model remains historically useful precisely because it is modest. It cannot prove consent, eliminate deception or guarantee compliance. It can make a claim of permission inspectable and give the recipient a way to contest it. Before consent became a ubiquitous interface label, RFC 3098 had already recognized that the placement of a checkbox, the content of a confirmation and the ownership of a list were decisions about power on a shared network.
Sources
- https://www.rfc-editor.org/rfc/rfc3098.html
- https://www.rfc-editor.org/info/rfc3098
- https://datatracker.ietf.org/doc/rfc3098/
- https://www.rfc-editor.org/rfc/rfc2635.html
- https://www.rfc-editor.org/info/rfc2635
- https://datatracker.ietf.org/doc/rfc2635/
- https://www.rfc-editor.org/rfc/rfc2505.html
- https://www.rfc-editor.org/info/rfc2505
- https://datatracker.ietf.org/doc/rfc2505/
- https://www.rfc-editor.org/rfc/rfc1855.html
- https://www.rfc-editor.org/rfc/rfc2142.html
- https://www.rfc-editor.org/rfc/rfc2369.html
- https://www.rfc-editor.org/rfc/rfc3013.html
- https://www.ftc.gov/legal-library/browse/statutes/controlling-assault-non-solicited-pornography-marketing-act-2003-can-spam-act
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance