
Summary
- Revision 02 of an individual Informational Internet-Draft proposes separate authority for identity, content, relationship mapping, reconstruction and output release. It remains work in progress, not an IETF standard, certification or deployment record.
- The practical contribution arrived in the 6 September revision sequence: expensive preparation may happen on a cold path, but current session, epoch, revocation, association, destination and receipt checks remain on the hot path. A cached decision cannot authorize a later consequential join merely because it was once valid.
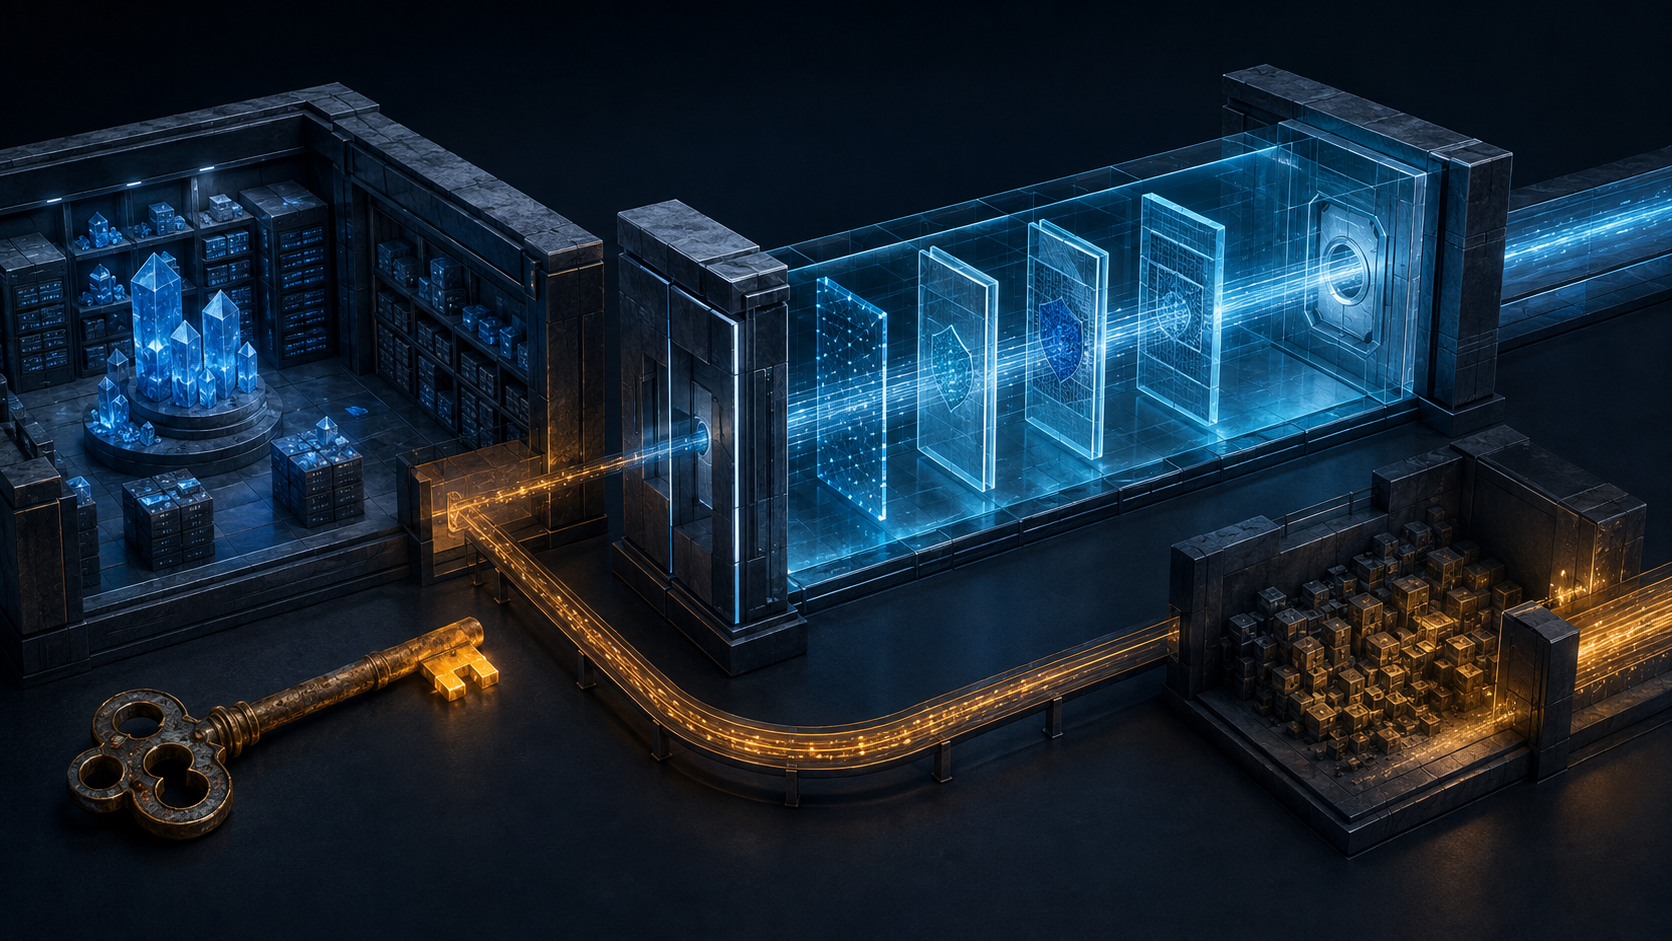
- A gateway, proxy or sidecar becomes a control boundary only when old database credentials, debug interfaces, alternate APIs, file paths and network exits can no longer complete the protected act. The right acceptance test is a bypass attempt, not the presence of a component.
The migration team has placed a policy sidecar beside the enterprise assistant. Every approved request now appears to pass through it. The dashboard shows green checks; the demo produces a signed receipt; the latency graph is respectable. Then an engineer opens an old service account, connects directly to the original database and retrieves the same identity-content join. The architecture changed. Authority did not.
That is the sharpest idea in revision 02 of A Compromised AI Server Must Not Become a Map of the Enterprise. The document is an individual Internet-Draft by S. Das, dated 6 September and listed by the IETF Datatracker in I-D Exists. Its intended status is Informational. It is not a working-group result, IETF consensus, an RFC or evidence that any enterprise has deployed the design.
The document history matters because the versions do different work. Revision 00 establishes the proposed separation between reconstruction and release. Revision 01 answers the obvious operational objections: multiple vaults sound slow, and most enterprises cannot replace joined databases or existing model interfaces at once. Revision 02 adds a review FAQ and motivation while explicitly saying it does not change the core normative requirements.
Preparation is not permission
The draft allows a cold path to prepare compiled policies, permitted-association graphs, protected indices, workload measurements, destination manifests, attestation collateral, revocation state and provenance schemas. This is sensible engineering. A system should not repeat invariant work on every model turn merely to look rigorous.
But preparation and permission occupy different reality layers. A policy compiled yesterday says what the rules were then. An identity lookup says what a record resolved to when it ran. An attestation says something about a measured workload at a stated time. None says that this actor, session, purpose, recipient and destination are authorized now.
The proposed hot path therefore keeps the conditions whose omission could create an unauthorized join or external effect: current session epoch, policy, revocation, workload correspondence, association scope, provenance, destination, recipient, receipt state and release boundary. The draft's rule is unusually useful for procurement: a cached policy decision, identity result, mapping result or attestation cannot independently authorize a later reconstruction because it was once valid.
That distinction also prevents a familiar performance bargain from silently rewriting the security model. A team may precompute more, cache more and fan out work in parallel. It may not move the decision that creates authority into the cache.
Parallel vaults can remain independent
The design separates identity, content and relationship mapping. Having permission to read a name and permission to read a ticket does not automatically confer permission to say that the named person owns the ticket. The association itself is protected authority.
A Reconstruction Authorization Object binds a proposed join to purpose, session, epoch, fields, association scope, execution context, use count and reconstruction domain. Once that object exists, the three domains need not answer serially. They can evaluate in parallel, so latency approaches the slowest required decision plus orchestration rather than the arithmetic sum of every round trip.
Parallelism is not pooled sovereignty. A release by one vault does not compel the others. If the relationship authority denies, returns stale state or becomes unavailable, the successful identity and content releases do not add up to an authorized reconstruction. Partial success must be discarded, invalidated or retried under unchanged state—not reinterpreted as permission to use the missing path.
The same principle continues after computation. The model produces a Candidate Output. The proposal then seals it, validates current conditions, commits a receipt and issues a single-use capability bound to the output, recipient, destination, session and boundary. A screen render, file commit, memory write, tool invocation or network send is treated as release because that is where the result becomes usable.
RFC 7515 can bind a signature to a JSON object; RFC 8785 can make its representation deterministic; RFC 9334 distinguishes evidence from appraisal and the resulting attestation decision. Those mechanisms can make a claim inspectable. They do not close a forgotten socket.
Legacy compatibility has a negative requirement
The draft permits incremental migration. A protected intermediary may translate ordinary model requests into vault-local operations. Existing records may be decomposed when accessed. Relationship mappings may move before content. An identity field may be tokenized while a legacy database still holds the substantive record.
This flexibility is valuable and dangerous for the same reason: both old and new paths coexist. A diagram can show the new gateway while a service account, maintenance console, cached secret, direct query, retrieval endpoint, file share or emergency egress route preserves the old power.
The draft calls non-bypassability the final requirement. If the compromised workload can still use a direct database credential to reconstruct the identity-content relationship, Technical Non-Joinability has failed. If it can send the derived result through an unmediated API, debug channel, file, message or network route, output finality has failed. Installing a sidecar beside the old path is not migration completion.
The observable test is negative: attempt the forbidden act through every authority-equivalent path and require denial. Inventory credentials, not just services. Trace where plaintext first becomes readable, where associations can be formed and where outputs first become usable. Include break-glass, batch, backup, analytics and developer routes. A control boundary is the set of paths that no longer work without current authority.
Running code narrows the claim
The accompanying v0.1.0 reference repository reports 16 tests and a roughly 2.38 ms median for a warm, local, sequential 500-iteration benchmark. Both the draft and repository bound that number carefully: it excludes network calls, remote attestation, HSM or KMS work, distributed commit, model inference, production databases, logging and real external effectuation.
More importantly, the three example vaults are Python objects in one process. Compromise of that process can defeat their local boundaries. The implementation shows that the proposed state machine can execute; it does not show production isolation, compliance or universal resistance to semantic inference. Repeated individually lawful outputs may still reveal a protected relationship.
Heng Lu's reality-layer discipline keeps the draft, configured component, live credential, receipt, denial and external effect separate. Running-Code Primacy puts the bypass test above the diagram. The Minimum Initial Specification supplies the right scale: standardize the few bindings needed for independent verification and leave vault topology and migration order local.
The result is a harder but cleaner definition of progress. A sidecar is not successful when traffic can be shown passing through it. It is successful when the old authority can no longer complete the same act.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance