
Executive summary
- Traefik Labs is the private open-core company behind Traefik Proxy, whose first code was written by founder Emile Vauge in 2015 before the company was formed as Containous in 2016.
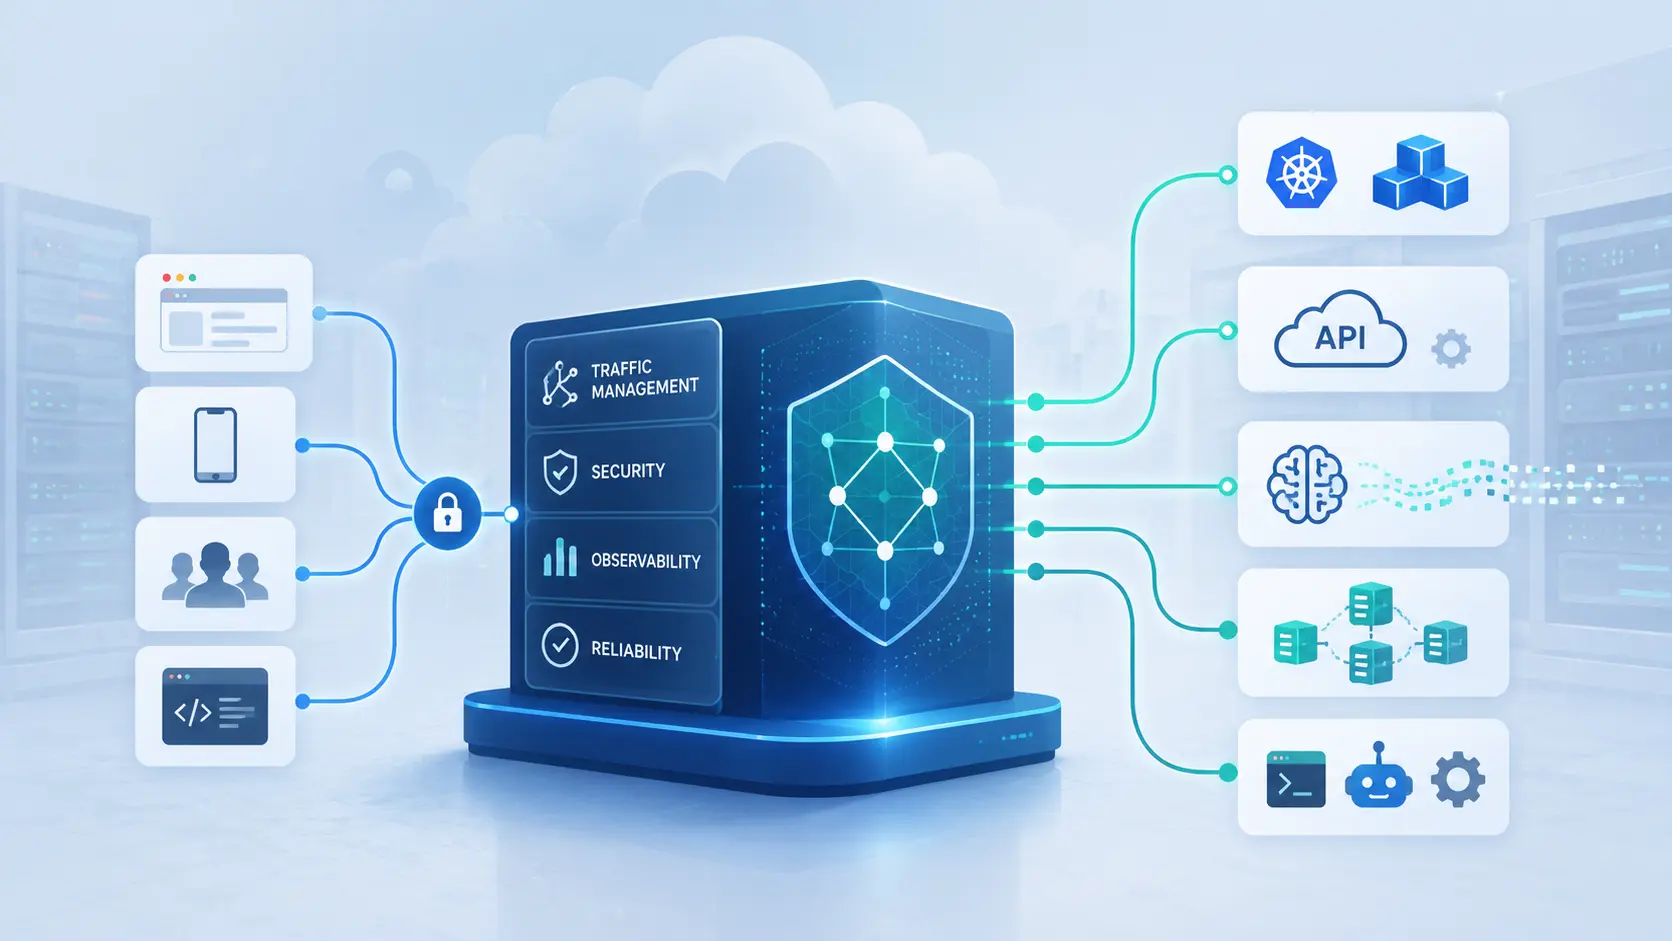
- Traefik’s provider-driven architecture watches infrastructure sources such as Docker and Kubernetes, then converts service metadata into routing and policy objects without rebuilding a static proxy configuration after every change.
- Traefik Hub, AI Gateway and MCP Gateway extend the company’s commercial reach from ingress into API governance, model-provider traffic and agent-to-tool connections, increasing both its value and its operational responsibility.
- Traefik reported 1,000 contributors and 3.5 billion official Docker-image pulls in July 2026, but those figures do not establish a unique installation count, customer total or paid conversion rate.
A gateway company, not a network operator
Traefik Labs does not own a global content-delivery network, provide cloud-computing capacity, operate an autonomous system or sell access connectivity. Its software normally runs on infrastructure selected and controlled by customers. Even so, a Traefik deployment can sit directly in the path of production traffic, accepting a connection before the application sees it, terminating encryption, selecting a backend, applying authentication, modifying headers, enforcing rate limits and recording operational data.
That position gives the company influence beyond the apparent size of a proxy binary. A gateway is a decision point between external demand and internal services. When the configuration and policy are correct, application teams can release services quickly while infrastructure teams apply consistent controls. When they are wrong, one change can expose an administrative endpoint, trust an attacker-supplied identity signal, break certificate handling or redirect traffic across a large application estate.
This profile concerns Traefik Labs, the private software company, rather than Traefik Proxy alone. Traefik Proxy is an open-source project with its own repository, contributors, releases, licence terms, issues and security advisories. Traefik Labs employs maintainers, develops commercial products, sells support and enterprise functions, and uses the proxy’s broad adoption as an open-core distribution channel. The project and company are tightly connected, but they are neither legally nor institutionally identical.
The verified operating structure includes Traefik Labs SAS in France and Traefik Labs, Inc. for parts of the company’s non-European activity. Current legal material identifies the French entity at 132 rue Bossuet in Lyon and lists SIREN number 818103475. Public sources do not provide consolidated audited accounts, a complete capitalisation table, current valuation, product-level revenue or a verified customer count, so the available evidence supports an analysis of Traefik’s operating and commercial model rather than a complete financial assessment.
The central issue is straightforward. Traefik became useful because it removed repetitive configuration work from a rapidly changing application environment. The company now wants the same gateway position to govern APIs, model providers, agents and tools. That expansion can give customers one consistent policy layer, but it also increases the consequences when the layer fails, is compromised or becomes difficult to replace.
Traefik began with a configuration problem
Traditional reverse-proxy operations assumed that backend services changed comparatively slowly. An administrator could define a list of servers, configure virtual hosts, test the file and reload the proxy. That method remained effective for stable estates, but containers and orchestrators changed both the pace and ownership of infrastructure change. Services could be created, rescheduled, scaled, replaced or destroyed while applications continued to operate, making the address of one backend less durable than the service identity stored in orchestration metadata.
In such an environment, every manual configuration step becomes a source of delay and failure. A deployment system can start a service in seconds, yet the service remains inaccessible until the traffic layer recognises it. A ticket queue can become the slowest part of an otherwise automated platform, while repeated file generation and reloads create opportunities for stale endpoints, conflicting changes and configuration that no longer matches the running infrastructure.
Traefik’s answer was to make the proxy observe the system that already holds the desired state. Docker labels, Kubernetes resources, configuration files and other provider interfaces become inputs. Traefik interprets those inputs and reconciles its runtime routing objects, allowing application deployment metadata and network behaviour to move through the same operational loop.
The design was sometimes described as making networking “boring”. In this context, the term means predictable enough that a developer should not need a specialist ticket for every route or certificate. A service appears with approved metadata, the gateway discovers it, the route becomes available and certificate automation handles a repeated task. Network specialists can then spend more time on platform design, security boundaries and exceptional failures instead of routine service exposure.
The first Traefik code was written by Emile Vauge in 2015. The commercial company was established in 2016 under the name Containous, so the project and company have related but distinct starting dates. The early project gained attention because its use case was immediate and demonstrable: developers could run Traefik beside Docker, define routing through labels and experience the value before entering a procurement process.
Kubernetes created another natural deployment point as cluster ingress became part of mainstream cloud-native architecture. Automatic certificate acquisition through the Automatic Certificate Management Environment, or ACME, removed a second category of repetitive work. These capabilities made Traefik easy to evaluate and helped the project spread through developer and platform-engineering communities before the company had to persuade each user through a conventional sales process.
Containous gave the project a commercial structure able to employ engineers, maintain documentation, develop enterprise functions and support organisations whose requirements went beyond a community deployment. It also introduced a difficult business question: how could the company build durable revenue around software whose basic appeal depended on being freely available and easy to adopt?
By 2020, the corporate name and project name had become misaligned. Developers recognised Traefik, while investors, employees and customers dealt with Containous. The company rebranded as Traefik Labs in September 2020, aligning its identity with the project that carried the strongest recognition. The change also made the company’s reputation more directly dependent on the health, openness and security of the public project.
Dynamic configuration turns metadata into network policy
Traefik’s operating model rests on several concepts that separate network exposure, configuration discovery, request matching, backend delivery and policy. Entry points define where traffic reaches the gateway, usually through particular ports and protocols. Providers supply configuration from infrastructure sources. Routers decide whether a request matches a rule, services identify the backends able to handle it, and middleware changes or filters the request between matching and delivery.
Entry points define the outer shape of the deployment. They may represent ordinary HTTP, encrypted HTTPS or another supported protocol, and they determine listeners, addresses and foundational transport behaviour. A platform team can use separate entry points for public, internal and administrative traffic, although the strength of the separation still depends on the surrounding network, credentials and deployment design.
Providers connect Traefik to changing infrastructure. A Docker provider can inspect labels and container state, while a Kubernetes provider can watch Ingress resources, Traefik custom resources or Gateway API objects. A file provider can load dynamic routing and policy objects from configuration files. Provider permissions therefore determine more than what Traefik can observe; they define the part of the platform from which network authority can be derived.
Routers evaluate host names, paths, headers, methods and other conditions. When a request arrives at an entry point, matching and priority rules determine which router handles it. That router can reference a middleware chain and a service. The abstraction is understandable in ordinary deployments, but overlapping rules can still produce an outcome that is technically consistent with precedence while surprising the operator who created one of the routes.
Services represent the delivery side of the system. They identify backend servers or destinations and can distribute traffic among them, using health checks, sticky-session behaviour and transport settings where configured. Dynamic discovery helps keep membership aligned with the orchestrator, but it cannot prove that an application returning a nominally healthy response is producing correct business results. Application health and gateway health remain related but separate concerns.
Middleware is the point at which traffic direction becomes policy. Redirects, path rewriting, authentication, header processing and rate control can be created once and reused across routers. This reduces duplication, but the order of operations becomes part of the security model. A path transformed before authorisation may be treated differently from one transformed afterwards, and a header added before authentication may interact differently from one added after a trusted identity has been established.
The architecture also separates static and dynamic configuration. Static configuration establishes process-level conditions such as entry points and enabled providers, while dynamic configuration contains routers, services and middleware that can change while the gateway remains running. The distinction prevents every metadata source from changing every aspect of the gateway, creating an outer operational boundary within which application-level routing can remain flexible.
The reconciliation loop connects these parts. A provider observes a source, detects a desired-state change, translates it into Traefik objects and updates the runtime configuration. The system does not need a human or external script to render a complete proxy file after every event. It continuously turns infrastructure state into the routing and policy state that the gateway should apply.
This model reduces configuration lag, but it introduces distributed-systems failure modes. Provider events may be delayed, permissions may change, an object may be accepted by the orchestration platform but rejected by Traefik, or two controllers may interpret related resources differently. Operators need visibility into both the source object and Traefik’s resulting configuration because neither view alone establishes that the intended traffic path is operating.
Service discovery makes this trade-off especially clear. The orchestrator already knows which services and endpoints exist, allowing Traefik to follow workloads as they move without maintaining a separate server inventory. The service identity remains stable while individual backend instances appear and disappear. The same convenience means that discovery scope becomes authority scope: metadata which once described a workload can now determine whether and how it is exposed.
A routing label, annotation or custom resource should therefore be treated as executable network policy. Organisations need to decide which identities may publish routes, which namespaces they may affect, which entry points and middleware they may reference, and whether they may expose a new public host. Automation removes a handoff, but it does not remove the need to allocate authority.
Admission controls and policy engines can prevent some unsafe resources from entering the platform. They can require approved host patterns, certificate issuers, middleware references or namespace relationships, and they can detect forbidden annotations or overlapping routes before the gateway receives them. Runtime verification remains necessary because the final interpretation belongs to the controller and data plane rather than to the admission rule alone.
Routing and health checks carry similar limits. Traefik can choose among backends and withdraw an endpoint that fails a configured check, but it cannot determine whether a successful application response represents a correct transaction. A service may return an HTTP success status while serving stale data or depending on a failed downstream system. The gateway automates transport decisions; it does not replace application-level observability or business validation.
The safest operational model tests both successful and rejected behaviour. A platform should verify that intended requests reach the correct application, but also that unexpected hosts, administrative paths, unapproved methods and malformed identity headers are rejected. A shared gateway can reproduce good policy across many services, yet it can reproduce a mistaken template with the same efficiency.
Kubernetes widened both adoption and governance
Kubernetes gave Traefik an environment closely matched to its provider model. Traditional Ingress resources offered a standard way to expose HTTP services, while annotations supplied implementation-specific behaviour. Traefik custom resource definitions provided richer routing and middleware objects. The newer Kubernetes Gateway API attempts to define clearer roles for infrastructure providers, gateway operators and application teams.
Supporting these models gives organisations several migration and compatibility paths. An established cluster can retain Ingress resources, use Traefik-specific objects where additional capability is needed and adopt Gateway API as the platform matures. The breadth is commercially useful, but it also creates a larger testing and documentation burden because feature availability, status handling and cross-resource behaviour can differ by release and configuration model.
Gateway API is strategically important because it makes organisational authority more explicit. Infrastructure teams can manage GatewayClass and Gateway resources, while application teams attach routes within permitted scopes. Reference grants and namespace controls can reduce the ambiguity created by annotation-heavy patterns, although they work only when the implementation and platform policy enforce those relationships correctly.
Support for a standard should not be read as support for every optional feature. A resource may be accepted by the Kubernetes API server while remaining unresolved or only partly implemented by the controller. Platform teams still need release-specific tests covering route attachment, certificate references, protocol support, filters, status reporting and cross-namespace access.
Migration requires behavioural comparison rather than mechanical conversion. An Ingress annotation may not map directly to a Gateway API filter, and a Traefik middleware chain may have no exact equivalent in a standard resource. Rewriting manifests without testing the resulting traffic path can change precedence, identity handling or certificate behaviour while leaving the deployment apparently healthy.
The wider ingress market is also changing as projects evolve, products are retired and organisations reconsider their controller strategies. Traefik can benefit when it offers a credible migration path, strong Gateway API implementation and familiar operating model. It can lose ground when supporting several resource systems makes behaviour difficult to reason about or when a managed cloud gateway removes enough operational work to justify tighter provider dependence.
Kubernetes therefore expanded more than Traefik’s adoption opportunity. It made the gateway part of a distributed governance system in which application manifests, namespace permissions, custom resources, admission policies and controller behaviour all contribute to one traffic decision. The proxy configuration became less visible as a single file, but the underlying policy did not disappear; it spread across the platform.
Identity and encryption create the most sensitive boundary
Middleware allows platform teams to provide reusable controls for authentication, redirection, header handling, path rewriting and rate limiting. That can improve consistency by keeping common outer-layer policy out of individual applications. It also means that one middleware component or chain may influence many services at once, increasing both the value of careful review and the blast radius of a mistake.
Identity handling is among the highest-risk uses. A gateway may authenticate a user through an external service and pass identity information to the backend in headers. The application then relies on Traefik to remove any attacker-supplied versions of those headers and insert trusted values. The security boundary therefore includes header normalisation, removal, insertion, trusted network paths and the application’s willingness to reject direct requests that bypass the gateway.
A Traefik security advisory published in July 2026 illustrated the sensitivity of this mechanism. In affected authentication-middleware configurations, underscore variants and header-name handling could allow an attacker-supplied identity header to remain in a request and be trusted downstream. Operators needed to upgrade to patched releases and review whether their configuration relied on the affected pattern.
The advisory does not establish that every Traefik authentication configuration was unsafe, nor does the patch remove the architectural need for a trusted-proxy design. It shows that apparently small differences in header handling can alter the identity boundary. The backend must be reachable only through authorised paths, and the gateway must remove or replace untrusted identity signals before the application receives them.
Middleware ordering can create similar consequences without a software defect. Rewriting a path before authorisation may change the resource assessed by the authentication service. Adding, preserving or stripping a header at the wrong stage can alter what the application trusts. Reusable chains therefore need explicit semantics, version control and behavioural tests rather than informal assumptions about the effect of their names.
Ownership must be designed with the same care. Allowing every application team to create or attach arbitrary middleware can weaken central controls, while forcing every change through one platform group can recreate the ticket queue Traefik was designed to avoid. One workable division is for security or platform teams to maintain approved components and for application teams to select among them within clearly defined namespace and host boundaries.
TLS automation adds another form of leverage. Through ACME and configured certificate sources, Traefik can obtain and renew certificates, terminate encrypted connections and centralise transport policy. This removes repetitive renewal work and can make secure service exposure easier, but it also places private keys, certificate state and external account credentials in an infrastructure component serving many applications.
Certificate automation depends on more than the proxy process. DNS challenges may require credentials for a DNS provider, HTTP challenges require reachability, certificate authorities impose rate limits, and failed renewal or storage migration can affect several domains. Organisations need expiry monitoring, tested backup and recovery, controlled access to account material and a clear understanding of where certificate state is stored.
TLS termination also gives the gateway visibility into request metadata and, depending on configuration, decrypted content. That visibility supports routing, logging and threat detection, but it creates privacy and data-governance duties. Logs and traces should not become uncontrolled stores of credentials, personal information or application payloads merely because the gateway can observe them.
Centralised certificate handling can also increase switching costs. Moving to another gateway may require transferring account state, certificates, renewal responsibility and trust policy in addition to reproducing routes. A resilient design should therefore document both recovery and migration, allowing the identity and encryption layer to survive the failure or replacement of one gateway platform.
Open source built distribution; Traefik Labs built the business
Traefik Proxy is the company’s main adoption engine. Developers can download it, run official images, inspect the code, report issues, contribute changes and develop operational familiarity without first buying a commercial product. That lowers the cost of evaluation and gives Traefik Labs access to a distribution channel that a closed infrastructure platform would struggle to reproduce.
The company converts a portion of this adoption into demand for support, management, governance, hardened packaging and specialised gateway capabilities. Organisations that have already operated Traefik Proxy may be easier to educate about Traefik Hub because the data-plane concepts are familiar. The commercial relationship begins from an installed technical base rather than from a wholly new platform sale.
The boundary between project and company remains important. Traefik Labs controls its commercial roadmap and employs central maintainers, while external contributors participate in the public repository. Contributing code does not create ownership or corporate voting rights, and investor relationships do not automatically determine the outcome of every public design discussion. Practical influence is visible through maintainership, review, release decisions, licensing and the distribution of technical work.
Open-core businesses have to balance several interests. Community users expect a capable, maintained and trustworthy open product. Enterprise customers expect differentiated functions and reliable support. Investors expect growth, while maintainers need enough time and resources to preserve quality. If commercial packaging weakens the community edition or creates uncertainty about previously expected functions, the distribution engine can lose trust; if the paid layer offers too little additional value, the company may struggle to fund the maintenance and enterprise development expected of it.
Containous announced a $10 million Series A on 15 January 2020. Balderton Capital led the round, with Elaia and 360 Capital participating. The financing supported enterprise product development, commercial expansion and international growth as Kubernetes and cloud-native networking moved further into mainstream infrastructure planning.
The verified Series A should not be presented as the company’s complete financing history. Current company material also identifies Kima Ventures and OSS Capital among investors, but the public record does not disclose ownership percentages, current board voting arrangements, total capital raised through every instrument or a current valuation. An investor list establishes participation, not control.
The September 2020 rebrand from Containous to Traefik Labs coincided with a broader product ambition. At the time, the company referred to products including Proxy, Mesh, Enterprise and Pilot. Those names describe the historical portfolio rather than the present strategy. By the 2026 research cutoff, the clearest commercial emphasis was Traefik Proxy, Traefik Hub, AI Gateway and MCP Gateway.
Executive leadership changed on 1 February 2024. Sudeep Goswami became chief executive, while founder Emile Vauge moved from the CEO role to chief technology officer. Gerald Croes is publicly identified as vice president of engineering and Sebastien Francois as head of finance, although public evidence does not disclose the company’s complete board, internal voting rights or reporting structure.
The transition separates commercial scaling from the founder’s technical and community role. A specialist chief executive can concentrate on enterprise sales, international expansion and organisational design while the founder maintains architectural continuity. The arrangement can also create different centres of influence, with commercial performance and project trust placing pressure on the same roadmap from different directions.
The community has no formal corporate vote merely because it contributes code or uses official images, yet its willingness to adopt, report, review and recommend the software has material economic value. Leadership must therefore manage a constituency that is central to the business without being equivalent to customers, employees or shareholders. Long-term resilience depends on review capacity and maintainership succession extending beyond any one founder or executive.
Traefik’s reported adoption indicators are large. In July 2026, Emile Vauge said the project had reached 1,000 contributors and 3.5 billion official Docker-image pulls. These figures establish broad participation and repeated consumption of the official images, but they do not establish 3.5 billion unique installations, customers or users.
One cluster may pull the same image many times, while continuous-integration systems, mirrors and automated updates can produce further events. A single organisation can account for a large number of pulls. Contributor totals have similar limits because one documentation correction and years of maintenance both count as contribution, despite representing very different levels of responsibility.
The company had reported more than two billion downloads during the 2020 rebrand, but historical and current figures may use different definitions. They should not be converted into a growth rate without a consistent method. The direction of adoption is well supported; the current number of active production deployments, maintained versions and paying customers remains unavailable.
Traefik Hub moves the company beyond ingress
Ingress answers how external traffic reaches an application. API management adds questions about identity, policy, versioning, discovery, observability and organisational ownership. Traefik Hub represents the company’s move from a routing component towards a commercial API gateway and management platform.
The product builds on the proxy runtime while adding discovery, policy, management and enterprise visibility. This creates a relationship between a data plane that processes traffic and a management or control plane that helps operators define, distribute and observe policy. Customers need to understand which functions continue locally during a management-plane outage and which updates depend on continued access to central services.
Central discovery can help organisations find interfaces that would otherwise remain distributed across clusters and teams. Shared policy can reduce inconsistent authentication and rate controls, while management tools can provide an inventory of routes, certificates and gateway health. These functions become more useful as the number of services grows faster than a central platform team can inspect manually.
API management is nevertheless broader than reverse proxying with a management interface. Large organisations may expect developer portals, lifecycle governance, version controls, analytics, identity integration and policy workflows. Companies such as Kong and other API-platform vendors compete on those dimensions, while cloud providers offer managed gateways tied closely to their own identity, billing and operational systems.
Traefik’s advantage is continuity with a data plane and developer experience that many teams already understand. An organisation already using Traefik Proxy can add management and policy without replacing every runtime component. The disadvantage is that enterprise requirements can pull the product away from the simplicity that drove adoption, creating a platform whose internal behaviour becomes harder for application teams to inspect.
Commercial packaging therefore matters. Product names and pages establish that functions are offered, but they do not prove that every capability is included in every edition or contract. Buyers need to evaluate the exact management, policy, support and recovery functions they require. The commercial test is whether Hub produces enough governance and operational leverage to justify the additional control-plane dependency.
AI and MCP gateways widen the consequences of a routing decision
AI applications often call model providers through HTTP-based interfaces, which makes the traffic appear similar to an ordinary API. The operational meaning is different. Requests may incur costs measured in tokens, responses can stream for long periods, provider models differ in quality and policy, and prompts may contain proprietary, personal or regulated information.
Traefik AI Gateway applies authentication, provider routing, quotas, observability and policy to this traffic. A central gateway can keep provider credentials away from individual applications, provide a common record of consumption and help organisations apply limits across teams. It can also give platform operators one place to implement provider-selection and failure rules.
Model routing cannot be reduced to ordinary load balancing. Two providers or models may not produce equivalent outputs, and a failover that preserves availability may change quality, safety behaviour, data residency, price or contractual treatment. Operators need to define when substitution is acceptable and how the application learns that it occurred.
Token economics also change the meaning of rate control. One request can be far more expensive than another, and a small prompt may lead to a large streamed response. Useful policy may need to consider token volume, model class, concurrency, tenant budget and duration rather than relying only on requests per second. The accuracy of those controls depends on provider metadata and the gateway’s ability to interpret it consistently.
Data governance is especially sensitive because a gateway may observe prompts and outputs. Logging useful for debugging can create a second store of sensitive content. Redaction, access control, retention, encryption and residency therefore need to be designed before the gateway becomes a central point for model traffic.
Independent evidence of large-scale adoption of Traefik’s AI Gateway was limited at the research cutoff. The product is aligned with a genuine infrastructure need, but availability does not establish market leadership or broad production use. Its commercial position will depend on customer references, provider breadth, policy quality and the pace at which the product adapts to changing model interfaces.
The Model Context Protocol, or MCP, extends the policy problem from model requests to agents and tools. MCP allows hosts and agents to discover servers exposing tools and resources. A tool call can read a document, query a database, modify a ticket, run code or trigger an external action, giving the gateway influence over activity with consequences beyond returning information.
Traefik MCP Gateway applies routing, inventory, authentication and access controls to these connections. It can reduce the number of direct, unmanaged relationships between agents and tool providers and make the environment easier to inspect. The useful policy boundary, however, is often narrower than the server itself.
An agent authorised to list documentation may not be authorised to delete records, even when both operations are available through the same MCP server. Tool-level permissions, tenant separation, origin controls and audit are therefore necessary if the gateway is to provide meaningful governance rather than simple connection brokering.
Prompt injection adds a different limitation. An agent can be influenced by untrusted content before choosing a tool, and the gateway cannot determine the safety of every semantic decision merely by authenticating the connection. It can restrict the available tools, require stronger approval for dangerous actions, record calls and limit network reach, but it does not make an unsafe agent or server safe.
MCP also creates discovery and lifecycle challenges. Servers, tools and schemas may change rapidly, credentials need rotation, and an experimental integration can become business critical without passing through an established API-governance process. A gateway inventory can make these relationships visible only when the inventory is linked to ownership, classification and change control.
Independent deployment evidence for MCP Gateway was also limited at the cutoff. The product represents a coherent extension of Traefik’s original logic because dynamic endpoints and policy remain central to the problem. The uncertainty is whether Traefik Labs can add the security semantics required for agents and tools without weakening the reliability and clarity of its core proxy and API products.
Security and operations decide whether consolidation is safe
A reverse proxy processes attacker-controlled traffic at a privileged boundary. Traefik may parse protocols, terminate TLS, call authentication services, modify headers and select internal destinations. Each capability creates additional code paths, configuration choices and trust assumptions, while the commercial expansion into APIs, AI and MCP increases the range of data and actions passing through the gateway.
The project published or updated several security advisories during 2026 and described the year as a record period for vulnerability reports. A high report count can reflect a large and heavily scrutinised attack surface, active disclosure and genuine software defects at the same time. The number alone is therefore less useful than severity, exploitability, response speed, patch availability and the rate at which operators deploy fixed versions.
The July identity-header advisory showed the operational work required after disclosure. Teams had to identify affected versions, determine whether they used the relevant authentication pattern, apply a patched release and test the complete trusted-proxy chain. A fixed upstream version provides no protection to an untracked deployment that remains pinned to an older image.
Configuration is a separate risk category. A fully patched gateway can still expose a service through an overly broad route, trust the wrong namespace, retain sensitive logs or allow clients to bypass the gateway and reach a backend directly. Security guidance must therefore cover software vulnerabilities, routing authority, provider permissions, middleware semantics, certificate handling and surrounding network controls.
Traefik Proxy v3.7.10 was released on 31 July 2026, showing an active patch and release cadence at the cutoff. Release frequency becomes operationally useful only when organisations maintain an inventory of deployed versions and can test upgrades against the behaviour they rely on. A process that starts successfully may still have changed route precedence, middleware handling or Gateway API status.
A useful inventory should identify each deployment, its version, enabled providers, entry points, configuration model, attached middleware and support owner. Gateways created independently by application teams can escape central patching and monitoring. Cumulative image-pull figures offer no indication of whether an affected instance remains active in production.
Upgrade testing should examine the traffic path rather than only process health. Critical hosts, rejected access cases, certificate renewal, authentication headers, timeouts, retries and backend selection all need behavioural checks. Canary deployments can reduce risk by directing a limited portion of traffic through a new version before wider promotion.
Blast radius is a design choice. A shared gateway reduces duplicated work and makes common policy easier to apply, but one configuration error or software defect may affect many teams at once. Separate deployments can isolate tenants, environments or critical services, although they create additional operational work and more instances to inventory.
Redundant replicas protect against the failure of one process or host. They do not protect against an incorrect dynamic configuration distributed to every replica. Resilience therefore requires configuration validation, reliable rollback and, for critical services, a tested route to a last-known-good state.
Observability must connect the whole decision chain. Operators should be able to trace a request from its entry point through the selected router, middleware chain and backend, and then identify the label, annotation, custom resource or file that created that path. Metrics may reveal that requests are failing, but configuration provenance is often required to explain why.
Continuity also requires an exit plan. Customers should understand how to recreate routes, certificates, policies and management-plane state on another platform. Portability is not evidence that Traefik lacks value; it is evidence that the gateway is being managed as replaceable infrastructure rather than allowed to become an undocumented permanent dependency.
Competition now spans several infrastructure markets
Traefik faces different competitors depending on the problem a customer is solving. In open-source reverse-proxy and Kubernetes ingress deployments, NGINX, NGINX Ingress and HAProxy have long operating histories. Envoy-based systems provide programmable data planes used in gateways and service meshes, while other Kubernetes-native controllers compete through simplicity, standards conformance and ecosystem integration.
In enterprise API management, Traefik competes with Kong, Tyk, Gravitee, Apache APISIX and other platforms offering policy enforcement, developer tooling, analytics, lifecycle management and support. Cloud providers offer managed ingress and API gateways that reduce the customer’s operational burden within one ecosystem. Those services may be attractive even when they increase dependence on the provider or make policy less portable across environments.
Service-mesh gateways overlap with Traefik when organisations want workload identity and east-west policy in addition to north-south ingress. One architecture may use Traefik at an external boundary and another data plane internally, while another may prefer a unified Envoy-based system. The relevant comparison depends on the operating model rather than a general feature list.
AI gateway competition is expanding as specialist startups and established API-management vendors add model routing, token accounting, provider monitoring and guardrails. Traefik benefits from an existing proxy, a cloud-native user base and experience operating in the traffic path. It must still demonstrate that its AI capabilities address the distinct cost, data and failure characteristics of model traffic rather than presenting ordinary API controls under new terminology.
MCP governance is less mature. Competitors include specialised agent-security companies, controls built into broader platforms and direct management of individual MCP servers. Launching a gateway in this market establishes strategic intent, but it does not establish leadership while the protocol, security model and operating practices remain in development.
Traefik’s clearest differentiation is the combination of provider-driven dynamic configuration, developer familiarity and a path from an open-source proxy to commercial traffic governance. Its constraints include limited financial disclosure, competition across several product categories and pressure from vendors with deeper API-management portfolios or built-in cloud distribution.
Standards will influence how durable that differentiation becomes. Strong Kubernetes Gateway API support can reduce migration costs and make Traefik relevant across a wider range of deployments. Proprietary policy functions can create commercial value, but they can also increase switching costs. The company must decide which capabilities should remain portable and where specialised functions justify tighter control.
The strategic test is whether simplicity survives concentration
Traefik Labs has a coherent expansion logic. Traefik Proxy began by discovering changing application endpoints and routing traffic to them. APIs added identity, lifecycle and policy requirements. Model providers introduced token cost, data handling and provider-selection decisions, while MCP servers exposed changing sets of tools and resources to agents.
Across these categories, the gateway performs a related function: discover endpoints, accept requests, identify clients, select destinations, apply policy and record activity. If the strategy succeeds, Traefik Hub could provide one control layer for application, API, AI and MCP traffic while Traefik Proxy remains the familiar open-source data plane. Customers could reuse identity systems, policy methods and operational processes instead of deploying a different gateway for every workload.
The same consolidation creates concentration risk. One platform would need to operate reliably across HTTP routing, Kubernetes integration, API governance, model-provider policy, prompt handling and tool authorisation. A configuration error, software vulnerability or management-plane compromise could affect several workload classes at once.
Expansion also places pressure on organisational focus. Maintaining a widely distributed open-source proxy already requires engineering, security, documentation and release capacity. API management requires additional product and support work, while AI and MCP introduce fast-changing interfaces and specialised security problems. Investment in those markets may strengthen Traefik Labs’ platform position, but it can also divert attention from the reliability of the core gateway.
The decisive evidence will come from operational boundaries rather than product names. Data planes should continue to enforce safe local policy when central management services are unavailable. Policies should remain inspectable, critical workloads should be isolatable, and AI prompts should not enter ordinary logging systems without deliberate controls. MCP authorisation should operate at the level of tools and actions rather than only at the level of a server connection.
The public record establishes Traefik’s origin, company formation, 2020 Series A, rebrand, leadership transition, core architecture and current commercial direction. It also supports the reported contributor and image-pull milestones and the existence of a material 2026 security-advisory record. It does not establish consolidated revenue, profit, current valuation, paid-customer numbers, product-level adoption or a verified count of production installations.
Those gaps define the limit of the commercial assessment. Traefik Labs is demonstrably a significant open-core gateway company whose project has reached a wide technical audience. The unresolved question is how effectively it converts that reach into durable enterprise revenue and governance while preserving the openness, simplicity and trust that supported its adoption.
Traefik’s original insight remains persuasive: in a dynamic application platform, the traffic layer should follow service state rather than wait for a person to rewrite a configuration file. Its next phase is more demanding because the gateway is being asked to follow not only services, but identities, APIs, model providers, agents and tools. Traefik Labs will have proved the wider strategy when customers can gain that additional control without losing the ability to understand, isolate, recover and replace the layer through which so much of their traffic must pass.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance