
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,255 articles

IETF
Michael Prorock and the Algorithm Identifier That Did Not Choose a Trust Policy
An algorithm label can make two implementations speak precisely about the same kind of key. It cannot tell a verifier why that key arrived, who stands behind it, which claims it may support, or what action the verifier should take. RFC 9964, co-authored by Michael Prorock and…

IETF
The IETF Trust Has a Final Chair. Its Exit Still Needs an End-State Record.
A transition can be described truthfully and still be incomplete as a public record. A named final chair tells readers who is carrying a residual office. An asset-transfer announcement tells them that an important legal step happened. Neither statement, by itself, tells them…

IETF
Dan Harkins and the Bootstrap Key That Could Not Supply Its Own Custody
A device can demonstrate control of a private key without answering the question that mattered before the handshake: who put the corresponding public key in the server’s hands, under what conditions, and with what right? RFC 9966 makes that boundary unusually plain. Its…
IETF
David Benjamin and the Compatibility Code Point That Did Not Become a General Permission
An old cryptographic device can make a modern protocol migration fail at a very specific point. The remedy matters only if it preserves that specificity. RFC 9963 opens a constrained route for a legacy client signature; it does not reopen a general TLS 1.3 permission for the…

IETF
Al Morton and the Capacity Test That Did Not Become a Service Promise
A speed measurement can be valuable evidence about a particular method, path and time. It becomes unreliable when its bounded result is promoted into a promise about every future session, an access plan, an application or a whole network.

IETF
Muhammad Shahzad and the Device Record That Did Not Revoke Access
Deleting a device record can be an important operational signal. It is not, by its own force, a contemporaneous proof that a network enforcement point withdrew access, that the device stopped attempting connection, or that a later session was denied.

IETF
Cédric Fournet and the Receipt That Did Not Make a Log Complete
A signed receipt can answer a sharp question about an entry and a particular tree state. It cannot, merely by looking formal, answer the larger question operators often want to ask: whether every event that mattered reached a complete, trusted and still-current log.

IETF
Christian Amsüss and the DoC Security Context That Did Not Protect the Upstream Resolver
A protected DNS-over-CoAP exchange can be an important fact without becoming a story about the whole resolver path. RFC 9953, collectively authored by Christian Amsüss, says that DoC can provide confidentiality and integrity between parties sharing a DTLS, TLS or OSCORE context.…
IETF
IETF Can Limit the Footer. It Still Needs a Contribution-Status Receipt.
An IETF email footer can look like a verdict: *no derivative works*, a corporate disclaimer, a statement of reservation. The latest draft about derivative-work restrictions would make one boundary much clearer. The special no-derivatives mechanism would be available only for…
IETF
Paul Wouters and the IKEv2 Requirement That Was Not a Negotiation Receipt
“MUST implement” can sound like a deployment report. RFC 8247, co-authored by Paul Wouters, uses it for a narrower purpose: ensuring that IKEv2 implementations have a shared algorithmic baseline. It does not say which transform two peers offered, which one they selected under…

IETF
Bernie Volz and the DHCPv6 Trigger That Did Not Yet Configure a Client
A server log can make the word “Reconfigure” look final: the server issued the message, so a client must now have new settings. RFC 9915, co-authored by Bernie Volz, is more exact. Reconfigure is a carefully authenticated trigger for a later exchange. It is not, by itself, a…
IETF
CATS OAM Can Verify a Steering Policy. It Cannot Choose a Remedy.
The active CATS OAM draft is trying to close a real visibility gap. A service instance can remain reachable at the network layer while the application behind it is slow, exhausted or unavailable. A system that steers traffic only by network reachability may therefore send clients…

IETF
Wassim Haddad and the Prefix That Did Not Yet Authorize Forwarding
A mobile router can have a home-agent registration before it knows which mobile-network prefix it may use. RFC 6276, co-authored by Wassim Haddad, makes the next boundary explicit: only a valid DHCPv6 Prefix Delegation lease allows that prefix into the home agent's binding cache…

IETF
IETF's Survey Can Diagnose a Governance Problem. It Cannot Ratify a Repair.
The IETF Community Survey 2025 gives the organisation a more useful picture of itself than a slogan ever could: a large but imperfect sampling frame, a modest voluntary response, a clear account of what was counted, and a set of concerns that should not be wished away. That is…
IETF
Thomas Graf and the MPLS Label Number That Did Not Identify Its Control Plane
An MPLS label can look like an answer: a compact number at the top of a stack, captured in an export record and ready to be counted. Thomas Graf’s RFC 9160 begins with the smaller, more useful proposition. The number alone does not reliably tell an observer which control-plane…

IETF
SCITT Can Log a Statement. It Cannot Authorize a Release.
RFC 9943 gives software-supply-chain evidence a useful public property: a signed statement can be recorded in a transparency service and accompanied by a verifiable receipt. That can make an issuer’s assertion easier to inspect and harder to rewrite quietly. It does not answer…

IETF
IETF Separates Training Scripts From Slides. Now Test the Handover.
The IETF's latest training-procurement answers make captions, transcripts and narration scripts separate source assets. That is a useful move toward maintainable course material. Its value will become visible when someone other than the original producer has to correct a module.
IETF
Tommy Pauly and the QUIC ACK That Did Not Reach the Application
A QUIC acknowledgement can close one precise transport question while leaving the question an application actually cares about open. RFC 9221, co-authored by Tommy Pauly, makes that seam unusually visible for DATAGRAM frames: the receiver's transport processed a frame, but the…

IETF
DNSOP Can Recommend a Domain-Control Check. It Cannot Govern an Application Identity’s Lifecycle.
The DNSOP working group is in Last Call on a useful document about applications that use global-DNS names as identifiers. Its central discipline is easy to miss. A service may need proof that a registrant or an authorized party controls a domain when an integration is…
IETF
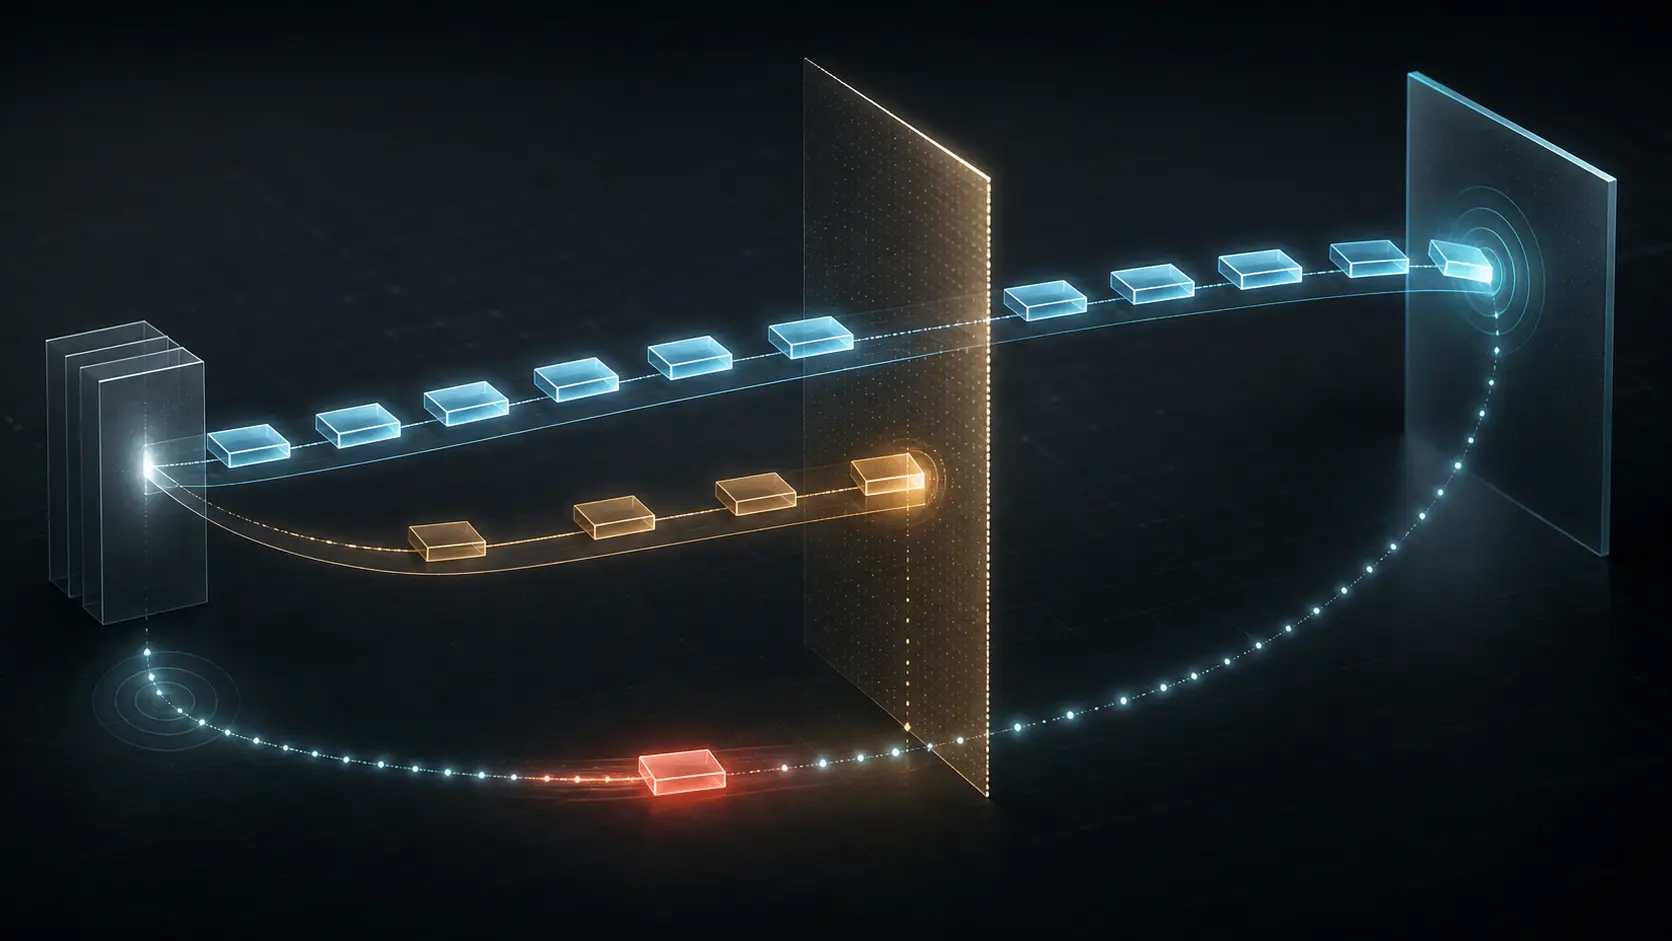
The Newer Packet Arrived First: How TCP RACK Used Time to Find Loss
RACK changes the evidence TCP can use when looking for loss: not only sequence-space gaps, but also the transmission times of data known to have arrived.
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance