
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,070 articles
IETF
The Prefix Arrived Before the Query: How RFC 9872 Changes NAT64 Discovery
An IPv6-only host that must reach IPv4 services needs to know which IPv6 prefix its network uses for address synthesis. RFC 9872 turns that knowledge into an access-network signal: learn PREF64 from Router Advertisements first, and use DNS discovery only when that signal is…

IETF
ZONEMD Lets a Secondary Verify the Zone After the Transfer Ends
A completed zone transfer proves that a delivery procedure finished. It does not, by itself, prove that the receiver assembled the exact zone the publisher intended. ZONEMD adds a digest over the zone as a whole, creating a verification boundary after transport and before a…

IETF
The Bitmap Says a UDP Option Appeared—not What It Did: RFC 9870
RFC 9870 gives IPFIX exporters a compact way to report which UDP Option kinds appeared in a Flow. Its bitmaps are useful precisely because their claim is narrow: they preserve observed presence, not a packet history, a receiver’s processing decision or an application outcome.
IETF
DNS TCP Fallback Is a Capacity Path, Not an Exception
A resolver can pass every small UDP health check and still fail the first answer that matters. When a response is truncated, correctness moves onto TCP; listener capacity, connection state and middlebox policy then become part of DNS availability.
IETF
Maciek Konstantynowicz and the Benchmark Result That Was Not a Service Guarantee
A network benchmark earns its value by saying exactly what it measured. RFC 9971 makes that discipline explicit: its MLRsearch result is a bounded result from stated trials and goals, not a transferable promise about every customer path, application or production hour.

IETF
IETF’s CSR Attestation Draft Leaves Verifier Selection to Format Designers
A last call on carrying device evidence in certificate requests puts a practical compatibility question in view: two services may understand the same format without being interchangeable destinations.
IETF
A Negative Trust Anchor Lets the Resolver Suspend DNSSEC Without Changing the Zone
When a signed domain breaks, a validating recursive resolver can either preserve the failure or create a narrow local exception. A negative trust anchor restores reachability without repairing the zone, but it transfers temporary authority over DNS authentication to the resolver…

IETF
IETF’s Broadband List Faces a Test of Reviewer Supply
A new discussion venue aims to give scattered access-network proposals a home. Its more demanding task is to assemble the people who can carry them through technical review.

IETF
Mukul Srivastava and the BMP Gauge That Counted a RIB but Did Not See a Route
A number can be both useful and radically incomplete. RFC 9972 gives BMP operators a more precise way to report how many routes occupy a named RIB view at a particular moment. It does not turn that count into a route record, a policy explanation or a delivery observation. Mukul…

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…
IETF
Rich Salz and the TLS 1.3 Requirement That Was Not a Deployment Receipt
A standard can make a demanding rule without manufacturing the evidence that the rule has become true in every running system. That distinction is not a loophole; it is how an operator can tell a sound protocol decision from an unsupported deployment claim. Rich Salz’s…
IETF
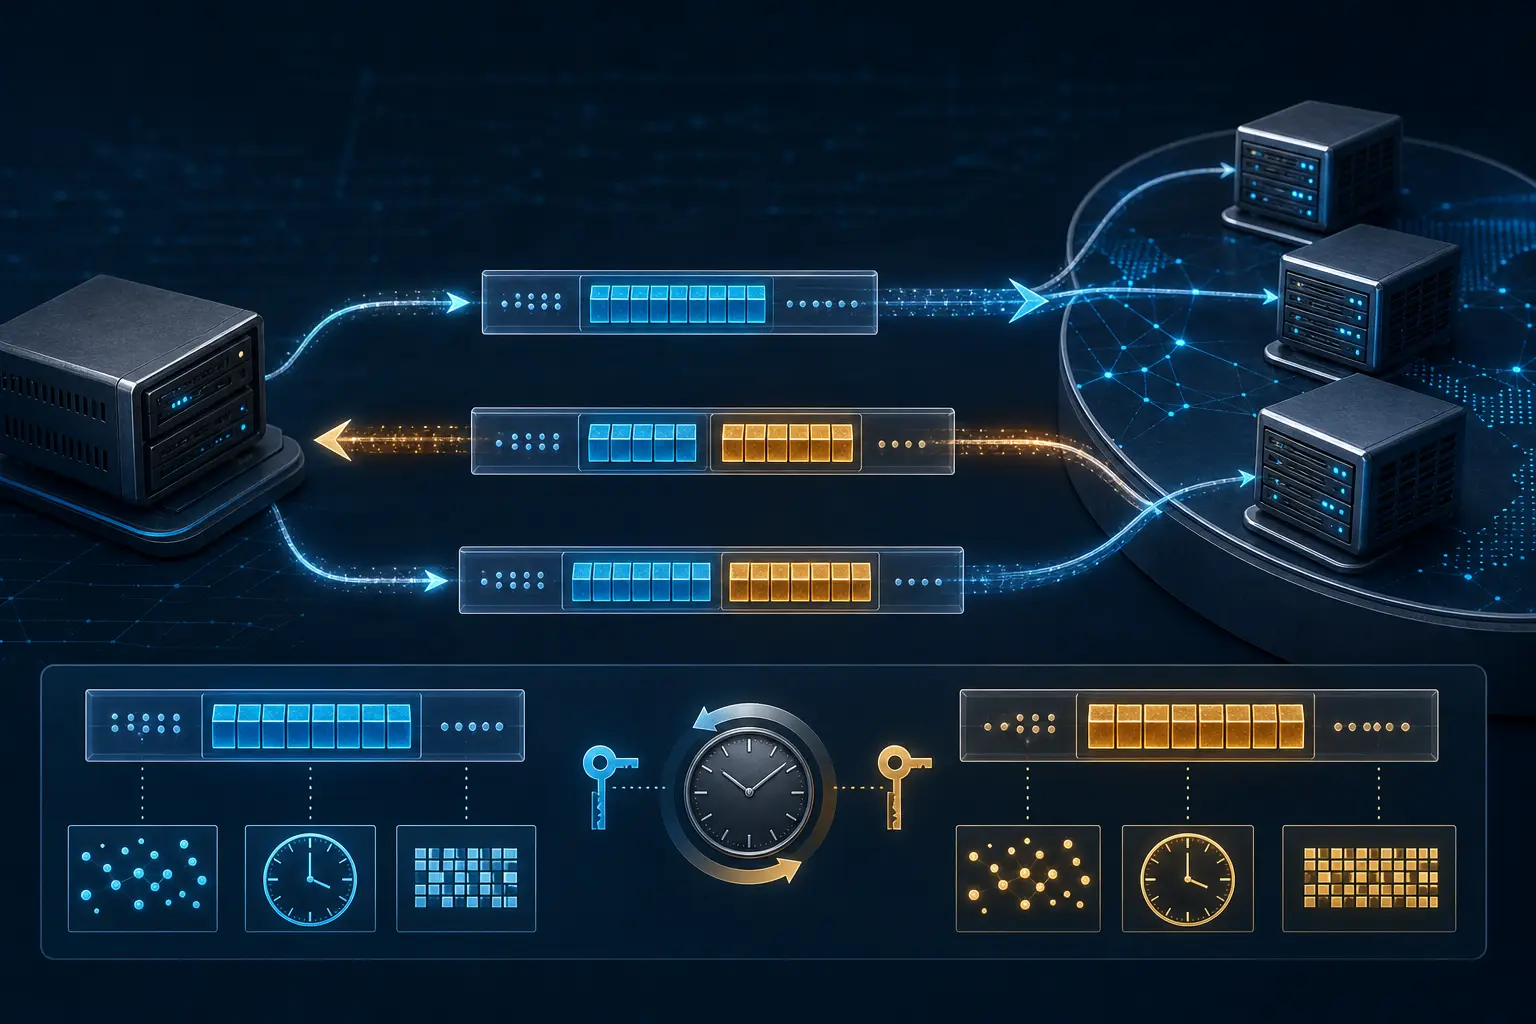
A DNS Cookie Supplies Return-Path Evidence, Not Client Identity
A valid DNS Server Cookie can show that a requester at a source address is returning a value issued in an earlier exchange. That is useful evidence against off-path forgery. It is not a login, a durable device identifier or permission to attach a person’s name to the query.
IETF
Nancy Cam-Winget and the SCIM Event That Was Not a Reconciliation Receipt
An identity system can tell another domain that something changed and still leave the receiving domain with consequential work to do. It must decide whether the resource is the one it knows, whether the schemas align, whether a callback is needed, what local rule applies, and…
IETF
Chris Wendt and the Signed Response That Did Not Authenticate the Media
A telephone caller needs more than a signal that looks official. The practical question is whether the party reached is the intended party, what evidence supports that conclusion, and what a device should do when the evidence does not arrive. Chris Wendt’s co-authored RFC 9970…

IETF
IETF’s Vienna Space Squeeze Tests the Forecast Behind Venue Selection
A popular meeting can still run short of places to work between sessions. The IETF’s Vienna review exposes the timing problem behind a venue decision: a forecast can change after the room for adjustment has narrowed.

IETF
Michael Prorock and the Algorithm Identifier That Did Not Choose a Trust Policy
An algorithm label can make two implementations speak precisely about the same kind of key. It cannot tell a verifier why that key arrived, who stands behind it, which claims it may support, or what action the verifier should take. RFC 9964, co-authored by Michael Prorock and…

IETF
The IETF Trust Has a Final Chair. Its Exit Still Needs an End-State Record.
A transition can be described truthfully and still be incomplete as a public record. A named final chair tells readers who is carrying a residual office. An asset-transfer announcement tells them that an important legal step happened. Neither statement, by itself, tells them…

IETF
Dan Harkins and the Bootstrap Key That Could Not Supply Its Own Custody
A device can demonstrate control of a private key without answering the question that mattered before the handshake: who put the corresponding public key in the server’s hands, under what conditions, and with what right? RFC 9966 makes that boundary unusually plain. Its…
IETF
David Benjamin and the Compatibility Code Point That Did Not Become a General Permission
An old cryptographic device can make a modern protocol migration fail at a very specific point. The remedy matters only if it preserves that specificity. RFC 9963 opens a constrained route for a legacy client signature; it does not reopen a general TLS 1.3 permission for the…

IETF
Al Morton and the Capacity Test That Did Not Become a Service Promise
A speed measurement can be valuable evidence about a particular method, path and time. It becomes unreliable when its bounded result is promoted into a promise about every future session, an access plan, an application or a whole network.
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance