
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

IETF
IPv6 Neighbor Discovery Puts Three Actions Behind One Boolean
A boolean is the smallest possible management choice. In the IPv6 Neighbor Discovery YANG model now in IETF Last Call, one such switch can authorize a much larger sequence: record a duplicate-address event, discard the triggering message and block the host that sent it. The draft…

History
The File Ended, Then Continued: RFC 1952 and Gzip's Member Boundary
A `.gz` filename suggests one entity. RFC 1952 describes something more interesting: a procession of self-closing members. Finish one, place another immediately after it, and a decompressor can continue as though the file had acquired a new chapter. The old compressed bytes need…

Global Cloud Services Trends
Cloudflare Keeps a Post-Quantum API That No Longer Changes the Setting
Automatic Key Exchange separates algorithm selection from algorithm restrictions. A surviving legacy endpoint no longer controls either in the way its old name suggests.

IETF
A Cleared Incident Does Not Prove Which Command Cleared It
An incident client sends one `incident-resolve` request containing several incident numbers. Later, separate notifications arrive. Two records now say `cleared`; another remains `updated`. The network view is useful, but the decisive question has vanished between the command and…

History
The Key Centre Disappeared into the Tree. Its Authority Did Not: RFC 1949
Scaling usually sounds like subtraction: remove the bottleneck, spread the work, let the network carry the rest. RFC 1949 did spread multicast key distribution, but it could not subtract trust. By letting authenticated tree nodes pass group secrets and authorise later joins, the…

IETF
A Capability Menu Is Not a Subscription Decision
An orchestrator sees a tidy answer before it opens a notification stream: this device supports HTTPS, XML or JSON, and two TLS versions. The discovery is valuable precisely because it is compact. It becomes dangerous only when a control system silently turns “listed” into…

History
The Password Was Correct Once. Acceptance Changed What Correct Meant: RFC 1938
Passwords usually sound like facts: either the claimant knows the right string or does not. RFC 1938 made that description incomplete. In its one-time-password system, a correct answer was consumed by success. The server replaced the value against which the next answer would be…

Story
RIPE Database 1.124.1 Fixed Certificate Selection. Its “No Evidence” Finding Needs a Search Boundary
RIPE NCC was right to ship a reported authentication vulnerability without waiting for a routine test interval. The next duty is different: show members what time, traffic and registry history were actually examined before “no evidence of exploitation” became the public…

Asia-Pacific National Telecom Trends
TM's CYDEC shifts the security pitch from alerts to context
Telekom Malaysia's new Cyber Fusion announcement promises a joined-up incident picture. The buying question is how far that picture reaches, and who can act on it.

IETF
ELA’s Voucher Arrives After the Device Identifies Itself
In a zero-touch join, the smallest interval can carry the largest governance consequence. A new device using the proposed ELA protocol authenticates a domain gateway, sends its credential identifier and waits while that gateway asks an enrollment server for authorization. Only in…
History
The Server Pool Was Redundant. The Address Authority Was Singular: RFC 1931
A workstation with no configured address asks a question that looks deceptively small: which IP address may I use? RFC 1931 answered with several servers, but not several truths. Dynamic RARP separated the machines that could hear and answer a request from the authority allowed…

IETF
A Cryptographic Malfeasance Report Cannot Revoke Trust
Three time servers sign answers that cannot all be true in the order they were received. Roughtime lets a client preserve that contradiction as portable cryptographic evidence. Yet the proof does not name the guilty server, appoint the reviewer, alter a trusted-server list or…
IETF
One EDHOC Key ID Can Point to Several PSKs
A constrained device sends a compact key identifier inside an EDHOC exchange. The responder looks it up, tries a pre-shared key and authenticates the message. Revision 09 of the IETF LAKE working group’s EDHOC-PSK draft changes what may sit behind that lookup: one identifier can…

History
The Gold Paper Clip Looked Decorative. It Was a Workflow Command: RFC 1927
A paper clip is legible before anyone explains it. That was the charm of RFC 1927—and the trap hidden inside its joke. The memo asked one office-supply icon to express whether documents belonged together, how they should look, which workflow should run, where an annotation…

IETF
A Private Candidate Does Not Explain Why One Intent Won
Two engineers are authorized to change the same router. Each works in a private configuration branch, so neither can accidentally commit the other’s unfinished commands. Then both change the same node. The server can identify the collision and offer disciplined ways to resolve…

IETF
A Packet-Discard Counter Needs an Intent Epoch Before Automation Acts
At 02:14, an egress no-buffer counter starts climbing. The automation can move traffic in seconds. What it cannot see in the number is that a new service profile went live at 02:12, the line card restarted at 02:13, and the approved loss budget belongs to the configuration that…

IETF
One Shared Nameserver Is a Continuity Test, Not Proof of Delegation Control
A resolver looks again at a delegation it has cached. The parent now lists a mostly different set of nameservers, but one familiar name survives. That intersection can be enough to treat the delegation as continuous, provided any relevant signer overlap also holds. It is a useful…
Asia-Pacific National Telecom
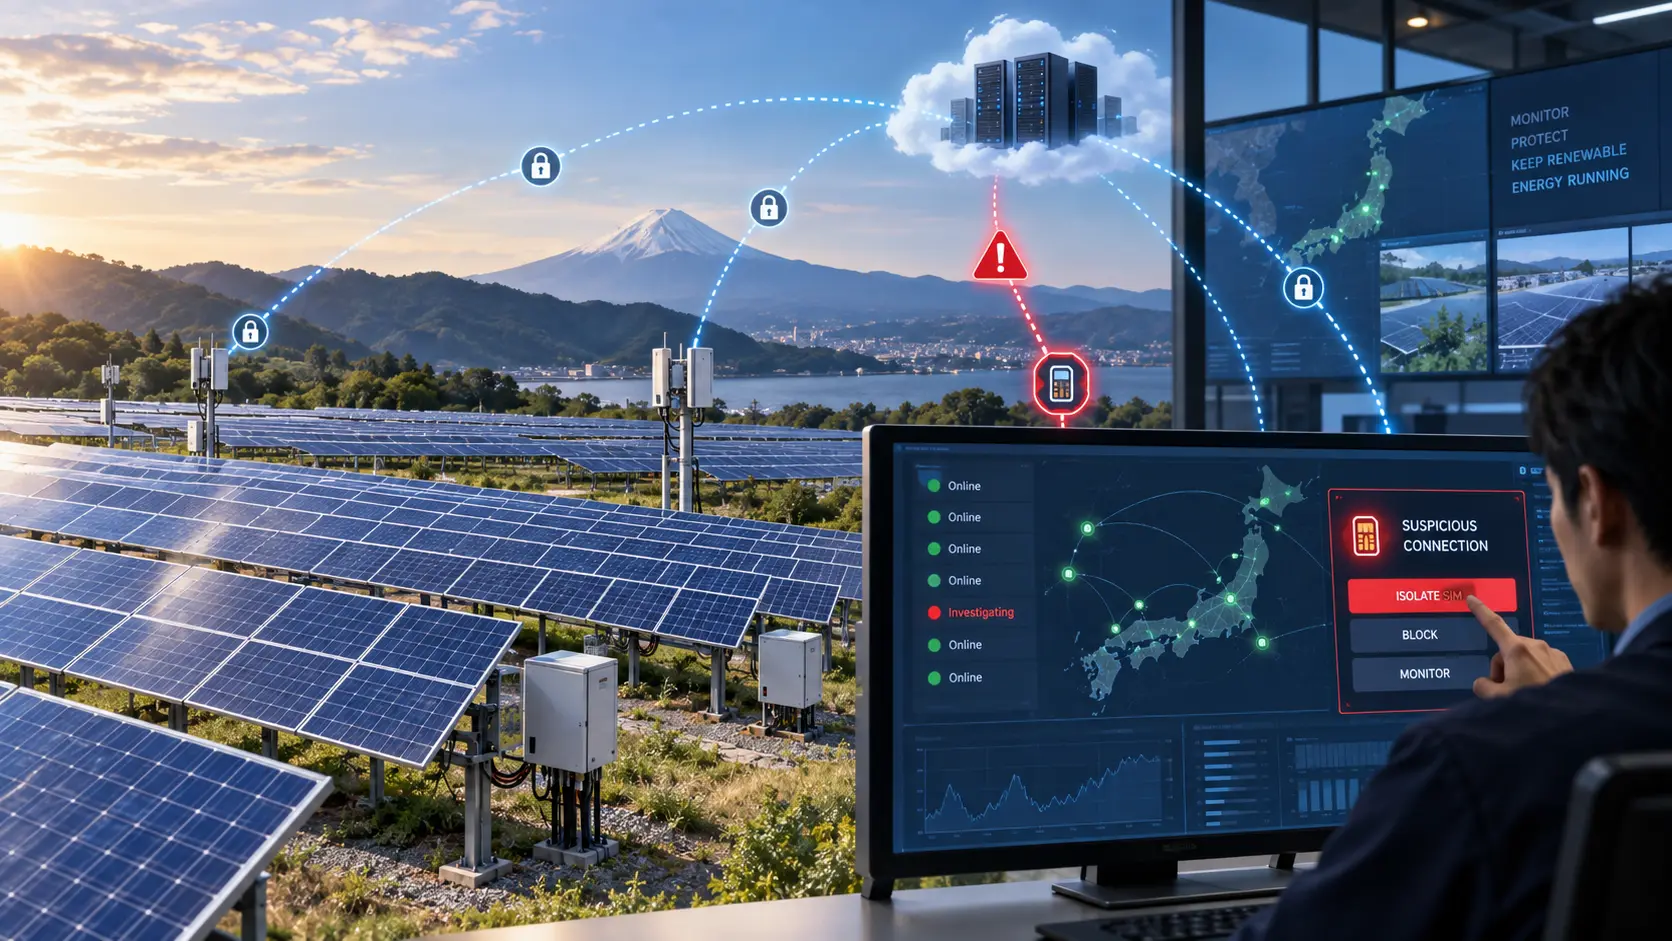
TESS, Docomo test security for solar monitoring
The pilot lets TESS block suspicious SIM traffic remotely while testing how solar monitoring continues when a connection is cut.

IETF
DNS GREASE Needs an Experiment Charter Before It Becomes a Default
A resolver deliberately puts a value with no useful meaning into a DNS query. A correct peer ignores it. A brittle peer may reject the query, stay silent or provoke a retry. The experiment protects tomorrow’s protocol by creating a small inconvenience today. That bargain is…

Global Cloud Services Trends
F5 ties scanning to the decision to block
A vulnerability report has limited value until someone can act on it. F5 wants a larger role in that decision—and in the interval before the code is fixed.