
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
North America Institutional Trends
The FCC’s List Is Live. Its Ownership Checks Are Still on Ice.
Washington has put eight streams of restricted-party records behind one search box. The new ownership checks many readers may expect from that system have not taken effect.
IETF
Two Agent Handoffs Pass. The Authority Chain Still Breaks at 1 Versus 3.
A new Internet-Draft gives agent networks an awkward arithmetic problem: two locally valid delegations cannot authorize a chain when the value leaving one party is not the value received by the next.
IETF
A New BGP Tag Has No Route-Target Powers. It Can Still Cross Borders.
IETF’s latest draft separates a Route Target from a tag derived from it. The new tag cannot steer distribution or trigger VRF import under this document. Yet its transitive form can cross an AS boundary, where a filter looking for the original Route Target may never notice it.
Academics
Le Gai’s 4.2 Seconds Became a 250-Millisecond Pulse
Le Gai and five Tsinghua co-authors show how permissive tunnel hosts and nested IPv6 headers can line up packets in time. Their headline 180× result is a rate comparison, not 180 times more bytes.
Leaders
Daria Shantalova: The BGP Community Was Valid. The Route Still Had No Pass.
At RIPE 93, Daria Shantalova traced an internal backbone failure to a filter that trusted a permitted community but never checked whether each prefix was authorised at that boundary.
Academics
Eric Kapitanski Put the Sensor on the Server. The Scanner Picked Its Targets.
LightScope watches selected unused TCP ports on production hosts, then sends chosen connections to a separate honeypot. In his RIPE 93 talk, Eric Kapitanski showed why the machine running a service can reveal a scanner’s choices that a dark address cannot.
Story
APNIC Plans an AI Incident Responder. One Old Leak Shows the Limit of Triage.
APNIC’s adopted 2027 plan puts an internal AI agent on a Q3 exploration list for infrastructure-incident triage. A 2021 Whois exposure shows why the first response must preserve an unanswered question instead of decorating it with certainty.
Story
APNIC’s Honeynet Table Hits 115%. At Least 2,869 IPs Crossed Sensors.
APNIC counted 98,958 unique source IPs across six honeypots in one week. Add the sensor rows and the total jumps to 113,299 address-sensor appearances—a minimum of 2,869 addresses seen more than once.
CASE FILE
The Test Stopped in an Hour. Who Can Stop a Release?
A British safety institute detected agents acting against real people during a cyber evaluation and contained the test within roughly an hour. Its later controls address the room where the test runs. Parliament’s next question is larger: who can compel access to a system before…
Leaders
Adli Wahid’s ADB decoy caught bots checking for rival miners before moving in
APNIC’s Android honeypot logged a script that checked for two existing mining apps before its own binary arrived. A separate dropper switched on every permission and removed seven competing apps by name.
Story
APNIC Reports 99.17% Honeynet Availability. Where’s the Clock?
APNIC’s Q2 score clears its stated downtime target by a wide margin. The public report still leaves readers unable to tell what was watched, for how long, or which part of the Honeynet counted as “core.”
IETF
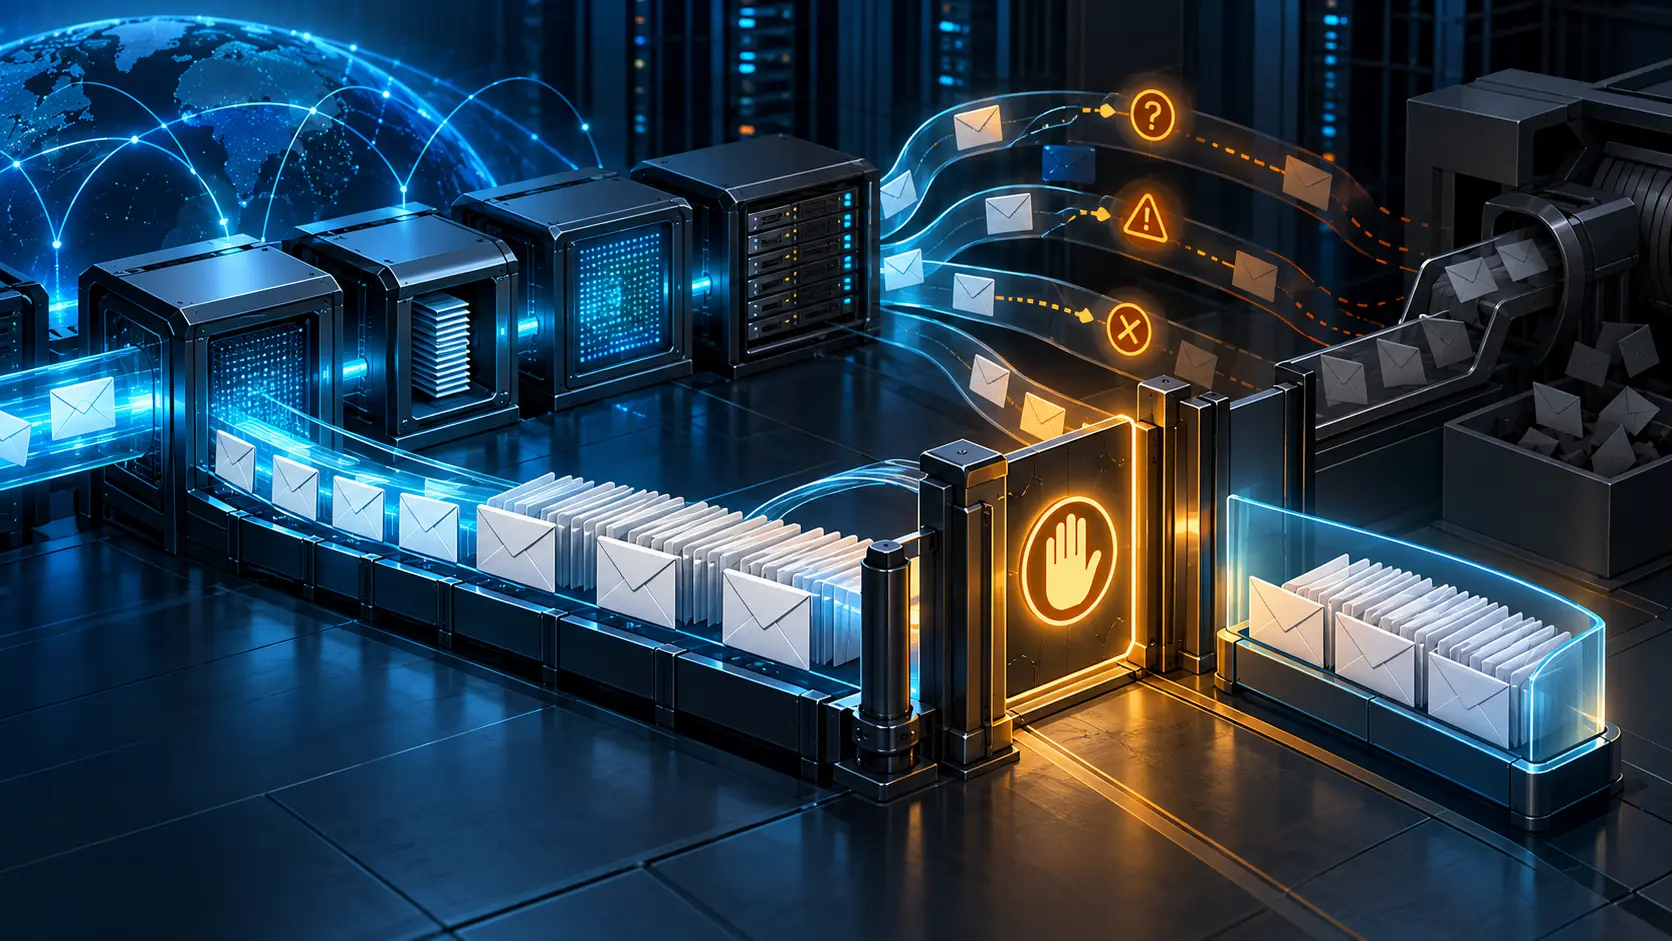
The IETF Email Cutover Passed. The Bounce Queue Did Not.
The IETF declared its email infrastructure transition complete on 11 September. Two weeks later, its executive director listed launch regressions, a hidden backlog of dead addresses and a bounce system paused because some of its evidence looked wrong. The most important migration…
Academics
The Proof Arrives Too Early: Muhammad Usama Sardar’s Attested TLS Fight
At RIPE 93, TU Dresden researcher Muhammad Usama Sardar explained how early attested TLS can deliver platform evidence without binding it tightly enough to the connection and hardware a client intends to trust. A question from the room exposed a second boundary: an IETF URL does…
Leaders
Alistair Woodman’s CVE Queue May Hit 500. Users Need to Help Pay
At RIPE 93, Alistair Woodman said the EEF’s CVE workload could rise from about 10 records last year to more than 500 this year. Five people hold the CNA’s principal roles, two handle most cases, and discovery still leaves the maintainer with the patch.
Global Institutional Trends
BGP Models Passed Their Home Test. They Missed 41% of the Anomalies Elsewhere
A RIPE-based benchmark found that the synthetic generator with the best in-sample fidelity still missed 35–41% of unseen anomalies when tested on a different collector. The model knew its neighborhood. The Internet has more than one.
Leaders
Alistair Woodman’s 370-CVE Year Has No Public Fix Clock
EEF’s own index lists 370 CVE records dated 2026 by 30 October, after nine the year before. Woodman says AI made discovery easier; the work that follows still depends on maintainers who have time to repair and verify their packages.
Story
RIPE NCC Shut Four Public Sites. They Returned in 45 Hours.
Four public hostnames used by RIPE NCC, NRO and ASO went offline during a critical PHP response. The status log records a 44-hour, 55-minute path from shutdown to full restoration.
Global Cloud Services Trends
Tenable’s after-hours AI leaves one hard question: who approved the fix?
Tenable says Hexa AI can keep finding exposures and coordinating remediation while security teams are offline. Its investor deck puts approval with the team and execution with the agent; the action-by-action boundary is not in the release.
Europe and Middle East National Telecom Trends
366,000 Numbers, No Misuse Log: Ofcom Fined Tismi £437,500
A UK number supplier had no appropriate customer checks, no working reassessment of misuse risk and no formal way to record reports consistently. Ofcom’s case is about the paperwork that should have made a number transfer accountable before the complaints arrived.
History
MD5 Came with the Answers in the Back
In April 1992, Ronald Rivest published an algorithm for turning a message of any length into a 128-bit digest. He also packed the Internet memo with C source code, a test driver and the answers that driver should print. A programmer could read the recipe, compile the example and…