
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

IETF
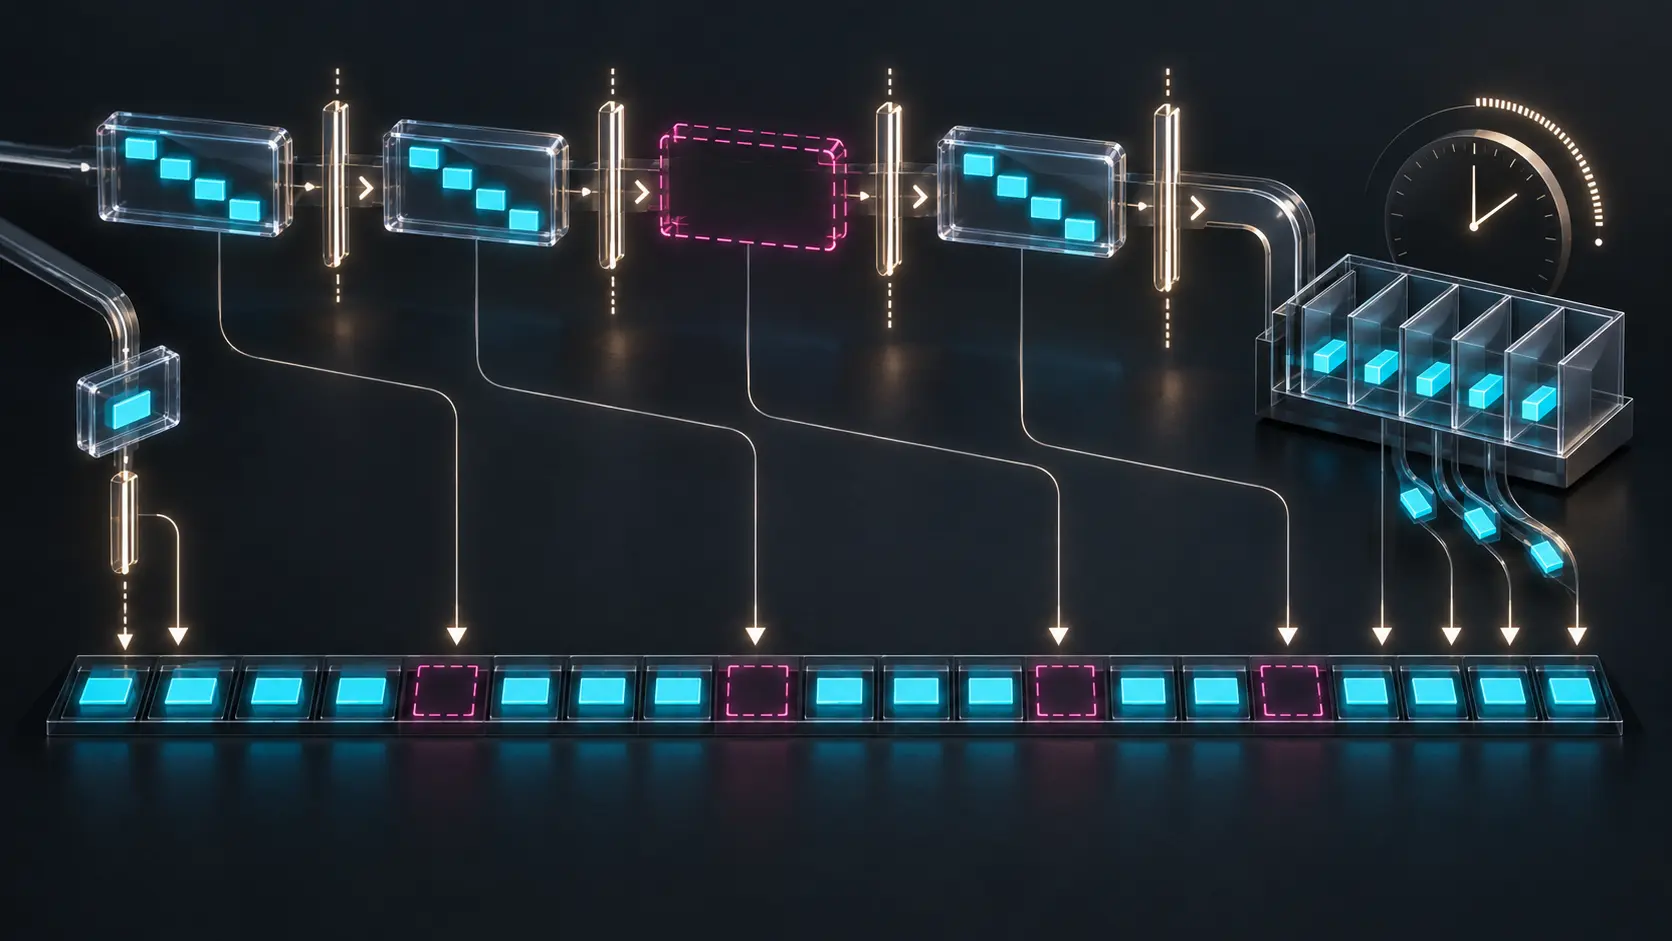
The Server Said Nothing Had Changed. Another Authority Was Already Serving Something Else.
The resolver received a tiny “nothing new” signal and kept the large signed RRset already in its cache. That saved a retrieval. It did not establish that every authoritative server held the same generation—or that the cached entity still represented the operator's current intent.
IETF
One Packet Vanished. The Damage Arrived in Instalments.
An interleaver can turn one lost datagram into several separated 20-millisecond holes instead of one continuous wound in speech. That sounds like recovery. It is not. RFC 3558 buys a different loss shape by making the receiver hold more state and wait longer before it knows what…

IETF
The Update Was Accepted. The Parent Had Not Published It Yet.
The child received `NOERROR` from the delegation update receiver and closed its change ticket. Minutes later, an authoritative parent server still returned the previous delegation. Nothing in that constructed sequence contradicts the draft: acceptance means the change should…
IETF
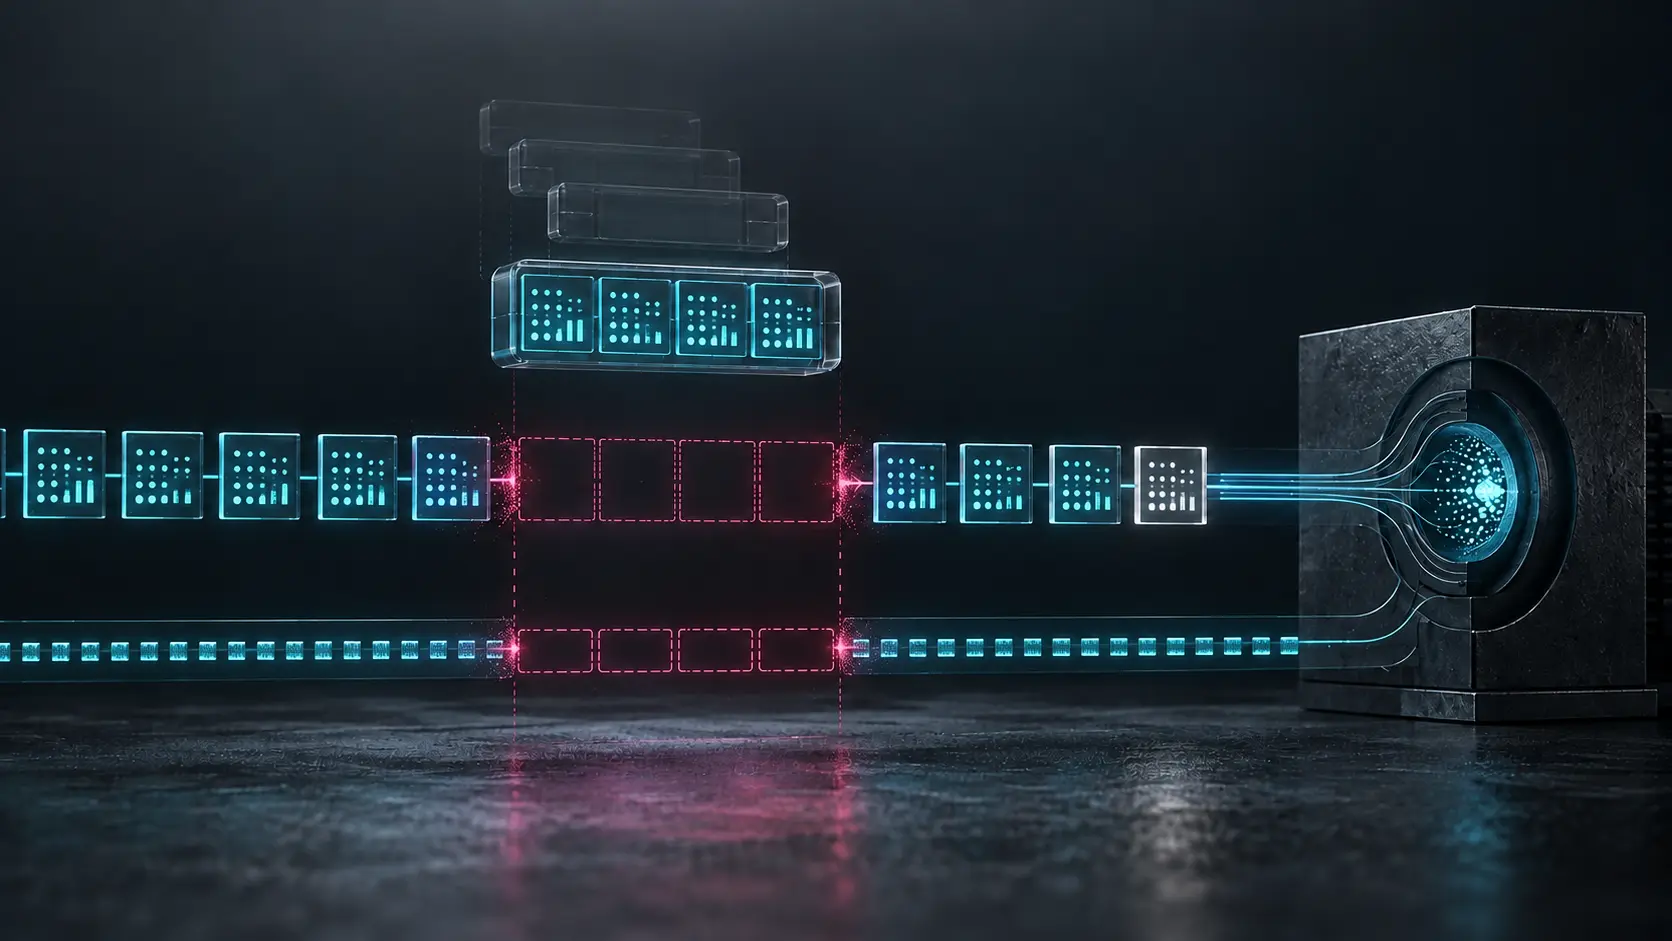
The Packet Saved Three Headers. It Lost Eighty Milliseconds at Once.
Four 20-millisecond feature pairs shared one RTP packet. The packetizer paid for one header instead of four. When that datagram disappeared, the speech engine did not lose a header-efficiency statistic; it lost one continuous 80-millisecond stretch of evidence. RFC 3557 makes…

IETF
The Peer Was Valid. One Claimed Address Could Still Redirect the Traffic.
The certificate checked out, the IKE exchange completed, and the SCTP association had several paths to choose from. One address at the end of the selector list belonged to somebody else. RFC 3554 makes the uncomfortable point explicit: authenticating the peer is not the same as…
IETF
The Timer Reached Zero. One Signer Was Still Serving Yesterday.
In a constructed operator transition, the controller completed its last configured wait and marked the departing DNS provider safe to remove. The parent showed the new nameserver set. The shared DNSKEY view looked correct. One remaining secondary, however, was still serving an…
IETF
The Agents Agreed the Binding Was Gone. The Mobile Node Was Still on the Old Path.
The revocation crossed the tunnel, its authenticator checked out, and an acknowledgment came back. Between the home agent and foreign agent, the record looked closed. Below that exchange, the mobile node could still be waiting for a sequence-zero advertisement, trying the route…
IETF
The Token Matched. The Privilege Scope Was Still Blank.
In a constructed operating case, a DNS administrator placed an opaque TXT value at the requested challenge name. The provider found the exact token and granted control over several service features. The record proved that a challenge had reached DNS. Nothing in it showed that the…

IETF
Failover Copied the Login. One Server Said Accept, the Other Reject.
The watchdog expired, so the client sent every pending request to an alternate AAA server. The alternate answered first. The original request had not vanished; it was still alive on the old path. One logical login had become two opportunities to decide, and a faster recovery…
IETF
The Origin Changed the File. DNS Kept the Old World.
In a constructed operating case, an origin replaced its `origin-svcb` JSON and the fetch returned valid HTTPS. The dashboard marked the ECH rotation complete. The zone serial had not changed, one zone factory had rejected an endpoint, and recursive caches still carried the…

IETF
The Ceiling Was Large. The Memory Was Never Promised.
A capacity model saw a peer advertise a very large TLS receive limit and booked the same number of bytes as dependable headroom. In the constructed test, many connections exercised that permission together. The protocol ceiling held; the memory assumption did not. A maximum…

IETF
The Allocator Moved the Capacity. The Controller Still Held Yesterday’s Map.
The switching element reported a smaller resource envelope. The partition never restarted, its control session stayed up and its existing state remained present. Yet the controller could continue planning against the old limit until a later request failed. A successful…
IETF
The Directory Agent Said Accepted. The Mesh Had Not Yet Heard.
The service agent received a clean acknowledgment and closed its registration transaction. At that instant, another directory agent in the same scope could still answer without the new record. The receipt was genuine. The conclusion drawn from it was not.

IETF
Every Receiver Held the Key. None of Them Became the Sender.
A constructed multicast service admitted one receiver, delivered the group secret over an authenticated channel and began sending encrypted media. The receiver could decrypt exactly as intended. In a naïve symmetric design, it could also construct a tag that looked valid to every…

History
The Protocol Could Propose Any Sequence. It Could Not Pre-Approve the Charge: RFC 3354
An online trade can be arranged as a sequence: offer, approval, shipment, payment and receipt. RFC 3354 wanted IOTP to make that order flexible. Its more durable lesson is that arranging the steps did not grant authority to perform them.
IETF
The Group Was Larger. The Exponent Could Still Be the Weakest Link.
The negotiation selected an 8192-bit MODP group. The audit celebrated the largest number in the exchange. It had no record of how the private exponent was generated, whether the peer’s public value was tested, or which endpoint had actually been authenticated.

History
The Tag Stayed 96 Bits. The Hash Behind It Changed: RFCs 2403 and 2404
Two IPsec transforms kept the transmitted authenticator at 96 bits while changing the hash underneath it. That stable field made packet formats comparable; it did not make the algorithms, key sizes or later implementation advice identical.

IETF
TLS Delivered the Cookie. It Had Not Proven Who Set It.
A `Secure` cookie can arrive over an authenticated encrypted channel and still carry state whose provenance the application has not established. Transport, cookie scope, server-side session validity, authorization and business outcome are different receipts.

IETF
The ACK Proved the Retransmission Was Needless. It Did Not Undo the Recovery.
The first acceptable acknowledgment returned with an older timestamp. That was enough to show that the original transmission—not the retransmission—had earned the acknowledgment. It was not enough to widen the congestion window that the sender had already narrowed.

IETF
The Dashboard Said Failure. The Server Had Declined a Purpose.
A spike in a proposed HTTP status can be operationally useful only if the dashboard preserves what the status actually says. `419 Purpose Declined` would classify one request by its declared purpose; it would not prove an outage, a durable ban, an origin-only decision or the fate…