
Topic
RPKI and Route Security
Within the Topic facet, RPKI and Route Security topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Number Resource Society
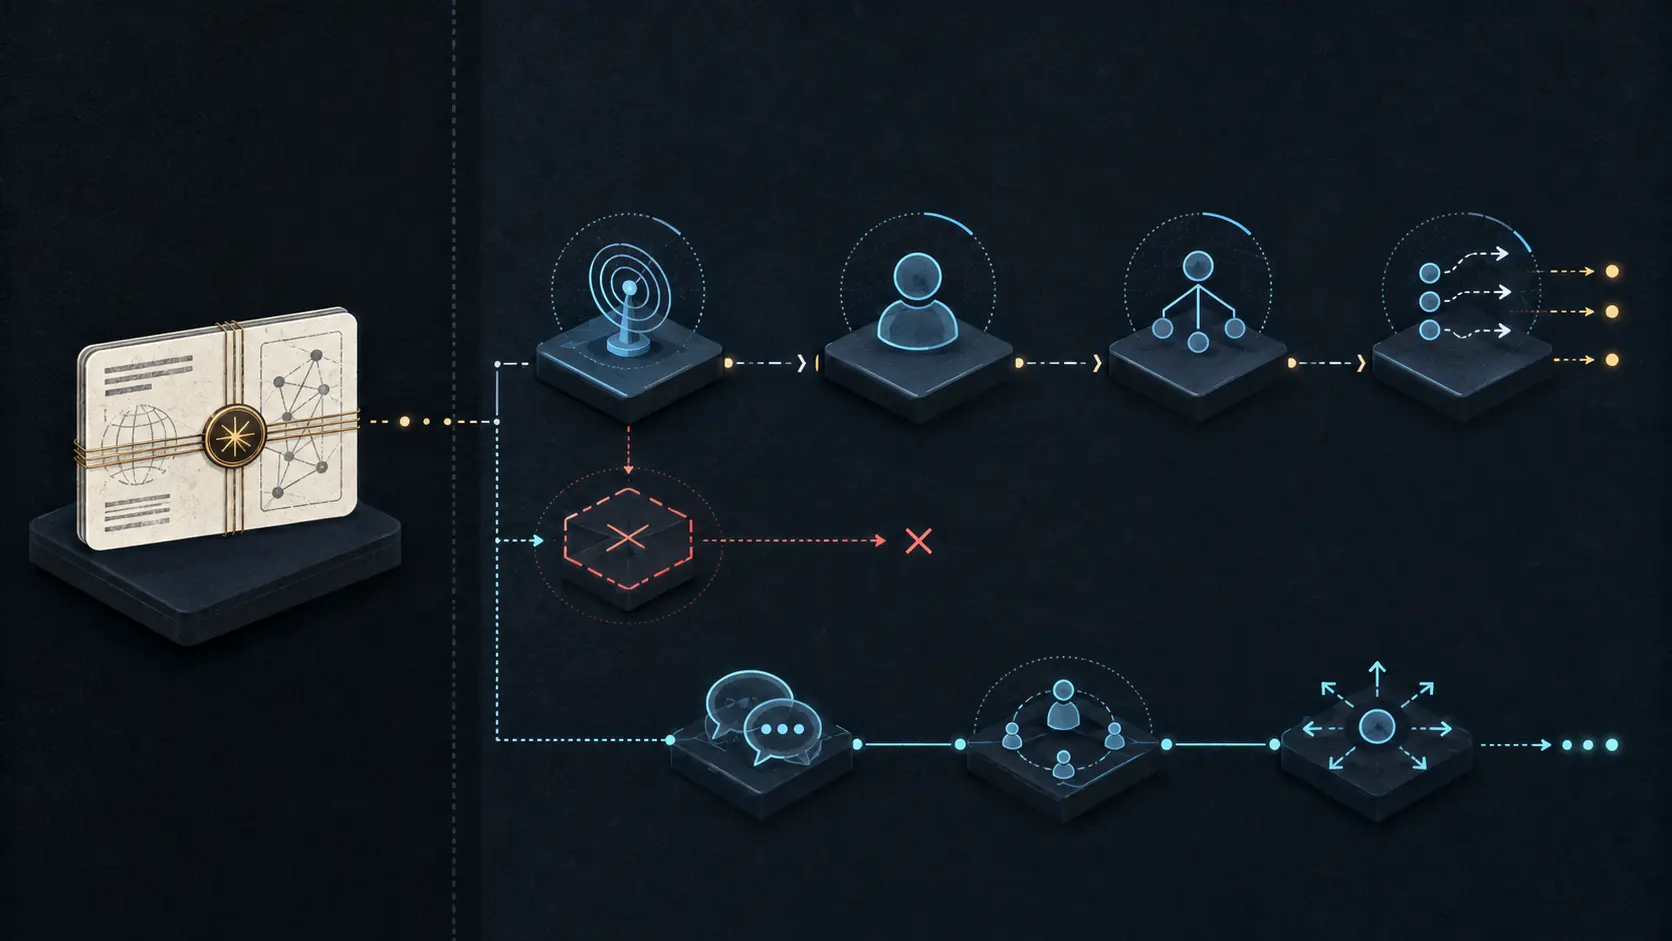
A Ghostbusters Record Is Not an Incident Command Roster
An RPKI relying party can validate every byte of a Ghostbusters Record and still not know whether anyone is watching the listed channel when action is needed. The signed entity solves discovery of minimal CA-maintainer contact data; operational accountability begins where that…

Number Resource Society
A Trust Anchor Rollover Needs an Acceptance Ledger
An RPKI trust-anchor operator can publish a successor key without making every relying party ready to use it. The transition is a sequence of verified observations, not a launch date: a defensible record must show what was announced, what remained stable, which validators crossed…

Number Resource Society
An RPKI Publication Point Needs a Commit-to-Visibility Ledger
An RPKI publication server can accept an authenticated update atomically while relying parties still hold an earlier repository view. That is not necessarily a contradiction or a failure. It is a boundary between different authorities, protocols and observation times. A useful…

Number Resource Society
An ASN Transfer Needs a Routing-Identity Handover Ledger
An ASN Transfer Needs a Routing-Identity Handover Ledger intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…

North America Regional ISP Trends
Plus Analytics: what an invisible route can and cannot prove about a VPN
Plus Analytics presents privacy as a service outcome. Its public number-resource record presents a different entity: administrative control. The gap between them is where a buyer’s diligence should begin, not where a verdict about the service should end.
Global Regional ISP Trends
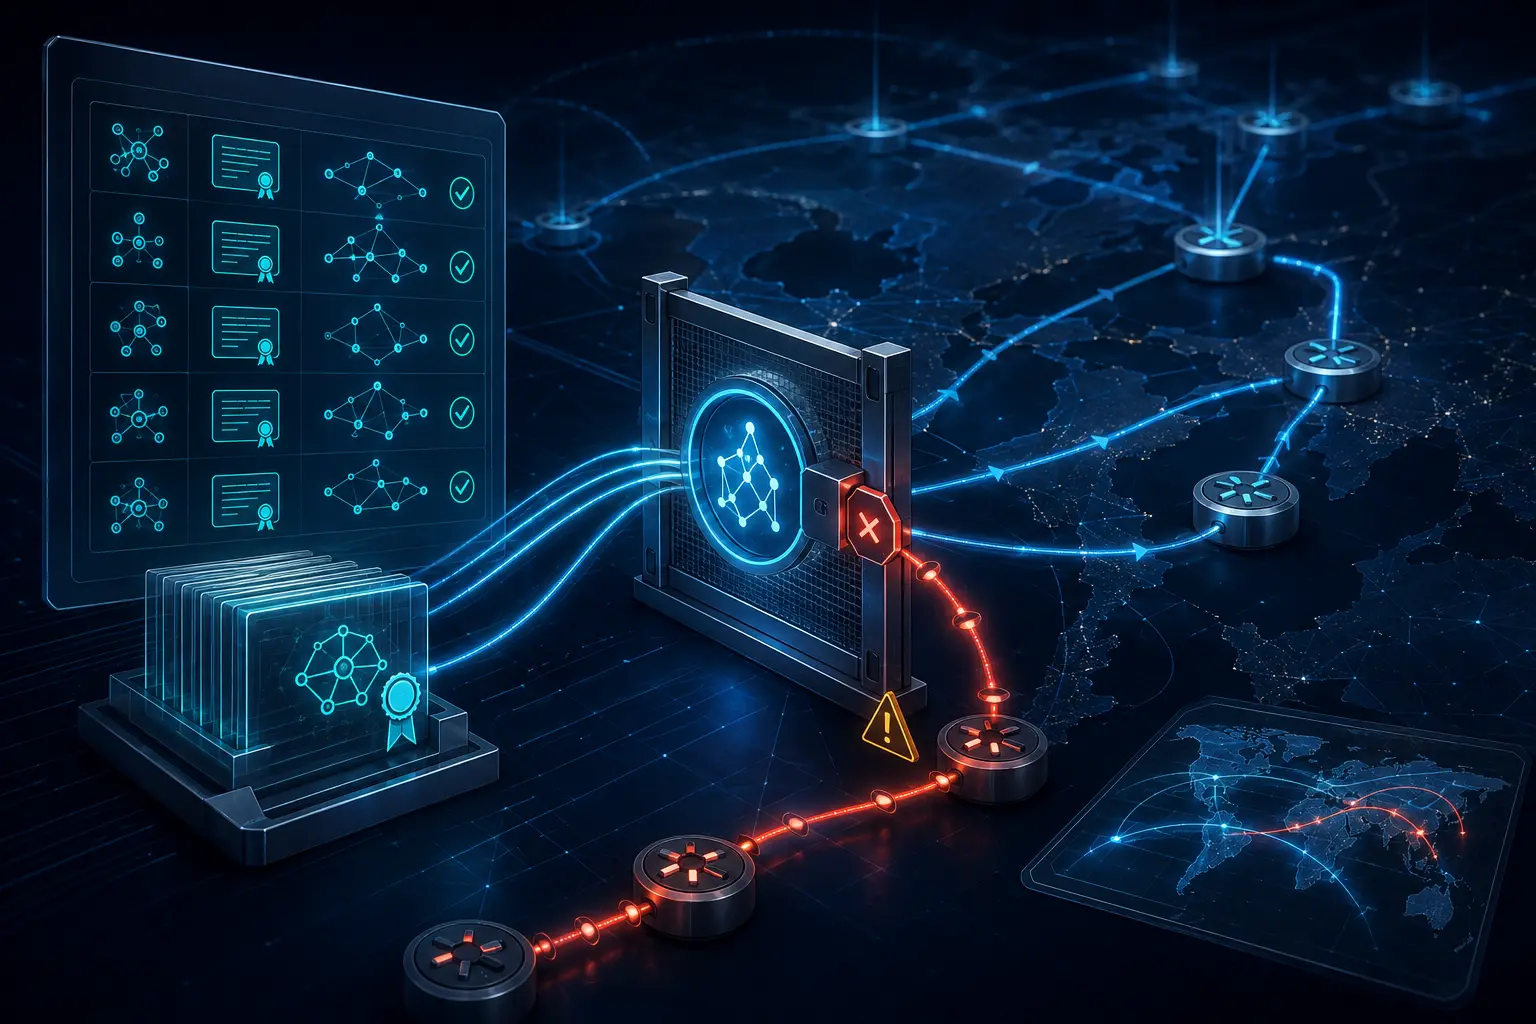
An ASPA Record Is Not a Route-Leak Rejection Policy
An ASPA can publish which networks are authorized upstream providers. It cannot show that a production router has consumed that evidence, classified a path correctly, or rejected it without collateral damage.
IETF
Default Reject Turns Missing EBGP Policy from Silent Authority into an Explicit Failure
An external BGP session can be established while its authority to receive or advertise routes remains undefined. RFC 8212 changes the default at that boundary: without import policy, accept no routes; without export policy, announce none. The leadership question is not whether a…
NPNOG
After the RPKI Panel: Did npNOG’s 2020 Routing-Security Moment Survive the Screen?
The official page does not, by itself, prove that entities created ROAs, deployed validation or changed production routing policy afterwards.

IETF
Enhanced uRPF Lets an Operator Admit Feasible Source Paths Without Trusting Every Route
A valid packet from a multihomed customer can arrive on a link that the receiving router would not choose for the return journey. Strict reverse-path forwarding may discard it; loose checking may accept any routed source. RFC 8704 defines a narrower middle ground: build an…

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…

NPNOG
A decade of meetings, but where is the outcome ledger? Auditing npNOG’s institutional value
npNOG can document that it kept opening the room. Its public chronology runs from the first numbered meeting in 2016 to npNOG-11 in 2025, with a virtual programme in 2020. The archive shows workshops, conferences, fellows, committees and technical subjects. That is not trivial…

Story
RIPE’s IRR Study Says RPKI Can Replace a Route Object, Not a Customer Cone
A new RIPE Labs study makes a useful distinction that is easy to lose in general talk about replacing the IRR. A prefix–origin record and the policy information used to discover a customer cone are not the same operational entity, so they cannot share one retirement decision.

Story
AFRINIC Says Douala-IX Strengthens Local Exchange. Its Public Snapshot Does Not Yet Measure It.
AFRINIC’s March community bulletin frames its support for Douala-IX as a way to strengthen local interconnection in Cameroon. The public evidence now available is useful, but it is an inventory of exchange attributes—not a measurement of the claimed operational result.

Story
RIPE’s RPKI Key Plan Is Not Yet a ROA Scope Receipt
RIPE NCC’s plan to move RPKI API keys toward OpenID Connect is a statement about a future access mechanism. It is not yet a public way to reconstruct which resource authority and which state-changing action stood behind an individual ROA change.

Story
LACNIC’s Bogon Guide Has Three Different Data Clocks.
A BGP filter can reject a route without saying why that route was rejected. Treating every rejected route as one security statistic may be convenient for capacity reporting, but it is too coarse to explain what the underlying evidence meant at the moment of the decision.

Story
APNIC Reissued Four Expired ASPAs. Its Repair Needs a State Receipt.
APNIC has reported a bounded correction: automatic renewal did not run, four ASPA entities expired, and the entities were reissued and published at 11:03. That is useful operational disclosure. It is not yet a measurement of what every repository, validator, router or customer…
Story
ARIN Kept Five Services Running Without Updates. Its Service-Level Report Has No Freshness Column
A registry can answer a question and still have nothing new to say. ARIN's planned July maintenance made that distinction visible: five reader-facing services remained operational while updates were not being published. The public service-level report measures availability well…

Story
LACNIC’s FORT Guide Skips the Signature Published Beside Its Tarball
The guide checks the validator after installation. It never checks the archive before extraction, even though the release already offered a digest, a detached signature and a public keyring.

Story
ARIN's Two Audit Findings Sound Opposite. They Test Different Controls
One ARIN Board record says no audited ticket was out of policy; another says inconsistencies appeared in every area examined. The difference is not a proven reversal in performance. It is a warning that audit findings become misleading when the test, standard and denominator are…

Story
LACNIC Calls Postman Its Current API. The Website Still Says ROAs Change by Serial Number
LACNIC gives an API operator two public descriptions of the same control surface. Its Registration API page says Postman holds the most current v3 documentation, while the route table beside that instruction describes modifying or removing one ROA by `serialNumber`. Follow the…