
Time Horizon
NEAR TERM
Within the Time Horizon facet, NEAR TERM time-horizon intelligence organises articles by the period over which a signal is expected to matter. The page helps readers distinguish immediate operational changes from longer-cycle governance, investment, standards, and infrastructure shifts that may unfold across quarters or years. It connects timing assumptions with public evidence, related actors, market context, customer exposure, policy pressure, and infrastructure planning so readers can judge whether a development is urgent, strategic, or still waiting on confirming evidence. The page also explains how time horizon changes the meaning of a signal, which organisations may be exposed, and which infrastructure decisions require short-term action or long-cycle monitoring.

IETF
A D-PATH Stops Loops Only When Gateways Agree on the Domain
A BGP attribute can carry a domain history, but it cannot decide what a domain is. RFC 10039 makes that prior decision operationally consequential: the same configured identifier that lets a gateway reject a returning route can also discard a legitimate route when the gateways…

IETF
RFC 7506 Is Historic. Router Alert 69 Can Still Be on the Wire
A standards register can retire a behavior without touching a single router. RFC 7506 is now Historic, its MPLS OAM Router Alert value is deprecated, and RFC 9570 says new LSP Ping implementations must not set it. None of those facts proves that value 69 has disappeared from an…
North America Institutional Trends
Rigetti’s CHIPS Cash Comes in Tranches. The Shares Do Not
Rigetti’s new federal package puts two nearly identical $100 million values on different clocks. The cash depends on technical milestones; the 7.74 million-share block is issued as one instrument, then constrained by separate transfer, voting and repurchase rules.
IETF
A NAT64 Mapping Is Not a Filtering Policy
A repeatable public tuple can prove how a stateful NAT64 translator allocates an address and port. It cannot prove which IPv4 sources are allowed to use that state on the way back. Treating those two facts as one control turns an interoperability test into a security verdict it…

North America Institutional Trends
Chime’s $590 Million Bank Deal Has an 18-Month Contract Fallback
Chime wants to replace a sponsor-bank relationship with ownership. Yet its merger agreement also prices the possibility that regulators prevent that change: under a narrow failure pathway, three agreements with Stride Bank do not expire on schedule but roll forward for at least…

IETF
One Operator Does Not Make One SRv6 Trusted Domain
A merger puts two routing estates beneath one legal owner. The new diagram draws a single box around them, and an automation team proposes removing the filters at the seam. The diagram may be administratively correct. It proves nothing about whether the two SRv6 instances share…

IETF
A Cleared Incident Does Not Prove Which Command Cleared It
An incident client sends one `incident-resolve` request containing several incident numbers. Later, separate notifications arrive. Two records now say `cleared`; another remains `updated`. The network view is useful, but the decisive question has vanished between the command and…

IETF
A Capability Menu Is Not a Subscription Decision
An orchestrator sees a tidy answer before it opens a notification stream: this device supports HTTPS, XML or JSON, and two TLS versions. The discovery is valuable precisely because it is compact. It becomes dangerous only when a control system silently turns “listed” into…

IETF
An Enrollment Voucher Arrives After Identity Leaves the Device
A constrained device can withhold its operational identity and still disclose enough to be enrolled. In Lightweight Authorization using EDHOC, that disclosure is deliberate: an authenticated domain authenticator receives the device’s enrollment identity and sends it to a trusted…

IETF
A Cryptographic Malfeasance Report Cannot Revoke Trust
Three time servers sign answers that cannot all be true in the order they were received. Roughtime lets a client preserve that contradiction as portable cryptographic evidence. Yet the proof does not name the guilty server, appoint the reviewer, alter a trusted-server list or…
Story
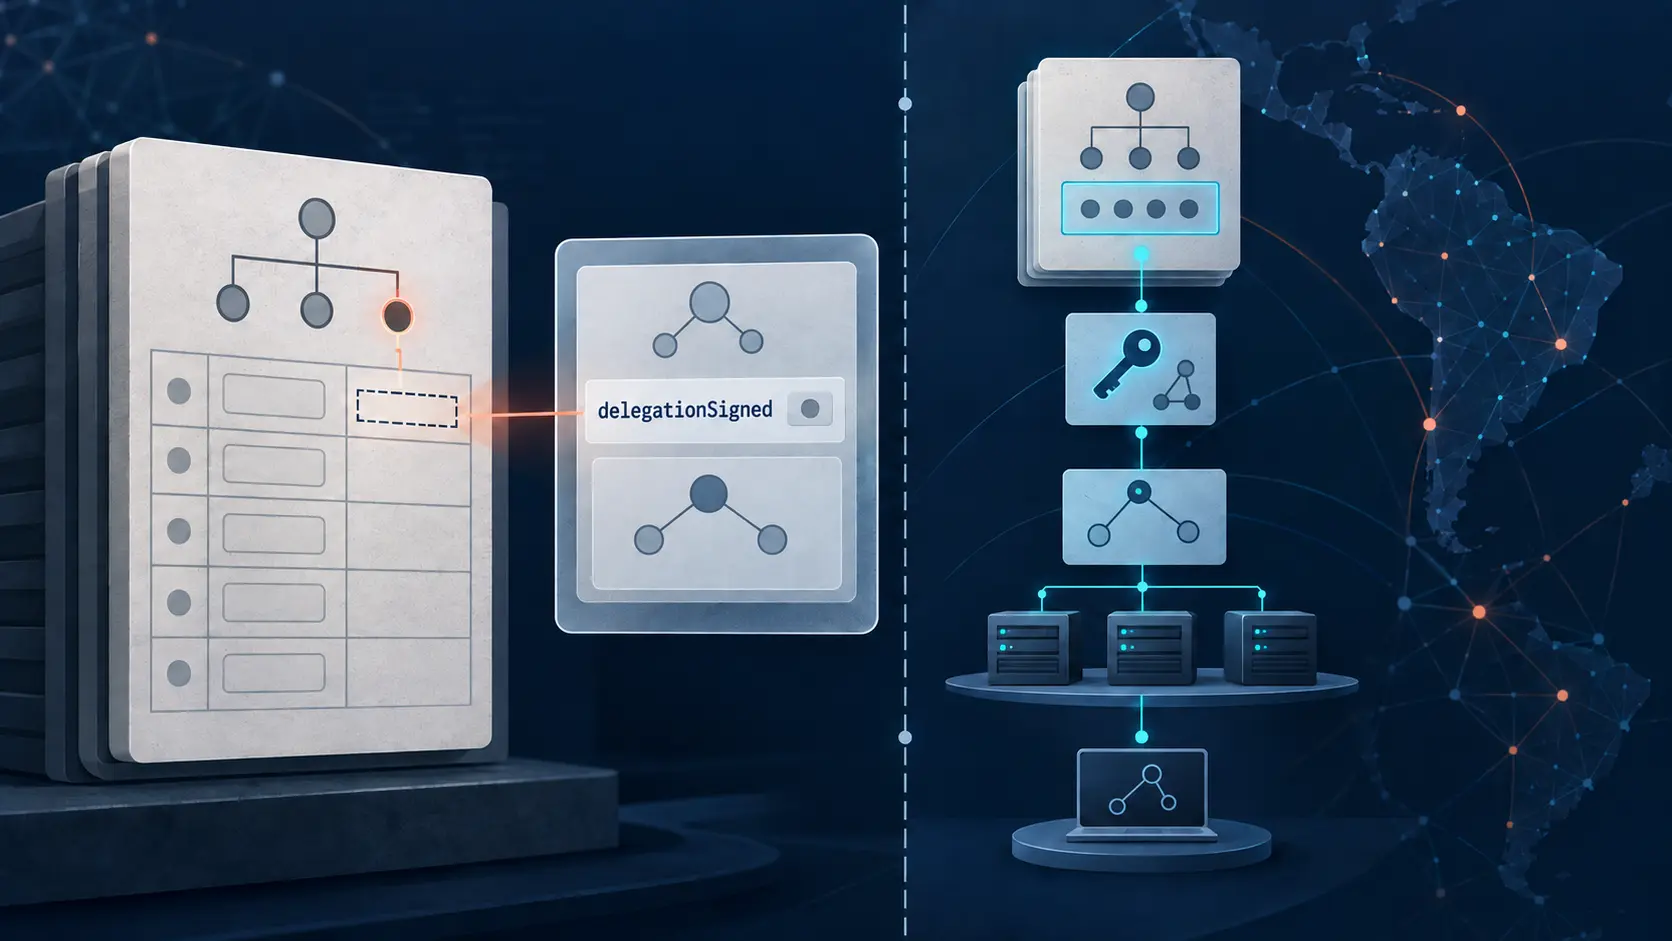
LACNIC's RDAP delegationSigned Records Parent DS Presence, Not DNSSEC Validation
A boolean in a registry response can look like a verdict on the security of a DNS chain. LACNIC's RDAP `delegationSigned` field answers a narrower question: whether the registration view reports DS records in the parent. It does not run a resolver, test the child keys or prove…

IETF
A Private Candidate Does Not Explain Why One Intent Won
Two engineers are authorized to change the same router. Each works in a private configuration branch, so neither can accidentally commit the other’s unfinished commands. Then both change the same node. The server can identify the collision and offer disciplined ways to resolve…

IETF
A YANG Minimum Version Is Not a Compatibility Floor
An importer asks for version 3.1.0 of a YANG module. On the shelf it finds 3.1.2 marked `_non_compatible` and 4.1.2, whose major number announces a breaking change. Both can satisfy the request. The result is not a loophole hidden in an implementation: it is the deliberately…
IETF
A Packet-Discard Counter Needs an Intent Epoch Before Automation Acts
At 02:14, an egress no-buffer counter starts climbing. The automation can move traffic in seconds. What it cannot see in the number is that a new service profile went live at 02:12, the line card restarted at 02:13, and the approved loss budget belongs to the configuration that…

IETF
One Shared Nameserver Is a Continuity Test, Not Proof of Delegation Control
A resolver looks again at a delegation it has cached. The parent now lists a mostly different set of nameservers, but one familiar name survives. That intersection can be enough to treat the delegation as continuous, provided any relevant signer overlap also holds. It is a useful…

IETF
DNS GREASE Needs an Experiment Charter Before It Becomes a Default
A resolver deliberately puts a value with no useful meaning into a DNS query. A correct peer ignores it. A brittle peer may reject the query, stay silent or provoke a retry. The experiment protects tomorrow’s protocol by creating a small inconvenience today. That bargain is…

IETF
Dry-Run DNSSEC Tests a Resolver Cohort, Not the Internet
A zone is signed, a validator finds the signature wrong, and the user still gets an answer. That apparent contradiction is the point of dry-run DNSSEC. Failure is exposed to an operator without yet becoming failure for the ordinary client. The rehearsal can reveal a broken…

IETF
A Deprecation Date Retires an RDAP Label, Not Its Clients
An IANA registry can mark an RDAP extension obsolete. An operator can publish an end date. Yet somewhere beyond both records, a client may still ask for yesterday’s interface. That is not a contradiction. It is a map of divided authority—and a warning against treating one date as…
IETF
DNSSEC Recovery Runs on Clocks No Signer Controls Alone
The private key is unusable. The zone is still answering, and yesterday’s signatures still validate. That is not recovery; it is borrowed time. A new DNSOP draft explains how to use that interval without destroying the trust that remains. Its harder lesson is institutional: the…
IETF
A Self-Signed Delegation Update Proves a Key, Not Its Authority
A DNS message can prove that its sender holds a private key and still leave the decisive question unanswered: who entitled that key to alter a child’s delegation? A DNSOP proposal for rapid child-to-parent updates makes that distinction explicit. Its lasting value will depend on…