
Time Horizon
Multi-year
Within the Time Horizon facet, Multi-year time-horizon intelligence organises articles by the period over which a signal is expected to matter. The page helps readers distinguish immediate operational changes from longer-cycle governance, investment, standards, and infrastructure shifts that may unfold across quarters or years. It connects timing assumptions with public evidence, related actors, market context, customer exposure, policy pressure, and infrastructure planning so readers can judge whether a development is urgent, strategic, or still waiting on confirming evidence. The page also explains how time horizon changes the meaning of a signal, which organisations may be exposed, and which infrastructure decisions require short-term action or long-cycle monitoring.

CASE FILE
The VLAN Field Was Twelve Bits. The Guidance Gave It Sixteen: RFC 9895
RFC 9895 makes Ethernet tags part of DLEP credit control, but its management guidance gives a 12-bit VLAN field a 16-bit-looking range. The wire format resolves the executable boundary; configuration, tests and vendor interfaces still need proof that they resolve it the same way.

IETF
Rohan Mahy and the Certificate Purpose That Did Not Deliver an Instant Message
An IM certificate can say that a key is meant for an instant-messaging identity. That narrower purpose is useful security design. It does not say that an application submitted a message, that a service accepted it, or that any person received and read it.

IETF
Neil Jenkins and the StateChange That Did Not Audit a Mailbox
A JMAP client that sees a new state string has learned something important: its local view may no longer match the server. That is a signal to synchronize. It is not, by itself, a record of which message changed, which mailbox moved, which principal made a request, which policy…

Global Cloud Services Trends
An OAuth Access Token Is Not a Current Authorization Decision
An access token can remain acceptable after the decision that justified it has changed: a self-contained token may still pass local cryptographic checks, while an opaque reference token may still be accepted through a state lookup. The operational question is therefore not merely…
Global Cloud Services Trends
A TLS Delegated Credential Is Not a Delegation of Domain Control
A short-lived credential can let a CDN edge complete a TLS handshake without holding the certificate owner's long-term private key. That is a precise cryptographic delegation. It is not a transfer of the domain, certificate-issuance authority or the organisation behind either…

Leaders
Prasad Vadke and the Escalation Clock Behind Enterprise Email
An enterprise email incident starts two clocks at once. One measures the technical work of diagnosis and recovery. The other measures missed decisions, interrupted meetings and the widening cost of uncertainty. Prasad Vadke's public writing on service-level agreements is most…
Global Cloud Services Trends
A QUIC Connection ID Is Not a Subscriber Identity
A QUIC connection can survive a change from Wi-Fi to mobile access. The identifier that helps packets find that connection is transport state, not proof of who holds the handset, which account is active, or whether an application action remains authorised.

Global Cloud Services Trends
A Fast 0-RTT Handshake Is Not a Once-Only Transaction
TLS 1.3 and QUIC can remove a round trip from a resumed connection. That is a latency result, not a receipt that a state-changing request reached the application once, was committed once, and will never be replayed elsewhere.
CASE FILE
The Certificate Challenge Crossed the Delay. Authority Did Not: RFC 9891
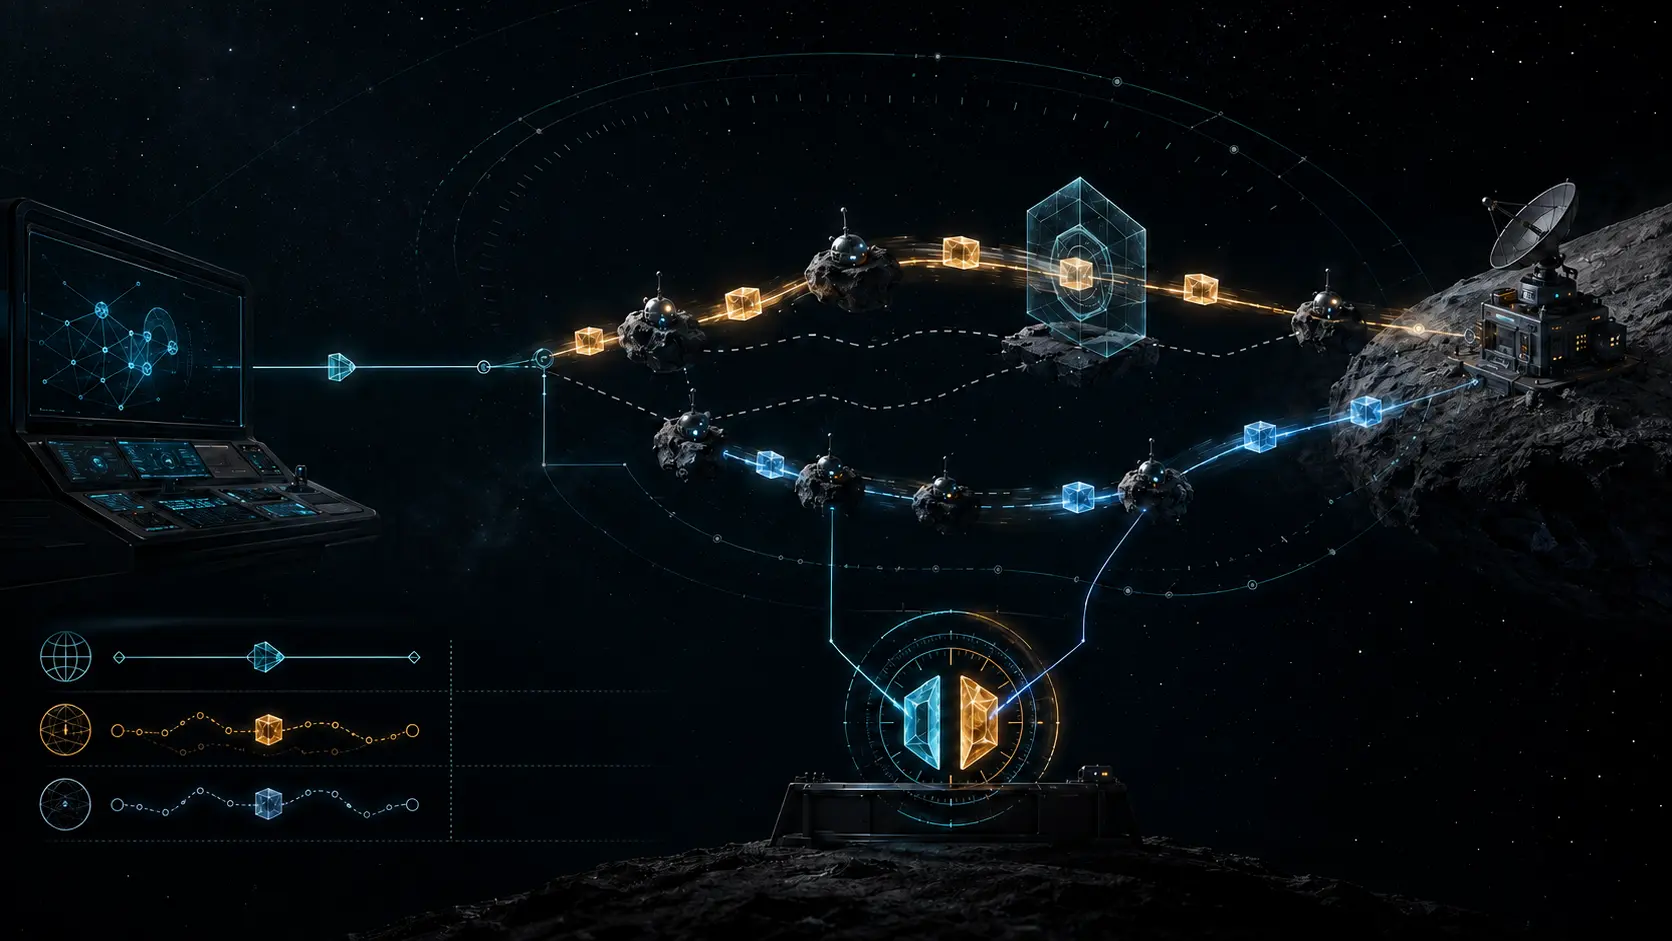
RFC 9891 carries an ACME proof through a delay-tolerant network, but it carefully stops the proof at control of a Node ID during one policy-bound exchange. Everything beyond that boundary still needs its own evidence.
Global Institutional Trends
A Valid Software Signature Is Not a Durable Authority Record
A green verification result can survive long after the authority that made a release legitimate has changed. The cryptography may still be sound. The missing evidence is organisational: who was permitted to sign, under which role, at what time, and what later revocation or…

Global Regional ISP Trends
A Graceful BGP Restart Can Lengthen a Blackhole
Graceful Restart is meant to keep traffic moving while a BGP process returns. Its safety depends on a fact the surviving session cannot prove by itself: whether the restarting router still has the forwarding state needed to carry packets. When a helper retains a route longer than…

Global Regional ISP Trends
A Fast IPv4 Fallback Can Make Broken IPv6 Look Healthy
A dual-stack service can answer every ordinary check while its IPv6 path is unusable. The availability result is real, but the protocol-family conclusion is not: a client may have escaped through IPv4 before the dashboard noticed what failed.

Global Cloud Services Trends
A Root Certificate Removal Is a Fleet Migration Before It Is a Browser Update
A root programme can withdraw trust in one release while many applications keep making decisions from older, private or embedded stores. The security change is complete only when the verifiers that matter can prove the intended rejection.
IETF
DNS TCP Fallback Is a Capacity Path, Not an Exception
A resolver can pass every small UDP health check and still fail the first answer that matters. When a response is truncated, correctness moves onto TCP; listener capacity, connection state and middlebox policy then become part of DNS availability.
IETF
Maciek Konstantynowicz and the Benchmark Result That Was Not a Service Guarantee
A network benchmark earns its value by saying exactly what it measured. RFC 9971 makes that discipline explicit: its MLRsearch result is a bounded result from stated trials and goals, not a transferable promise about every customer path, application or production hour.

History
Six Bytes Became an Address Only After the Domain Was Known: RFC 1449
An archive can preserve every octet and still lose the fact. Imagine finding six bytes in an old SNMP configuration: four could be an IPv4 address and two could be a UDP port. That reading is valid only if another field says the value belongs to the UDP transport domain. Without…

History
The Database Said One Address. The Reply Followed the Packet Back: RFC 1445
The address book and the live packet disagreed. For a new request, the 1993 SNMPv2 administrative model used the address recorded for the destination. For the reply, it ordered something else: use the transport domain and address from which this request actually arrived, even if…

History
The Clock Went Back. The Key Had to Change: RFC 1446
After a power failure, an SNMP agent wakes with yesterday’s shared secret and a clock that thinks yesterday has not happened yet. A captured request, previously too old to accept, can become “recent” again. Its digest never changed. The receiver’s boundary of acceptable time did.…

History
The Key Changed Before the Reply Arrived. The Manager Had to Remember Both: RFC 1446
The agent had already installed the new secret. Its reply was built with that new value. The manager, still waiting for the reply before changing its own database, continued to trust the old one. RFC 1446 made this awkward interval explicit: a secure command could succeed at its…
CASE FILE
The Name Stayed the Same. The Module Did Not: RFC 9890
RFC 9890 makes a small registry correction with a large evidentiary consequence: a YANG module keeps its name and XML namespace across revisions, so identity alone can never tell an operator which definitions a system actually uses.