
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

IETF
WiCoP Is a Historic Control Record, Not a Deployment Baseline: RFC 5414
RFC 5414 describes WiCoP, a Wireless LAN Control Protocol for centrally managing and provisioning large WLANs. The RFC Editor marks it Historic and identifies RFC 5415 as the replacement. That status changes the question for a leadership team: a controller diagram or provisioning…

IETF
SLAPP Security Is a Historical Boundary, Not Deployment Proof
RFC 5413 records the Secure Light Access Point Protocol as submitted during the CAPWAP work. Its discovery, authentication and secure transport ideas are useful historical evidence, but the RFC Editor says the document was published solely for the historical record, was not…

IETF
LWAPP Is a Historic Record, Not a Deployment Baseline
RFC 5412 documents the Lightweight Access Point Protocol as it was submitted during the CAPWAP work. It is valuable archival evidence about an access controller and wireless termination point model, but the RFC Editor explicitly labels it Historic and says it should not be used…

IETF
CATS Chose the Service Contact. The Backend Stayed Hidden: RFC 10053
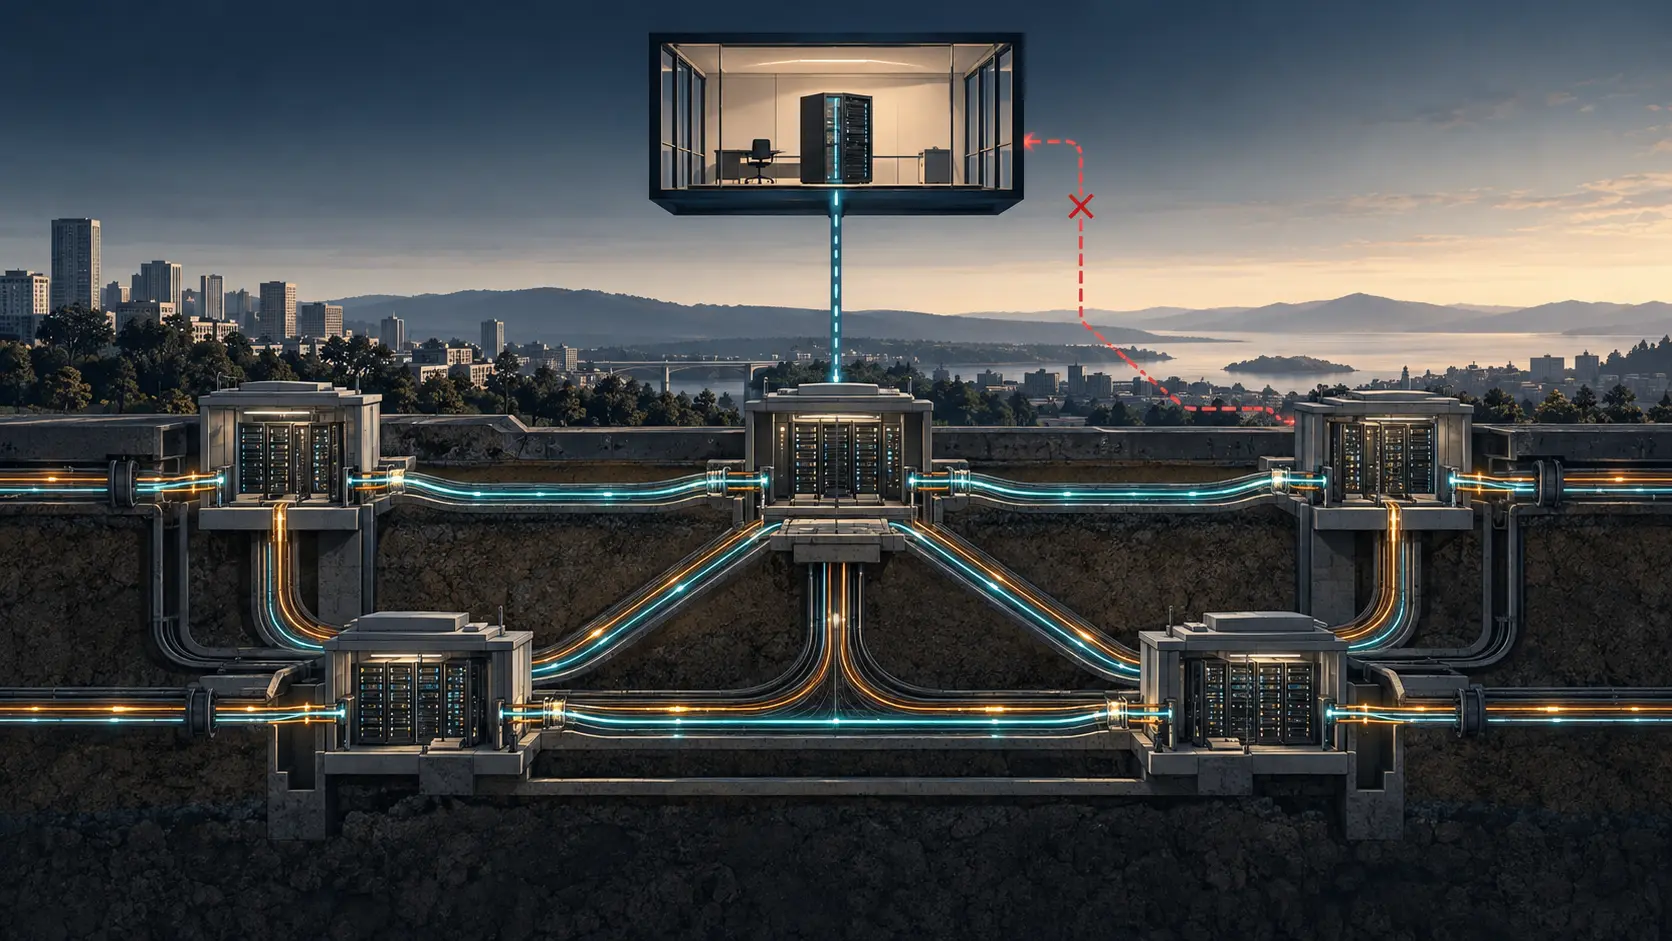
CATS can steer a request toward a promising service contact using network and compute conditions. That choice still may not reveal which service instance handles the request behind the contact, or whether the reported metrics describe that instance alone.
History
The Controller Needed a Network Before It Could Control One: RFC 7149
In March 2014, an IETF memo asked service providers to look past the seductive diagram of a central controller and ask a more operational question: how does that controller find, reach and safely influence the network beneath it? RFC 7149 treated startup, customer negotiation and…

IETF
A SIP Guide Is a Map, Not a Deployment Certificate.
RFC 5411 is useful precisely because SIP is too large to hold in one mental model. It groups the RFC series by topics, labels their status and points readers toward related work. But the document is an Informational snapshot, not a live inventory of what a carrier runs. A listed…

IETF
The Broadcast Extension Carried a Key Message. It Did Not Prove the Key Was Installed.
OMA BCAST needed MIKEY to carry more than one kind of control message: short-term keys, long-term keys, reporting data and parental-control information. RFC 5410 adds a General Extension payload for that transport. The payload proves that a particular message was encoded for a…

IETF
CMS Wrapped the Key. The Recipient Identity Still Had to Match.
RFC 5409 is not a general promise that “IBE works with email.” It defines the CMS conventions for encrypting a content-encryption key with Boneh-Franklin or Boneh-Boyen IBE, including recipient-identity encoding and algorithm identifiers. The envelope can be structurally valid…

IETF
The Identity Could Be a Public Key. It Still Was Not Permission.
An identity-based encryption design promises a neat operational shortcut: calculate a public key from the recipient's identity, encrypt immediately, and ask a trusted private-key generator for the matching secret only when the recipient needs it. RFC 5408 makes the shortcut…
Creators
A Phrase Traveled Without Its Author: Cory Doctorow and Interoperability’s Policy Boundary
When a Canadian parliamentary witness invoked Cory Doctorow’s phrase “adversarial interoperability,” she was speaking about a bill on copyright locks and software-enabled devices. The exchange carried an idea into a formal record, but it did not make Doctorow the witness, the…

IETF
A Better Edge Is Not Permission to Move the Session: RFC 10054
A client can leave the metro edge while its service remains stateful. RFC 10054 says a routing system may account for both network and compute conditions, but a mid-session move needs an explicit application indication that CATS is allowed. The faster destination and the…

IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An SIP gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5407 draws a harder line: SIP Version 2 can bind a SIP message to lower-channel information, but the binding does not become local…

IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An IPsec gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5406 draws a harder line: IPsec Version 2 can bind a IPsec message to lower-channel information, but the binding does not become…
IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
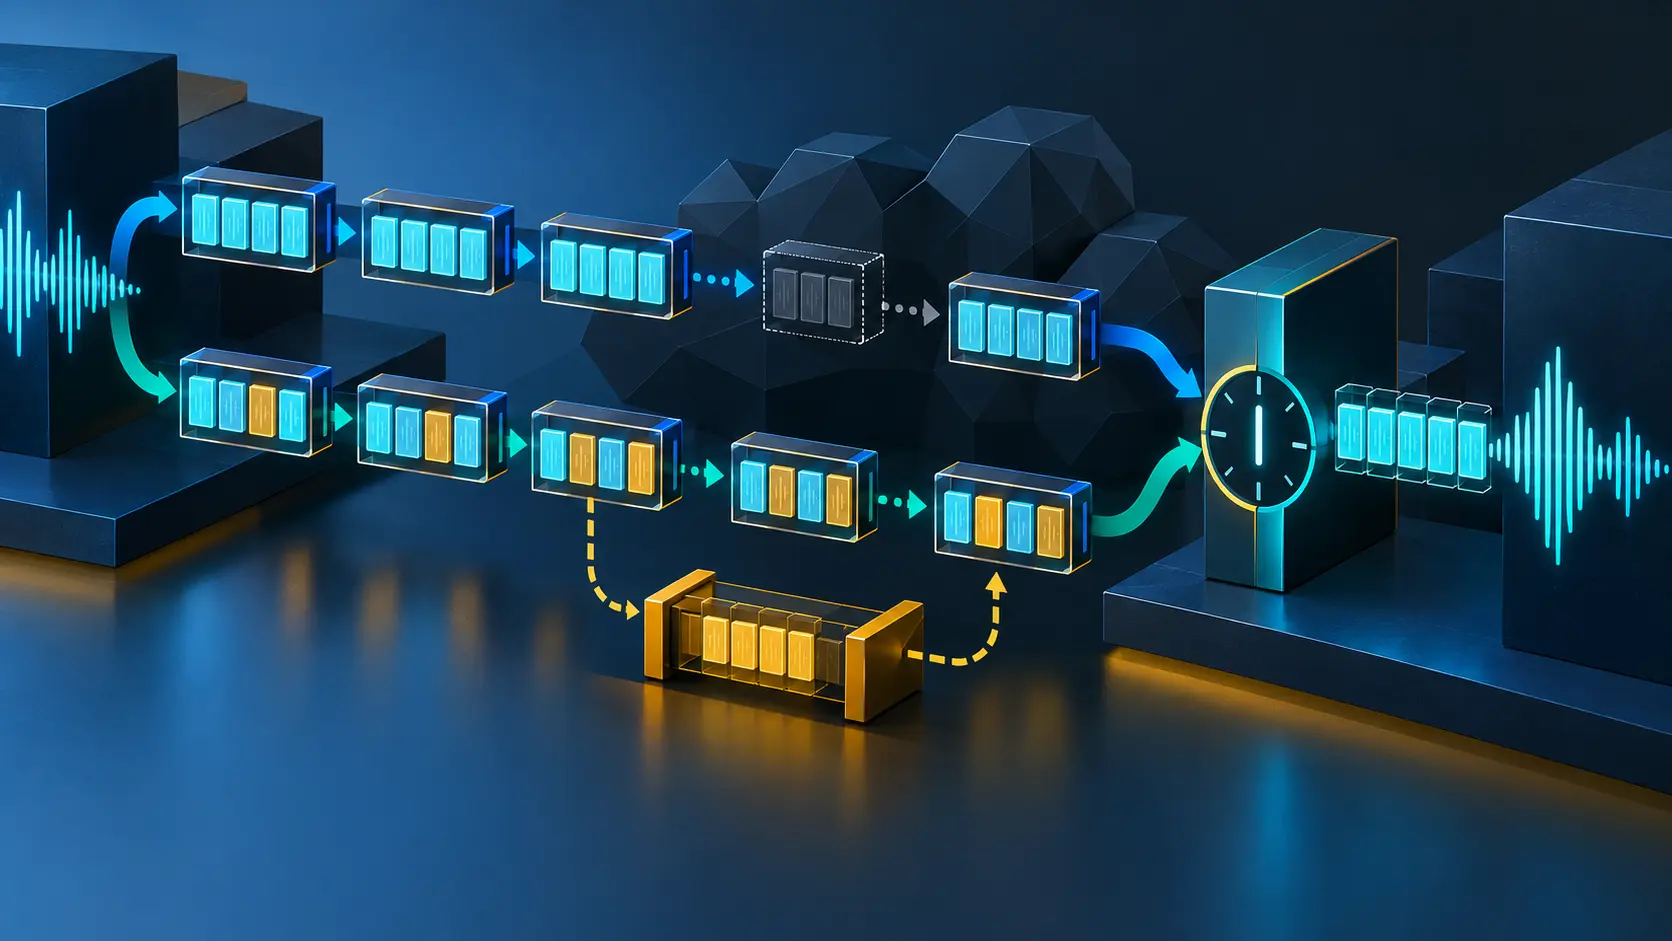
An RTP gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5404 draws a harder line: G.719 RTP Version 2 can bind a G.719 frame block to lower-channel information, but the binding does not…

IETF
The Channel Was Bound. The Operation Was Still a Separate Decision.
An RPC gateway showed a verified security context and a clean message check. The dashboard promoted that evidence into “authorised and complete.” RFC 5403 draws a harder line: RPCSEC_GSS Version 2 can bind a GSS context to lower-channel information, but the binding does not…
IETF
Only One Side Authenticated. Both Ends Still Had to Bind the Channel: RFC 5387
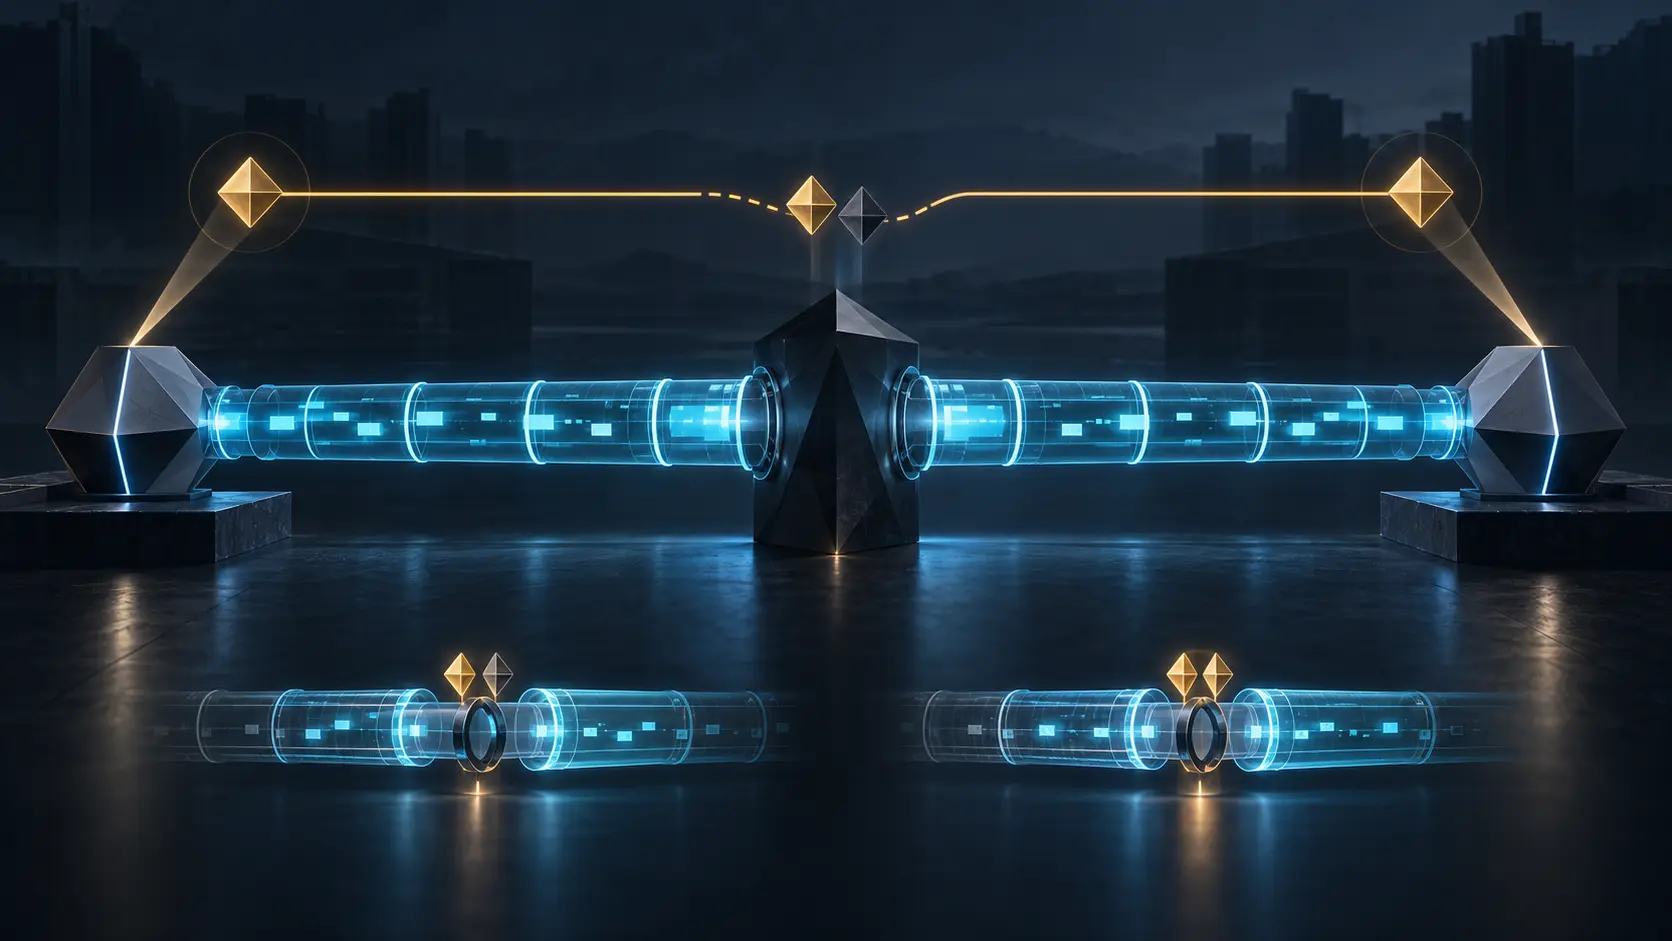
Two control panels can each show a green lock while an unauthorized proxy sits between them. RFC 5387 explains the missing evidence: authentication may intentionally run in one direction, but the claim that both parties share one protected channel has to be checked at both ends.…

History
A Global Address Could Be a Loan, Not a Host's Identity: RFC 1335
In May 1992, one proposed answer to IPv4's allocation pressure began with a quiet distinction: a machine could keep its address at home while borrowing a globally unique one only when it needed to cross the Internet.

IETF
The Receipt Matched. The Order Was Not Yet Accepted.
The trading gateway returned a signed receipt with the expected Message Integrity Check. A dashboard promoted that narrow success into “order accepted.” RFC 5402 shows why the promotion is unsafe: compression changes which bytes sit inside the signature and MIC boundary, while…

History
The Smaller Number Had to Move First: RFC 3988
One number said the path had grown wider. Another said it had just narrowed. RFC 3988 did not treat those reports as equally urgent, because only one of them could turn yesterday’s safe packet into today’s silent loss.
IETF
The Page Looked Final. The File Was Not: RFC 5385
An executive opens a document, checks that every heading, page break and reference looks right, and approves what appears on screen. RFC 5385 shows why that moment is useful but incomplete: the visible page was an authoring view, while compliant output still depended on styles, a…