
Profile
Intelligence Briefing
Intelligence Briefing profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

Global Cloud Services Trends
TLS 1.3 0-RTT Acceptance Is Not a Replay-Safety Decision
Early data can remove a round trip from a resumed connection. That speed is real, but accepting the bytes does not prove that the application operation is safe to execute twice, authorised under current policy or protected by a shared deduplication decision.

Number Resource Society
An ASPA Is Not a Complete AS-Path Attestation
An ASPA can help an operator test whether an AS path is consistent with published customer-to-provider authorizations. That is valuable route-leak evidence. It is not a signature over every hop, a proof of route origin, a commercial contract, or a guarantee that the published…

Global Regional ISP Trends
A QUIC Connection ID Is Not a Durable Principal
A connection identifier can keep a QUIC session reachable while the network path changes. That continuity is operationally useful, but it does not turn the identifier into an account, a subscriber or a durable statement about who is authorised now.

Number Resource Society
A ROA maxLength Is Not a Traffic-Engineering Policy
A route can be RPKI Valid because a ROA’s maxLength admits its prefix length. That result proves a bounded origin authorization. It does not prove that the more-specific route was planned, approved, currently announced or preferred by the operator. Those are separate facts, and…
Number Resource Society
A BGPsec Router Certificate Is Not Route-Origin Authority
A BGPsec Router Certificate Is Not Route-Origin Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Global Cloud Services Trends
A Fresh HTTP Cache Entry Is Not Current Origin Authorization
A cache can be correct about age and wrong about present authority. Freshness permits reuse of stored bytes; it does not prove that the origin still wants those bytes disclosed to this requester.

Global Cloud Services Trends
Kaleris Gained 25 EDI Links, Not One Repair Ledger
Newport Systems gives Kaleris an installed transport network between equipment owners and repair providers. The harder asset is common meaning for every estimate, authorisation, exception and invoice.
North America Datacenter Trends
Augmenta's 8.5x clock stops at the first populated model
An 82-hour model-population result may be commercially useful on a large data-centre job. It is not yet a clock for design approval, fabrication, installation or the finished building.

Global Datacenter Trends
Flex Has a $4.4bn Bridge for a $4.4bn Deal, Not SpinCo’s Final Balance Sheet
The acquisition price, the temporary funding ceiling and the planned separation sit on three different clocks. Investors still need the permanent financing and allocation record that connects them.
North America Datacenter Trends
A 54-MW turnkey promise still needs an acceptance sequence
Northampton and Provident have formed a joint venture for a North Dallas data centre targeted for late 2027. The commercial test is how utility, fit-out, network and customer obligations turn a site figure into accepted computing capacity.

Global Cloud Services Trends
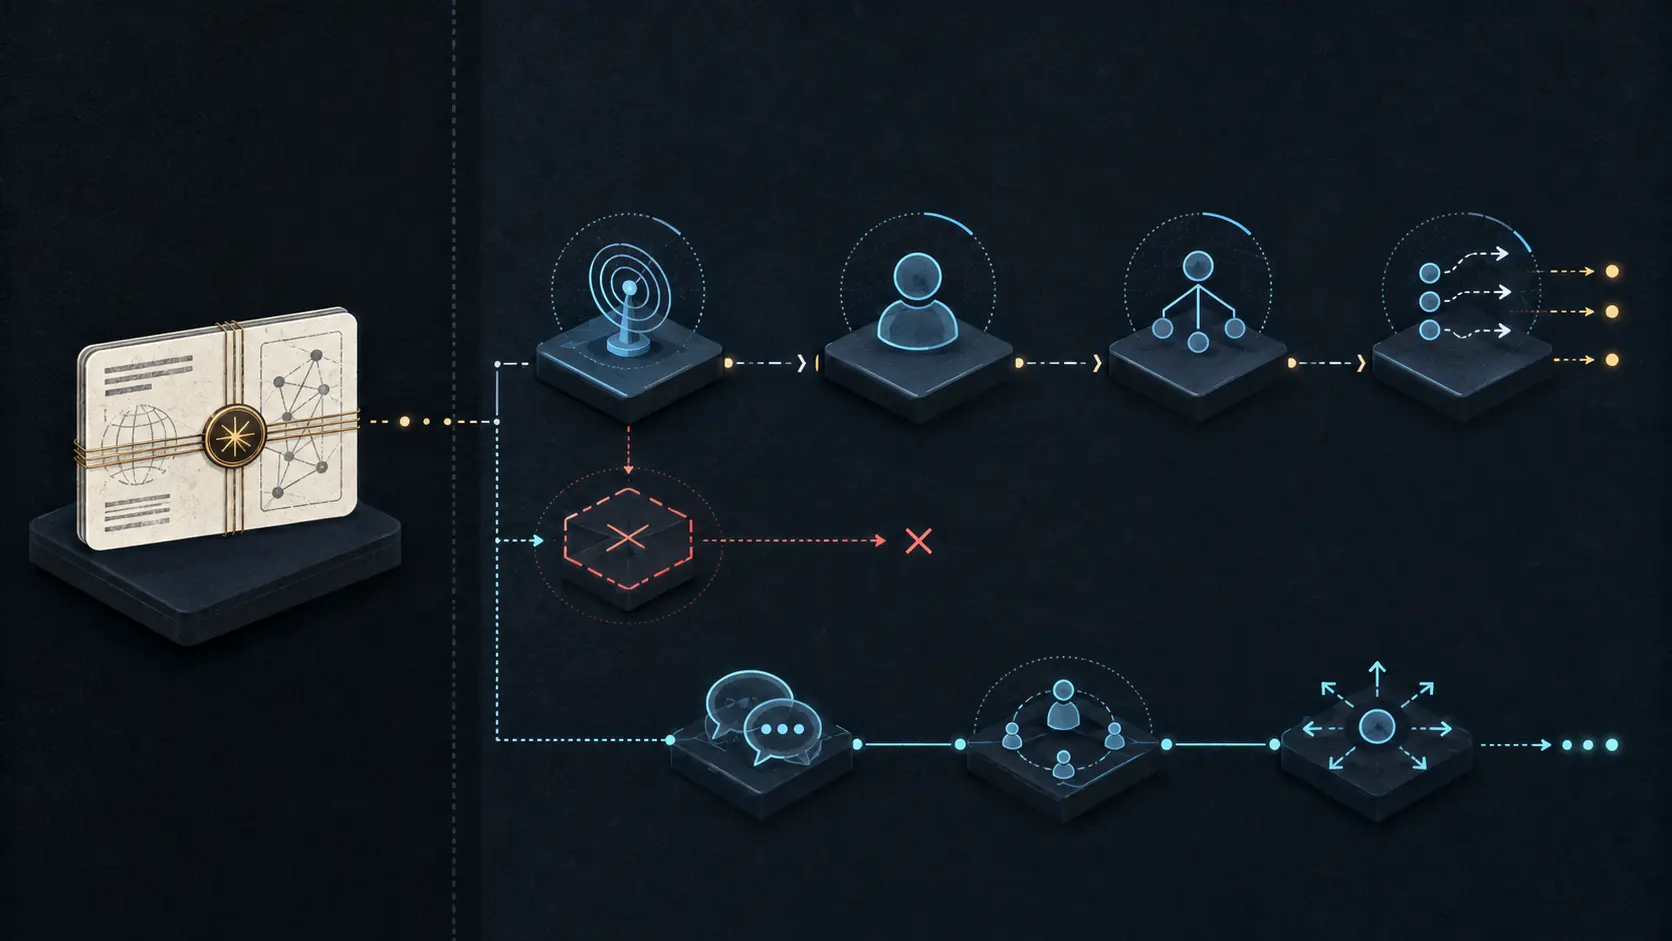
An OAuth Access Token Is Not a Current Authorization Decision
An access token can remain acceptable after the decision that justified it has changed: a self-contained token may still pass local cryptographic checks, while an opaque reference token may still be accepted through a state lookup. The operational question is therefore not merely…
Number Resource Society
A Ghostbusters Record Is Not an Incident Command Roster
An RPKI relying party can validate every byte of a Ghostbusters Record and still not know whether anyone is watching the listed channel when action is needed. The signed entity solves discovery of minimal CA-maintainer contact data; operational accountability begins where that…

Number Resource Society
A Trust Anchor Rollover Needs an Acceptance Ledger
An RPKI trust-anchor operator can publish a successor key without making every relying party ready to use it. The transition is a sequence of verified observations, not a launch date: a defensible record must show what was announced, what remained stable, which validators crossed…
Global Cloud Services Trends
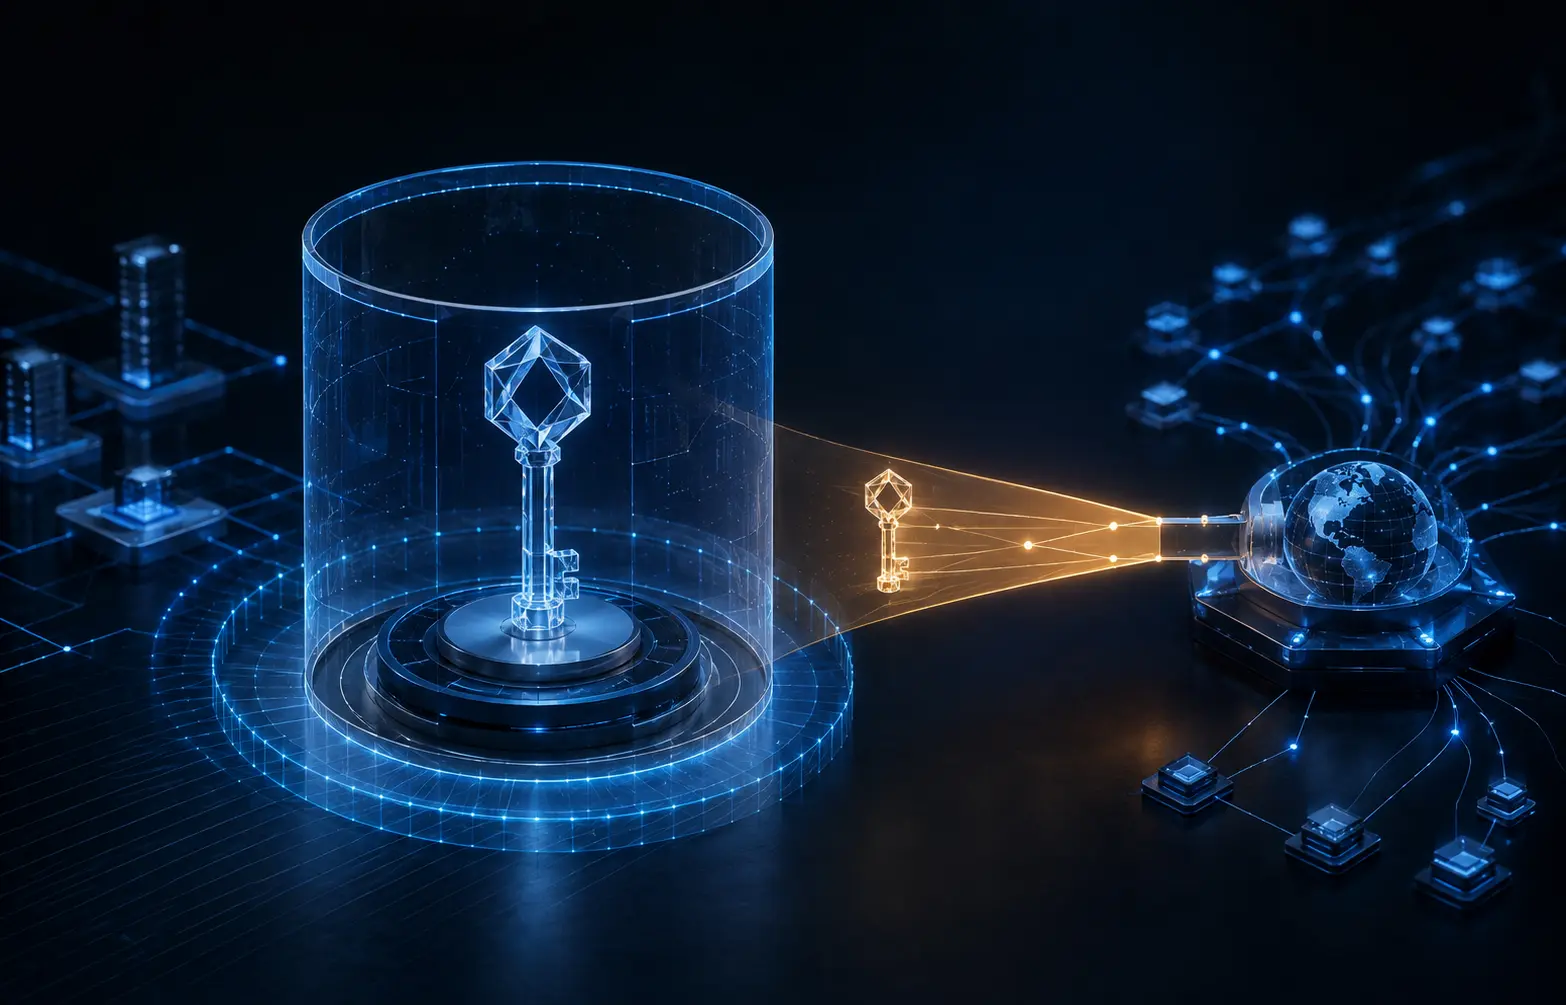
A TLS Delegated Credential Is Not a Delegation of Domain Control
A short-lived credential can let a CDN edge complete a TLS handshake without holding the certificate owner's long-term private key. That is a precise cryptographic delegation. It is not a transfer of the domain, certificate-issuance authority or the organisation behind either…

Number Resource Society
An RPKI Publication Point Needs a Commit-to-Visibility Ledger
An RPKI publication server can accept an authenticated update atomically while relying parties still hold an earlier repository view. That is not necessarily a contradiction or a failure. It is a boundary between different authorities, protocols and observation times. A useful…

Number Resource Society
An ASN Transfer Needs a Routing-Identity Handover Ledger
An ASN Transfer Needs a Routing-Identity Handover Ledger intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Global Cloud Services Trends
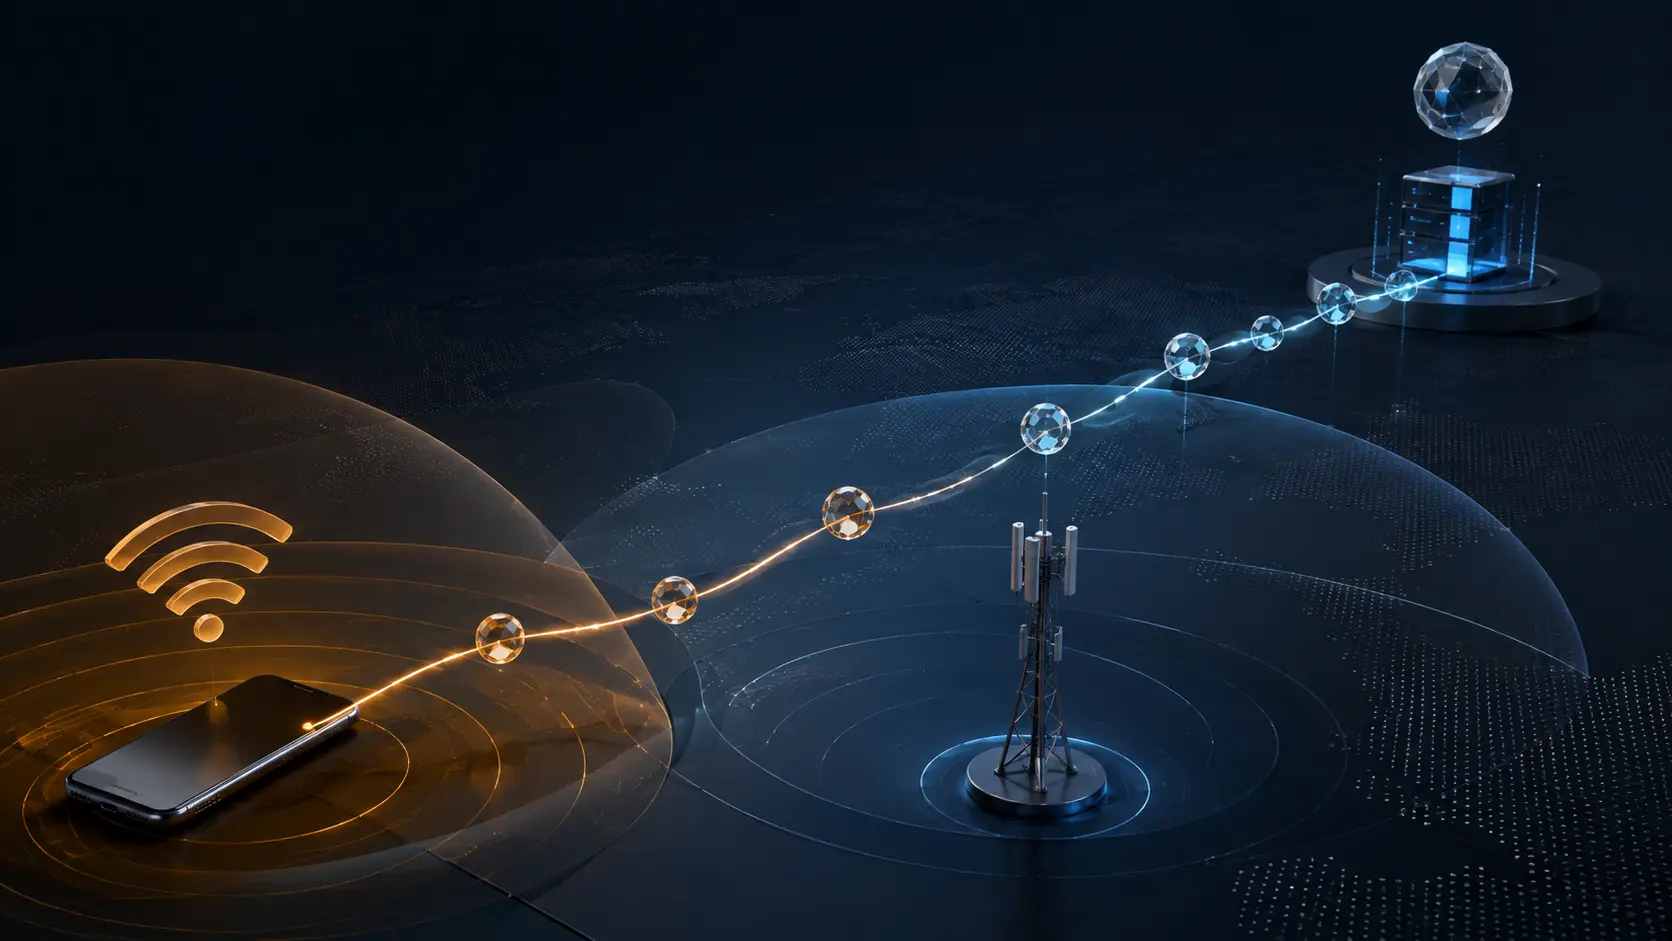
A QUIC Connection ID Is Not a Subscriber Identity
A QUIC connection can survive a change from Wi-Fi to mobile access. The identifier that helps packets find that connection is transport state, not proof of who holds the handset, which account is active, or whether an application action remains authorised.
Number Resource Society
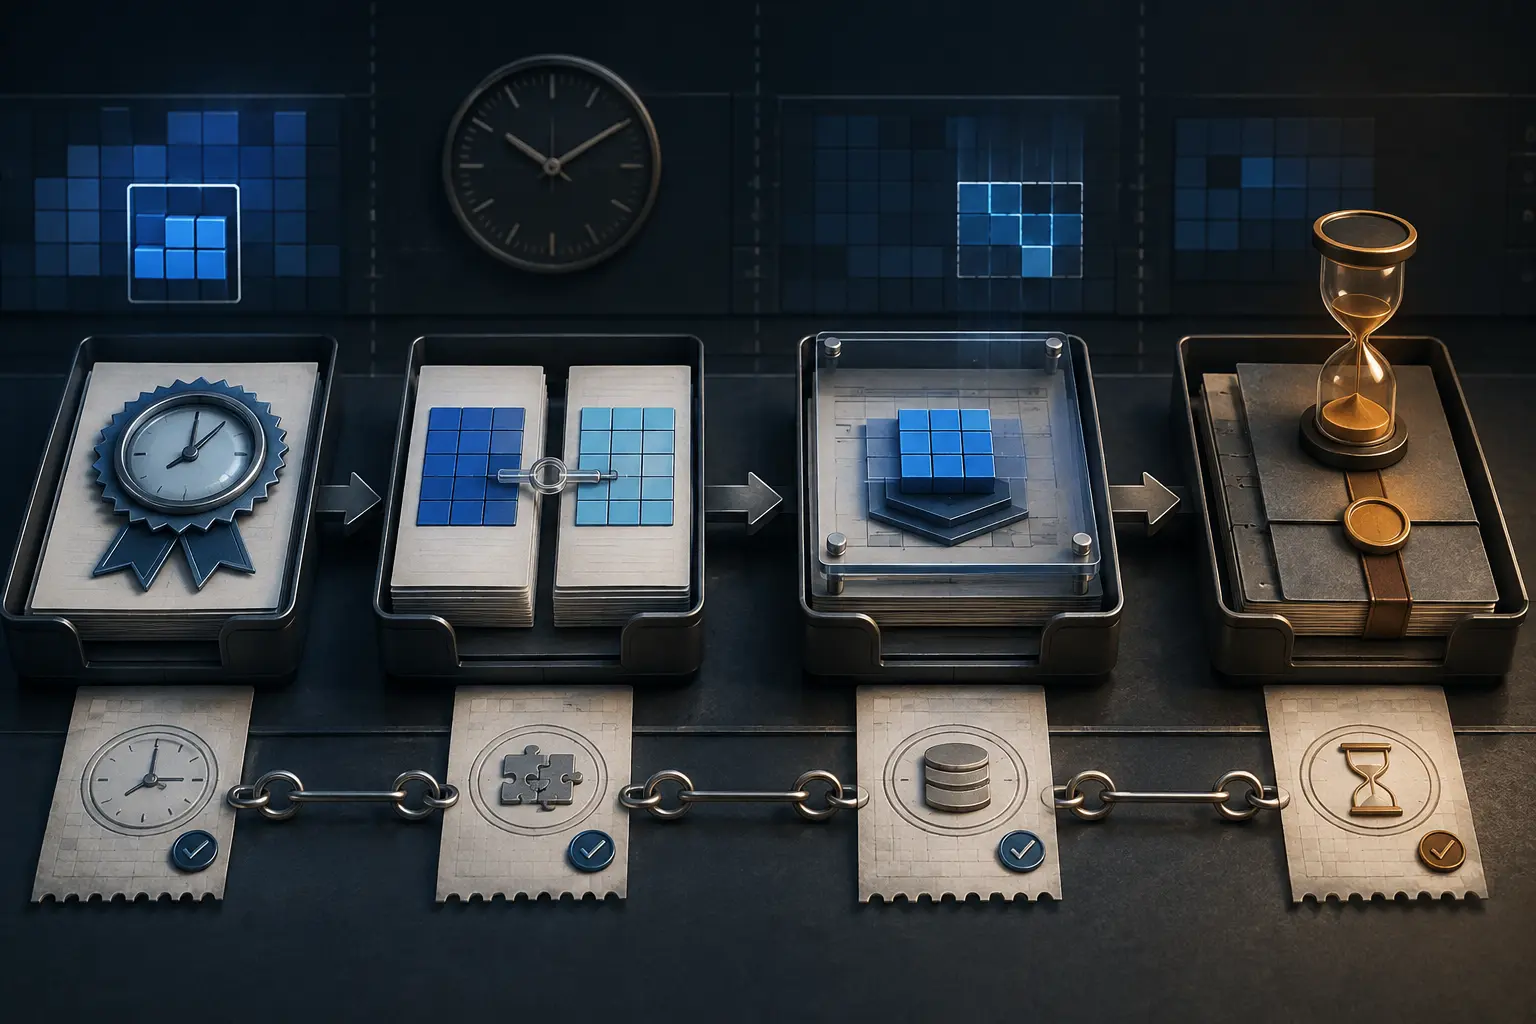
An IPv4 Transfer Pre-Approval Needs a Registration-and-Expiry Ledger
An IPv4 transfer pre-approval answers a narrow question: how much address space a recipient may qualify to receive during a defined period. It does not identify a source, complete a transfer or prove that the registry has changed.

Number Resource Society
A Number-Resource Policy Decision Needs an Adoption-and-Implementation Ledger
A consensus announcement is useful evidence, but it is not by itself a complete answer to what text applies or when an operational change took effect.

Global Cloud Services Trends
A Fast 0-RTT Handshake Is Not a Once-Only Transaction
TLS 1.3 and QUIC can remove a round trip from a resumed connection. That is a latency result, not a receipt that a state-changing request reached the application once, was committed once, and will never be replayed elsewhere.