
Primary Domain
Infrastructure
Within the Primary Domain facet, Infrastructure intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.
IETF
Default Reject Turns Missing EBGP Policy from Silent Authority into an Explicit Failure
An external BGP session can be established while its authority to receive or advertise routes remains undefined. RFC 8212 changes the default at that boundary: without import policy, accept no routes; without export policy, announce none. The leadership question is not whether a…

History
The Chain That Made a Public Key Believable: PEM Certificate Management
A public key does not identify its owner by itself. RFC 1422 addressed that gap for Privacy Enhanced Mail by specifying certificates, certification authorities, validation paths, and revocation information—the institutional machinery needed before a relying party could treat a…

IETF
Enhanced uRPF Lets an Operator Admit Feasible Source Paths Without Trusting Every Route
A valid packet from a multihomed customer can arrive on a link that the receiving router would not choose for the return journey. Strict reverse-path forwarding may discard it; loose checking may accept any routed source. RFC 8704 defines a narrower middle ground: build an…
IETF
The Prefix Arrived Before the Query: How RFC 9872 Changes NAT64 Discovery
An IPv6-only host that must reach IPv4 services needs to know which IPv6 prefix its network uses for address synthesis. RFC 9872 turns that knowledge into an access-network signal: learn PREF64 from Router Advertisements first, and use DNS discovery only when that signal is…

Europe and Middle East National Telecom Trends
A satellite handset in storage is not a local outage fallback until airtime, deployment and call routing are exercised
A satellite handset can diversify emergency communications when terrestrial services fail. Its presence in a resilience cupboard does not prove that the duty team can power it, deploy it, obtain service or complete the call route the local plan depends on.
History
The Pointer That Was Never Out of Band: TCP Urgent Data
TCP urgent data is a small control surface with a long history. The URG flag makes a 16-bit urgent pointer meaningful, but RFC 793 described the boundary it marks in two contradictory ways. That ambiguity crossed from the specification into implementations and application APIs.

IETF
ZONEMD Lets a Secondary Verify the Zone After the Transfer Ends
A completed zone transfer proves that a delivery procedure finished. It does not, by itself, prove that the receiver assembled the exact zone the publisher intended. ZONEMD adds a digest over the zone as a whole, creating a verification boundary after transport and before a…
IETF
The Bitmap Says a UDP Option Appeared—not What It Did: RFC 9870
RFC 9870 gives IPFIX exporters a compact way to report which UDP Option kinds appeared in a Flow. Its bitmaps are useful precisely because their claim is narrow: they preserve observed presence, not a packet history, a receiver’s processing decision or an application outcome.
IETF
DNS TCP Fallback Is a Capacity Path, Not an Exception
A resolver can pass every small UDP health check and still fail the first answer that matters. When a response is truncated, correctness moves onto TCP; listener capacity, connection state and middlebox policy then become part of DNS availability.

Europe and Middle East National Telecom Trends
A privileged-access SIM is not a local emergency communications plan until activation and use are verified
MTPAS can improve an eligible responder’s chance of accessing a congested mobile network. A special SIM in an inventory does not show that the right person can use it, that the activation route is understood, or that an alternative exists when mobile service is unavailable.

Story
A Failed RIPE Database Update Can Still Change Records
RIPE NCC's documentation describes an update message whose entities can finish differently. The useful response is therefore not just a verdict on the message: it is an account of the changes already made, those rejected and those the caller still cannot confirm.
IETF
A Negative Trust Anchor Lets the Resolver Suspend DNSSEC Without Changing the Zone
When a signed domain breaks, a validating recursive resolver can either preserve the failure or create a narrow local exception. A negative trust anchor restores reachability without repairing the zone, but it transfers temporary authority over DNS authentication to the resolver…

IETF
Mukul Srivastava and the BMP Gauge That Counted a RIB but Did Not See a Route
A number can be both useful and radically incomplete. RFC 9972 gives BMP operators a more precise way to report how many routes occupy a named RIB view at a particular moment. It does not turn that count into a route record, a policy explanation or a delivery observation. Mukul…

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…
IETF
A DNS Cookie Supplies Return-Path Evidence, Not Client Identity
A valid DNS Server Cookie can show that a requester at a source address is returning a value issued in an earlier exchange. That is useful evidence against off-path forgery. It is not a login, a durable device identifier or permission to attach a person’s name to the query.
Global Cloud Services
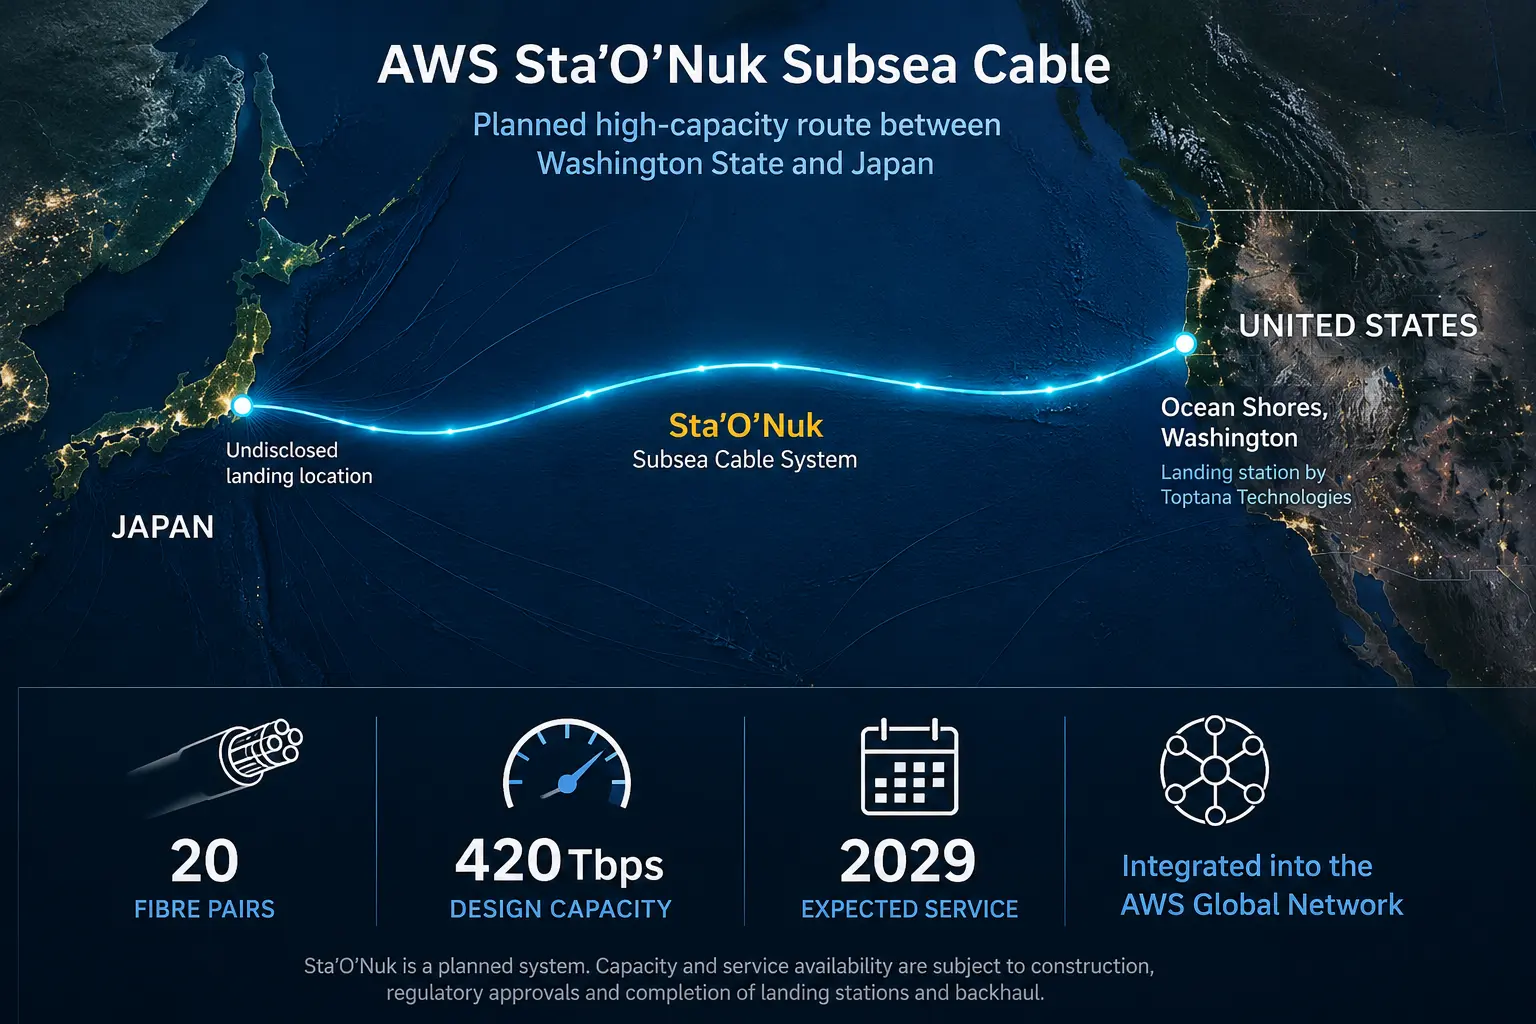
AWS plans 420Tbps US-Japan subsea cable
AWS is developing Sta’O’Nuk, a 20-fibre-pair subsea cable between Washington state and Japan that it expects to bring into service in 2029.

Global National Telecom Trends
SES, De Boer Marine expand FlexMaritime partnership
SES will supply FlexMaritime connectivity while De Boer Marine handles onboard installation and management for maritime customers under a multi-year agreement.

Asia-Pacific Institutional Trends
Shunkai quantum computer starts operation
Japan's Shunkai system is operating with an initial configuration of about 50 qubits as researchers begin work on stability, external access and larger-scale operation.

Europe and Middle East Institutional Trends
North Media buys BEAM grid-balancing platform for DKK 9m
North Media has acquired BEAM, a software platform designed to aggregate distributed energy assets for Denmark's grid-balancing market.

Europe and Middle East National Telecom Trends
Neo Space Group and Arabsat sign satellite services MoU
Neo Space Group and Arabsat will explore satellite communications, geospatial services and other space technologies across the Gulf and Middle East.