
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

History
The IPv6 /48 Was a Starting Point, Not a Size for Every Site
The story of the IPv6 /48 is not that the IETF discovered it was too large. It is that a tidy architectural recommendation became awkward when different kinds of real networks had to live inside the same prefix table.

IETF
What Exactly Did the Signed Conversation Container Prove?
The vCon drafts propose a portable home for parties, dialog, attachments and machine analysis. The difficult governance question begins after its signature verifies: whether the package captured the whole conversation, whether its claims are true, and whether its signer had…

History
The Core Forgot the Flow. The Edges Still Had to Prove Its Reservation: RFC 3175
RFC 3175 offered an attractive bargain in 2001: stop making every core router remember every reserved flow, but preserve end-to-end admission at the edges. The bargain worked only if state compression did not become evidence compression. One large reservation could carry…

History
The IETF Removed a Conduct Rule That Could Discourage Newcomers
In 2014, an IETF revision did more than refresh a conduct guide: it recorded that one warning to newcomers could be read as a reason not to participate—and removed it.

History
The DNS MIBs Never Reached Deployment. RFC 3197 Made That the Point.
RFC 3197 is a rare standards postmortem: it says two DNS management MIBs never found deployment, then treats that absence as evidence about the project—not about DNS itself.
History
The Zone Was Critical. That Did Not Make It a Permanent Root-Server Job: RFC 3172
In 2001, `.arpa` was important enough to inherit the operating expectations of the DNS root. Yet RFC 3172 did not convert that importance into a permanent claim on root-server machines. It recorded the shared service arrangement as something likely to change. The name could…

IETF
Who Gets to Vouch for a Client? OAuth’s New Two-Key Trust Problem
An emerging OAuth proposal lets a client publisher name the attesters allowed to speak for its software. The harder lesson is what the metadata cannot do: choose the authorization server’s trust, revoke an issued grant, or turn a verified statement into permission.
History
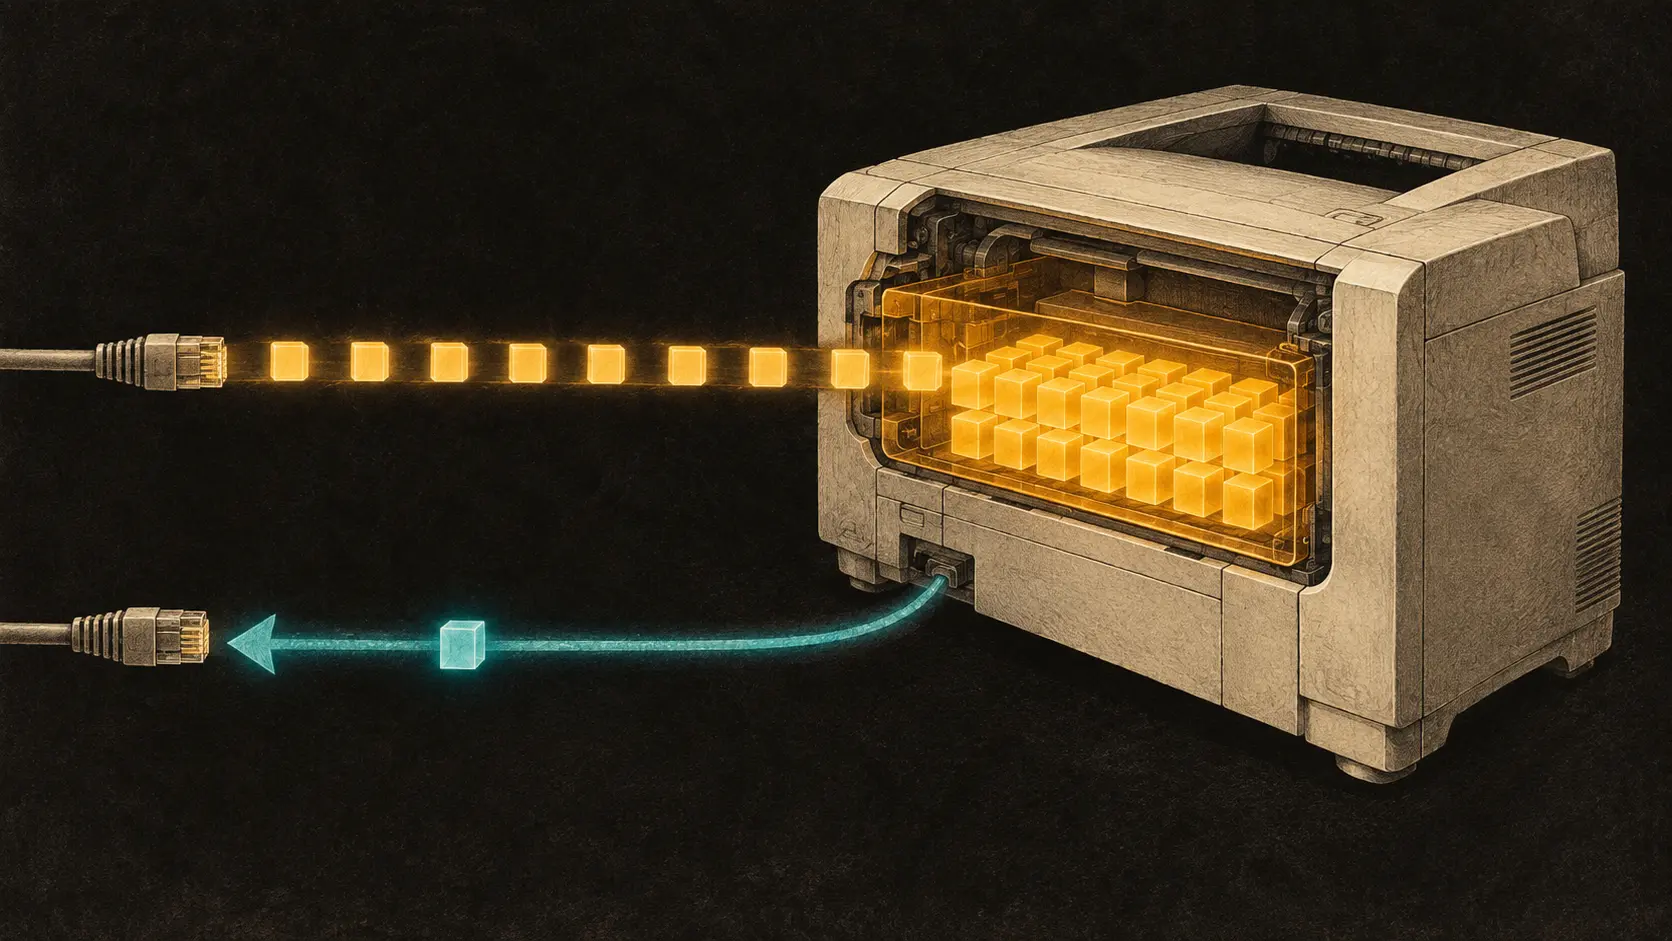
The Printer Had to Accept the Whole Request Before Replying: RFC 3196
In 2011, a small correction to an older printing guide changed a deceptively important boundary: an IPP printer’s final answer to a print request could no longer be treated as implementation-dependent while the document itself was still arriving.

History
The Registry Assigned the Multicast Address. It Still Had to Ask Whether Anyone Used It: RFC 3171
An entry in a registry can look permanent because the number does not move. RFC 3171 treated that stillness with suspicion. A globally coordinated IPv4 multicast address was scarce enough to require a reason, alternatives, periodic review and—where possible—reclamation. The…

IETF
The DNS Published the Schema. The Server Still Had to Decide Whether to Execute It.
A proposed DNS extension language could let new record types travel as configuration rather than wait for a software release. That shortens one adoption path. It also creates a sharper operational question: which evidence turns an authenticated description into behavior that a…

History
A BEEP receipt did not authenticate the event: RFC 3195
RFC 3195 moved syslog from a best-effort datagram into a reliable, ordered BEEP channel, then offered a second, per-entry reply model. Neither receipt says that an event is true, durably stored, or acted upon.
History
The Index Named the Policy Row. It Did Not Explain What the Row Meant: RFC 3159
A provisioning system receives two rows. Both contain the same values. Only their row numbers differ. Does that mean the network has received two different policies, the same policy twice, or merely two addressable records awaiting interpretation? RFC 3159 chose a precise answer…

IETF
The Controller Placed the Entropy Label. The Network Still Had to Use It.
A complete Entropy Label Position set can be valid, accepted and atomically installed in controller state while the forwarding path still fails to read, hash on or benefit from the label. Revision 07 makes the control transaction clearer; it does not turn that transaction into a…
History
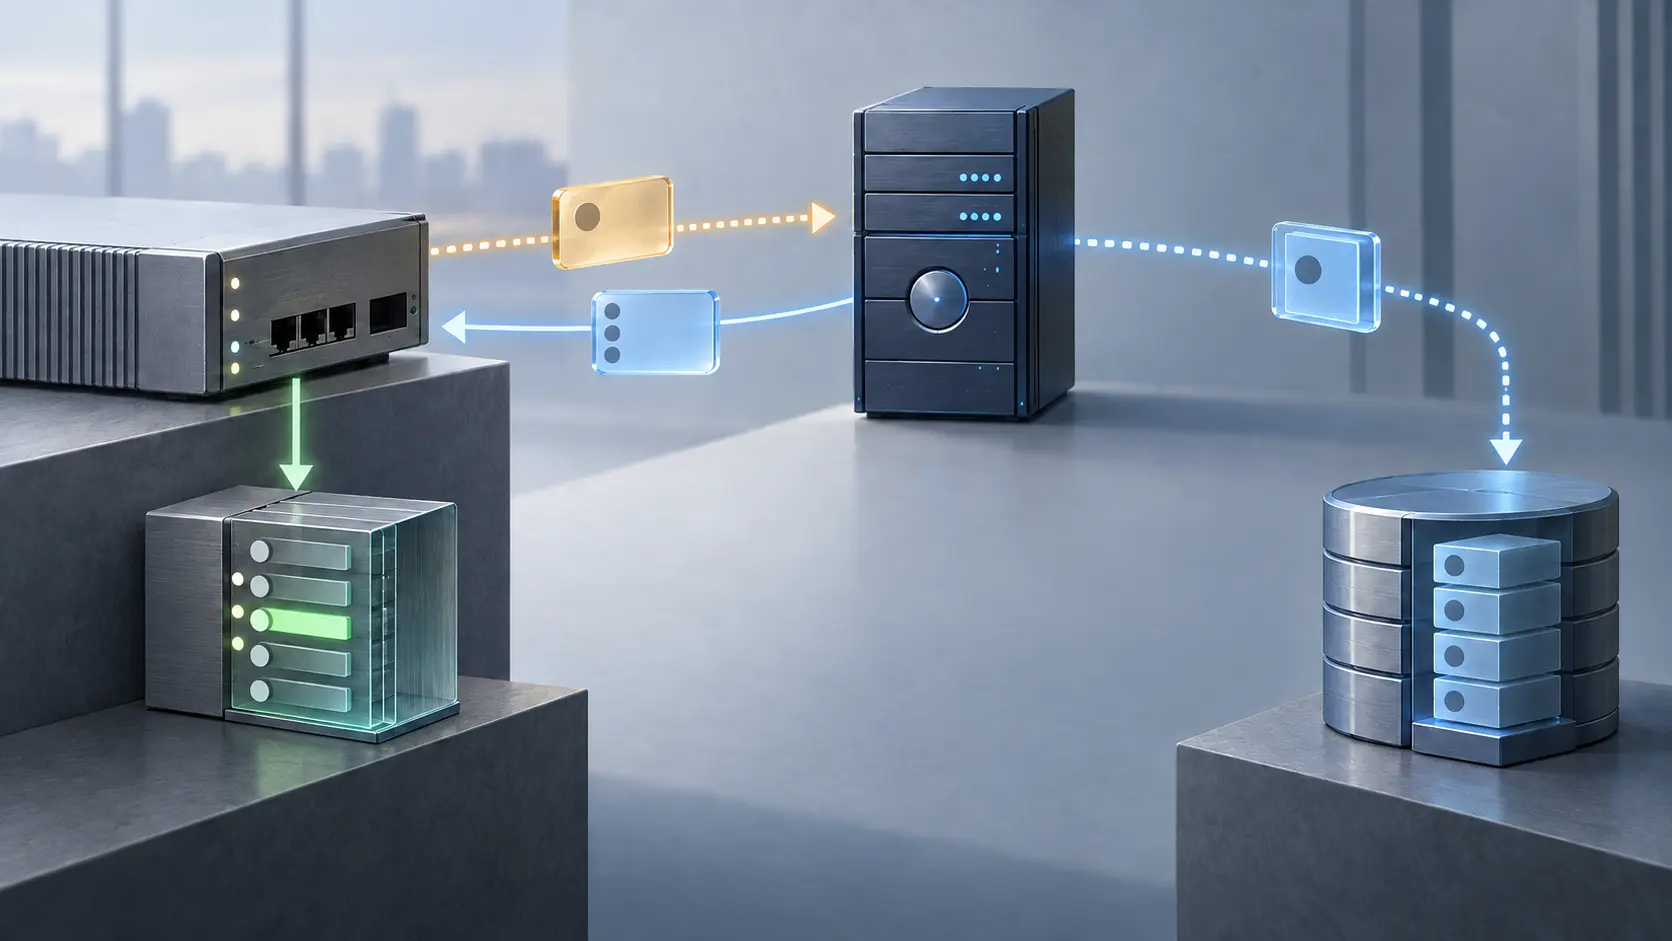
The Server Decided. The NAS Still Had to Act: RFC 3169
RFC 3169 drew a clean line between evidence sent by an access device, the authority to decide who may connect, and the equipment that must make that decision real. Its 2001 checklist is not proof that any network completed the whole chain.

History
The Translator Changed the Packets. It Had to Change the Reports Too: RFC 3158
An RTP translator could make a stream fit a different link by changing its encoding, packet size, sequence numbers or timestamp rate while preserving the source identifier. That success created a quieter obligation. The RTCP reports had to be translated into the same packet…

IETF
The Child Token Was Valid. The Chain Still Had to Authorize It.
A delegated token can carry a perfect signature and still have no usable authority. The proposed OAuth chain works only when every parent, every narrowing step, the leaf key, current status and the resource server’s own policy agree on the same bounded operation.

History
The RFC Still Said Standards Track. Its Record Said Historic: RFC 3167
An old standard can keep its original publication language while its live record changes. RFC 3167 captures one such handoff: a request grounded in a claim about use, followed in today’s catalog by a Historic label.

History
The Server Did Not Need the Plaintext. It Still Controlled Availability: RFC 3157
In August 2001, RFC 3157 asked how one cryptographic identity could follow a user or router from one device to another. Its answer began with confidentiality but did not end there. A credential server might store an entity it could not use as plaintext and still decide whether…

IETF
The Manufacturer Signed the New Trust Roots. The Delivery Server Was Still Untrusted.
A factory-installed key can let a device accept a new operational CA bundle from an endpoint it cannot yet authenticate. That is not a paradox if every grant stays narrow: the signature authorizes the entity, the entity changes a local trust store, and only a fresh validated…

History
The Junior Operator Could Start It. The Senior Operator Built It: RFC 3165
In 2001, the Script MIB made remote management code a set of visible, controllable entities. Its emergency example drew a consequential line: junior operators could press a prepared launch button, while senior operators kept the right to install the script and configure that…