
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

IETF
The Request Carried Its Own Proof. It Still Could Not Issue the Certificate: RFC 9733
RFC 9733 lets a device’s certificate request keep its cryptographic origin while it waits or crosses several transport hops. That makes industrial onboarding more resilient, but it does not make the request self-authorising: the registrar, RA, CA, pledge and access owner still…
History
The Strings Matched. The Identity Was Still Unproven: RFC 3454
Stringprep gave Internet protocols a disciplined way to make internationalized strings comparable. Its four ordered stages could erase, transform, normalize or reject code points until two inputs became character-for-character equal. That equality was valuable, but narrow: it did…
Global Cloud Services
Meta's $279 Billion Bet on Leases, Not Yet On Data Centers
Meta has committed roughly $279 billion to data-center leases that have not even begun. This longform examines what that financing structure actually buys, where announced capacity ends and operating capacity begins, and why the gap between the two registers is where delivery…

IETF
The Practice Statement Was Published. The Ceremony Still Needed Evidence: RFC 3647
The board received a polished certification practice statement. It described dual control, protected keys, revocation targets and annual assessment. What it did not contain was the evidence that last Tuesday’s key ceremony followed those practices, that the repository showed the…
History
Enough Symbols Rebuilt the Object. The Sender Still Did Not Know Who Finished: RFC 3450
ALC made reliable multicast scale by refusing to maintain a delivery conversation with every receiver. Forward-error-correction symbols let each listener finish independently, while the sender could transmit almost the same way for one receiver or a million. The achievement was…
History
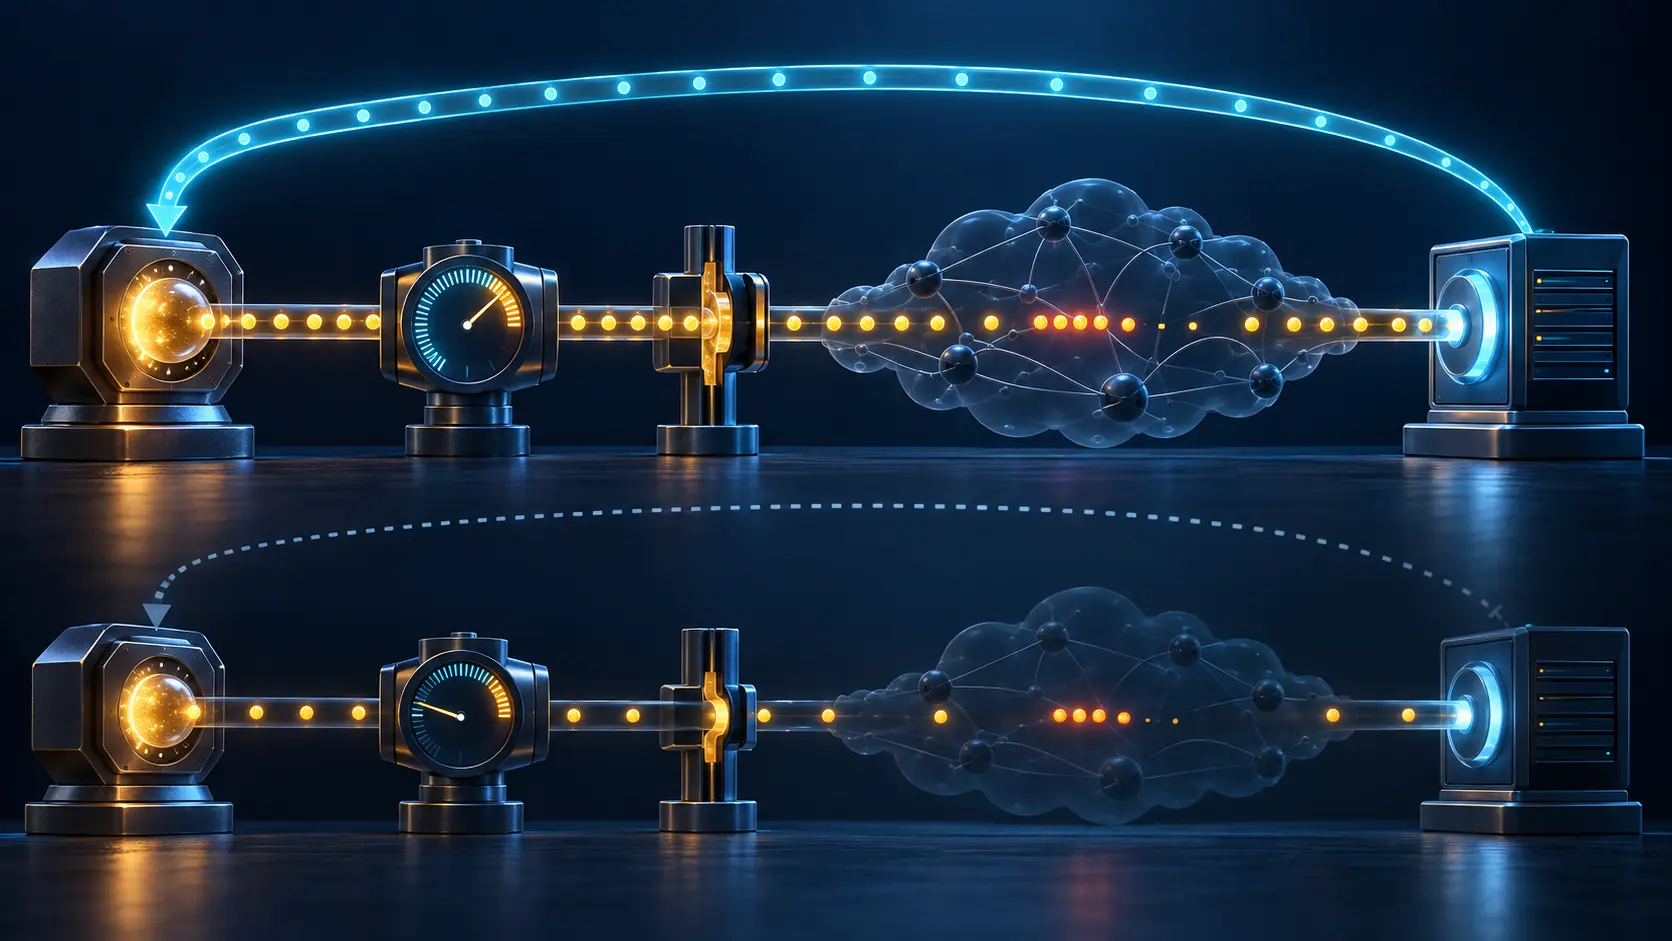
The Receiver Reported a Rate. The Sender Still Needed Its Own Limits: RFC 3448
TFRC was built for applications that wanted a calmer sending rate than TCP could offer. Its historical importance lies in how it distributed the calculation without surrendering the decision: the receiver described what had arrived, while the sender retained the equation, the…

Story
The Identity Chain Nobody Closes: What Can Actually Be Verified About almazcloud.network, AS210328 and AO ALMAZ
The Identity Chain Nobody Closes: What Can Actually Be Verified About almazcloud.network, AS210328 and AO ALMAZ intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the…
IETF
The Probe Came Back. The Tenant Service Still Needed Proof: RFC 9772
A clean Geneve OAM reply is a useful operational fact, but its meaning depends on which VNI, path, endpoint and traffic class the probe actually exercised. RFC 9772 gives leaders a disciplined way to keep tunnel evidence from being promoted into an unsupported promise about…
History
One Shared Address Needed Unique Identities Behind It: RFC 3446
Anycast could make several multicast rendezvous points look like one nearby service. It could not make them one machine. RFC 3446 worked because the address exposed to senders was shared while the identities used between replicas remained unique—and because the protocol never…

IETF
The DNS Server Arrived. The Resolution Path Did Not: RFC 3646
A DHCPv6 Reply can carry a preferred list of recursive servers and a domain search list in a few bytes. That is useful configuration evidence, but it is not a receipt for what the host installed, which resolver handled a query, what name was ultimately asked, whether DNSSEC…
History
One DNS Record Carried Keys That Did Not Share Trust: RFC 3445
The early DNS `KEY` record looked economical: place many kinds of public key in one familiar directory. Its economy disappeared when every query, signature and cache operation had to carry keys governed by different people, rules and failure consequences. RFC 3445 turned that…

IETF
The Group Cipher Opened. It Did Not Name the Sender: RFC 9750
A green decryption result can be entirely correct and still answer the wrong management question. RFC 9750 gives operators a sharper vocabulary for separating group-secret possession, client attribution, identity binding, application authority and delivery—five layers that…

IETF
The Signature Was Valid. Permission Was Still a Separate Question: RFC 3645
A green cryptographic check is seductive. It can make an operations console look as though the whole decision has already been made: the peer is trusted, the requested DNS change is allowed, the zone was updated and users can now see the result. RFC 3645 supports only part of…
History
The Physical Link Knew What the Tunnel Terminator Could Not See: RFC 3437
An L2TP tunnel put PPP control far from the wire whose limits it had to negotiate. RFC 3437 answered that information asymmetry with four messages: the access edge could state what it wanted and allowed, and the remote session owner could return the configuration packets that…

IETF
The Certificate Was Allowed to Sign for Messaging. It Did Not Name the Account: RFC 9734
RFC 9734 gives an instant-messaging certificate a narrower purpose. That is valuable precisely because it does less than many trust screens will be tempted to claim: the new OID can constrain a key’s use without deciding which account is current, which device is authorized, or…

IETF
The Port Was Visible. The Service Was Only a Guess: RFC 3639
A firewall can read a destination port with perfect accuracy and still be wrong about the service. RFC 3639 drew that boundary in 2003: transport labels coordinate endpoints, while a device on the path usually sees only a convention. The more aggressively an intermediary turns…

History
One Secure Stream Cost One TLS Connection: RFC 3436
SCTP promised many independent message streams inside one resilient association. RFC 3436 preserved that independence by giving every protected bidirectional stream its own TLS connection—but the price was a separate handshake, strict ordering, unlimited lifetime and a security…

History
The Notified Entity Received the Commands. It Did Not Resolve the Handover: RFC 3435
A media gateway could be redirected toward a backup Call Agent and still leave the hardest question unanswered: which controller possessed the complete, legitimate state of the call? RFC 3435 made the routing pointer explicit while admitting that controller-to-controller conflict…

IETF
The Counter Went Quiet When the Link Got Worse: RFC 3637
A monitoring curve can flatten for two opposite reasons: the faults stopped, or the counting rule stopped admitting them. RFC 3637 documented the second possibility with unusual candour. Its Ethernet WIS MIB reused deployed SONET management entities even where their interval and…

IETF
The Measurement Label Moved the Flow It Was Supposed to Observe: RFC 9714
A measurement can be internally precise and externally wrong about its subject. RFC 9714 gives MPLS packets a Flow-ID Label for Alternate Marking, yet warns that inserting that label may change ECMP selection—so the instrumented twin can leave the path of the production flow it…