
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
IETF
The String Was Exact. The Authority Was Still Local
A service can now hand a customer a precise DNS change instead of a paragraph of instructions. That removes one class of ambiguity. It does not tell the DNS operator who authored the request, whether the customer may alter the named zone, whether local policy should accept the…

IETF
The AS2 Names Matched. The Signer Was Still a Local Decision
A certificate rollover can leave every visible signal green—TLS connected, names reflected, signature valid, MIC matched—while one decisive fact remains outside the protocol transcript: who authorized this key to speak for this partner, in this direction, now?
IETF
The Channel Stayed Secure. Its Attested State Did Not Stay Current
Binding fresh attestation evidence to a TLS connection closes a dangerous substitution gap at the handshake. It does not freeze the endpoint’s software, policy or authorization state for the lifetime of that connection.

CASE FILE
The Draft Had Eight Numbers. The Registry Still Had None
On 1 October 2026, an OpenPGP implementer could place two official-looking documents side by side and receive two different answers. Revision 05 of a working-group draft called eight composite algorithms 37 through 44. The live IANA registry still called the entire range from 37…
IETF
The Site Reported Zero. Its Routes Could Still Remain in BGP
A revised edge-metadata draft turns one zero-value update into a site-wide forwarding decision. The control is compact; proving which routes, routers and live flows actually obeyed it is not.
History
The Firewall Allowed HTTP. It Had Not Approved the Packet Inside: RFC 3093
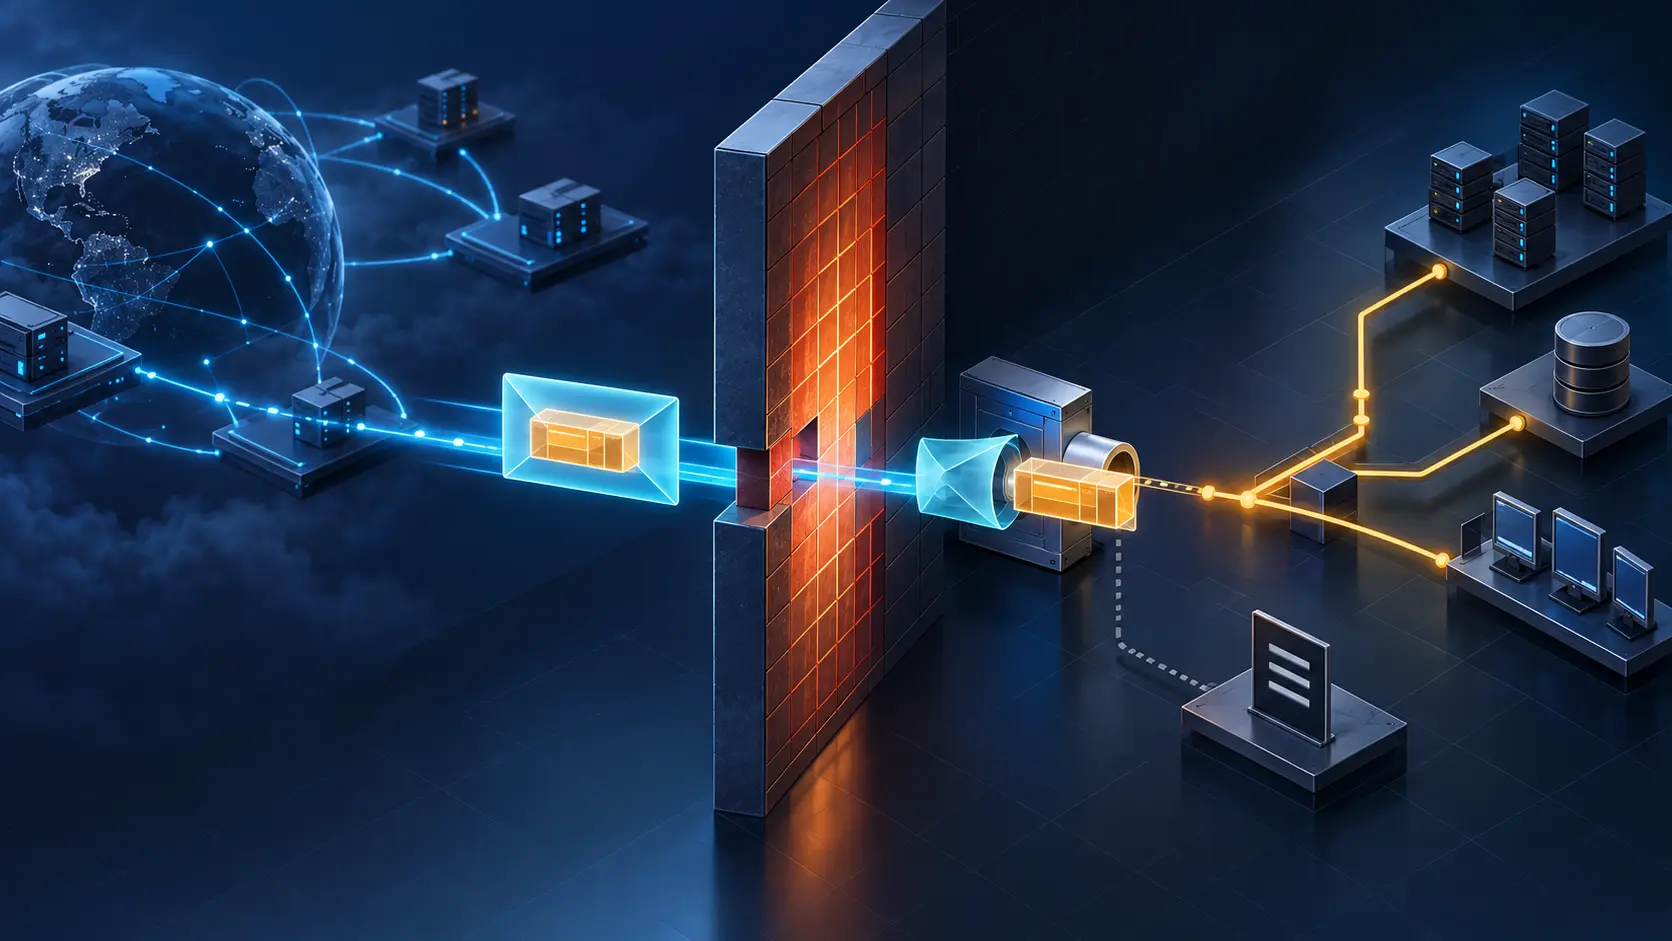
RFC 3093 proposed putting a complete IP datagram inside an HTTP message, passing it through the ordinary web opening, and reinserting it behind the firewall. Published on 1 April 2001, the comic design exposed a serious limit: a policy decision about an outer envelope says…

IETF
The PSP Key Arrived. No Protected Packet Had Crossed the NIC
The IKEv2 exchange can finish with two authenticated peers, an agreed PSP proposal, traffic selectors, SPIs and a wrapped receive key travelling in each direction. The control plane has done real work. Yet neither peer has proved that its sender installed the returned key, that a…
IETF
The Allowlist Could Reach Zero Errors. First the Configuration Had to Be Complete
A new IntraSAV draft replaces route inference with explicit source-prefix authorization. Its strongest promise begins where the operational proof is still missing: the completeness of the configuration installed on each interface.
History
The Same Zone Was Secure Here and Unsecured Elsewhere: RFC 3090
In 2001, DNSSEC could not answer “is this zone secure?” without first asking who was resolving it, which trust anchor that resolver held, and which path it followed. RFC 3090 named that awkward reality. A signed zone could belong to a local island of security and still look…

History
The URI Chose the Voicemail Menu. It Did Not Authenticate the Caller: RFC 3087
In 2001, SIP could carry a call to voicemail without carrying every trustworthy clue that an old telephone system used to choose the first greeting or menu. RFC 3087 turned the request target itself into a service instruction. That solved a routing problem, but it deliberately…

IETF
The Debug Header Named Every Step. It Could Not Prove Any of Them Happened
A new DKIM2 draft gives interoperability testers a common forensic trail inside the message. Its precision is useful precisely because its authority is deliberately zero.

IETF
The RADIUS Server Parsed the Wi-Fi Metric. It Still Did Not Know What Happened
An Access-Request can arrive with a perfectly valid Connect-Info string: a transmit rate, an RSSI and enough syntax for a policy engine to read both. That is useful progress. It is not yet evidence that the radio measured the right frames, that another vendor would report the…

History
The Policy Server Pushed the Rules. A Reconnect Had to Reconcile What the Device Kept: RFC 3084
RFC 3084 tried to make policy provisioning a disciplined conversation between a server and a network device. Its most revealing work began after delivery: a transaction needed a receipt, a failure needed rollback, and a broken connection left two machines that could remember…

IETF
The Refresh Ended. The Collector Still Needed Proof It Had the Whole RIB
A new BMP proposal can repair one stale routing view without tearing down every monitored session. Its ending marker closes a replay; it does not independently certify that nothing was lost inside it.

History
The Cable Link Encrypted Traffic. Its Management Plane Could Still Disable Privacy: RFC 3083
RFC 3083 turned DOCSIS Baseline Privacy into something operators could inspect, tune and reset through SNMP. That visibility helped diagnosis and incident response, but it created a second security boundary: the interface that observed encryption state could also change…

IETF
The Network Was SRv6. The Multicast Tree Was Not Segment-Routed
An operator can migrate the underlay to SRv6, advertise a source through Flex-Algo 128 and still forward every multicast packet through native IPv6 `(S,G)` state. The architecture label is true. The tempting inference—that a SID now describes, installs or proves the multicast…
IETF
The SID Chose the Lane. It Did Not Prove the Lane Was There
An updated Segment Routing draft gives a SID resource meaning as well as forwarding meaning. That makes a packet's intended lane legible. It does not make bandwidth, buffers, queues or an SLA materialise at every hop.

History
TCP Was Reliable. One Channel Could Still Starve the Others: RFC 3081
RFC 3081 placed one BEEP session on one TCP connection, then confronted a consequence TCP could not solve for it. Reliable delivery for the connection did not guarantee progress for every application channel inside it. The mapping therefore added local credit, priority control…

IETF
The Tree Went Silent. The Alarm Came Back on a Different Road
A new BIER Working Group draft lets an active tail report multipoint BFD failure without waiting to be asked. The alarm returns by unicast on a path deliberately separated from the multicast tree—and that separation limits what the receipt can prove.

CASE FILE
The SID Selected the Lane. It Did Not Prove the Capacity Was There
A new Segment Routing identifier can tell every router which resource partition a packet is meant to use. The difficult part begins after that lookup succeeds: proving that the promised bandwidth, buffers and queues were actually committed at every hop, remained bound to the same…