
Topic
DNS Delegation Power
Within the Topic facet, DNS Delegation Power topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
IETF
The Timer Reached Zero. One Signer Was Still Serving Yesterday.
In a constructed operator transition, the controller completed its last configured wait and marked the departing DNS provider safe to remove. The parent showed the new nameserver set. The shared DNSKEY view looked correct. One remaining secondary, however, was still serving an…
IETF
The Token Matched. The Privilege Scope Was Still Blank.
In a constructed operating case, a DNS administrator placed an opaque TXT value at the requested challenge name. The provider found the exact token and granted control over several service features. The record proved that a challenge had reached DNS. Nothing in it showed that the…

History
A DNS Alias Could Move a Service. It Could Not Prove One Existed: RFC 2219
In 1997, familiar labels such as `www` and `ftp` offered a convenient front door to a service that might move between machines. RFC 2219 turned that custom into guidance, while drawing a firm line between a useful naming hint and proof that a service was running.
History
The Zone Was Critical. That Did Not Make It a Permanent Root-Server Job: RFC 3172
In 2001, `.arpa` was important enough to inherit the operating expectations of the DNS root. Yet RFC 3172 did not convert that importance into a permanent claim on root-server machines. It recorded the shared service arrangement as something likely to change. The name could…
ICANN
ICANN Counted 1,616 Applications. It Had Not Added 1,616 TLDs.
Reveal Day will make the 2026 new-gTLD round visible. Visibility matters: it exposes applicants, proposed strings and collisions to scrutiny. But the number now circulating is a receipt for paid applications entering a long process, not a measure of namespaces operating in the…

History
A One-Day Workshop Could Not Test an Expiring Signature: RFC 3130
By the time DNSSEC specialists met around IETF 49, the short workshop had become a misleading unit of proof. A signer could run, a validator could answer and a demonstration could end successfully before the clocks, organisations and independent implementations that determined…
IETF
The String Was Exact. The Authority Was Still Local
A service can now hand a customer a precise DNS change instead of a paragraph of instructions. That removes one class of ambiguity. It does not tell the DNS operator who authored the request, whether the customer may alter the named zone, whether local policy should accept the…

Story
Two-Thirds, Not Unanimity: How the RIR Governance Document's Version 3 Rewrites Who Decides
The draft that would replace ICP-2 does not merely modernise twenty-five-year-old criteria for recognising Regional Internet Registries. Its Version 3 quietly redraws the voting arithmetic of recognition, derecognition and amendment — and those thresholds, not the prose around…
Asia-Pacific Institutional
The Challenger Who Never Held the Delegation: Cloud Registry Pty Ltd and the Contracted Enclosure of .au Authority
Cloud Registry Pty Ltd has spent more than a decade arguing that Australia's .au registry should be awarded by open tender, and it has never once held the contract. That record makes the small Sydney company a useful instrument for reading how delegated authority over a national…
IETF
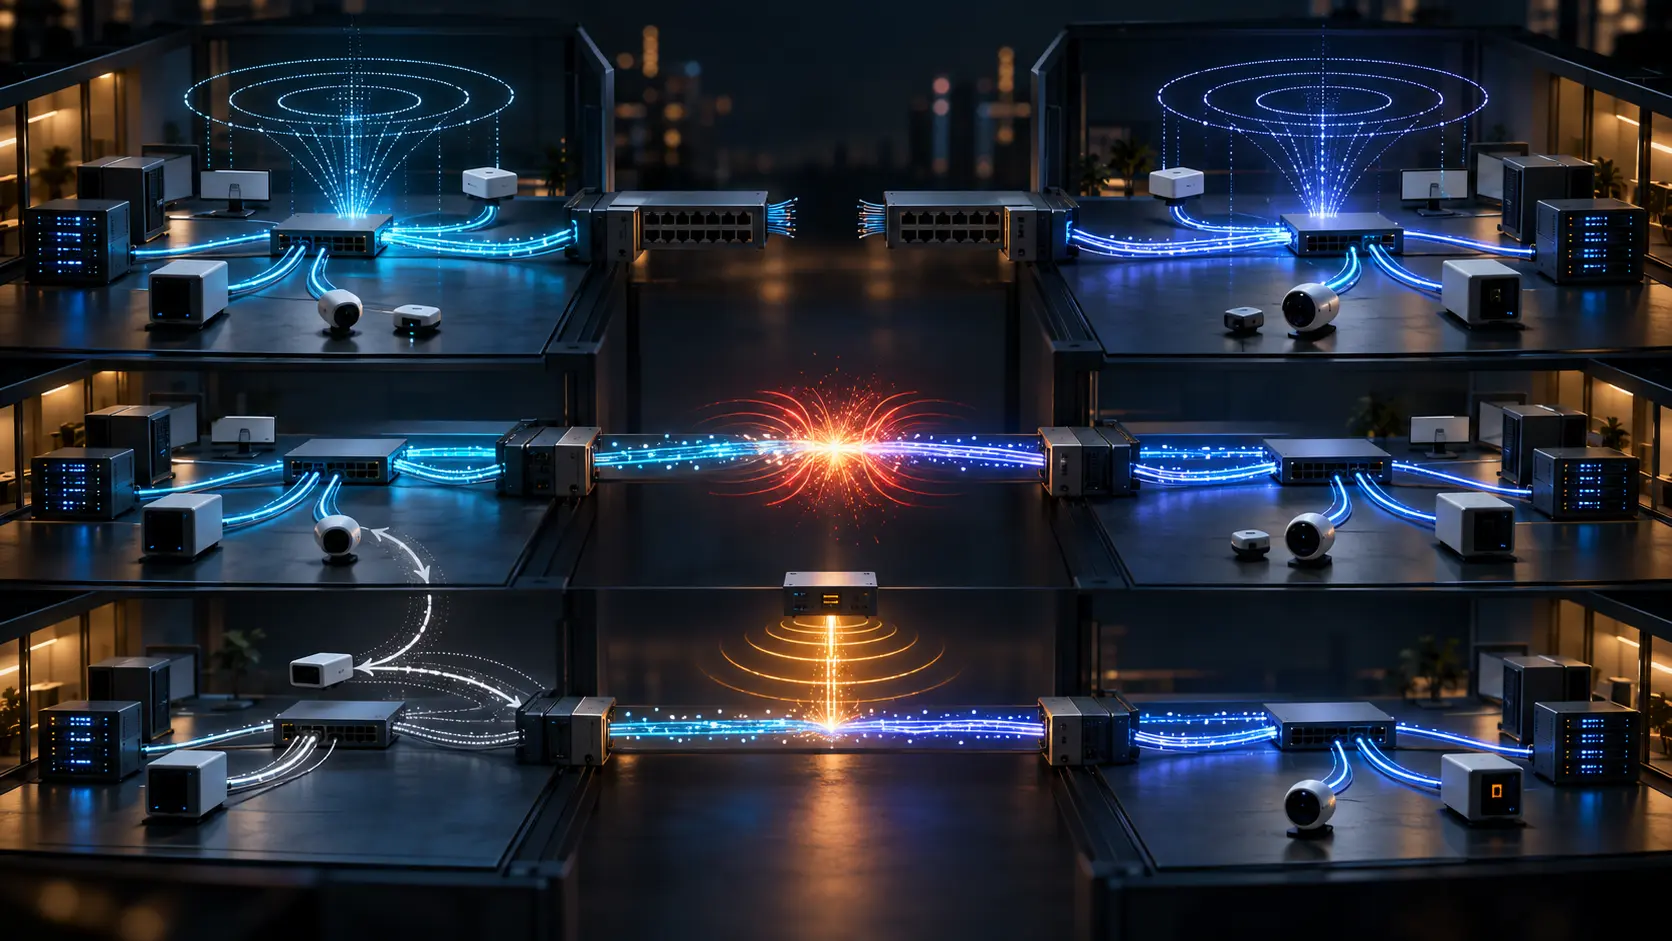
Silence Is Not Availability: The Multicast Address That Survives Until the Partition Heals
Two senders can each complete a clean probe, retain the same multicast group ID and continue without an alarm. The contradiction appears only when the switch comes back and the network becomes whole again. An IETF draft now makes that delayed failure unusually legible: its…
IETF
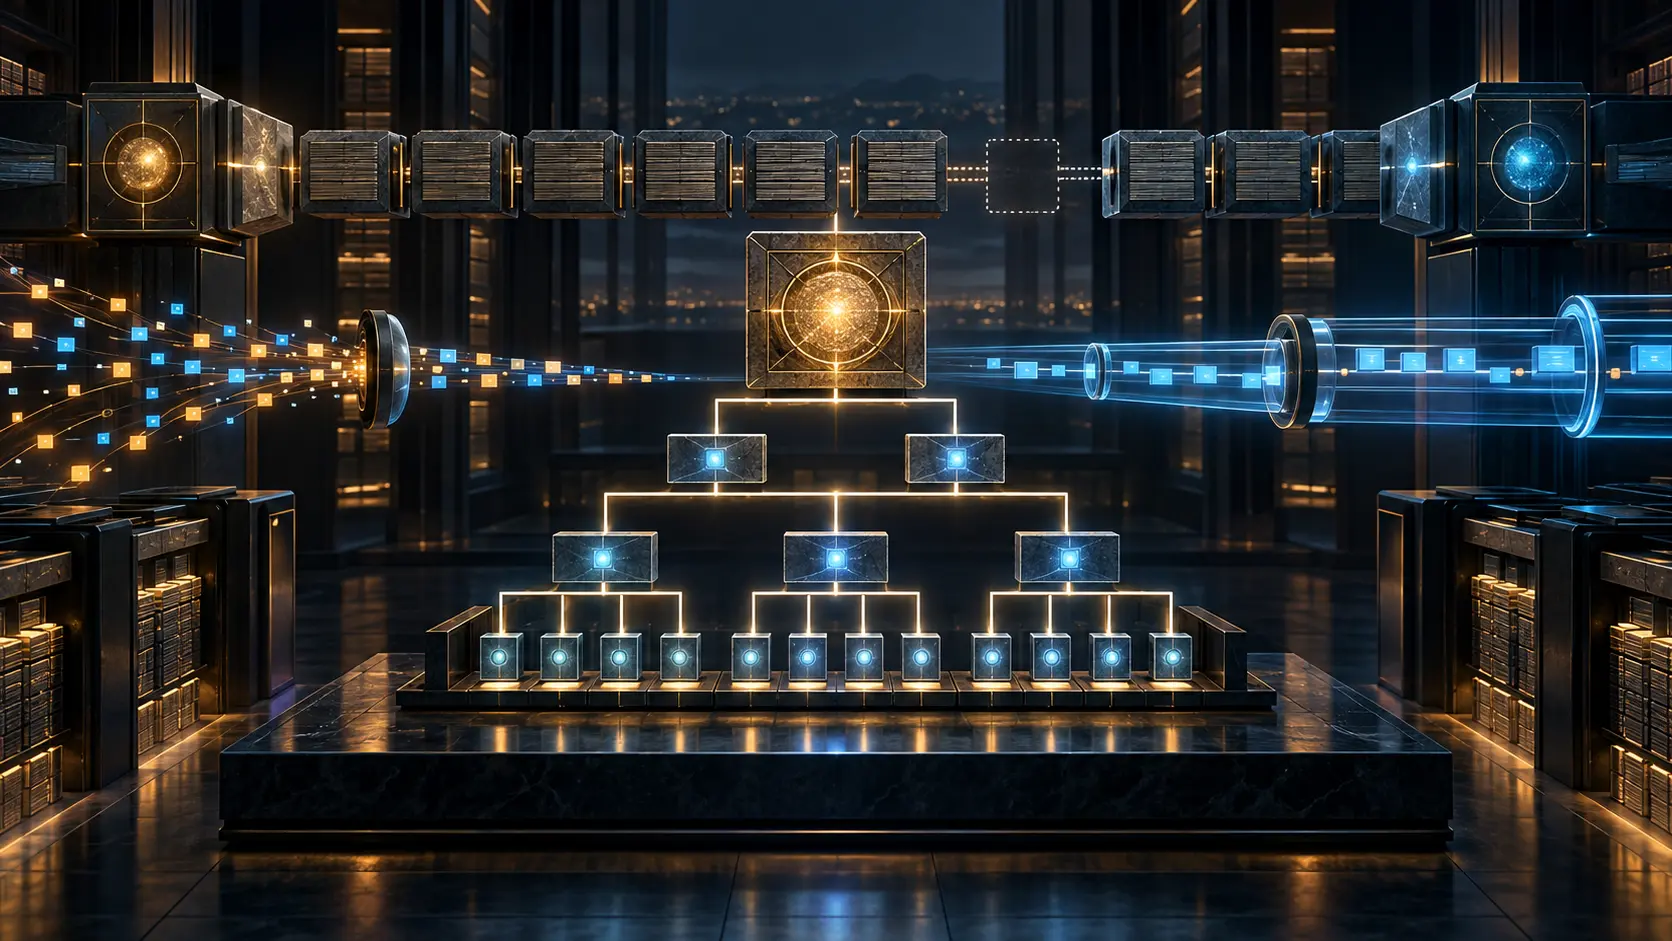
The Signature Got Smaller. The Signer Inherited a History.
The standby signer had the same zone and the same ML-DSA private key. What it did not have was the live node set: the series identifier, the next leaf index, the randomizers and the ladder against which current proofs had been built. Cryptography had reduced repeated signatures.…
IETF
An EPP Draft Adds a Remove-All Command for DELEG Records
An individual Internet-Draft now gives a registrar-side client a way to request removal of every DELEG record for one domain in a single EPP update. The proposed shortcut makes the authority for a bulk change, and the evidence of what it changed, more important than the brevity…

IETF
The Registry Accepted the New Delegation. The Parent Still Had Two Answers
An EPP success response can close a registry transaction while leaving the DNS change open. Revision 03 of the proposed EPP mapping for DELEG records makes that distinction operationally urgent: one command can remove every DELEG record, even as traditional NS data continues to…

Leaders
Martin J. Dürst and the Boundary Inside a Unicode URL
A link can look like one string to its reader and become several different things to software. Martin J. Dürst’s work on Internationalized Resource Identifiers helped make that handoff explicit: a Unicode host name, a DNS label, a URI path and a server-side resource key do not…
CASE FILE
The Child Still Answered. The Parent Had Already Moved the Delegation
A DNS server can answer authoritatively from the old home of a zone after the parent has assigned that zone elsewhere. Revision 14 of the delegation-revalidation draft turns that paradox into an operating rule: child-side credibility must never be allowed to renew parent-side…

IETF
The ACME Key Rotated. Yesterday's DNS Authorization Still Works
The newest ACME DNS persistence draft turns routine key rotation into an accounting problem. A retired signing key may be unable to place another order while its public thumbprint still keeps an earlier DNS authorization usable.

CASE FILE
The Name Was Allowed. Yesterday’s Address Blocked the Device: RFC 9726
A manufacturer can put the right service name in a MUD policy while a firewall enforces the wrong moment of that name. RFC 9726 exposes the hidden translation between DNS intent and packet rules—and why a clean policy file is not proof of a working or safe IoT device.

ICANN
The Second Face of JPRS: The Contract Track That Sits Beside Japan's .jp Mandate
Japan Registry Services Co., Ltd. is usually described in one sentence: it runs .jp. That sentence covers only half of the company's authority. The other half is not delegated by anyone — it is bought, signed and renewed, and it is policed by a different institution with a…

History
From Personal Delegation to Public Registry: The Instrument Trail That Moved .au, 1986–2001
In March 1986, the .au country-code top-level domain was delegated to one person: Robert Elz, then a network programmer at the University of Melbourne. By the end of 2001, the public record showed the domain's authority in the hands of .au Domain Administration Ltd (auDA), a…

ICANN
Who Controls the .jp Registry? The Instrument Chain Above JPRS
Japan Registry Services Co., Ltd. (JPRS) sits at the center of a layered control surface for the .jp country-code top-level domain: IANA and ICANN grant its international authority, JPNIC and Japan's government can challenge it, and a 2025–2026 evaluation cycle plus a second…