
Time Horizon
Immediate and Ongoing
Within the Time Horizon facet, Immediate and Ongoing time-horizon intelligence organises articles by the period over which a signal is expected to matter. The page helps readers distinguish immediate operational changes from longer-cycle governance, investment, standards, and infrastructure shifts that may unfold across quarters or years. It connects timing assumptions with public evidence, related actors, market context, customer exposure, policy pressure, and infrastructure planning so readers can judge whether a development is urgent, strategic, or still waiting on confirming evidence. The page also explains how time horizon changes the meaning of a signal, which organisations may be exposed, and which infrastructure decisions require short-term action or long-cycle monitoring.
Global Cloud Services Trends
A DNS Cookie Is Not Client Authentication
A DNS Cookie can help a server distinguish a request that carries previously issued protocol state from one that merely claims a source address. That is useful against several off-path attacks. It does not identify the person, subscriber or device behind a recursive resolver, and…

Global Cloud Services Trends
An OCSP Staple Is Not a Live Revocation Guarantee
A stapled OCSP response can save a client from making a separate status request during a TLS handshake. It can also be signed, correctly matched to the certificate and still inside its stated time window. Those are valuable properties. They do not prove that every serving edge…

Global Cloud Services Trends
TLS 1.3 0-RTT Acceptance Is Not a Replay-Safety Decision
Early data can remove a round trip from a resumed connection. That speed is real, but accepting the bytes does not prove that the application operation is safe to execute twice, authorised under current policy or protected by a shared deduplication decision.

Global Regional ISP Trends
A QUIC Connection ID Is Not a Durable Principal
A connection identifier can keep a QUIC session reachable while the network path changes. That continuity is operationally useful, but it does not turn the identifier into an account, a subscriber or a durable statement about who is authorised now.
Global Cloud Services Trends
A Fresh HTTP Cache Entry Is Not Current Origin Authorization
A cache can be correct about age and wrong about present authority. Freshness permits reuse of stored bytes; it does not prove that the origin still wants those bytes disclosed to this requester.

Global Cloud Services Trends
An OAuth Access Token Is Not a Current Authorization Decision
An access token can remain acceptable after the decision that justified it has changed: a self-contained token may still pass local cryptographic checks, while an opaque reference token may still be accepted through a state lookup. The operational question is therefore not merely…
Global Cloud Services Trends
A TLS Delegated Credential Is Not a Delegation of Domain Control
A short-lived credential can let a CDN edge complete a TLS handshake without holding the certificate owner's long-term private key. That is a precise cryptographic delegation. It is not a transfer of the domain, certificate-issuance authority or the organisation behind either…

Global Cloud Services Trends
A QUIC Connection ID Is Not a Subscriber Identity
A QUIC connection can survive a change from Wi-Fi to mobile access. The identifier that helps packets find that connection is transport state, not proof of who holds the handset, which account is active, or whether an application action remains authorised.

Global Cloud Services Trends
A Fast 0-RTT Handshake Is Not a Once-Only Transaction
TLS 1.3 and QUIC can remove a round trip from a resumed connection. That is a latency result, not a receipt that a state-changing request reached the application once, was committed once, and will never be replayed elsewhere.
Global Institutional Trends
A Valid Software Signature Is Not a Durable Authority Record
A green verification result can survive long after the authority that made a release legitimate has changed. The cryptography may still be sound. The missing evidence is organisational: who was permitted to sign, under which role, at what time, and what later revocation or…

Global Regional ISP Trends
A Graceful BGP Restart Can Lengthen a Blackhole
Graceful Restart is meant to keep traffic moving while a BGP process returns. Its safety depends on a fact the surviving session cannot prove by itself: whether the restarting router still has the forwarding state needed to carry packets. When a helper retains a route longer than…

Global Regional ISP Trends
A Fast IPv4 Fallback Can Make Broken IPv6 Look Healthy
A dual-stack service can answer every ordinary check while its IPv6 path is unusable. The availability result is real, but the protocol-family conclusion is not: a client may have escaped through IPv4 before the dashboard noticed what failed.

Global Cloud Services Trends
A Root Certificate Removal Is a Fleet Migration Before It Is a Browser Update
A root programme can withdraw trust in one release while many applications keep making decisions from older, private or embedded stores. The security change is complete only when the verifiers that matter can prove the intended rejection.
Global National Telecom Trends
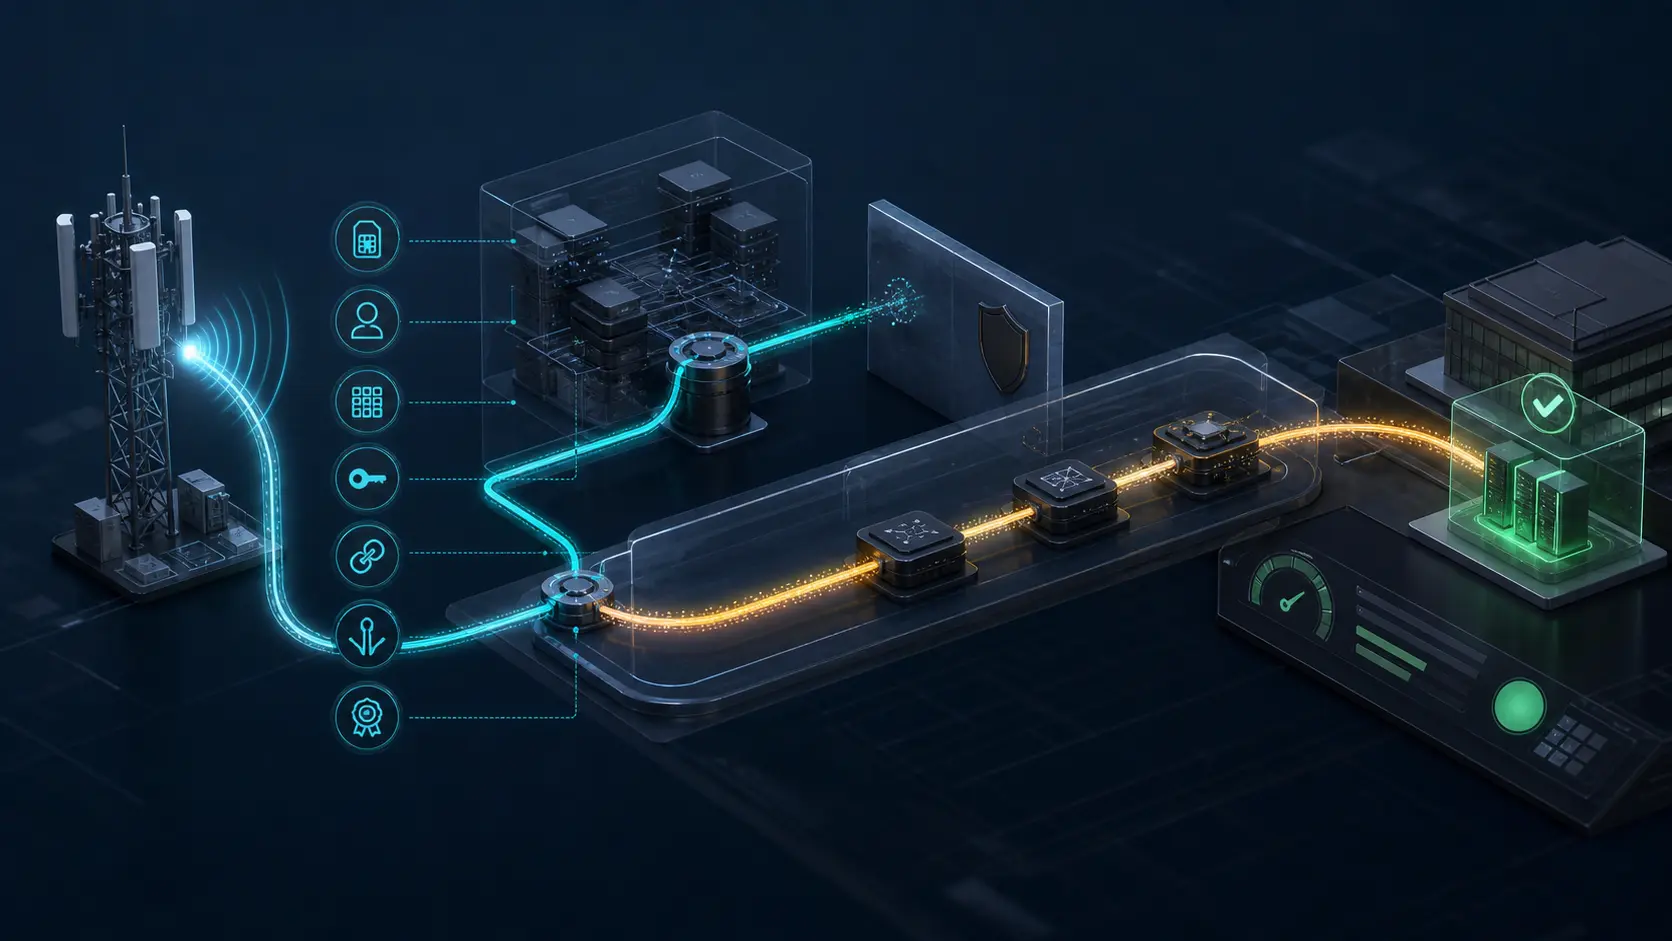
The Default Slice Can Make a 5G SLA Look Healthy
An application can remain reachable after the network path promised in its 5G service agreement has disappeared. The uptime chart stays green; the harder question is whether the device, session and packets still occupied the contracted slice.
Global Cloud Services Trends
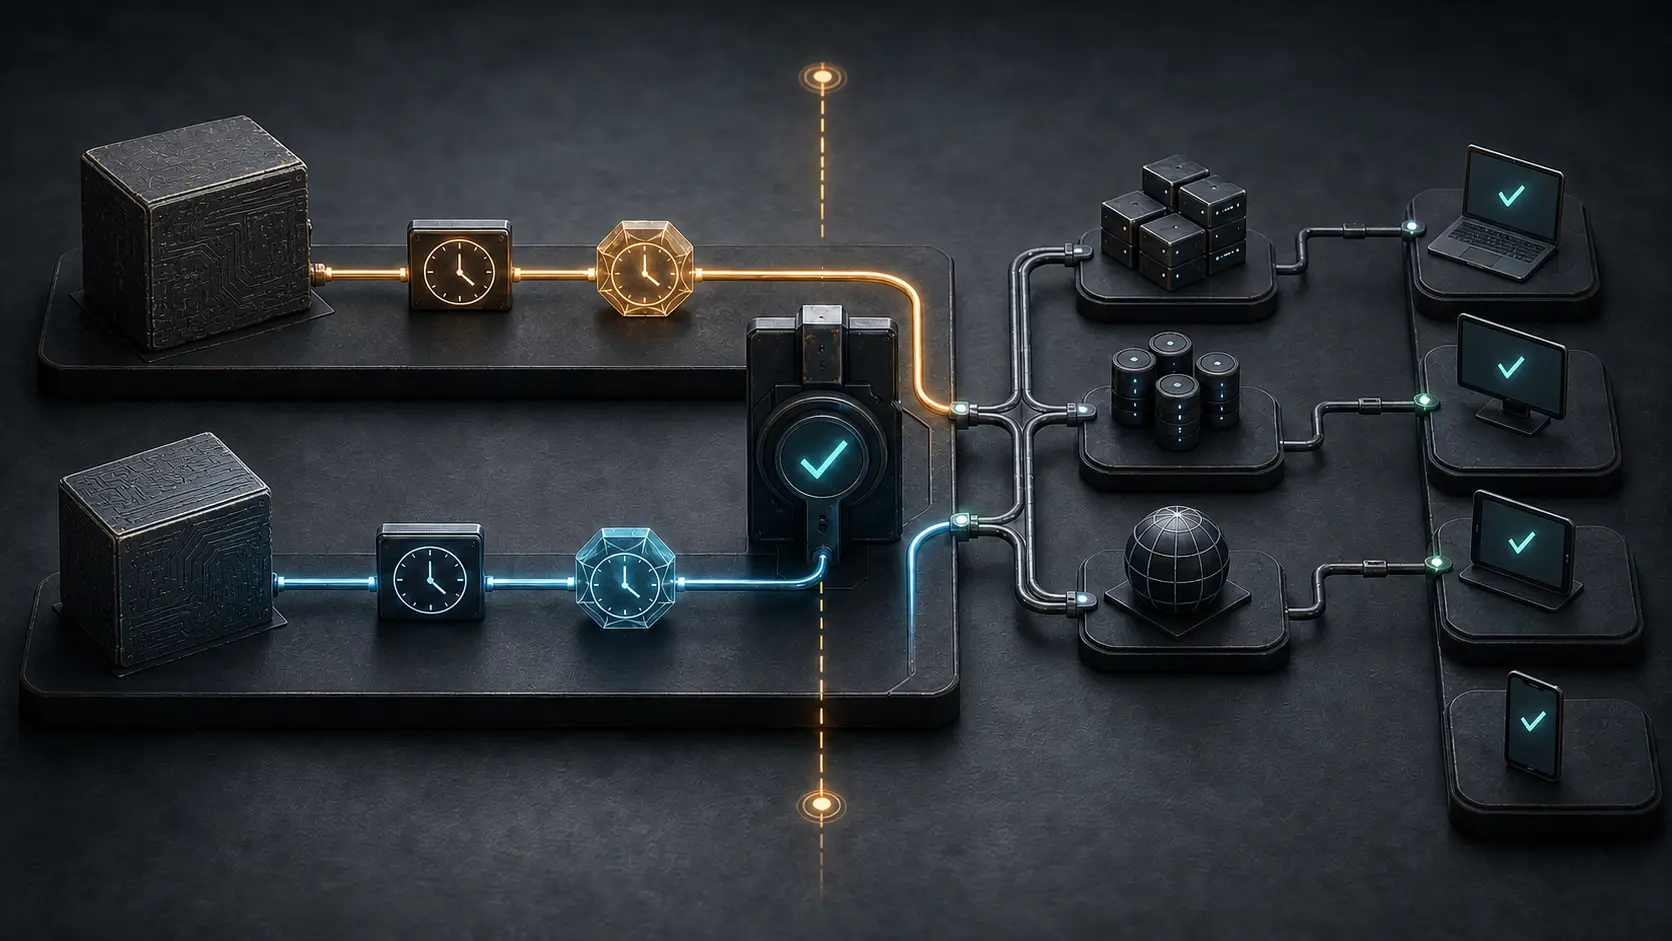
A Code-Signing Certificate Has Two End Dates
A replacement certificate changes tomorrow's build, but a valid timestamp can preserve yesterday's binary beyond the signer's expiry. The real cutover is therefore an inventory of artifacts, timestamp tokens, revocation time and verifier results—not a closed renewal ticket.
Global Cloud Services Trends
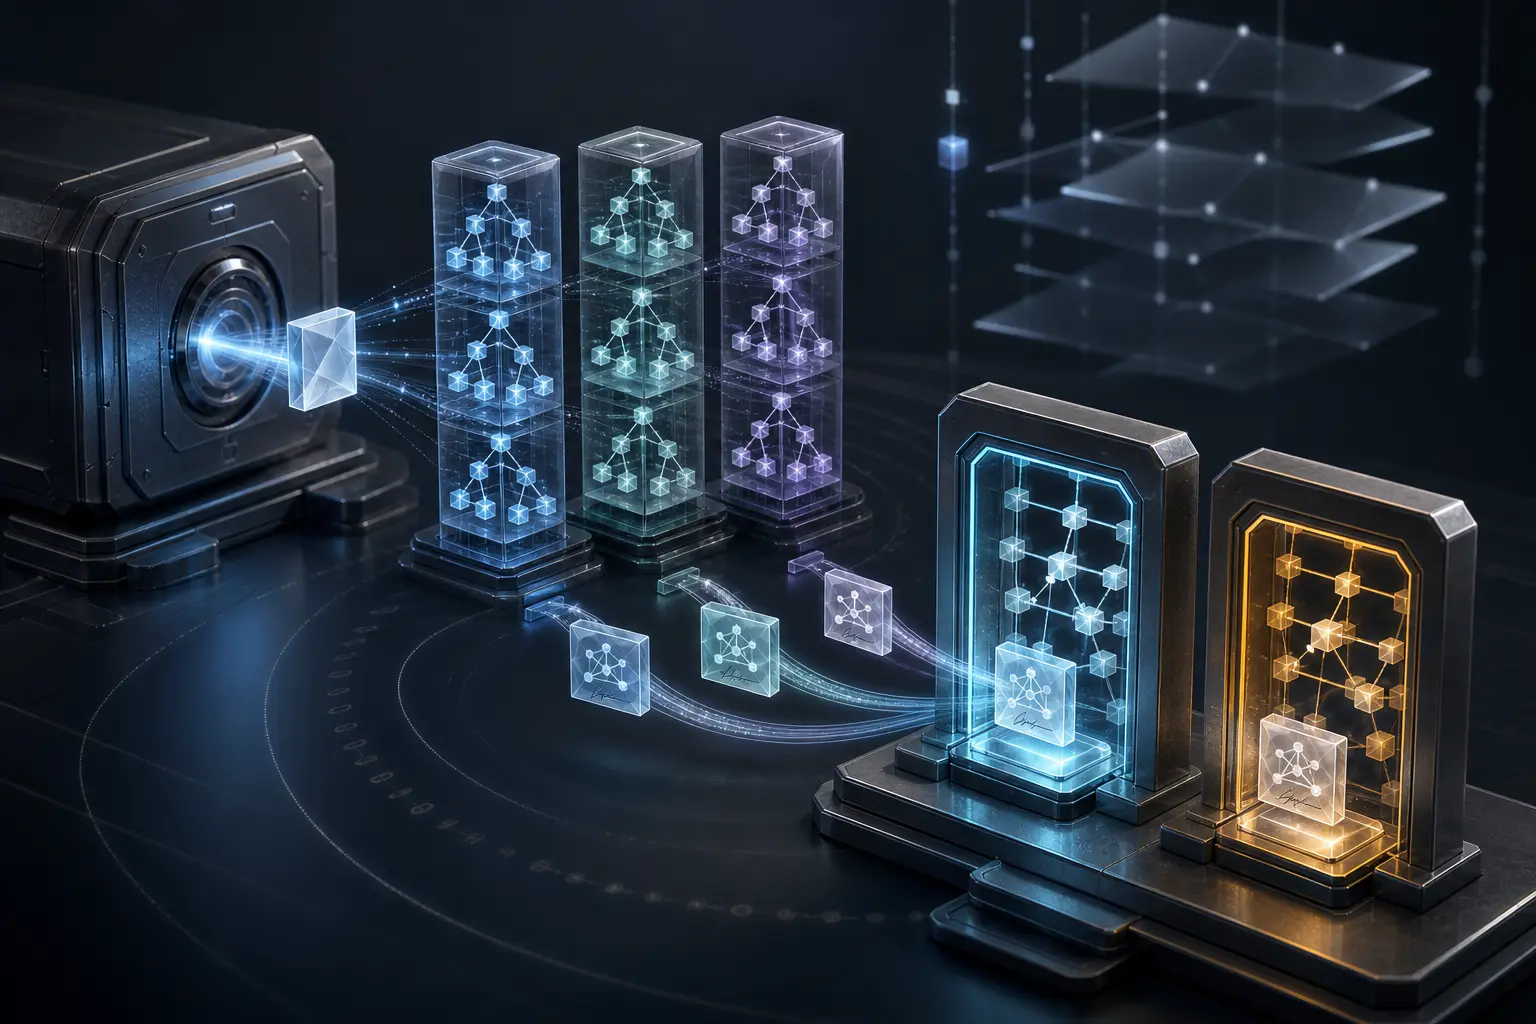
A Certificate Transparency Receipt Is Not Browser Acceptance Until the Log Set Is Reconciled
A certificate authority can return a certificate carrying several valid log receipts and still leave an operator with a failed browser handshake. Certificate Transparency becomes operational evidence only when the receipt is reconciled with the policy and log set used by the…

Global Cloud Services Trends
From 200 Days to 47, TLS Renewal Becomes Runtime State
Public TLS certificates are getting shorter. The consequential change is not a busier expiry calendar; it is that authority, issuance, deployment and external verification must now behave like one continuously observed production system.
North America Regional ISP Trends
BEAD awards do not become project cash until reimbursement clears
A fibre crew can finish a week's work while the contractor's payroll and the supplier's invoice fall due before the state has accepted the next BEAD payment trigger. The award may be valid, the construction eligible and the project economic, yet the subgrantee still has to…

North America National Telecom Trends
The outage clock starts before the root cause exists
Canada’s major-outage rules do not wait for an incident team to finish explaining the failure. They create a sequence of reporting clocks that begins with threshold evidence, continues through material updates and ends in a post-outage record that can survive both regulatory and…